Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

An ArchLinux based distribution for penetration testers and security researchers.

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

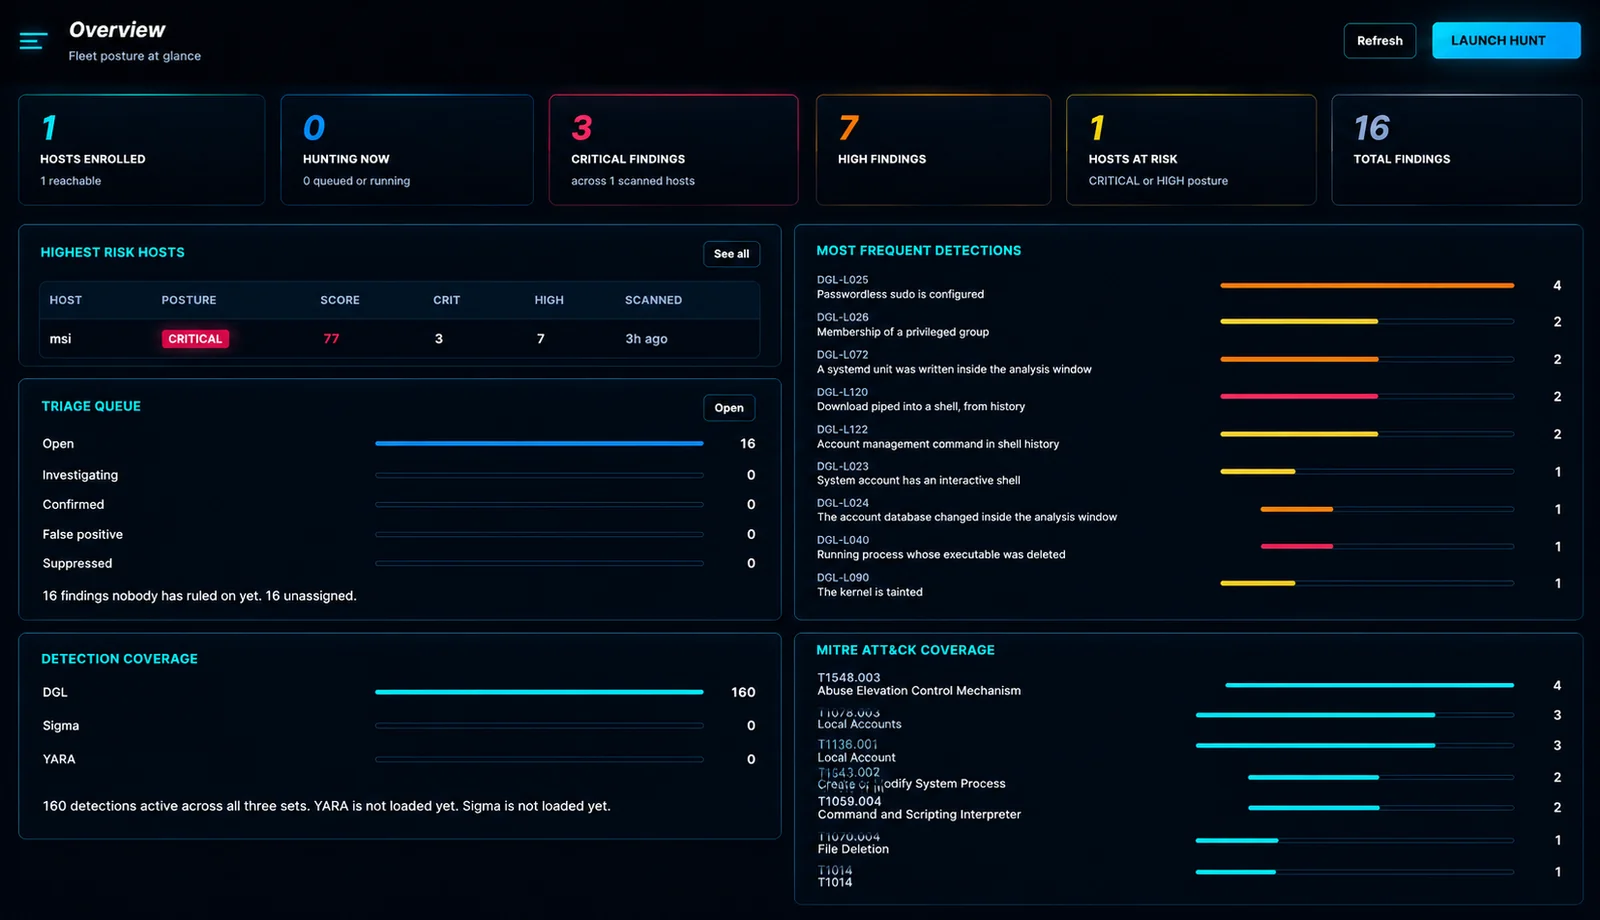
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…

Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

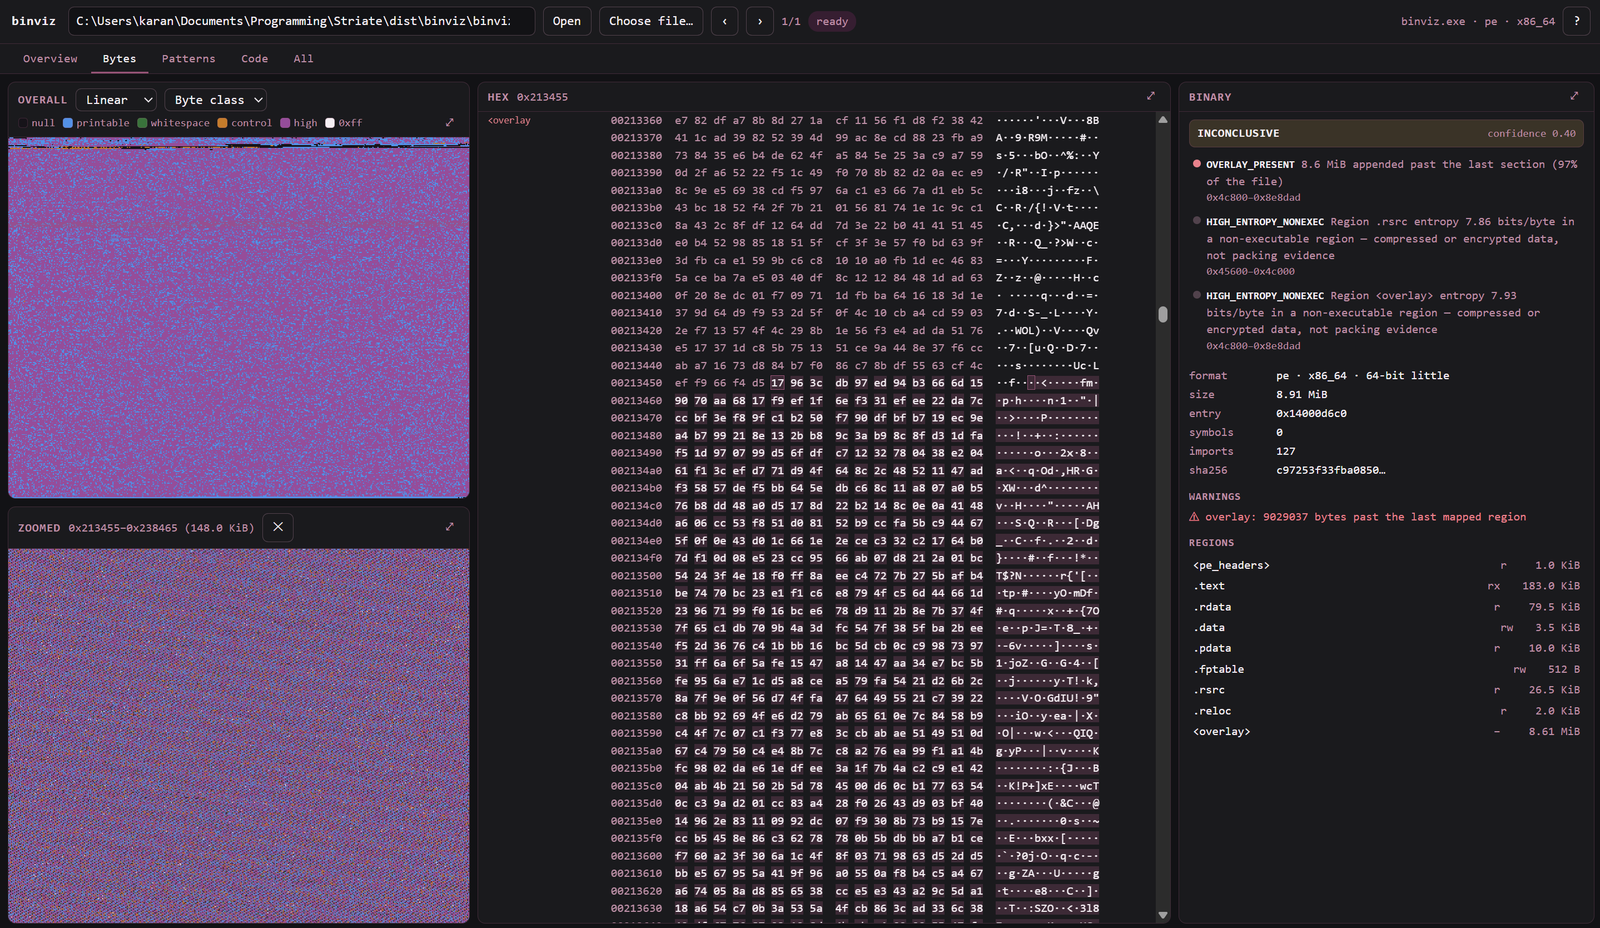
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.

Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)

YARA rule and python script to detect potential exploits for the CVE-2026-21509 vulnerability in MS Office

Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…

A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

🗒️ A [work-in-progress] collection for interview questions for Information Security roles

A cross platform parser for Apple UnifiedLogs!

A Repository to Track Anti-Forensic Techniques

HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root

🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…