

DMA-ProcessDumper
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
gmh5225/dma-processdumperSimple Process Dumper using DMA over a PCIe FPGA device
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 cyb3rtus/keepass_cve-2023-24055_yara_rule
Contains a simple yara rule to hunt for possible compromised KeePass config files
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 murrayr0123/cve-2024-3400-compromise-checker
A simple bash script to check for evidence of compromise related to CVE-2024-3400
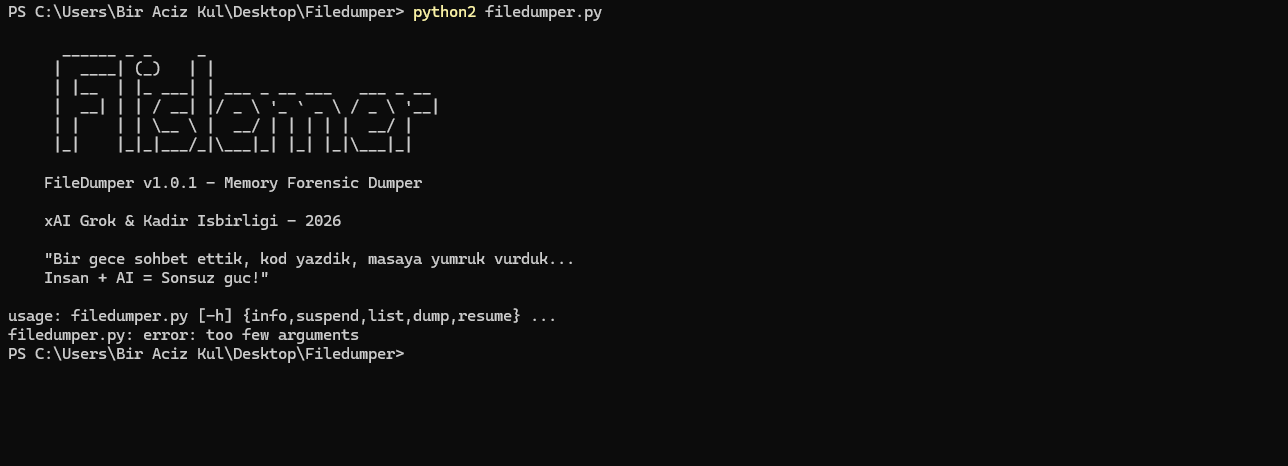 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 secrary/ssma
SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
 busindre/mozcache
Simple shell script to perform forensic analysis of the Mozilla-Browsers cache (Firefox, Iceweasel and Seamonkey).

 botherder/kraken
Cross-platform Yara scanner written in Go
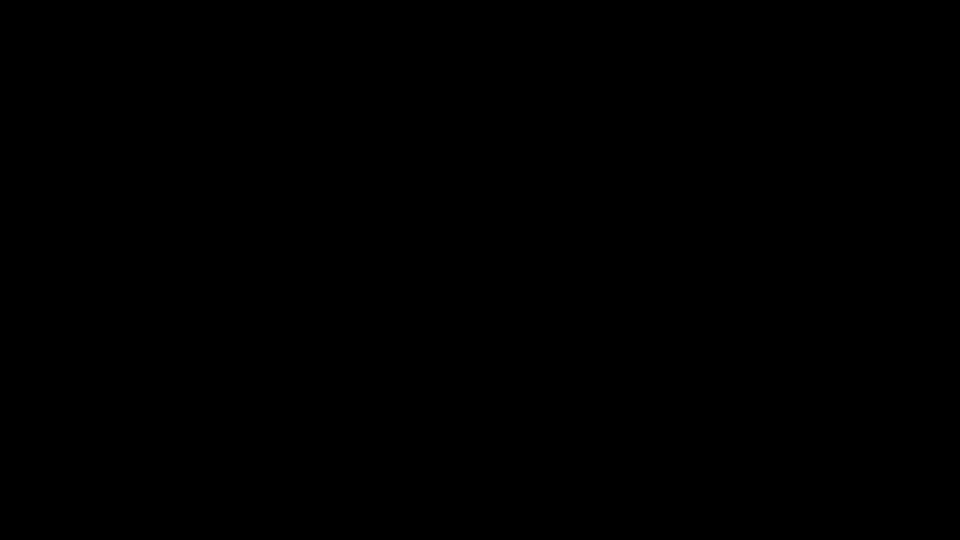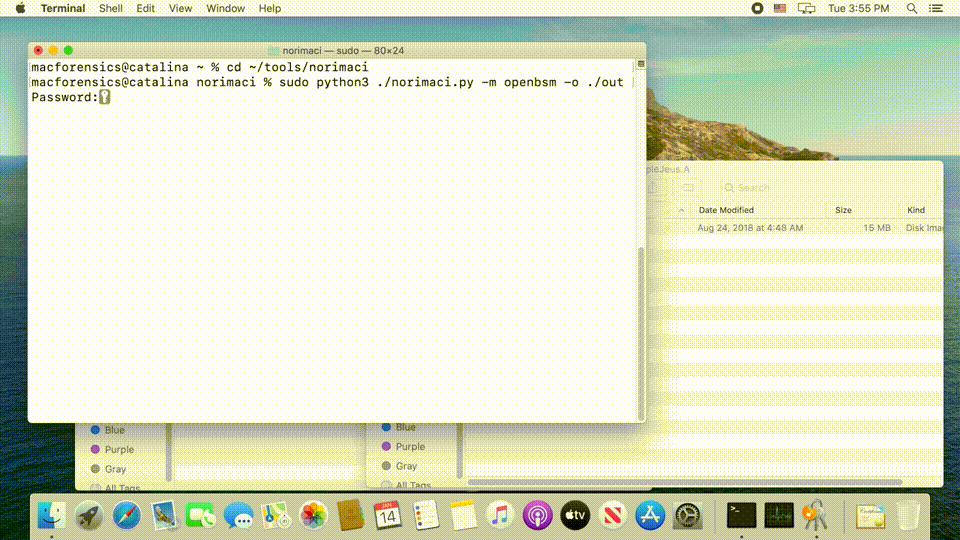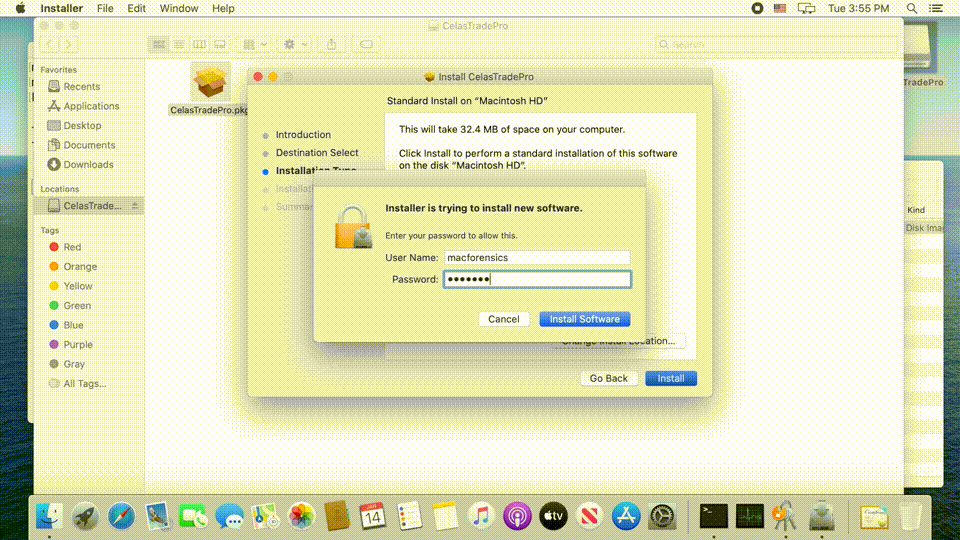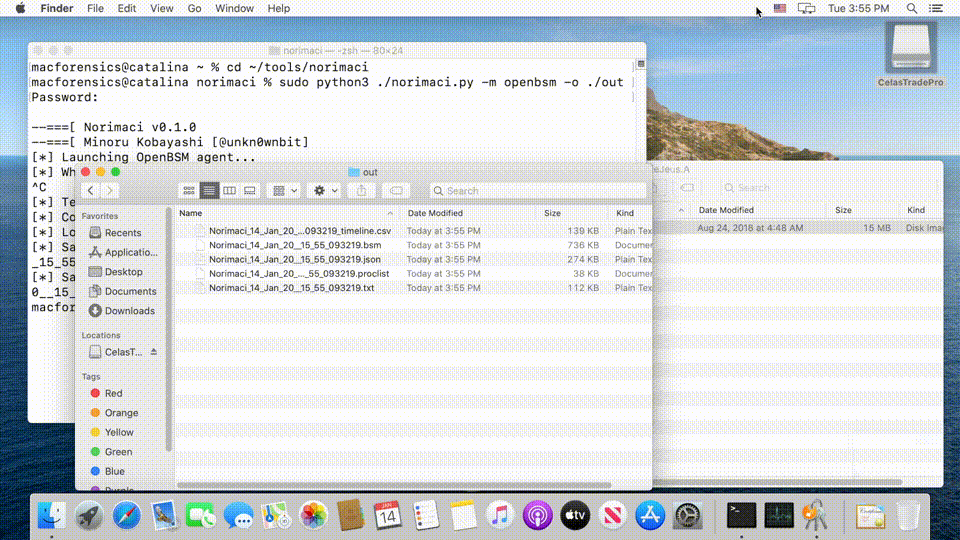 mnrkbys/norimaci
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
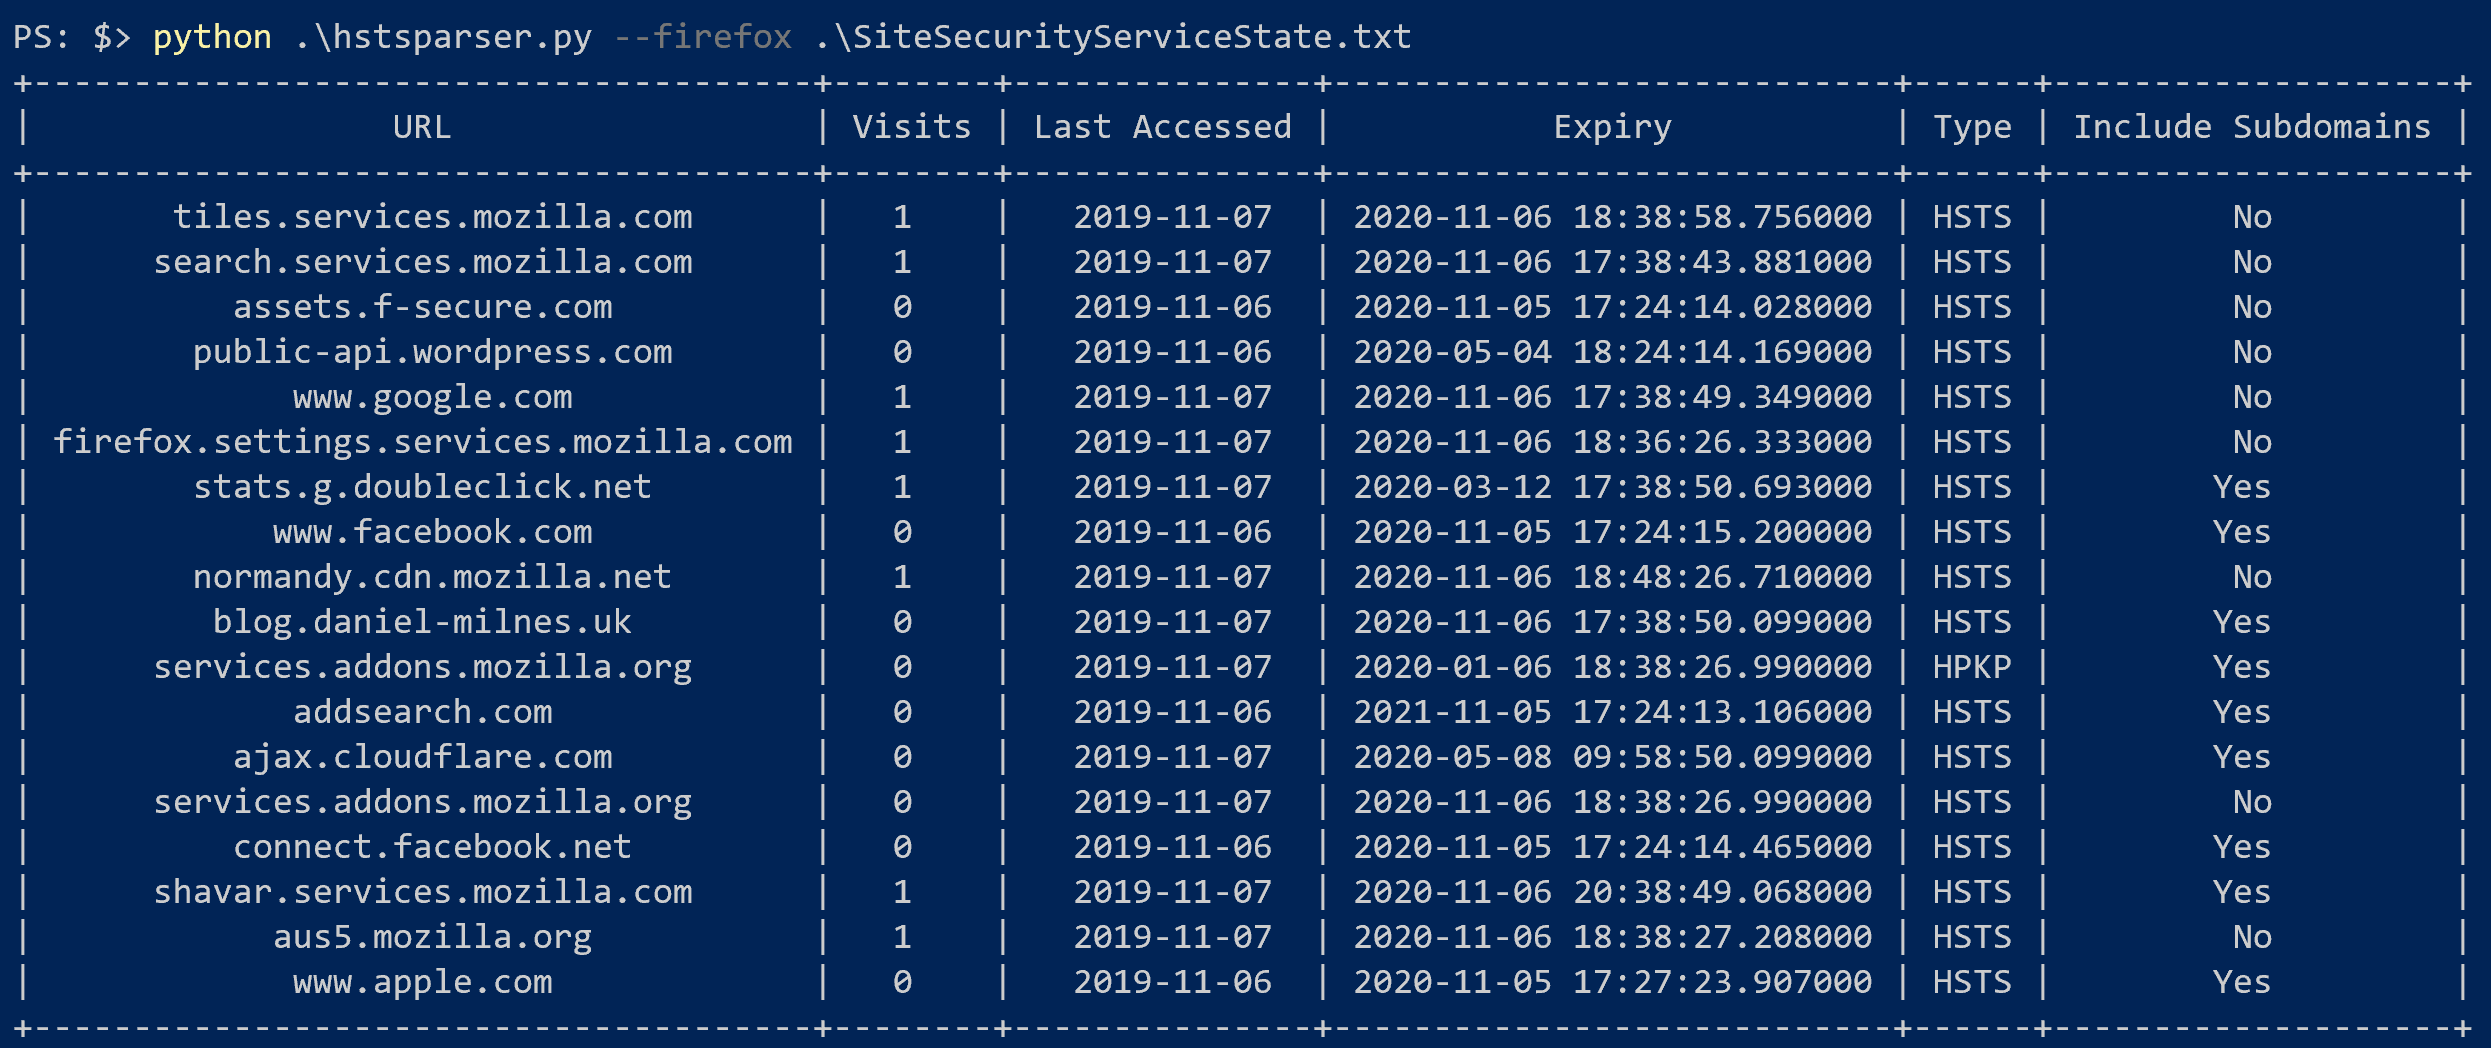 thebeanogamer/hstsparser
A tool to parse Firefox and Chrome HSTS databases into forensic artifacts!
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.