
frida-stalker-NtStrace
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+4
3
gmh5225/frida-stalker-ntstracefrida-stalker based system call tracer on windows(x64).
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
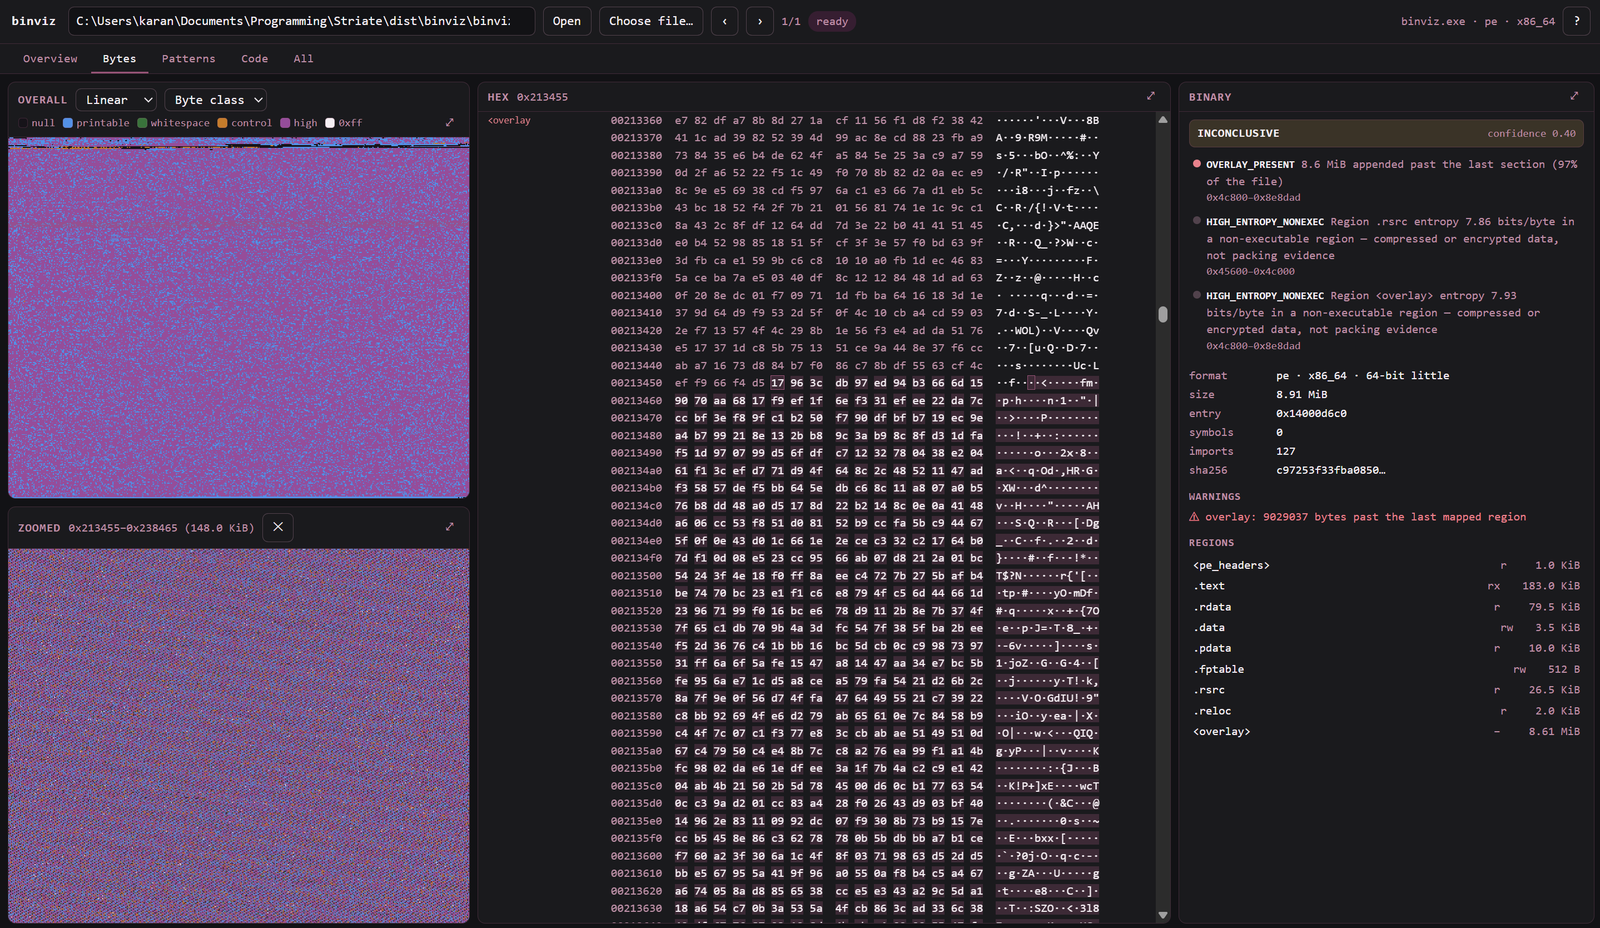 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
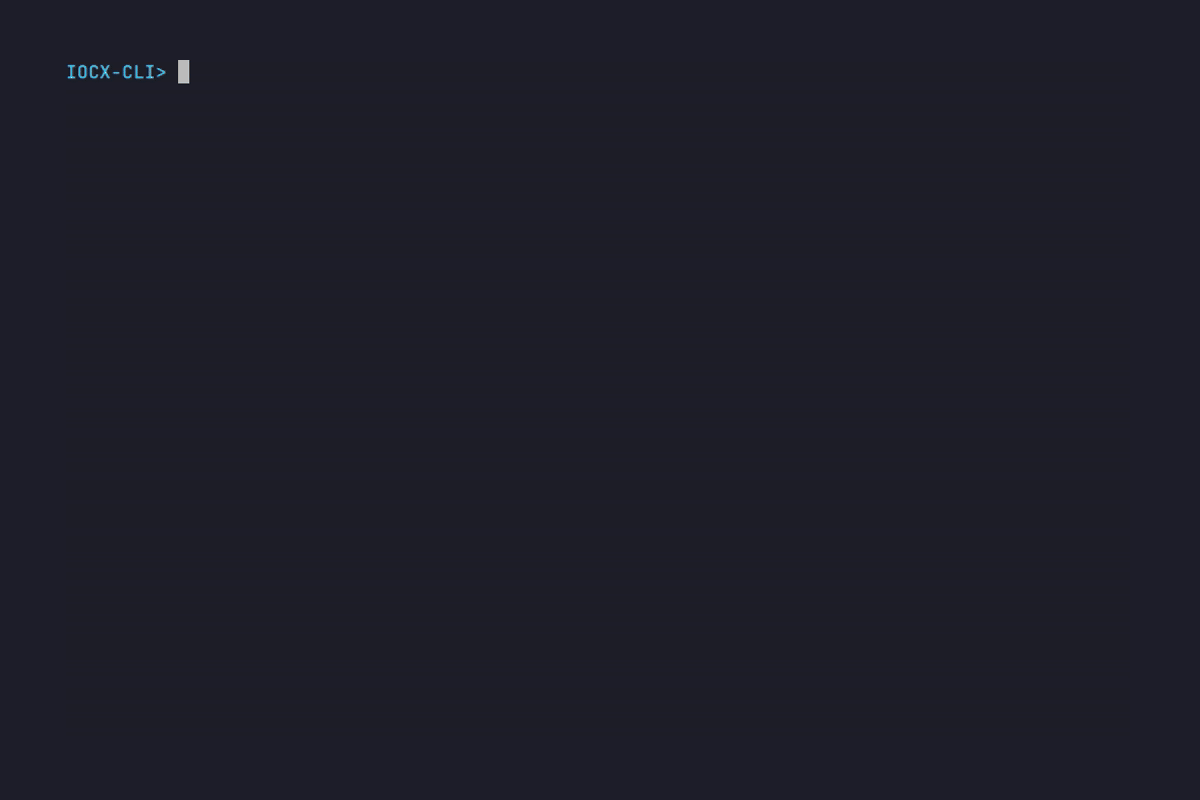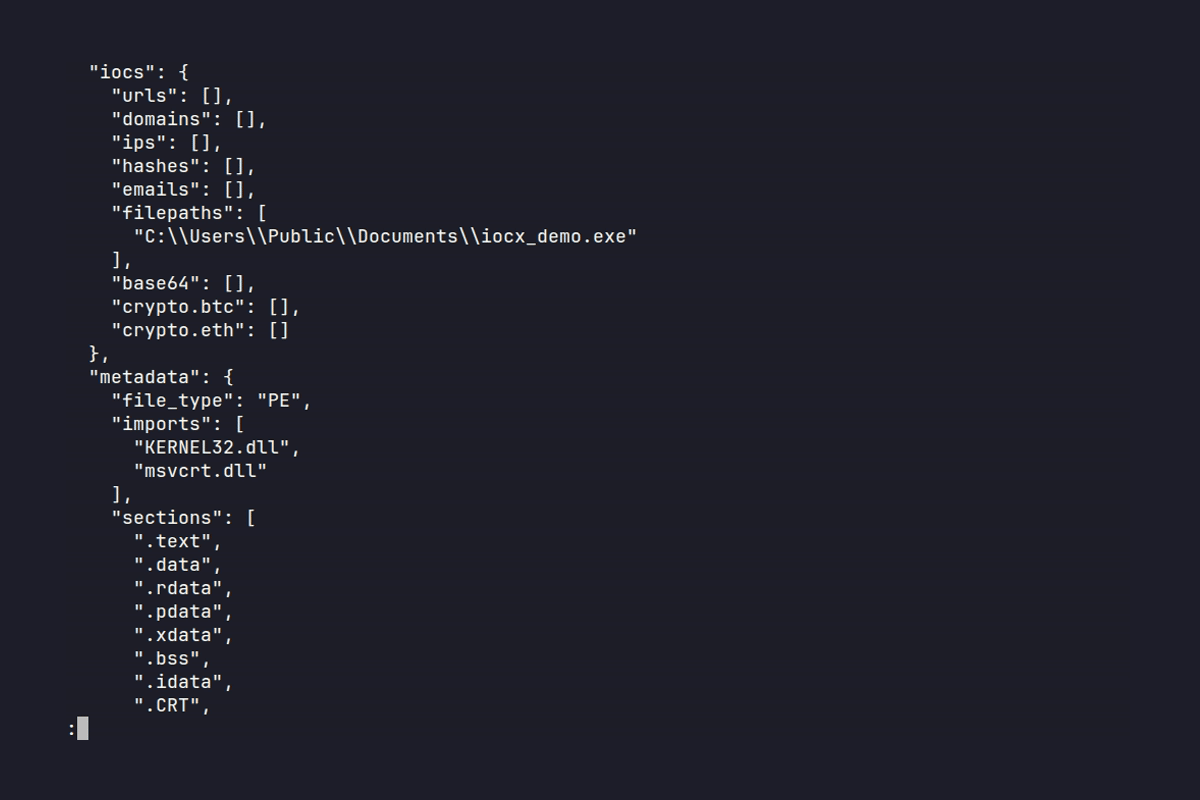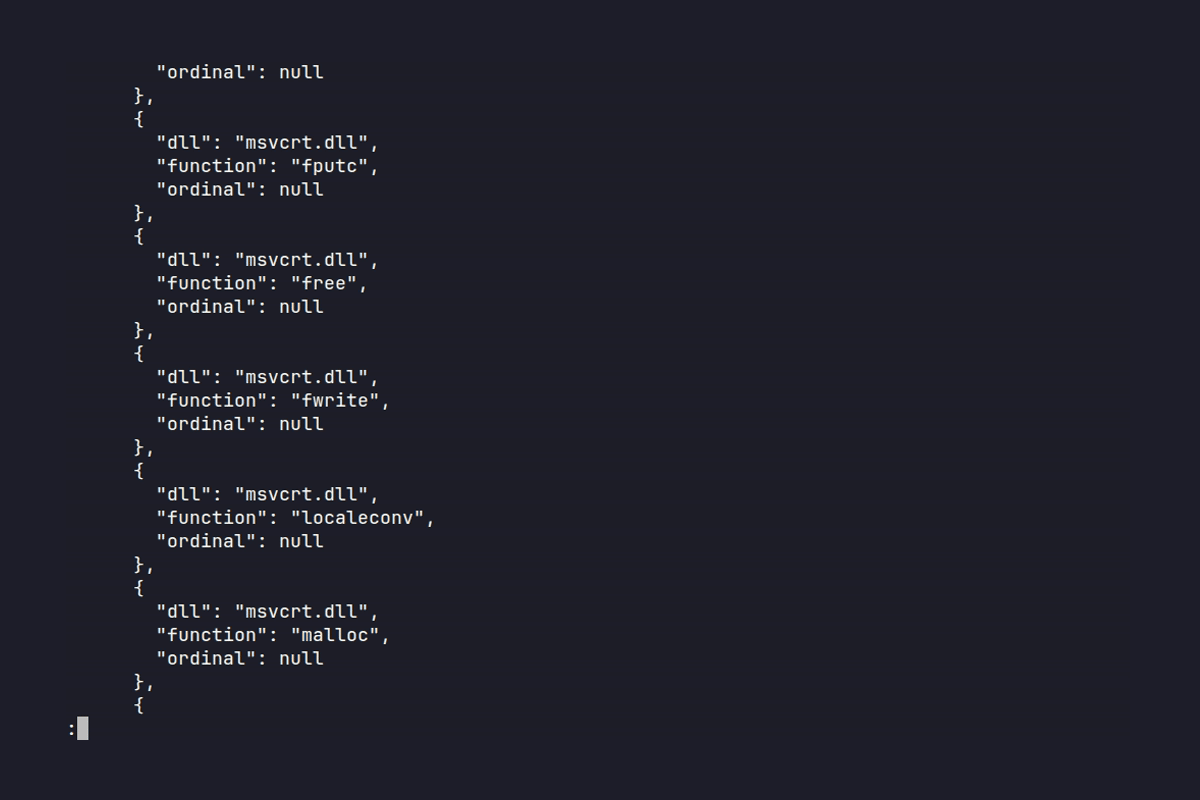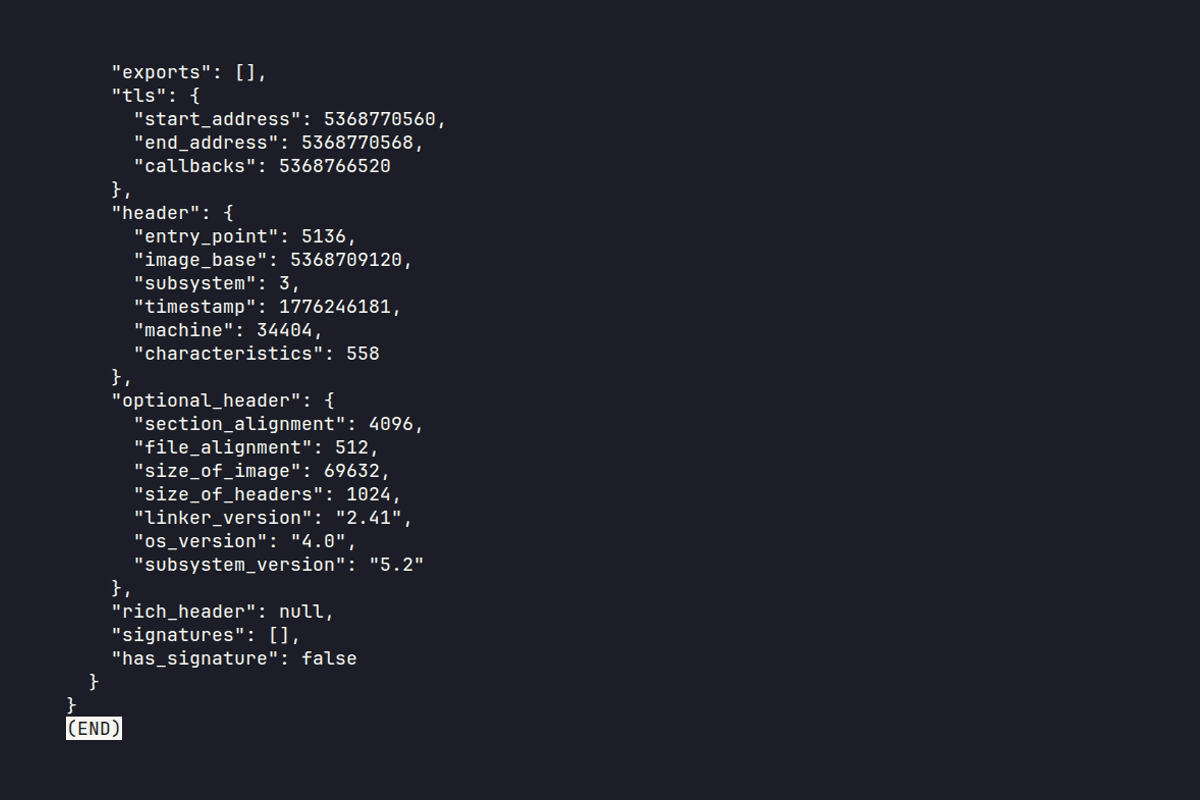 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
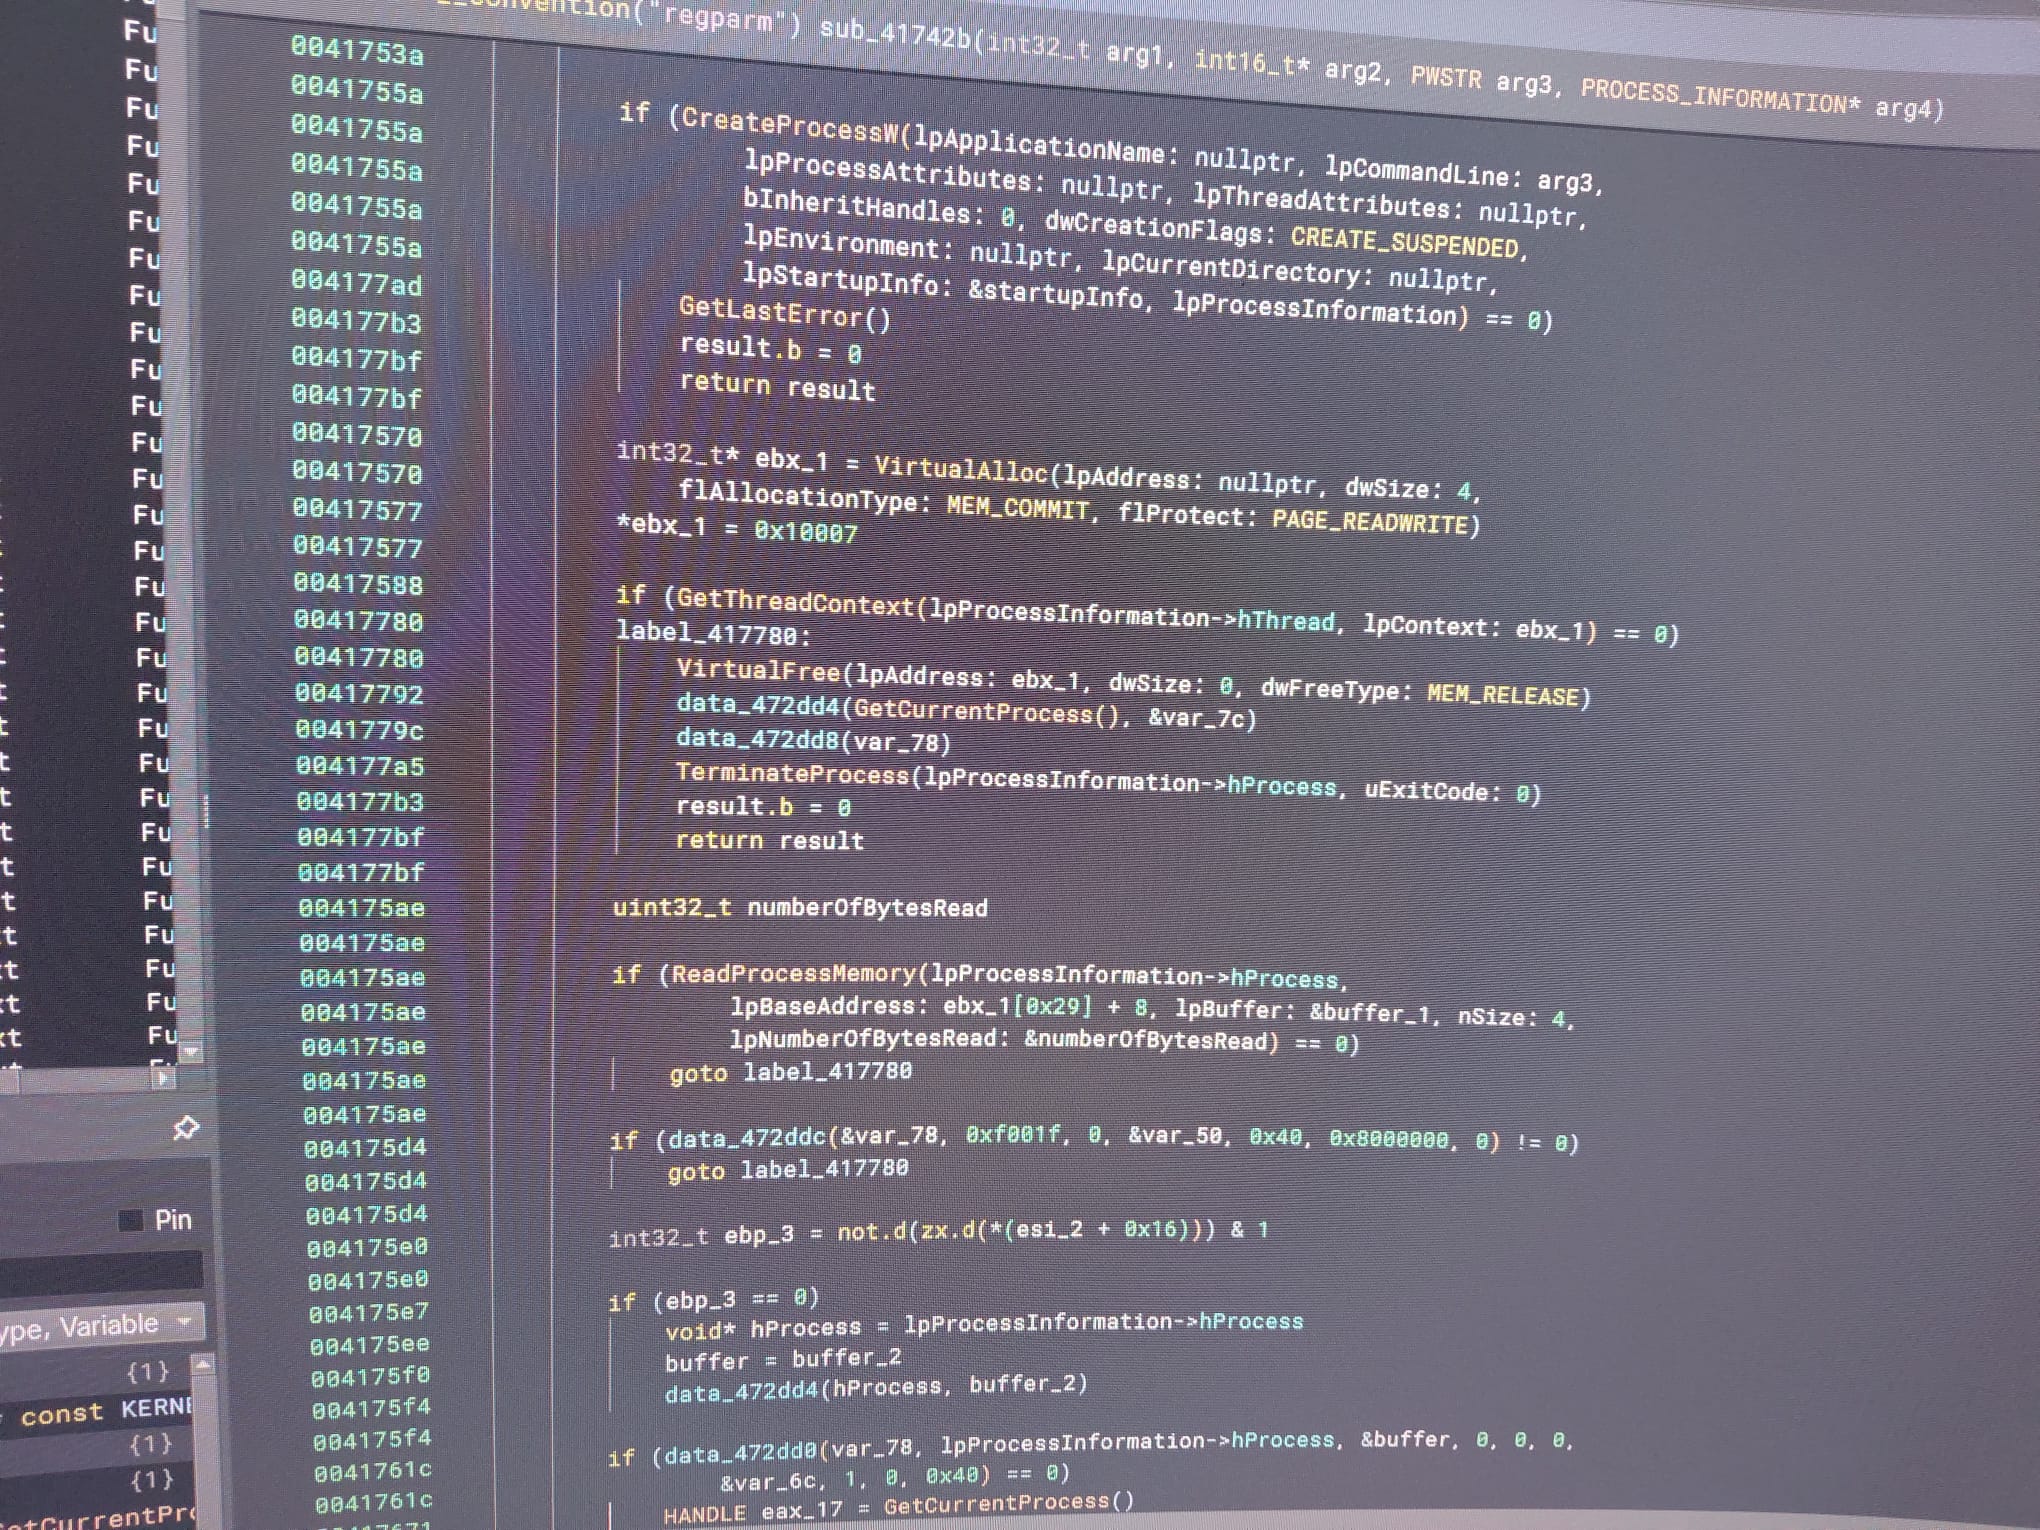 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 tracehound/tracehound
Operational security controls with forensic guarantees
 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
 zardus/ctf-tools
Some setup scripts for security research tools.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩