

ubuntils
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
configuration-auditingdefensive-toolsdigital-forensics+7
5
asmitdesai/ubuntilsPython CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 sebinxavi/cve-checker-2026
Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)
 ngksiva/cpanel-forensics
Форензика после CVE-2026-41940 (cPanel/WHM) — bash-скрипт и чек-лист
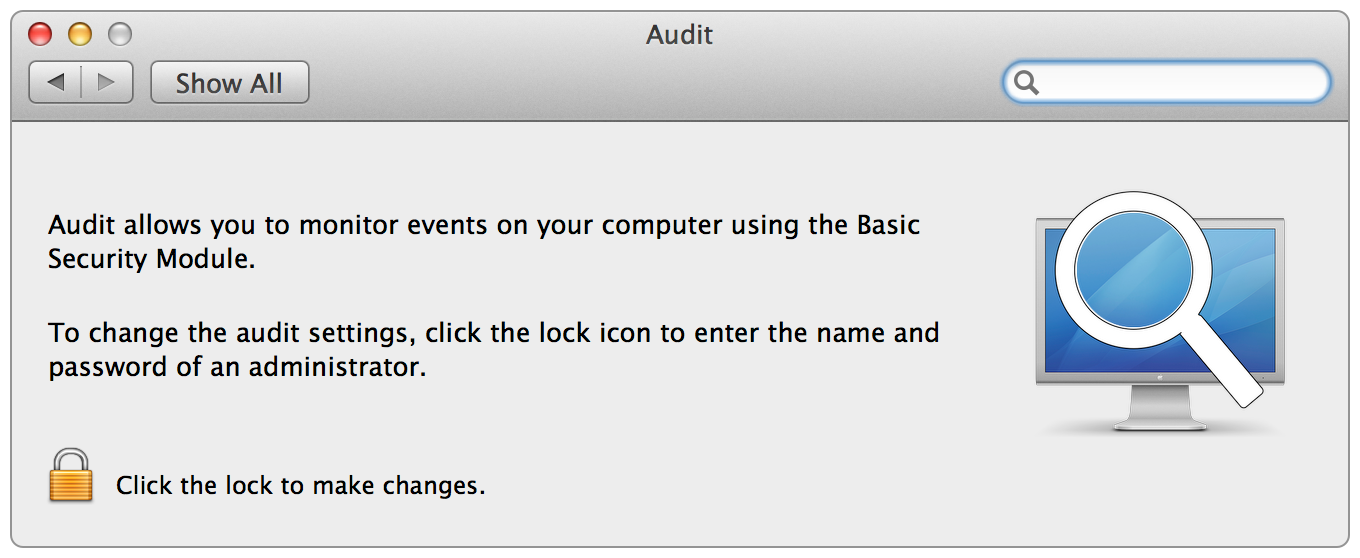 twocanoes/audit
Audit Preference Pane and Log Reader for OS X
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 mahfuzreham/cpanel-cve-2026-41940
cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 verveindustrialprotection/cve-2021-44228-log4j
Provides BigFix Fixlets and analyses to detect Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) across Windows and Linux…
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
 abdom.seada/security-checks
linux security checks
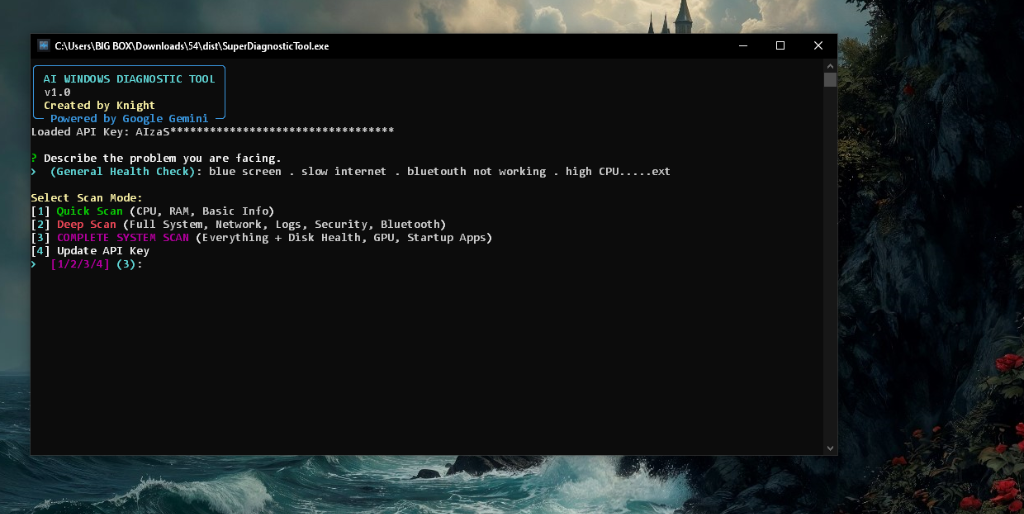 guettaf-hossam/superdiagnostictool
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…
 neo23x0/auditd
Best Practice Auditd Configuration
 resellnom/litespeed-cpanel-cve-2026-54420-fix
Defensive mitigation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel plugin, providing symlink detection, IOC hunting, and remediation…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
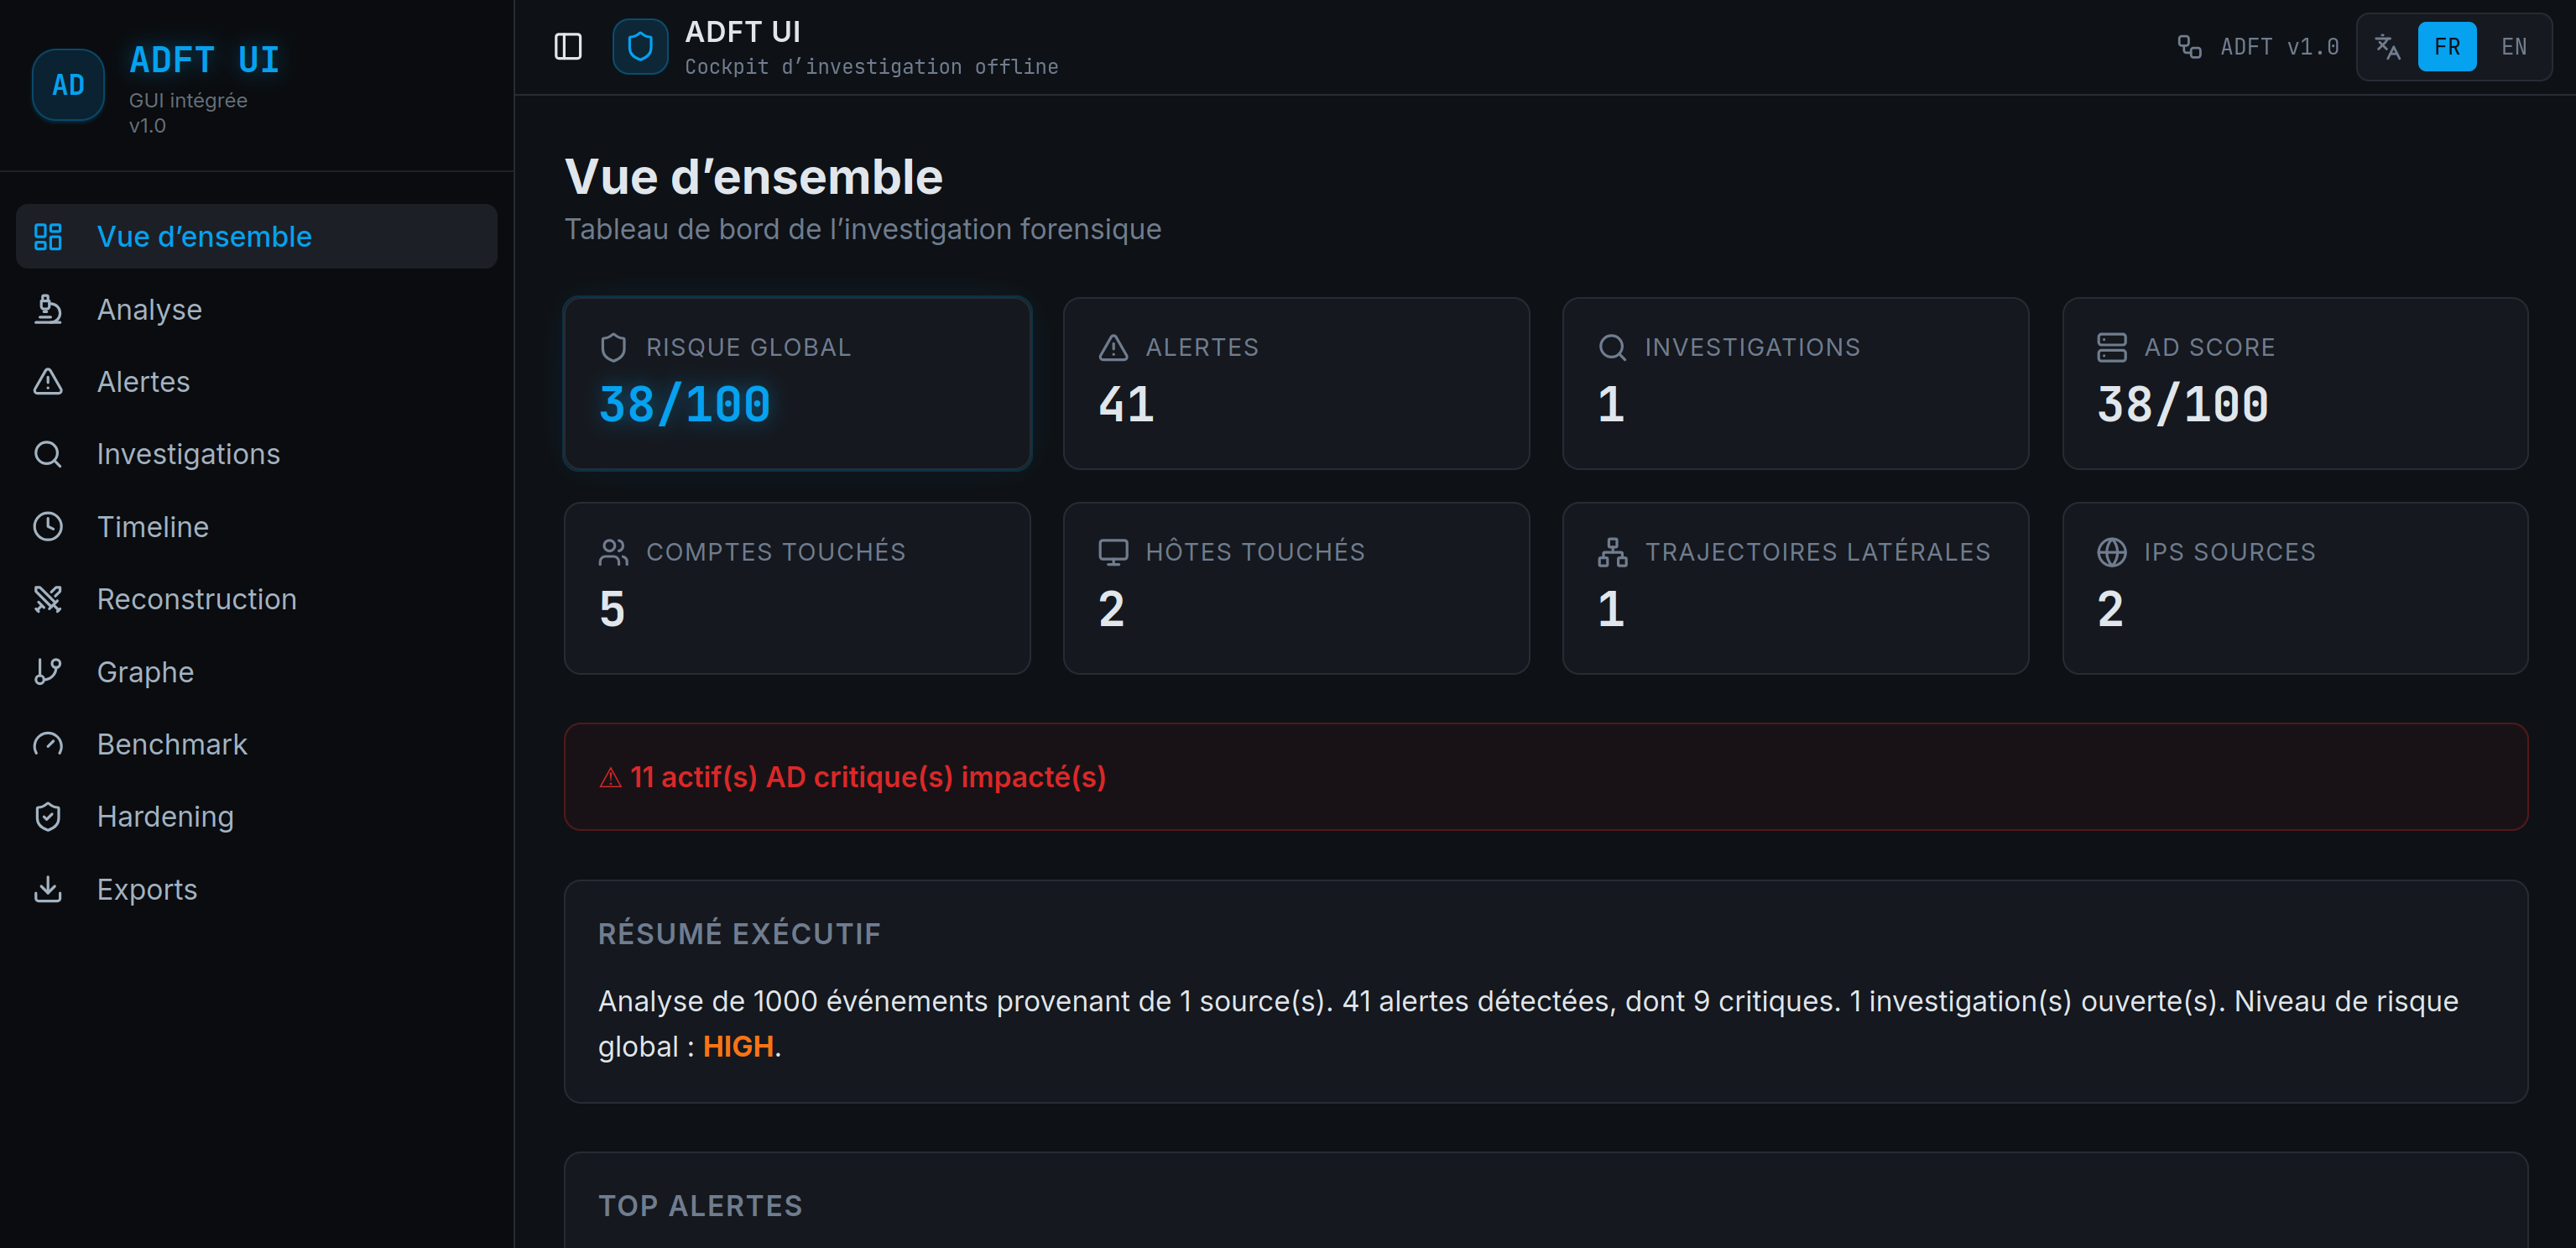 kjean13/adft
Active Directory Forensic Toolkit : Detect & reconstruct AD attacks from Windows event logs (EVTX)