Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

An ArchLinux based distribution for penetration testers and security researchers.

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

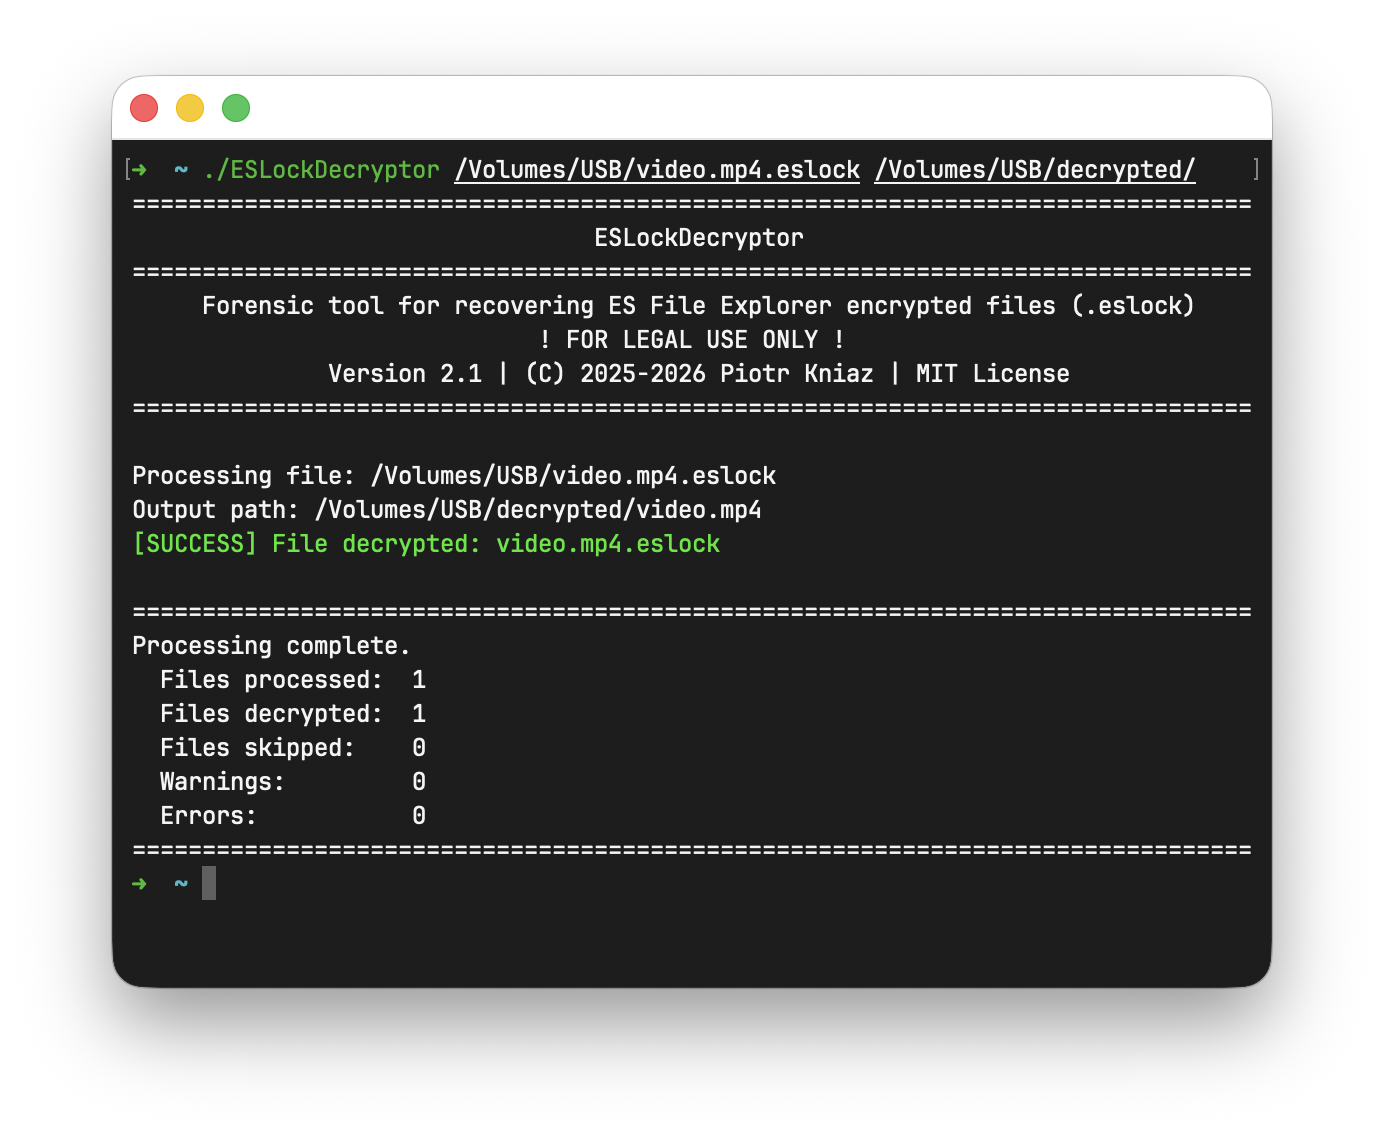
Utility for recovering ES File Explorer encrypted files (.eslock)

Release of the sandy framework.


android location service cache dumper

Linux Distro for Mobile Security, Malware Analysis, and Forensics

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…

Advanced SMB Honeypot: CVE-2025-33073 Research & Implementation

Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…

A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices

CVE-2026-30784: RustDesk hbbs Traffic Amplification PoC & PCAP Analysis

"A single malicious packet can own your device." — Android Security Team, Nov 2025

Poc for CVE-2024-36971

A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…

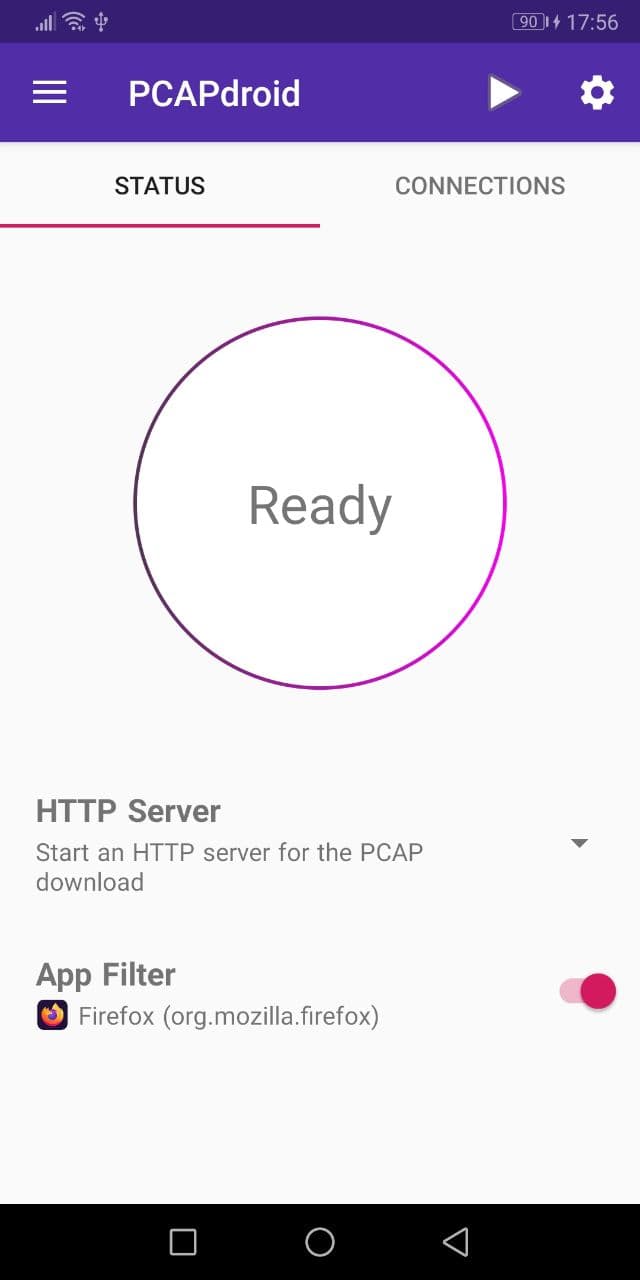
No-root network monitor, firewall and PCAP dumper for Android