
Santoku-Linux
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
android-securitydigital-forensicseducation+6
20712 years ago
santoku/santoku-linuxLinux Distro for Mobile Security, Malware Analysis, and Forensics
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
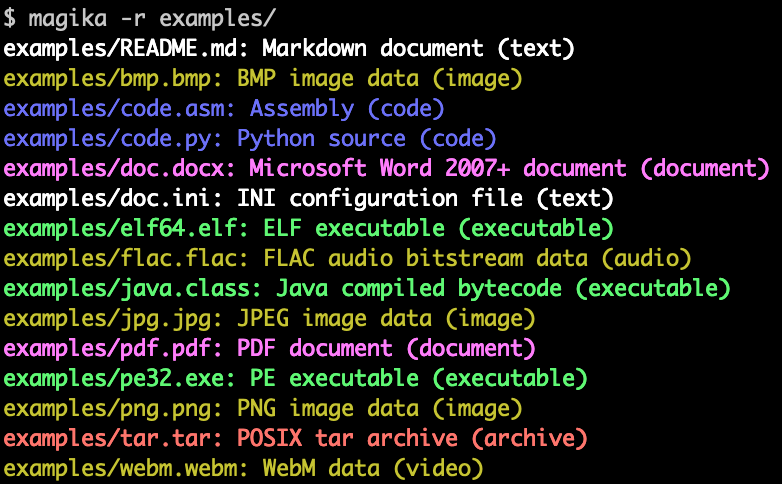 google/magika
Fast and accurate AI powered file content types detection
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
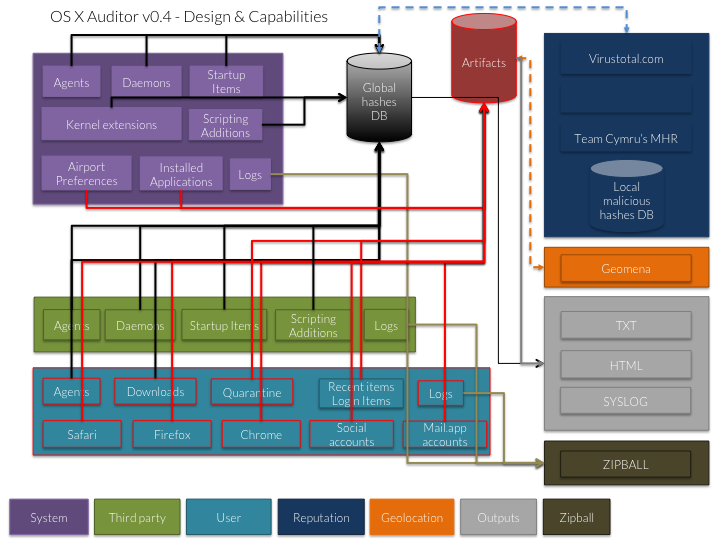 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.