
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
18513 days ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.

digital-forensicsforensicsincident-response+1
384 years ago
Evtx_Log_Browser preview

Evtx_Log_Browser

GitHubkacos2000/evtx_log_browser

Evtx Log (xml) Browser
defensive-toolsdigital-forensicsforensics+2
603 years ago
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

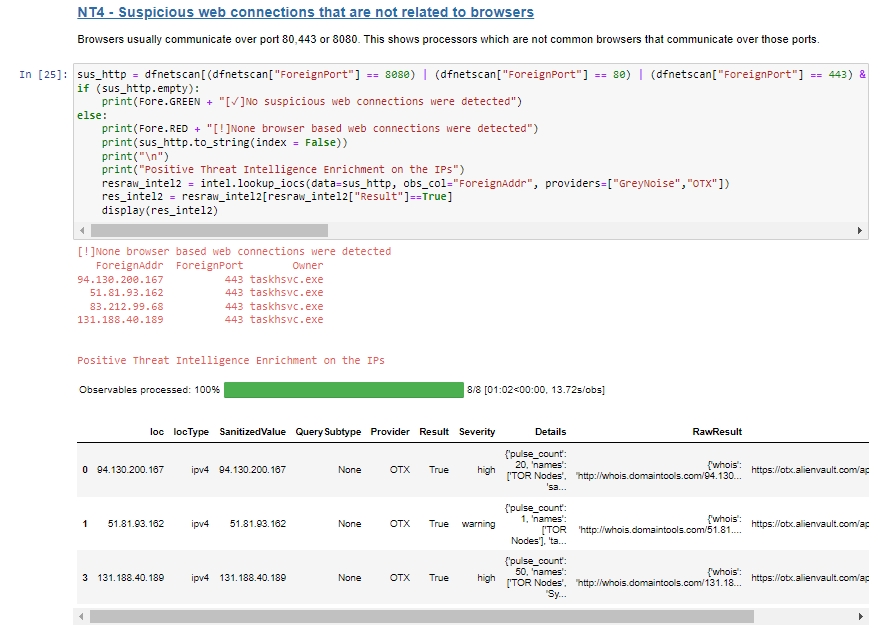
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
digital-forensicsforensicsincident-response+2
983 years ago
ForensiX preview

ForensiX

GitHubtheevidencehunter/forensix

Digital Forensics Intelligence Framework
digital-forensicsdisk-forensicsforensics+4
5 months ago
mt6985-CVE-2026-43499 preview

mt6985-CVE-2026-43499

GitHub233laoliu/mt6985-cve-2026-43499

CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
binary-exploitationexploitationexploit-frameworks+5
21 month ago
sandy preview

sandy

GitHubdonctl/sandy

Release of the sandy framework.
android-securitycryptographyencryption-decryption-tools+5
3911 years ago
awesome-rust-security preview

awesome-rust-security

GitHubosirislab/awesome-rust-security

Curated list of awesome projects and resources related to Rust and computer security
binary-analysiscloud-securitycryptography+9
6062 years ago
UnjailMe preview

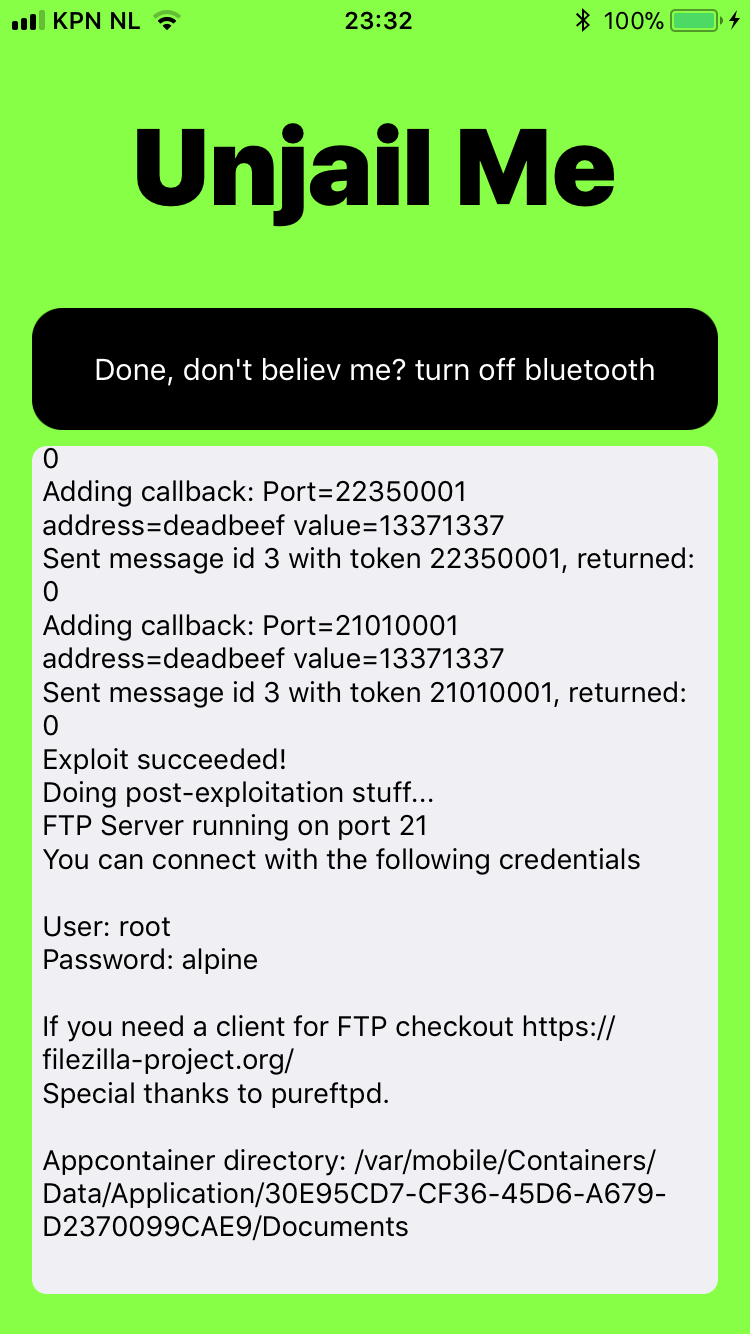
UnjailMe

GitHubmtjailed/unjailme

A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)

binary-exploitationexploitationexploit-frameworks+7
828 years ago
awesome-hacking preview

awesome-hacking

GitHubcarpedm20/awesome-hacking

A curated list of awesome Hacking tutorials, tools and resources

cryptographyctfcurated-resources+6
17.1k2 years ago
CVE-2025-32463 preview

CVE-2025-32463

GitHubdaryllundy/cve-2025-32463

Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
educationexploitationforensics+8
1 year ago
StegoForge preview

StegoForge

GitHubnour833/stegoforge

The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…

cryptographyctfdata-exfiltration+8
5915 months ago
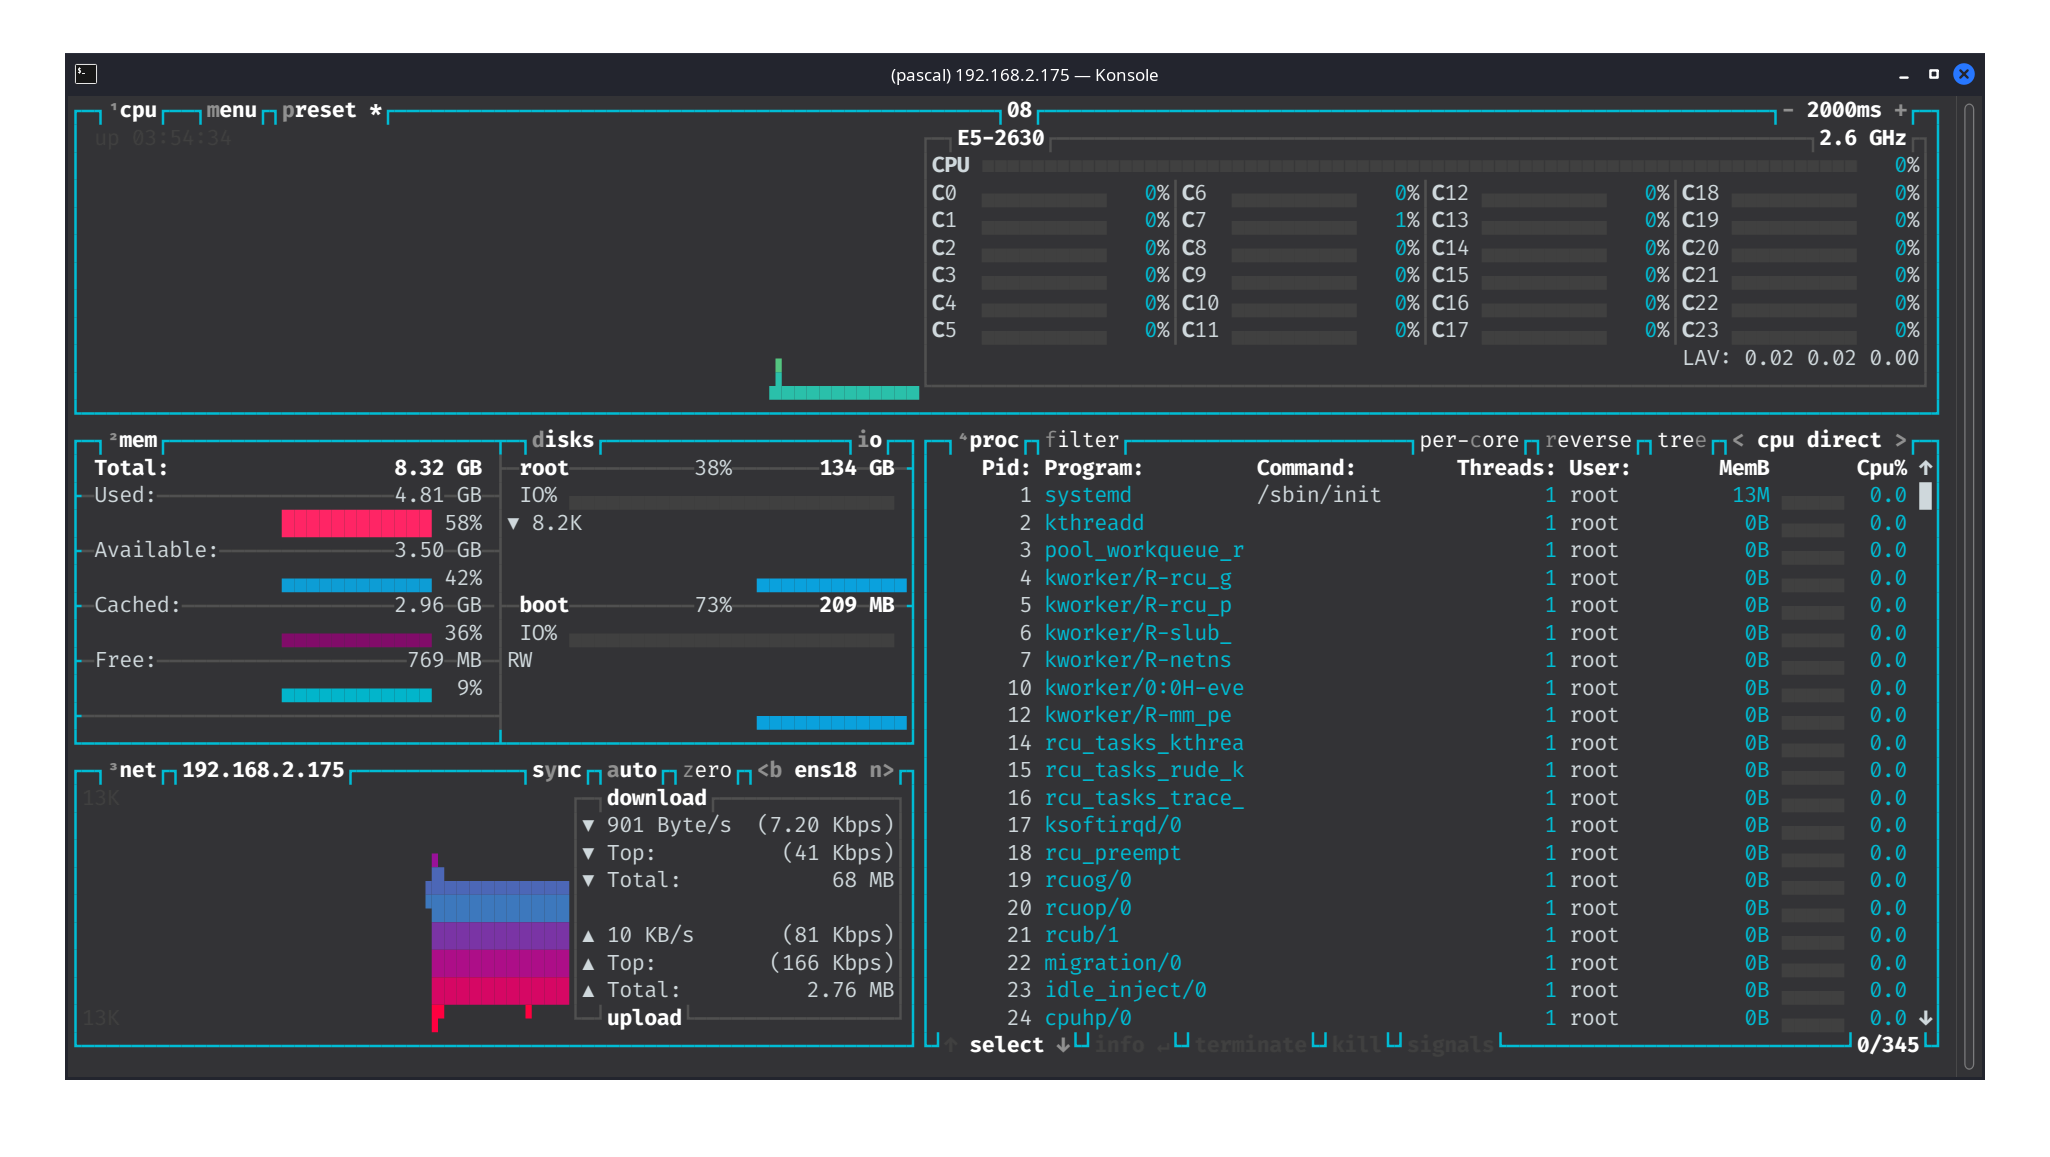
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.4k7 days ago
MagicArch preview

MagicArch

GitLabmagicbytes/magicarch

MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
exploit-frameworksforensicsinformation-gathering+8
22 years ago
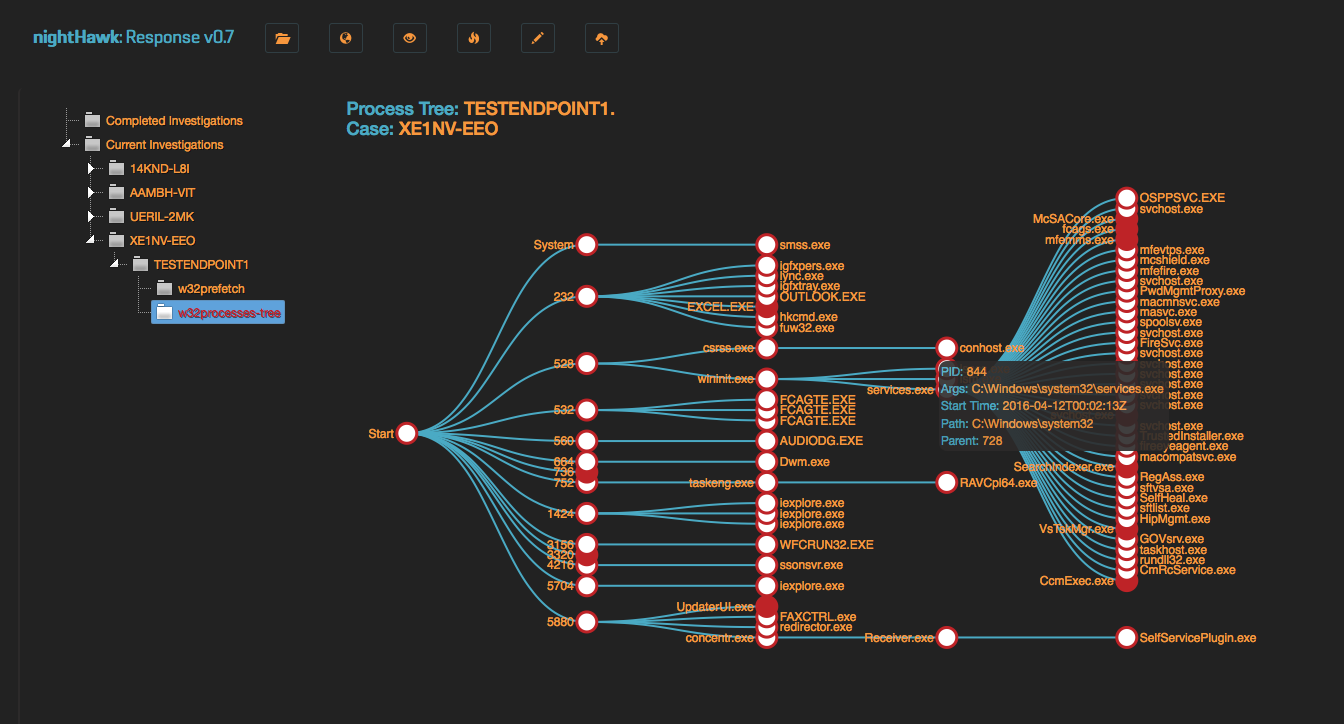
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework

digital-forensicsdisk-forensicsforensics+7
6076 years ago
operative-framework preview

operative-framework

GitHubgraniet/operative-framework

operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
forensicsinformation-gatheringosint+1
7511 year ago
python-haystack preview

python-haystack

GitHubtrolldbois/python-haystack

Process heap analysis framework - Windows/Linux - record type inference and forensics
binary-analysisdigital-forensicsforensics+2
959 years ago
CapTipper preview

CapTipper

GitHubomriher/captipper

Malicious HTTP traffic explorer

digital-forensicsexploit-frameworksforensics+5
7265 years ago
Previous123Next