
chainsaw
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
withsecureopensource/chainsawRapidly Search and Hunt through Windows Forensic Artefacts
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 mfarshad-abdullah-khan/cve-2025-53770-research
🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…
 psypanda/hashid
Software to identify the different types of hashes -
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
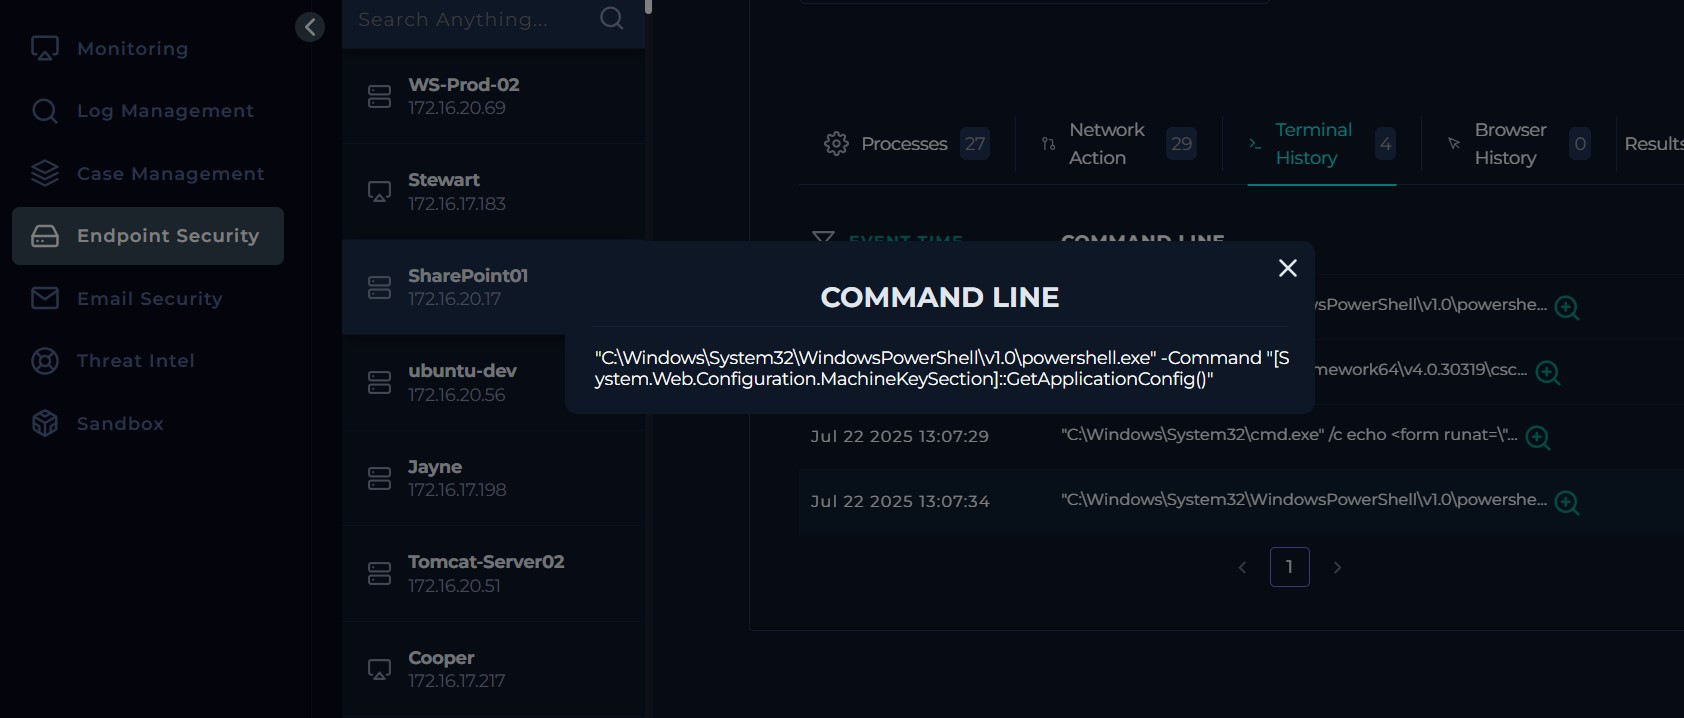 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
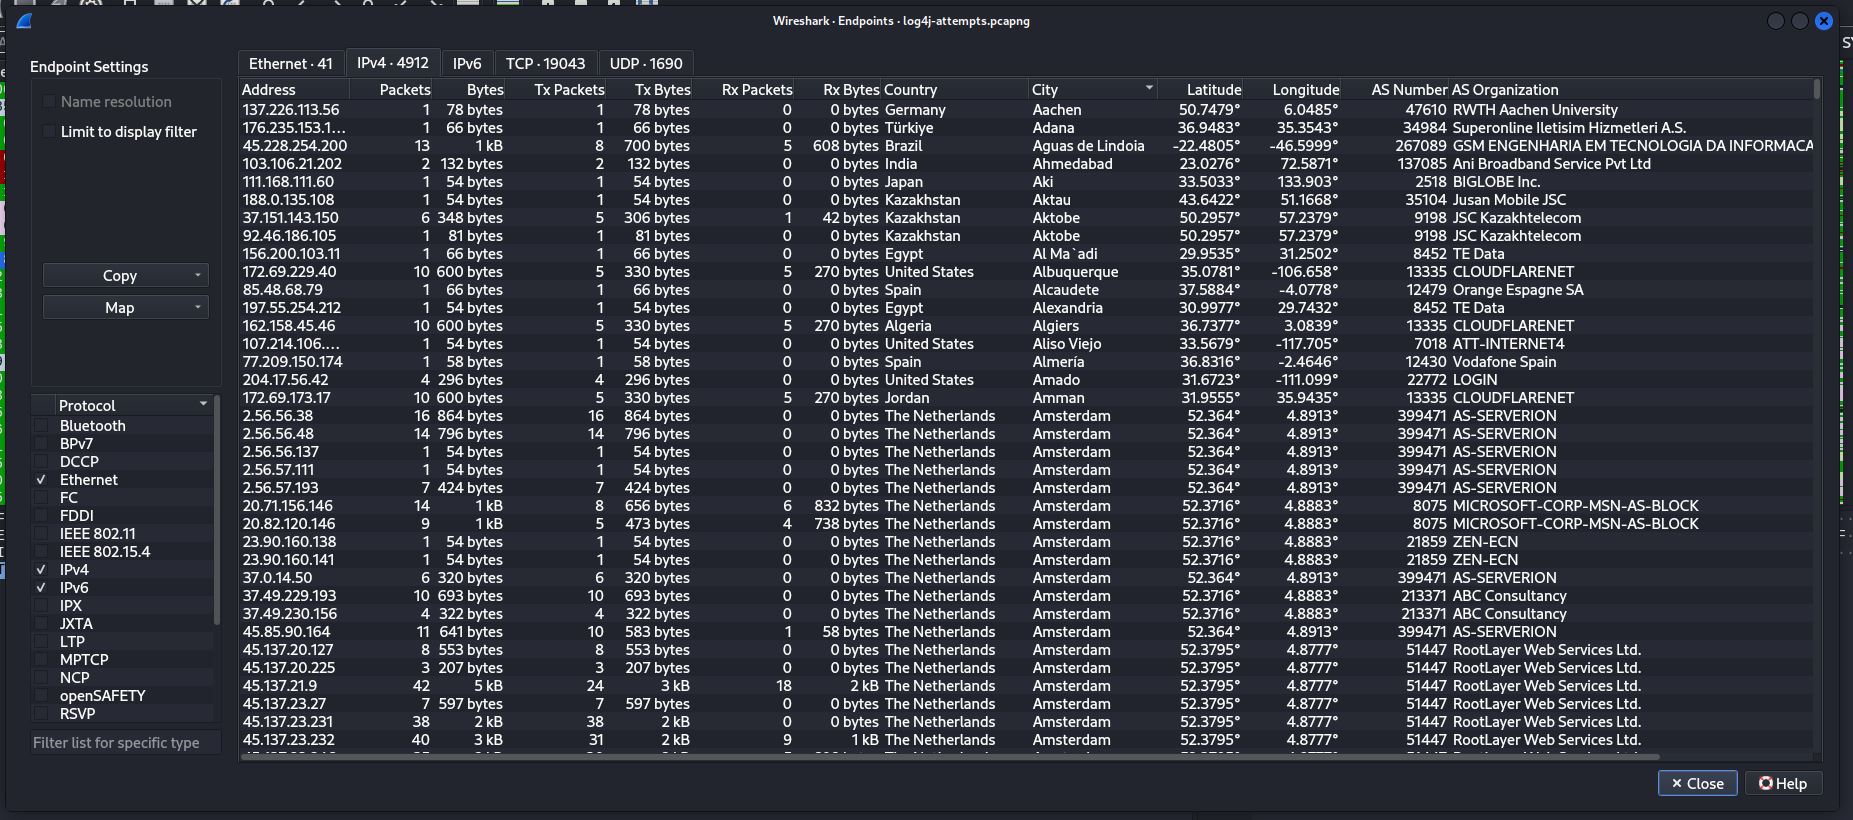 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 nkopylov/tanscript-exploit-check
IOC checker for the TanStack/Mini Shai-Hulud npm supply chain attack (CVE-2026-45321)
 iyargross/smb-cve-2025-33073
Advanced SMB Honeypot: CVE-2025-33073 Research & Implementation
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…

 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability