

BogusMips
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
ai-assisted-reversingandroid-securitybinary-analysis+8
4
jankammerath/bogusmipsForensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
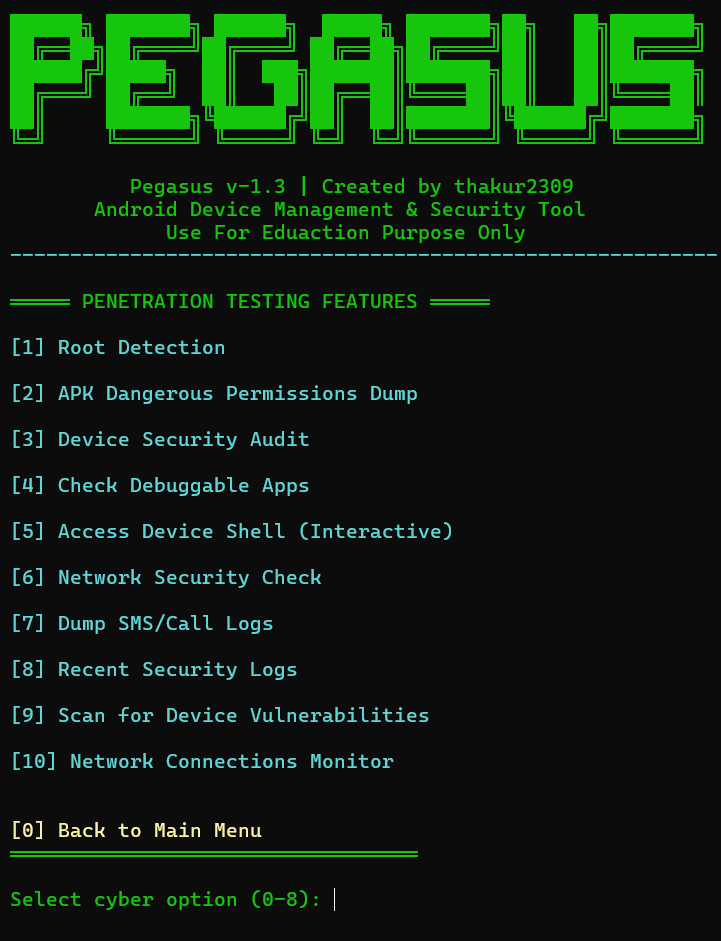 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 donctl/sandy
Release of the sandy framework.

 packetlss/android-locdump
android location service cache dumper
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 nictjh/threatdemos
Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…
 iyargross/smb-cve-2025-33073
Advanced SMB Honeypot: CVE-2025-33073 Research & Implementation
 thieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm
Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 malejdj/cve-2026-30784-rustdesk-poc
CVE-2026-30784: RustDesk hbbs Traffic Amplification PoC & PCAP Analysis