

TryHack3M-Bricks-Heist
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
ctfdigital-forensicseducation+5
anjai7/tryhack3m-bricks-heistTryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 yosasasutsut/blackash-cve-2025-53770
Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability
 vdohney/keepass-password-dumper
Original PoC for CVE-2023-32784
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
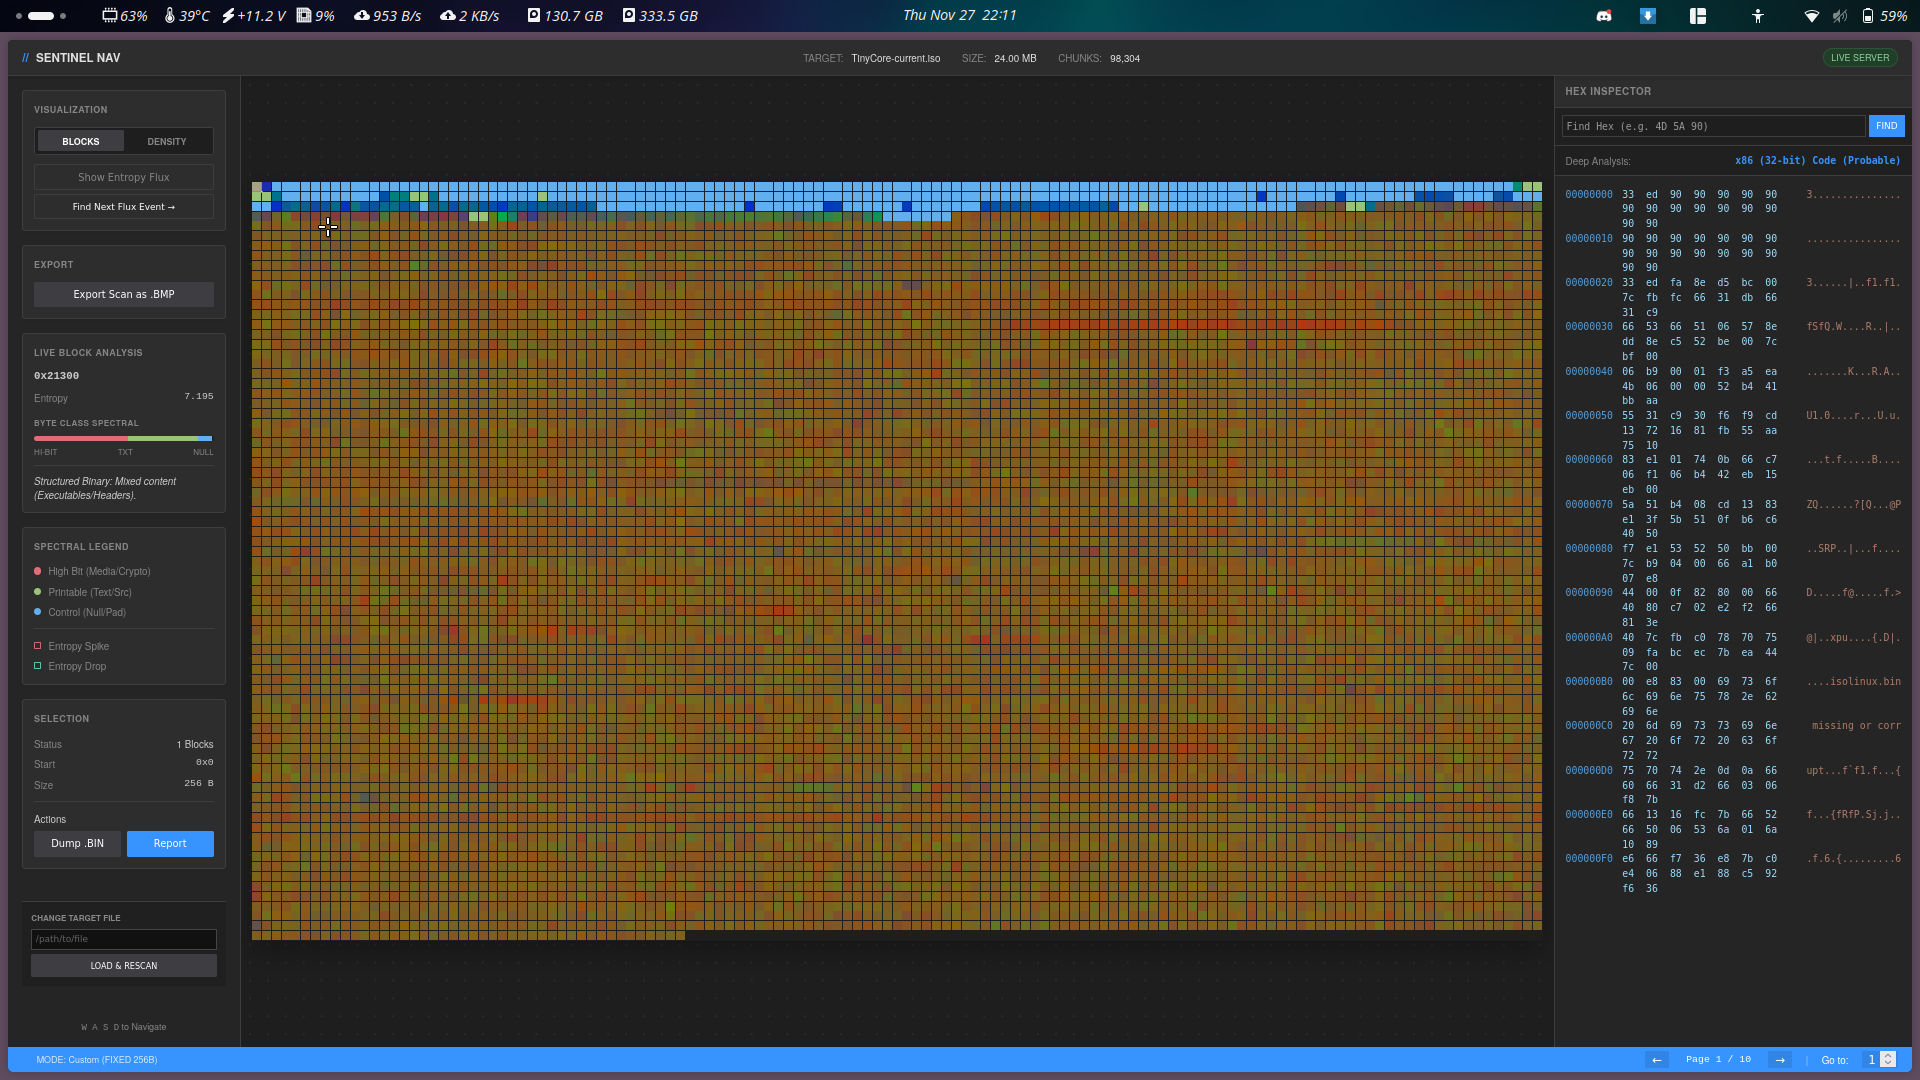 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber
 lordofpipes/acropadetect
Browser-based tool to detect Acropalypse (CVE-2023-21036) by analyzing PNG/GIF images for truncated pixel data, enabling quick vulnerability…
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
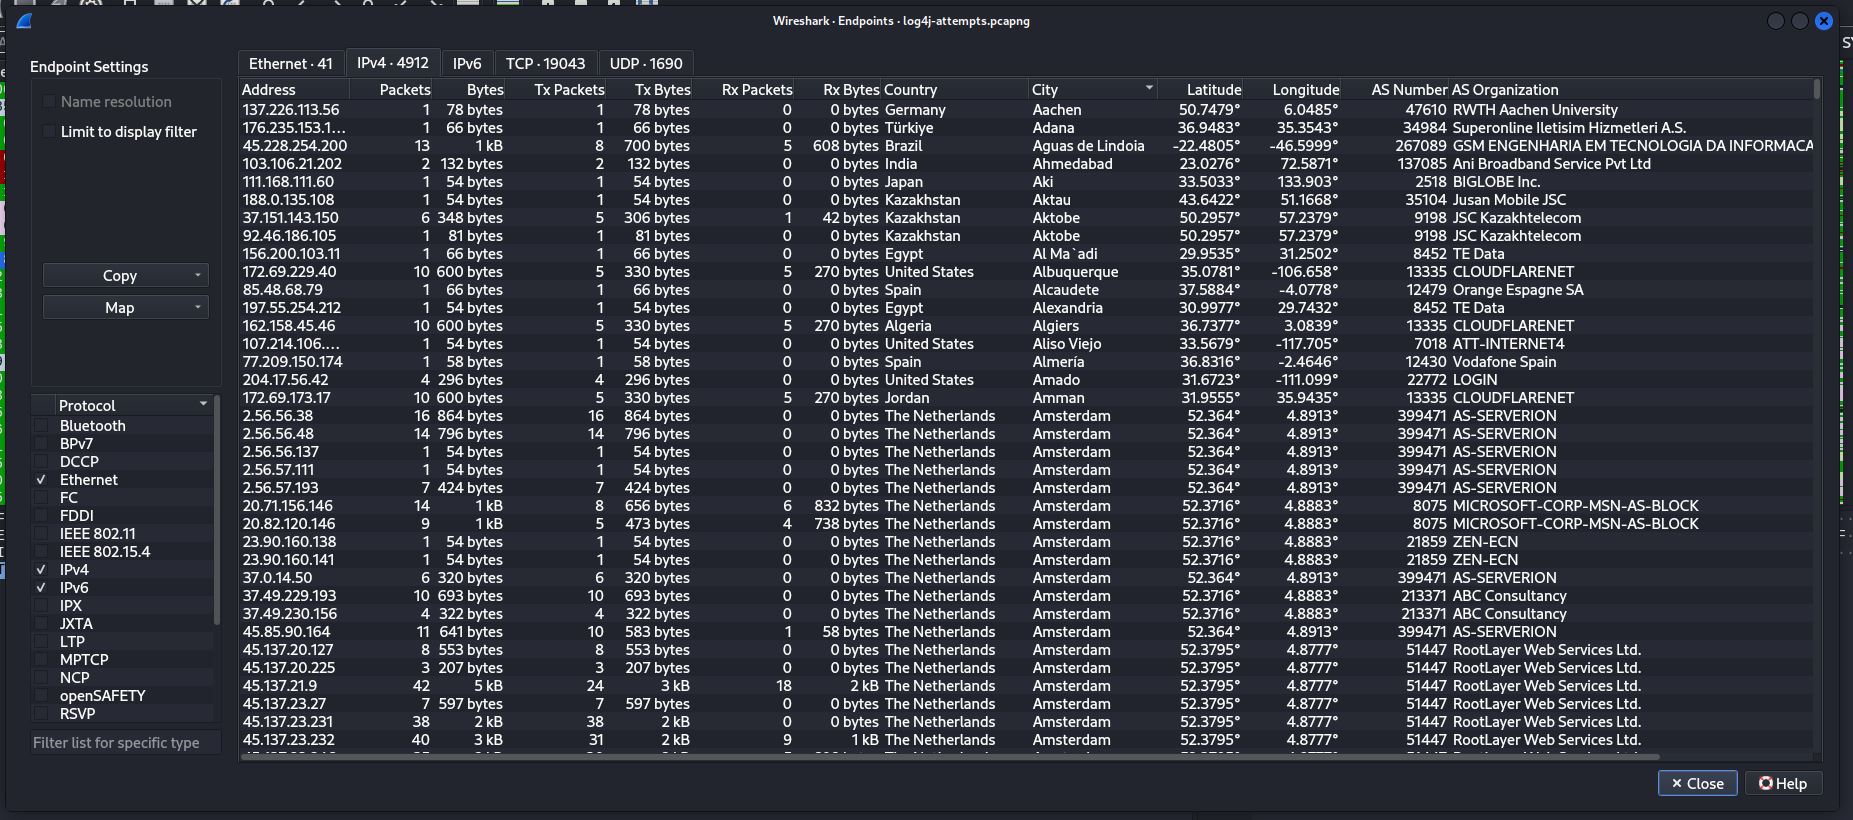 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 garethmsheldon/fortinet-fortiweb-fabric-connector-cve-2025-25257-detection
This repository provides production-ready detection engineering content for **CVE-2025-25257**, a pre-authentication SQL Injection vulnerability in…
 vdisec/cve-2019-19871-auditguide
Audit Guide for the Citrix ADC Vulnerability CVE-2019-19871. Collected from multiple sources and threat assessments. Will be updated as new methods…
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 atlas-ghostshell/cve-2025-27558_patching
Patching CVE-2025-27558 vulnerability that had affected my linux image.
 markuta/bw-dump
A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…