prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Dshell is a network forensic analysis framework.

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

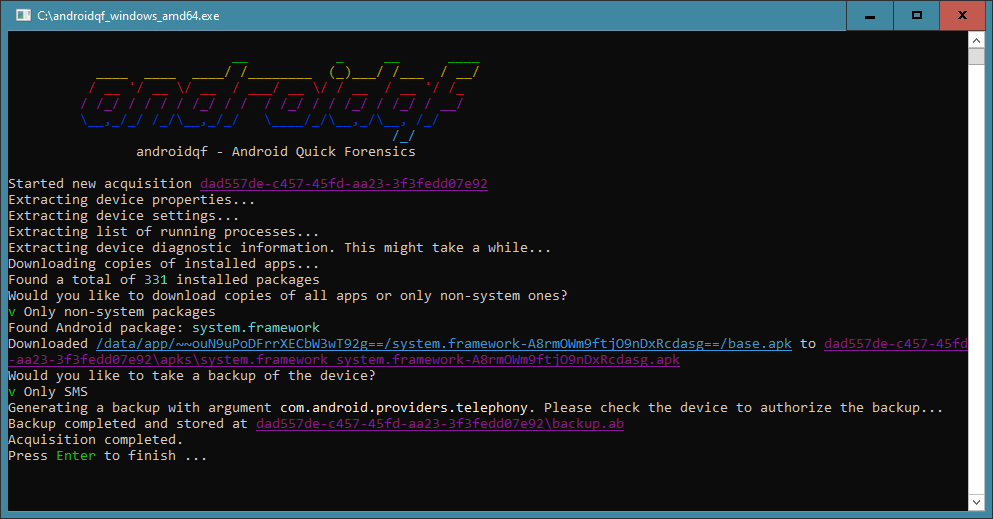
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done

ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.

A command line tool for pstree-like output on macOS with additional pid capturing capabilities

CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865


Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs