

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
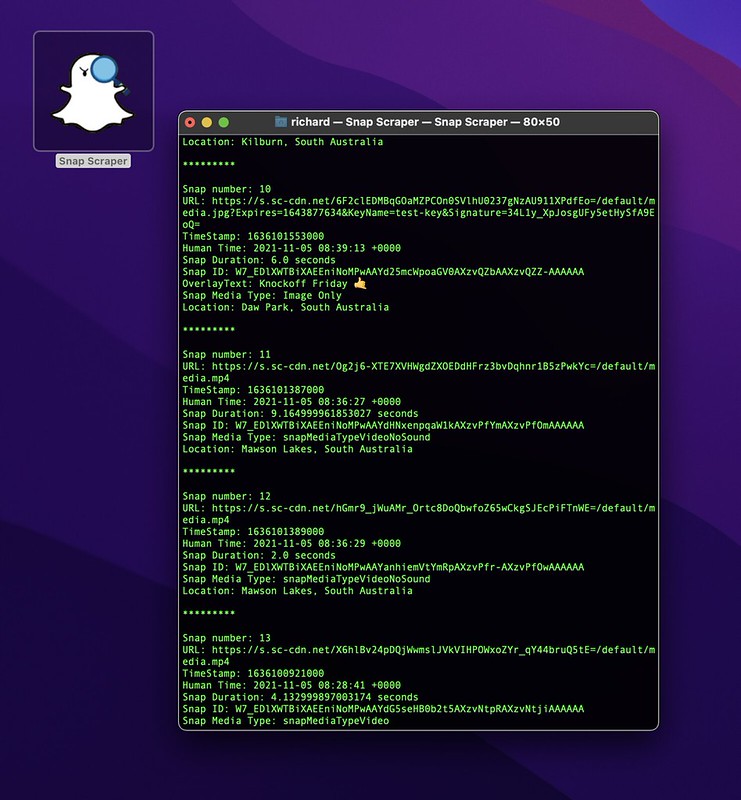 rhematt/snap-scraper
Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.
 neo23x0/auditd
Best Practice Auditd Configuration
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 stealth/psc
E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
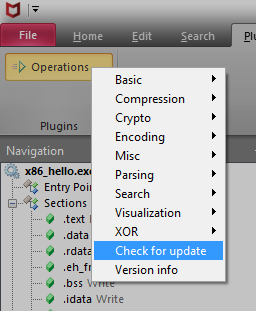 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections