
QLOG
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
defensive-toolsforensicsincident-response+1
44
threathunters-io/qlogETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
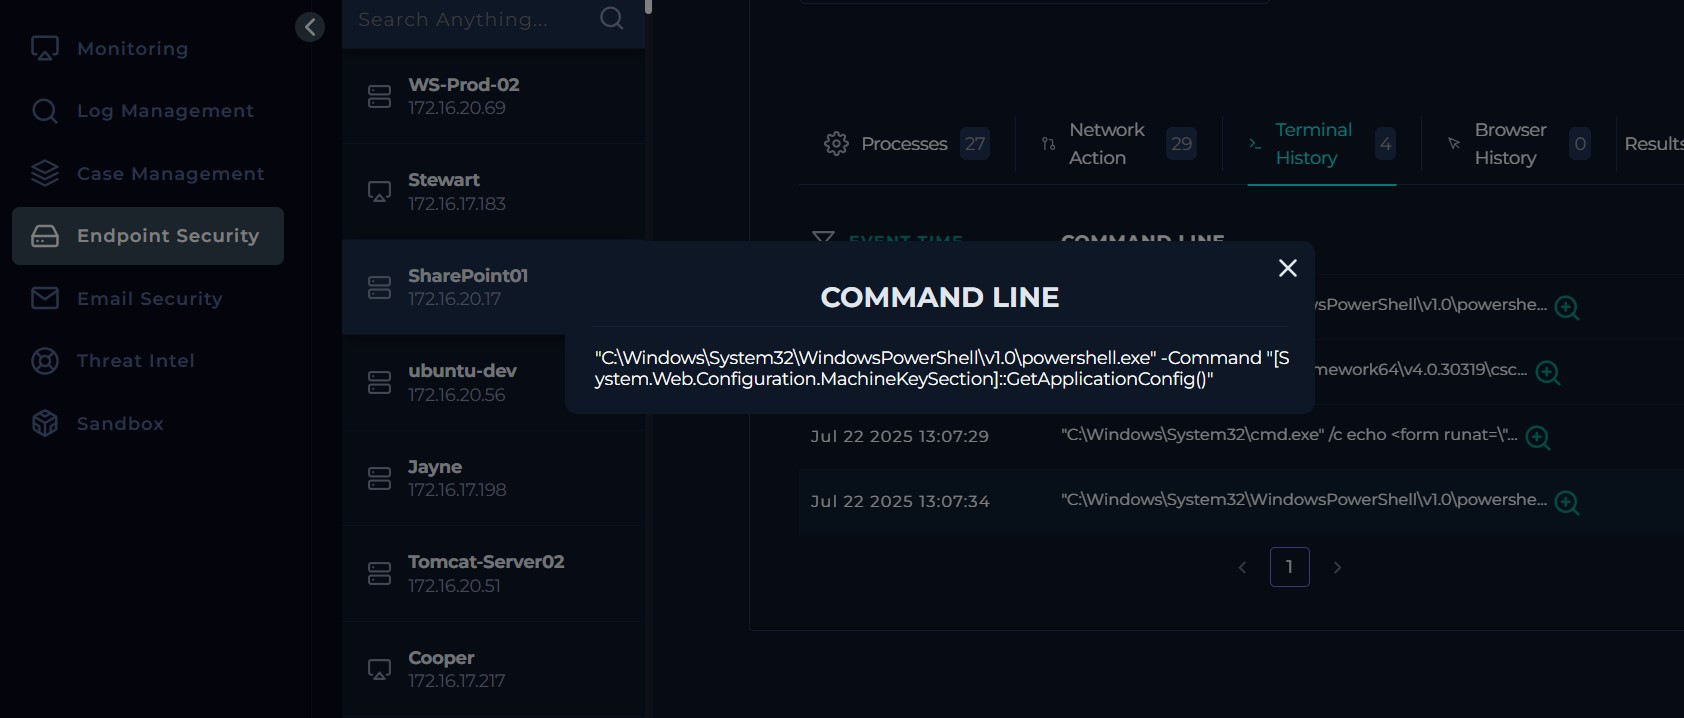 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…