
pefile
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k
erocarrera/pefilepefile is a Python module to read and work with PE (Portable Executable) files
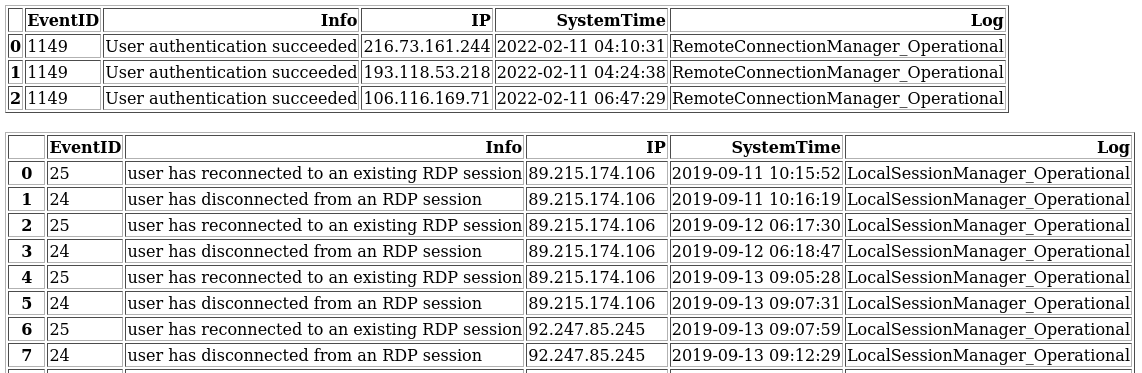 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
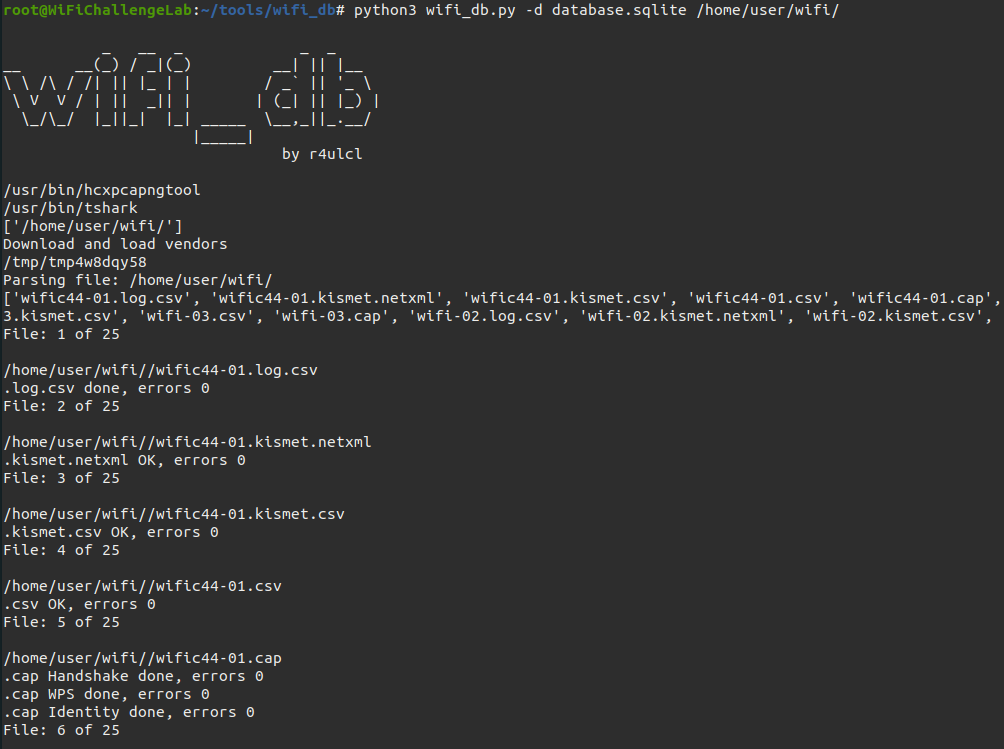 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
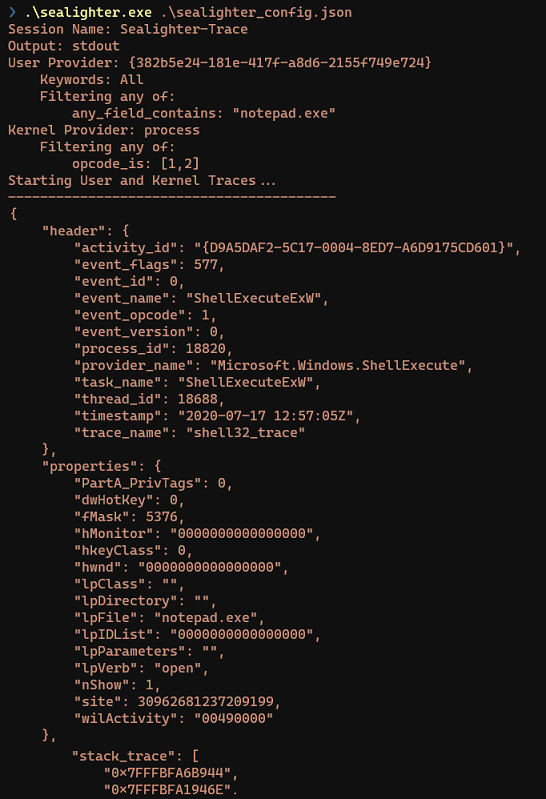 pathtofile/sealighter
ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
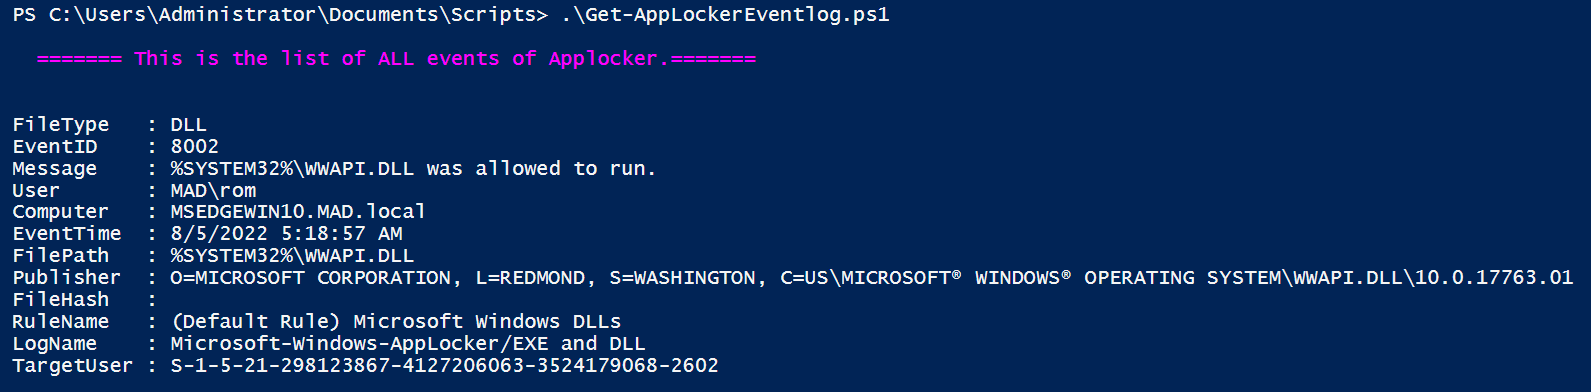 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
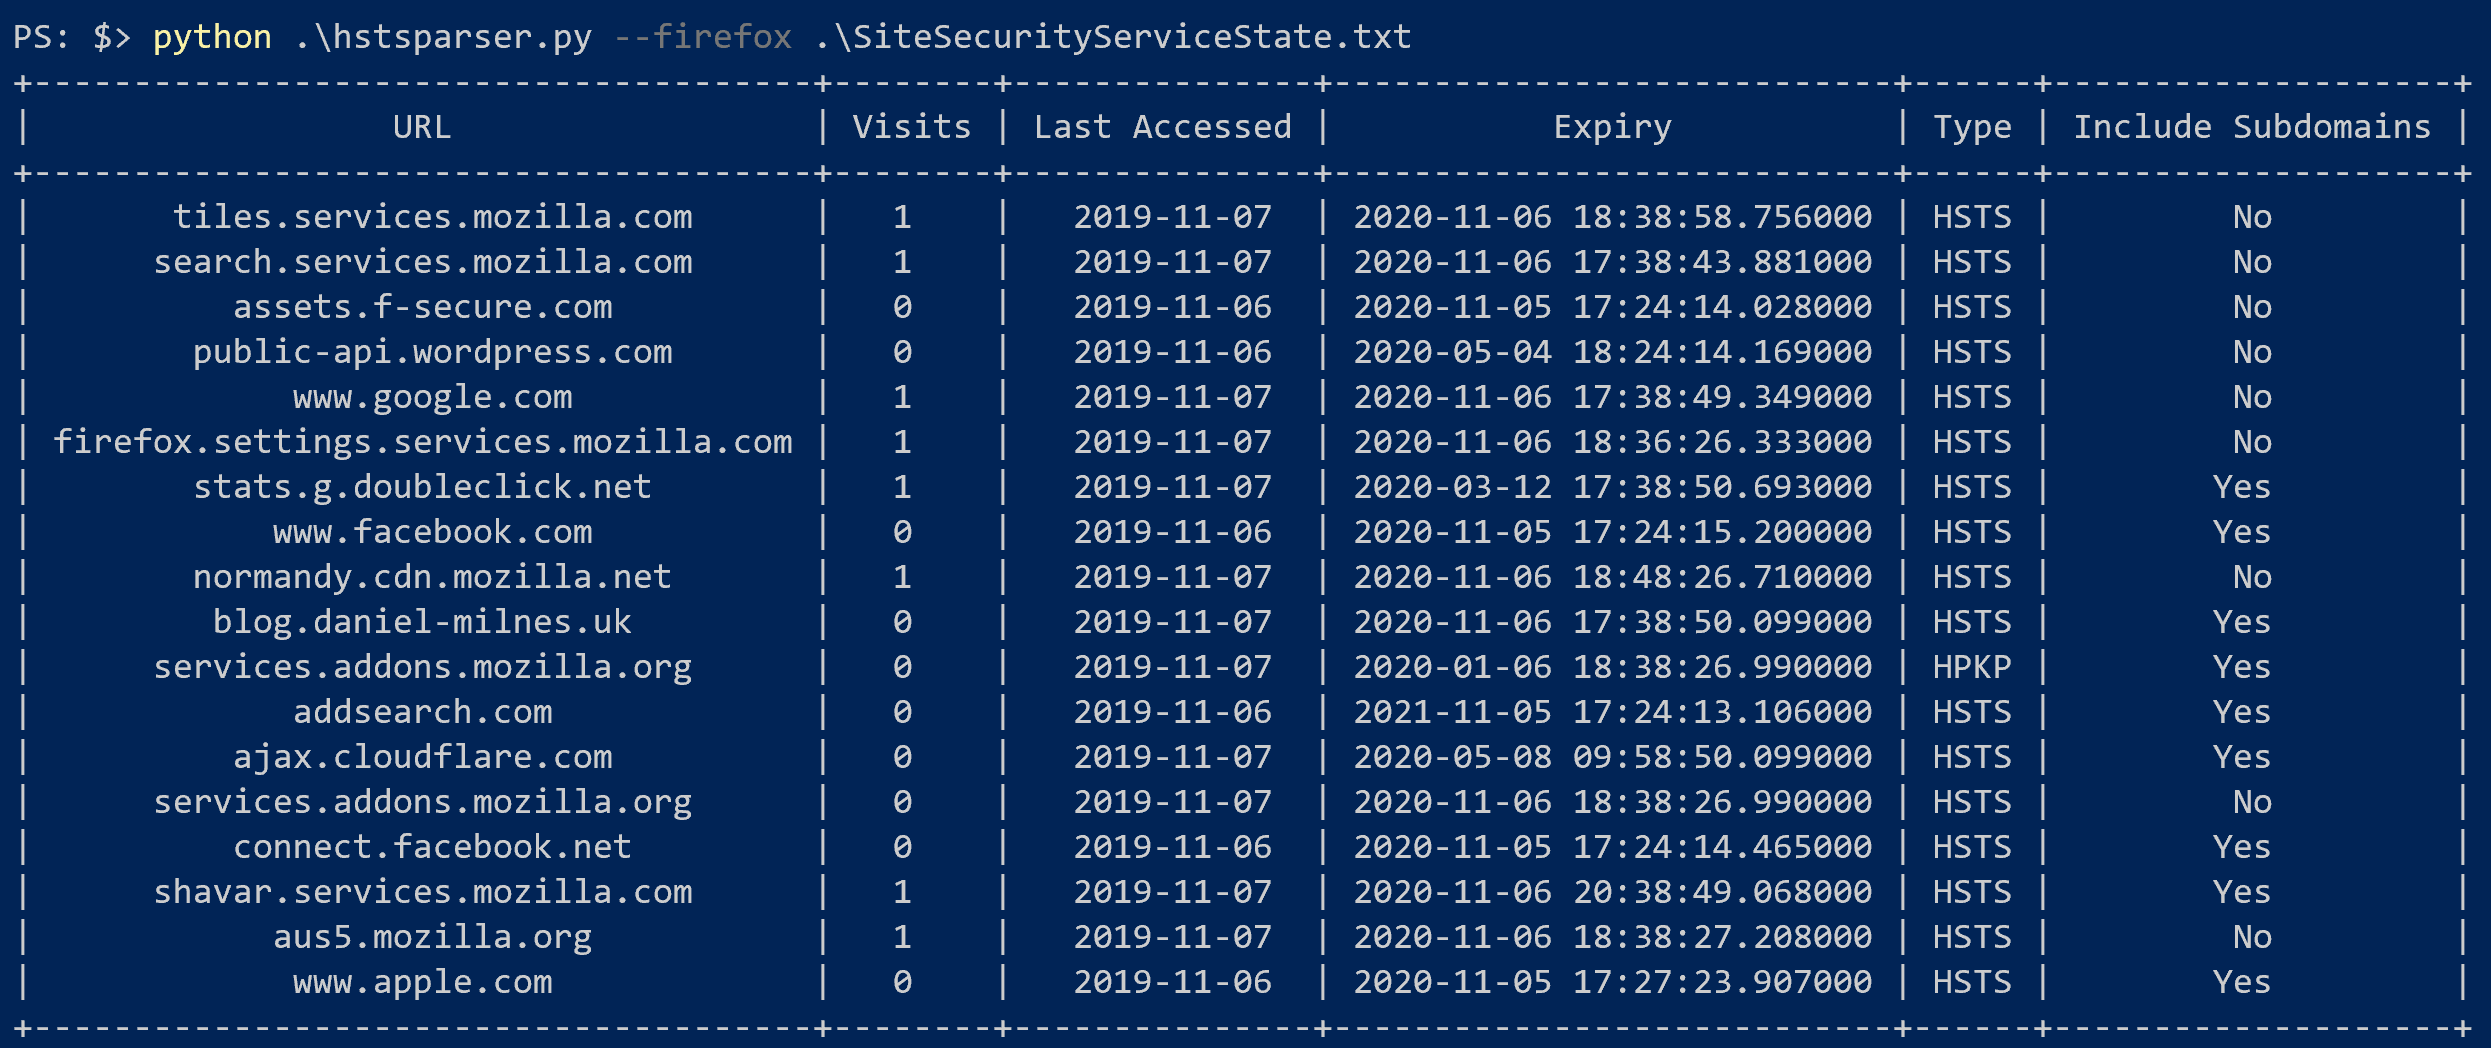 thebeanogamer/hstsparser
A tool to parse Firefox and Chrome HSTS databases into forensic artifacts!