

IPA
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
binary-analysisdefensive-toolsdigital-forensics+6
884
seekbytes/ipaGUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
 patrickdw123/paranoidf
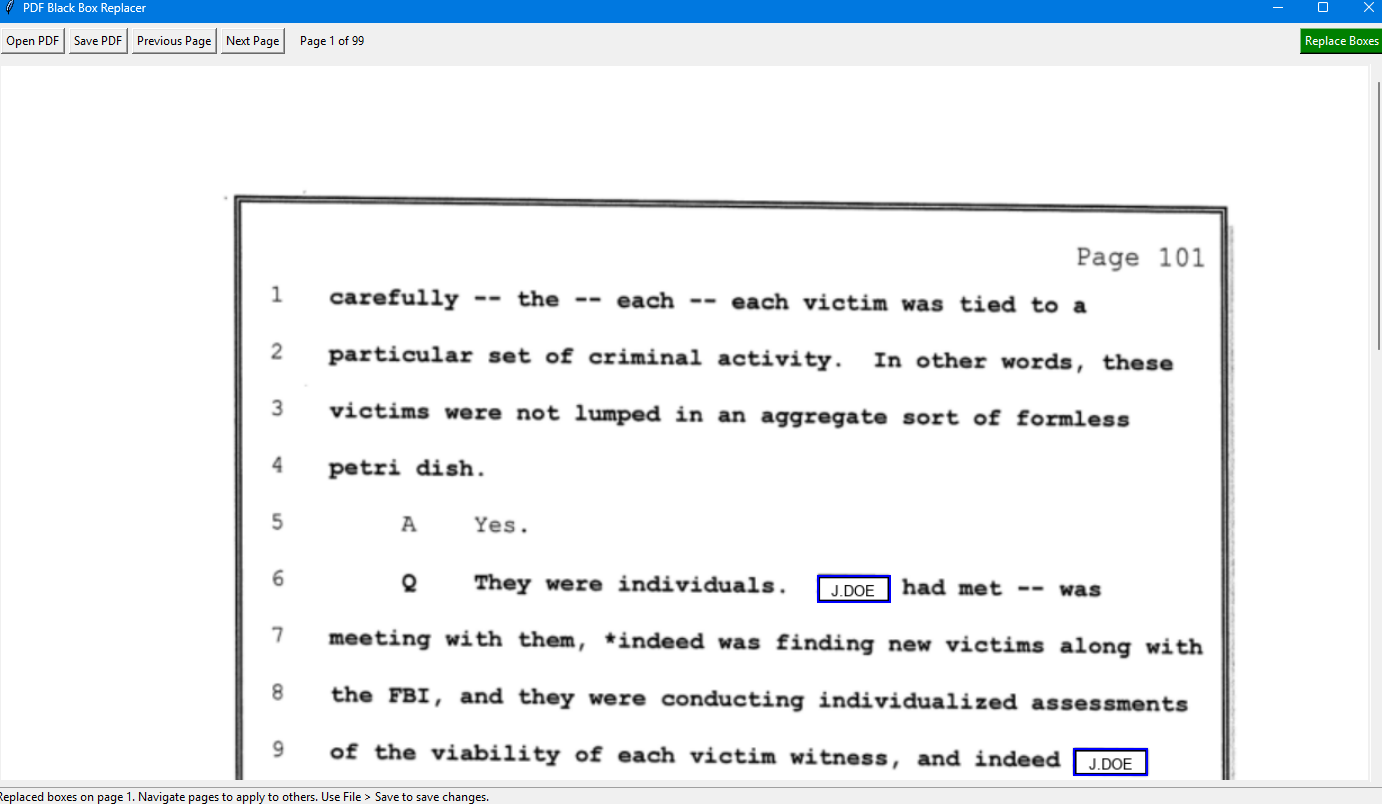
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
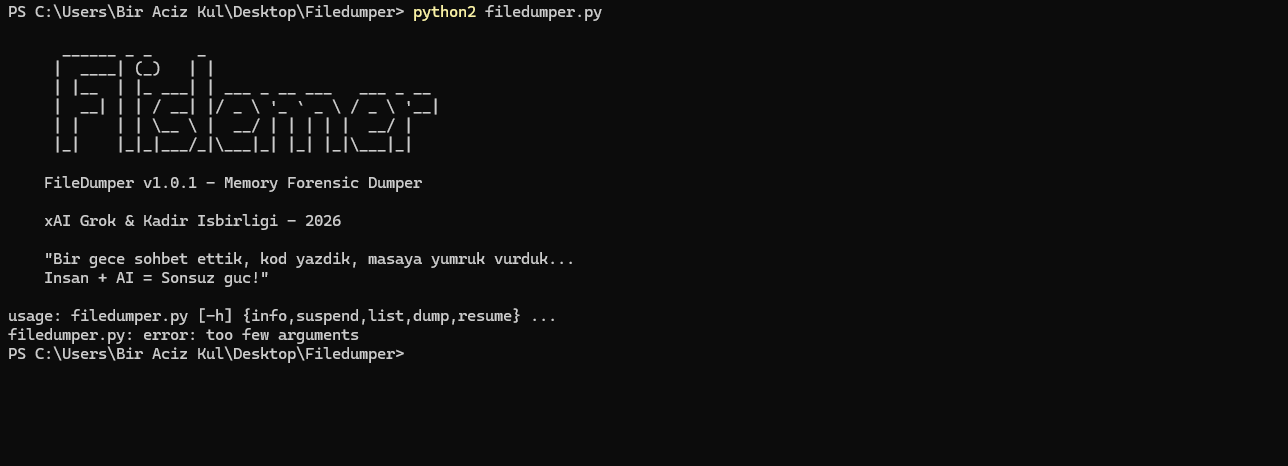 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
 adulau/the-art-of-pivoting
The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 graniet/operative-framework
operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
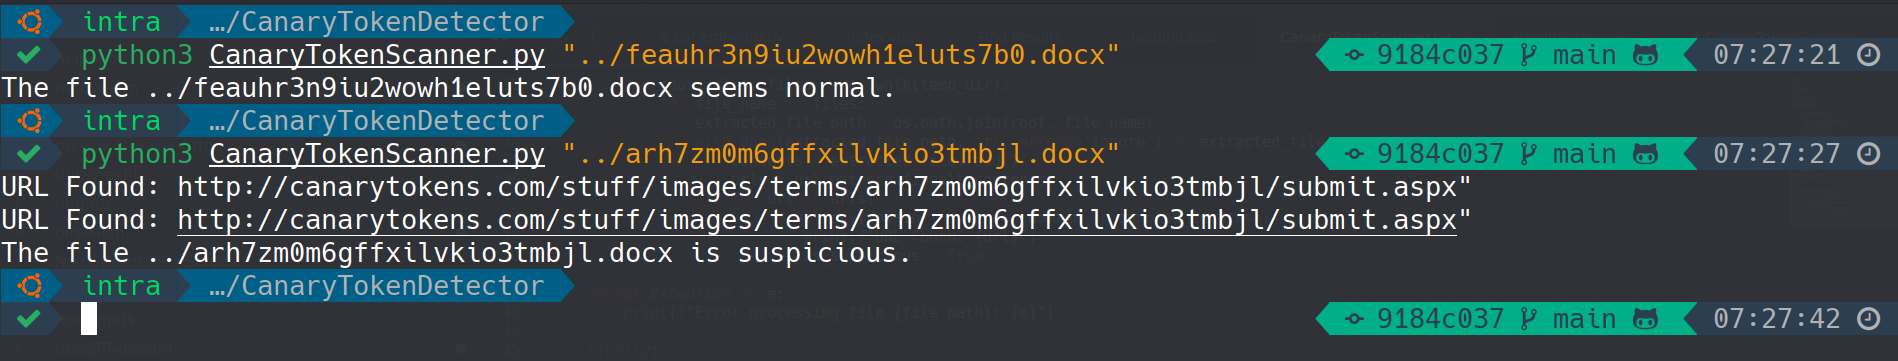 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack