Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).

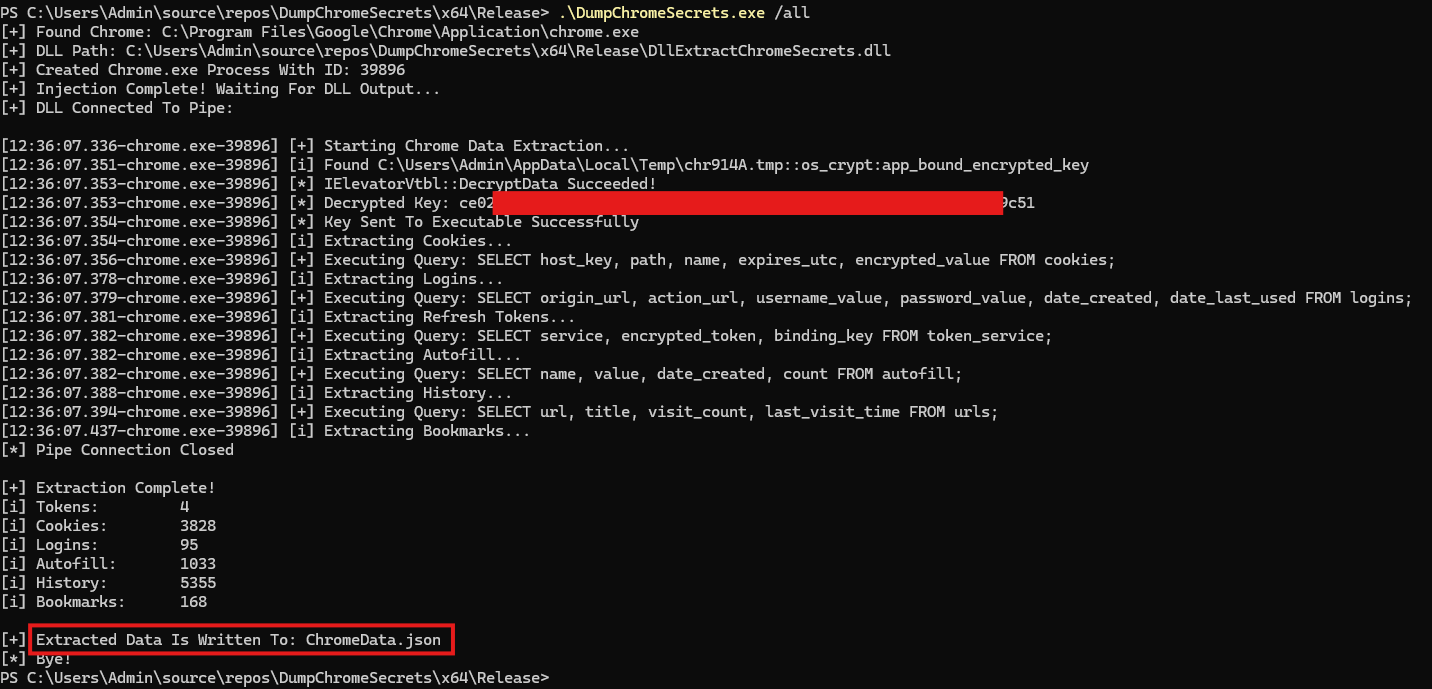
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

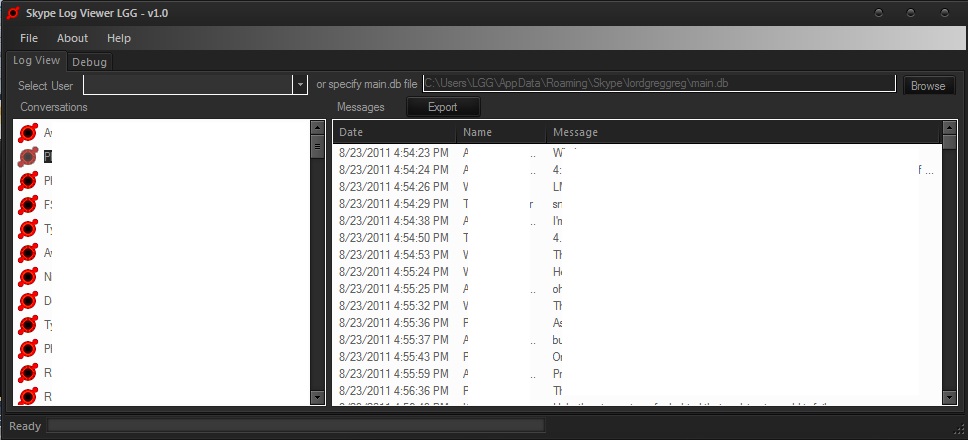
Download and View Skype History Without Skype

Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox

Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

Tracking history of USB events on GNU/Linux

Blockchain Transactions Investigation Tool

PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…