
SessionView
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
digital-forensicsforensicsincident-response+3
lsecqt/sessionviewA portable C# utility for enumerating local and remote windows sessions
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
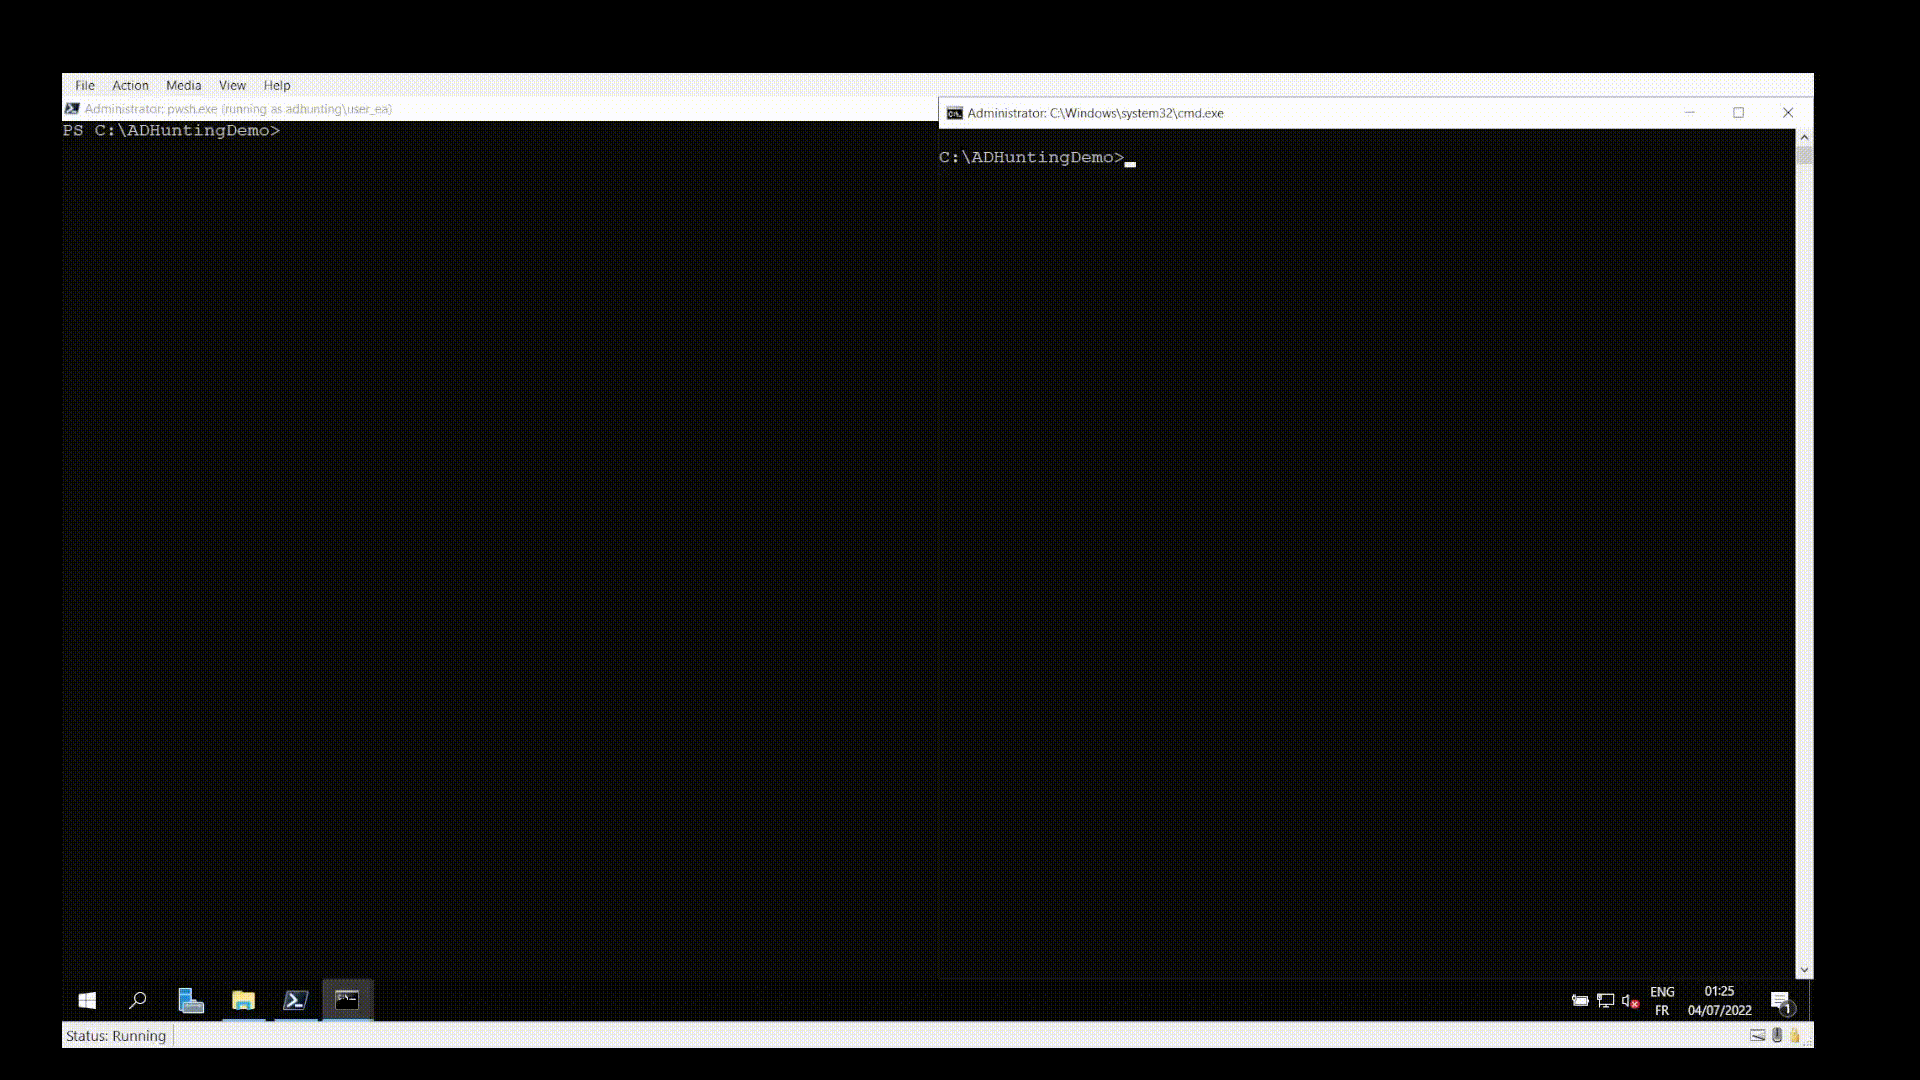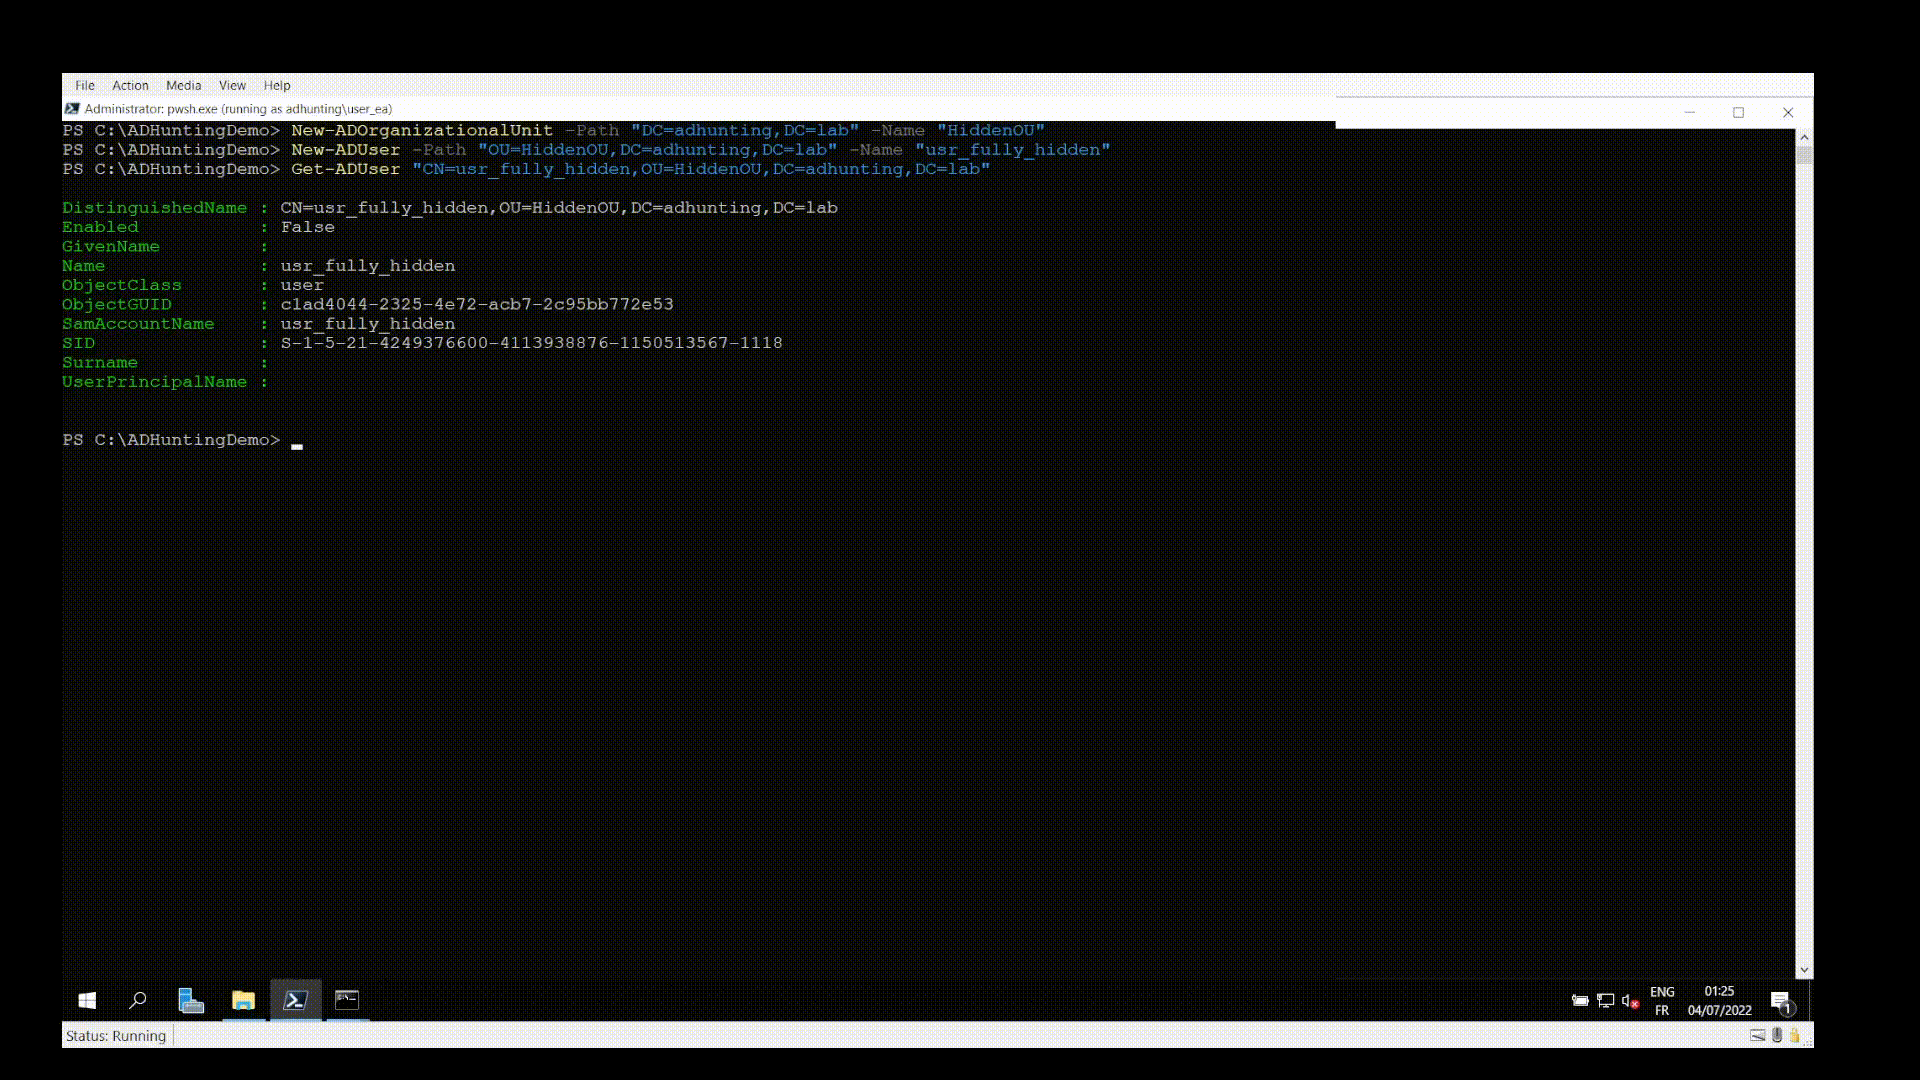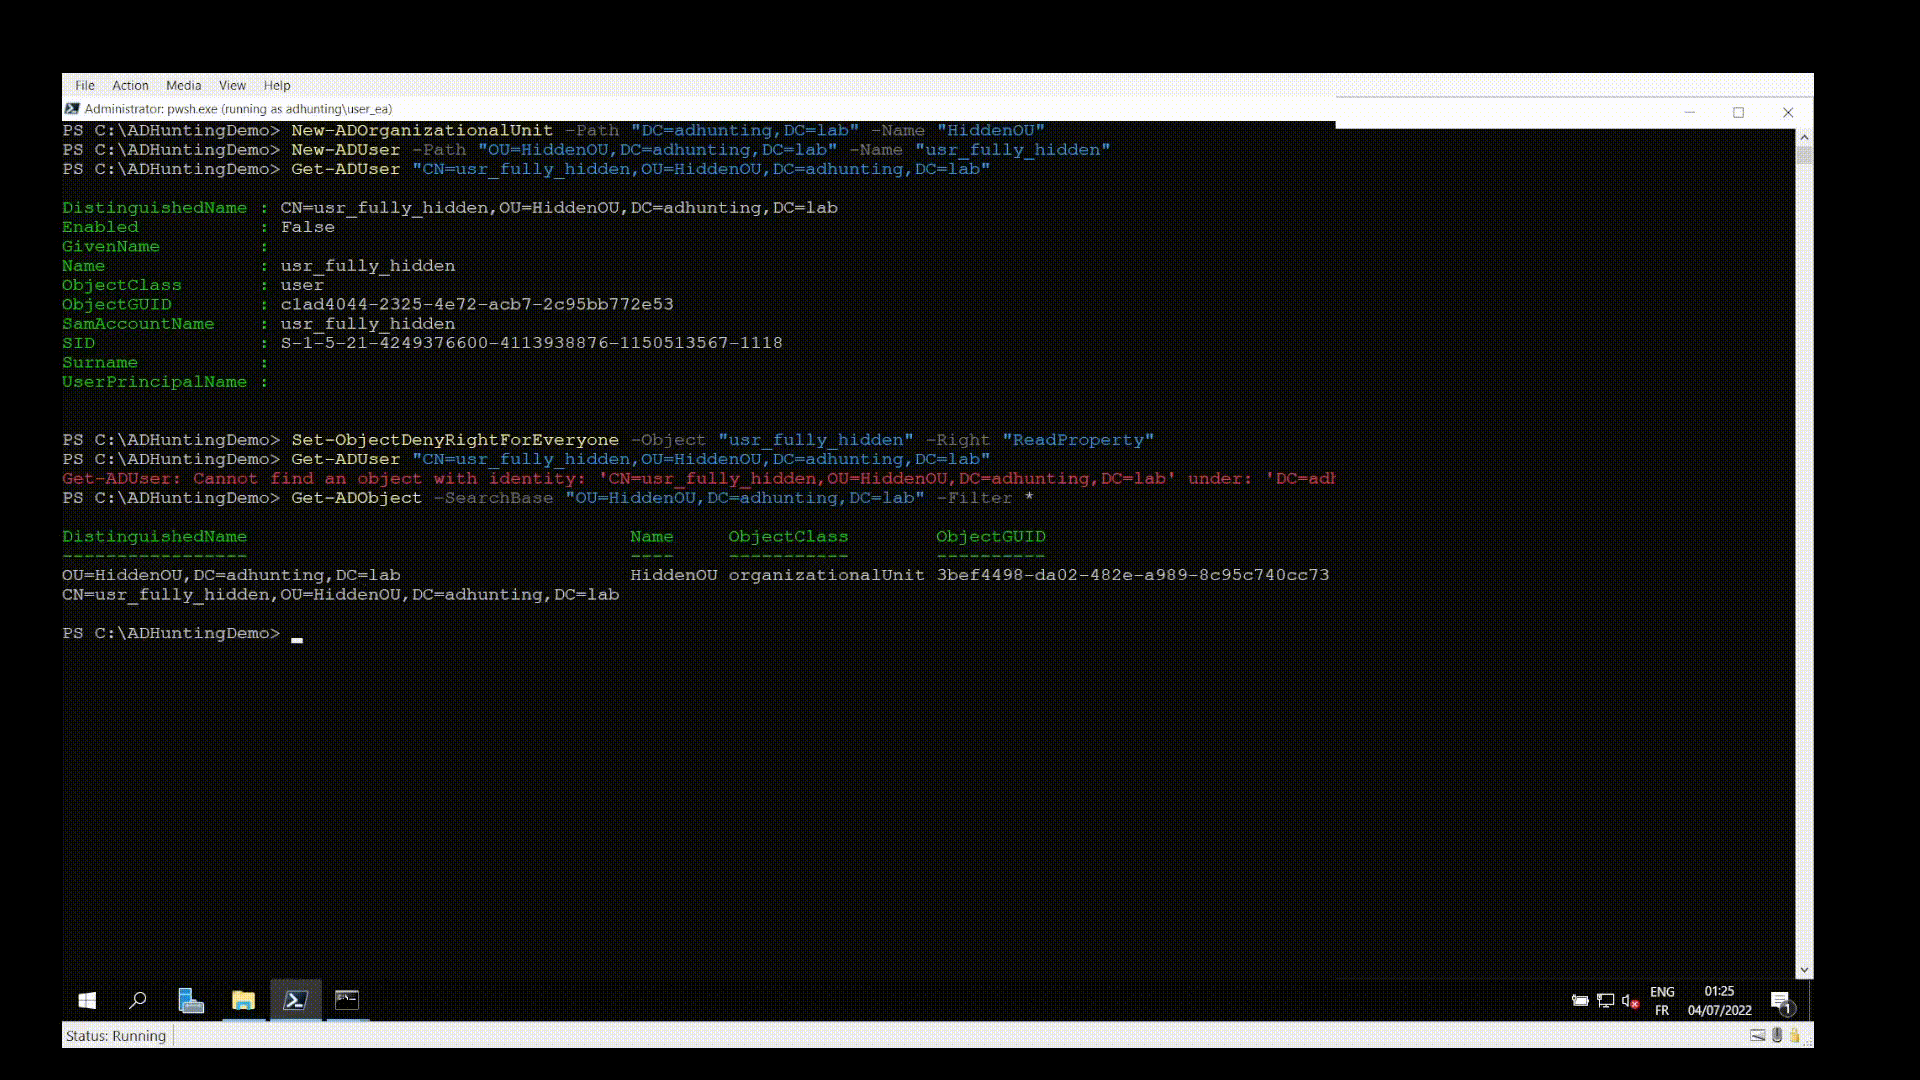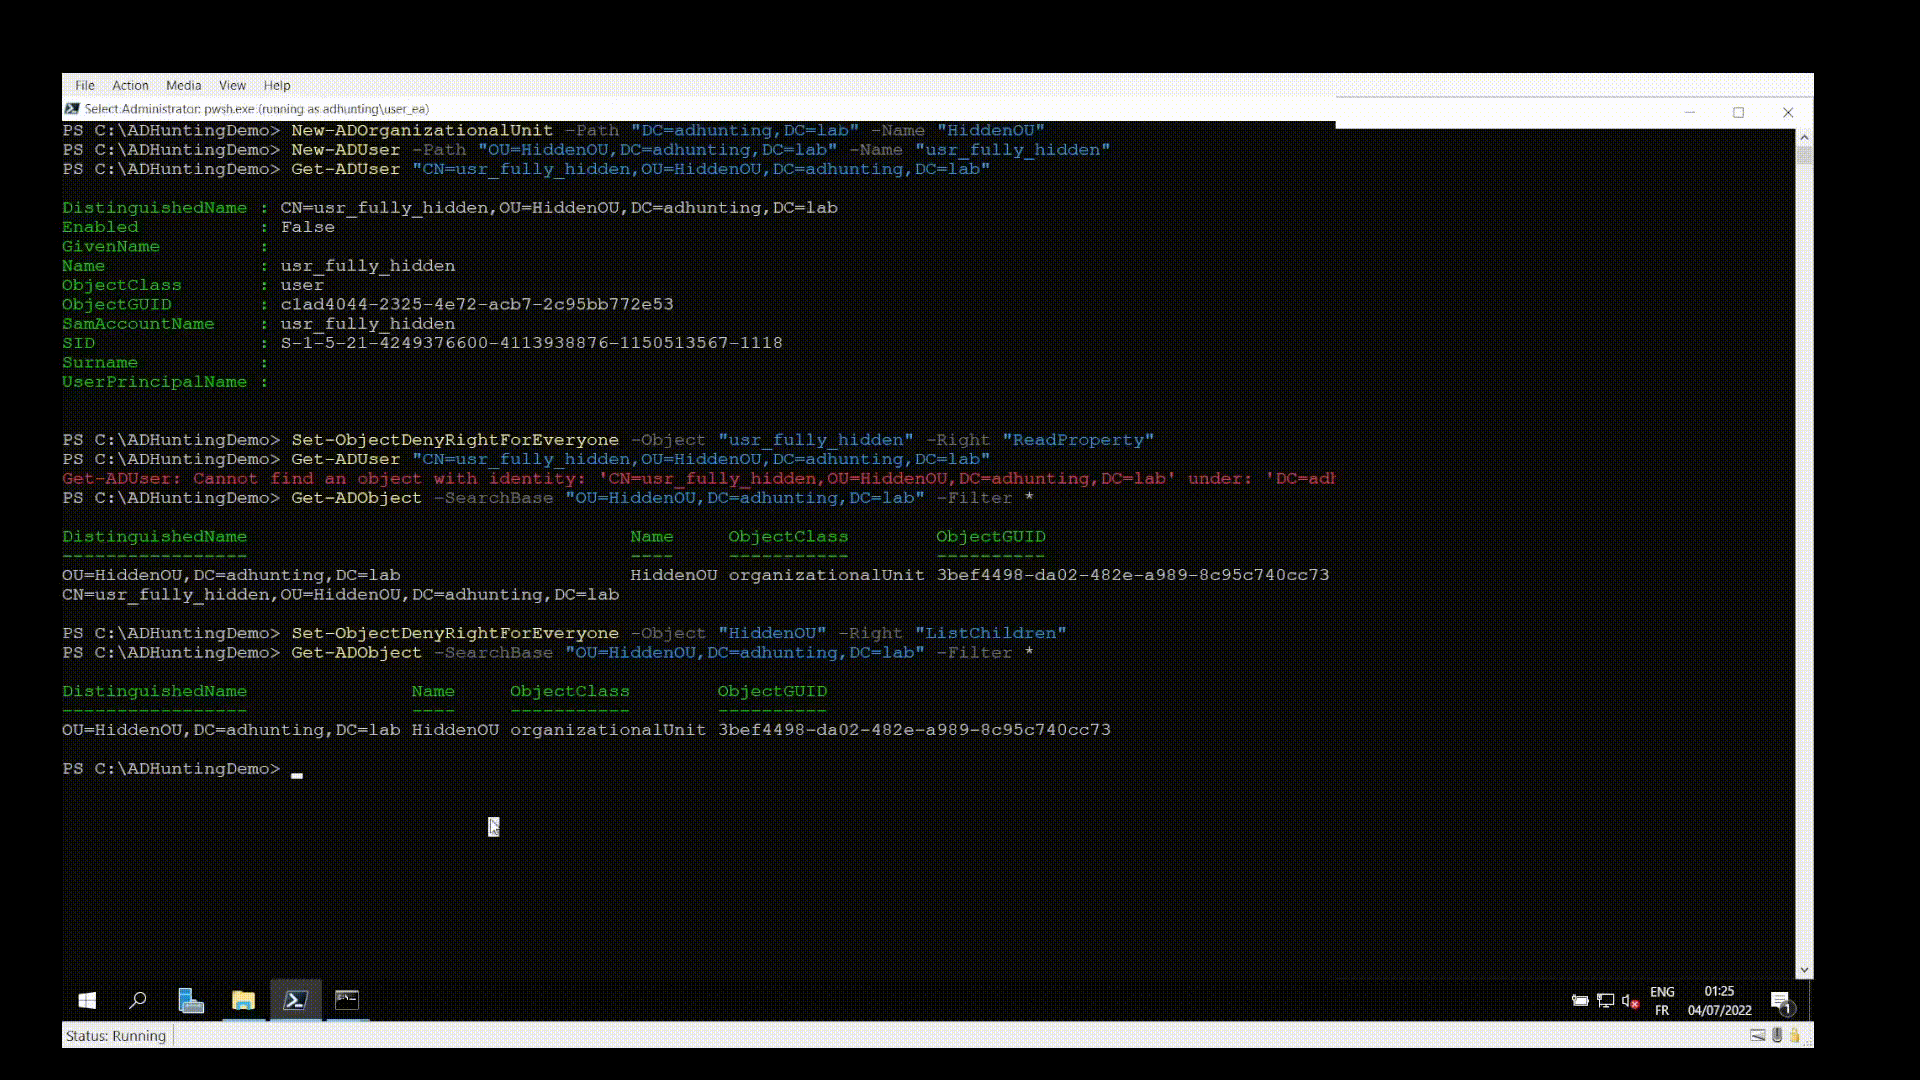 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…