
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
IG-Detective preview

IG-Detective

GitHubshredzwho/ig-detective

OSINT tool researched and designed to hunt down IG handles
educationfingerprint-spoofingforensics+7
1592 months ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
digital-forensicsforensicsnetwork-forensics+2
7421 year ago
rayhunter preview

rayhunter

GitHubefforg/rayhunter

Rust tool to detect cell site simulators on an orbic mobile hotspot
defensive-toolseducationembedded-systems-security+9
6.0k18 days ago
bytesrevealer preview

bytesrevealer

GitHubvulnex/bytesrevealer

Online Reverse Enginerring viewer
binary-analysiseducationforensics+4
153 months ago
darkfox preview

darkfox

GitHubaryanguenthner/darkfox

CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
crawlerforensicsinformation-gathering+6
1901 month ago
Snap-Scraper preview

Snap-Scraper

GitHubrhematt/snap-scraper

Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.
digital-forensicseducationforensics+3
1183 years ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
4931h 14m ago
Refloow-Geo-Forensics preview

Refloow-Geo-Forensics

GitHubrefloow/refloow-geo-forensics

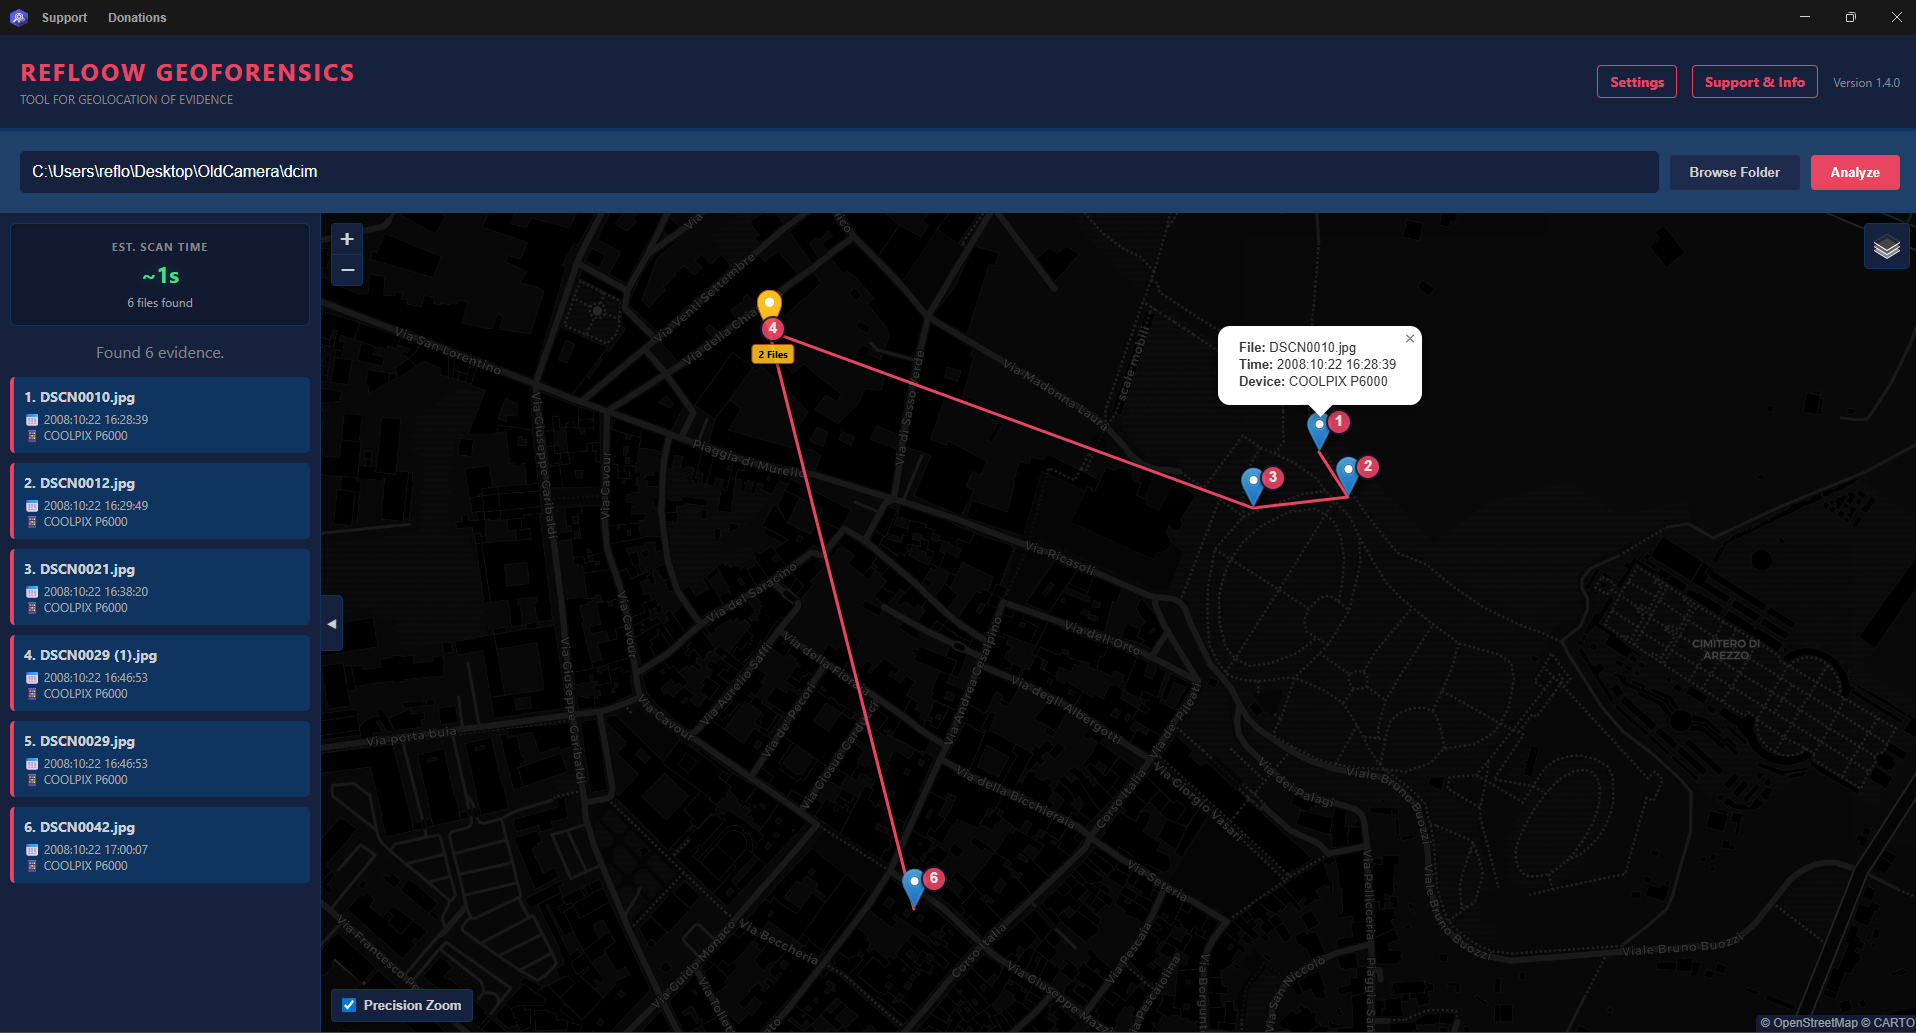
❤️ Free batch image & video geolocation digital forensics tool. Automatically extract EXIF data, visualize GPS coordinates on maps, and reconstruct…
digital-forensicseducationforensics+4
2321 month ago
xortool preview

xortool

GitHubhellman/xortool

A tool to analyze multi-byte xor cipher

binary-analysiscryptographyeducation+4
1.5k1 year ago
caronte preview

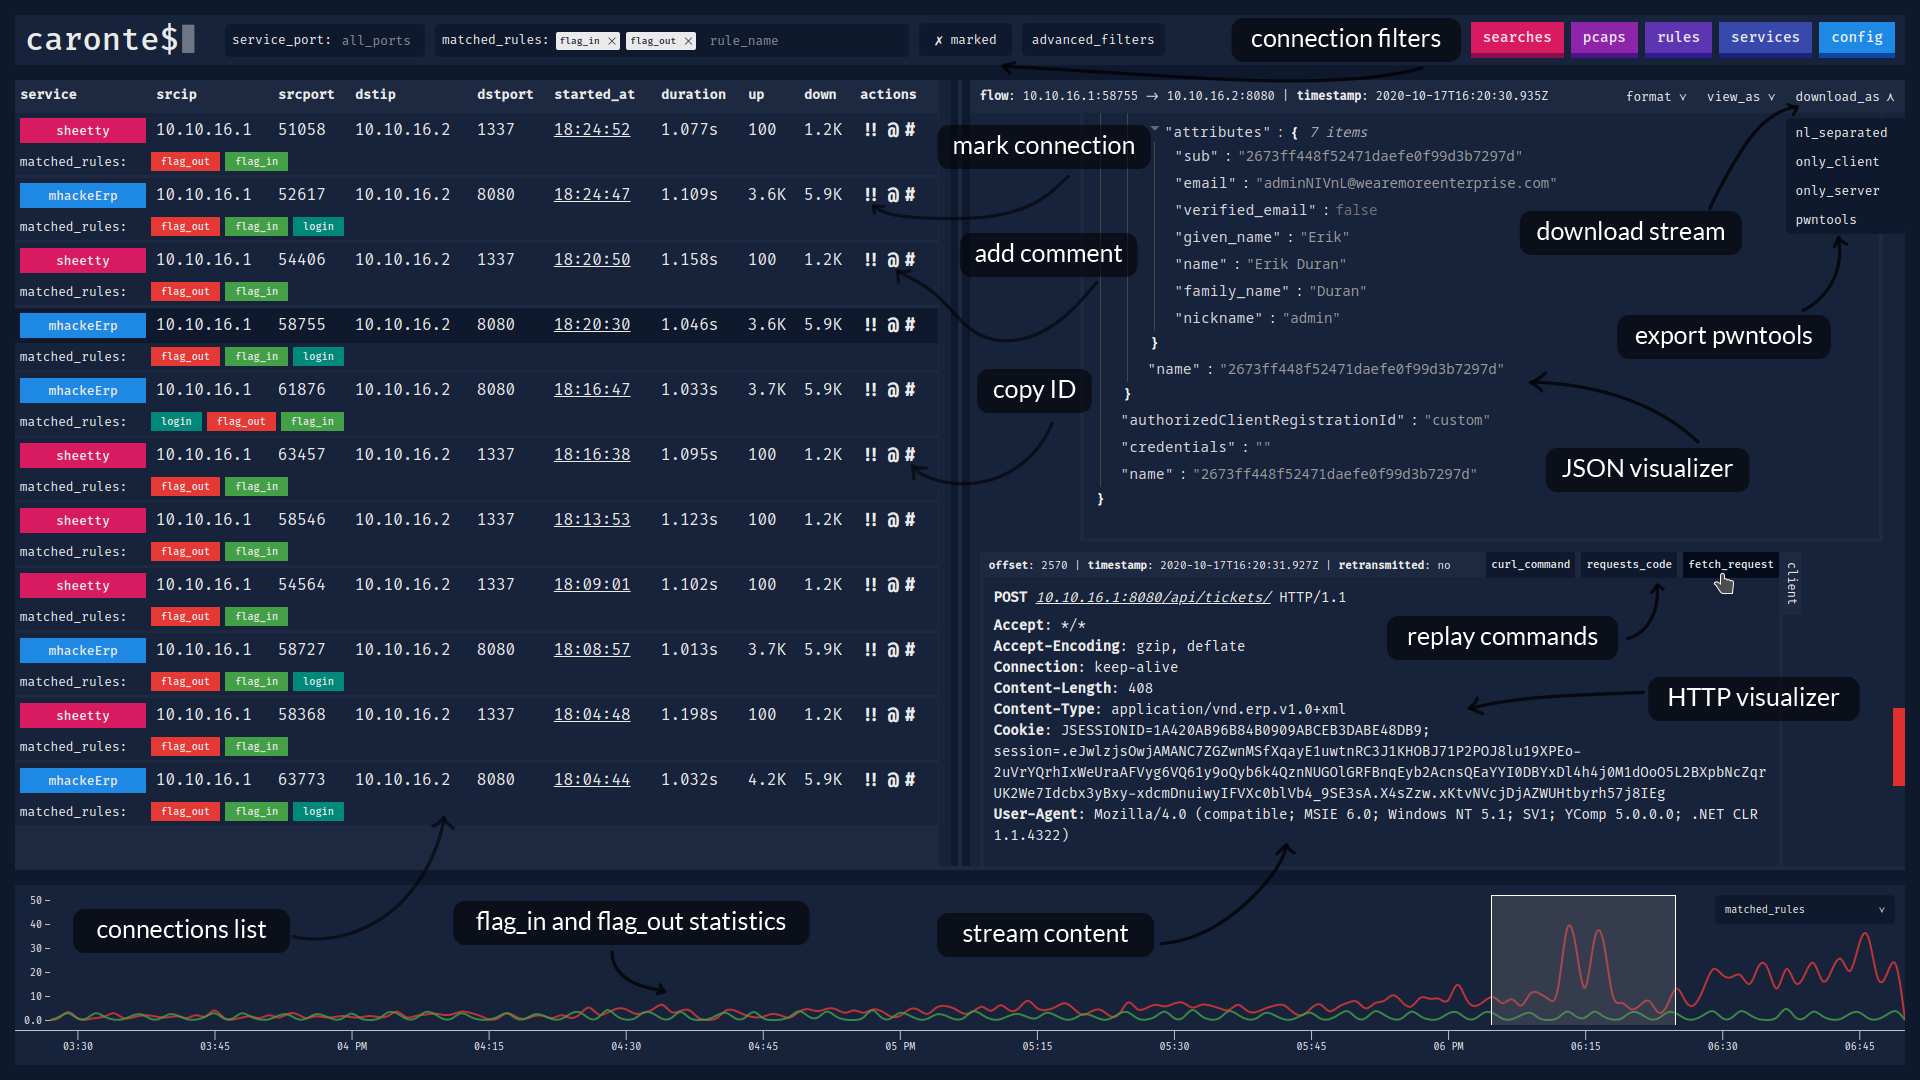
caronte

GitHubeciavatta/caronte

A tool to analyze the network flow during attack/defence Capture the Flag competitions
ctfforensicsnetwork-forensics+1
6534 years ago
vuke preview

vuke

GitHuboritwoen/vuke

Research tool for studying vulnerable cryptographic key generation (brainwallet, PRNG, milksad, LCG, xorshift)
cryptographyeducationexploitation+4
227 months ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
container-escapedigital-forensicseducation+7
33 months ago
chepy preview

chepy

GitHubsecurisec/chepy

Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
cryptographyctfforensics+2
1.1k6 months ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

debuggersdynamic-analysis-sandboxingforensics+1
2485 years ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
207 months ago
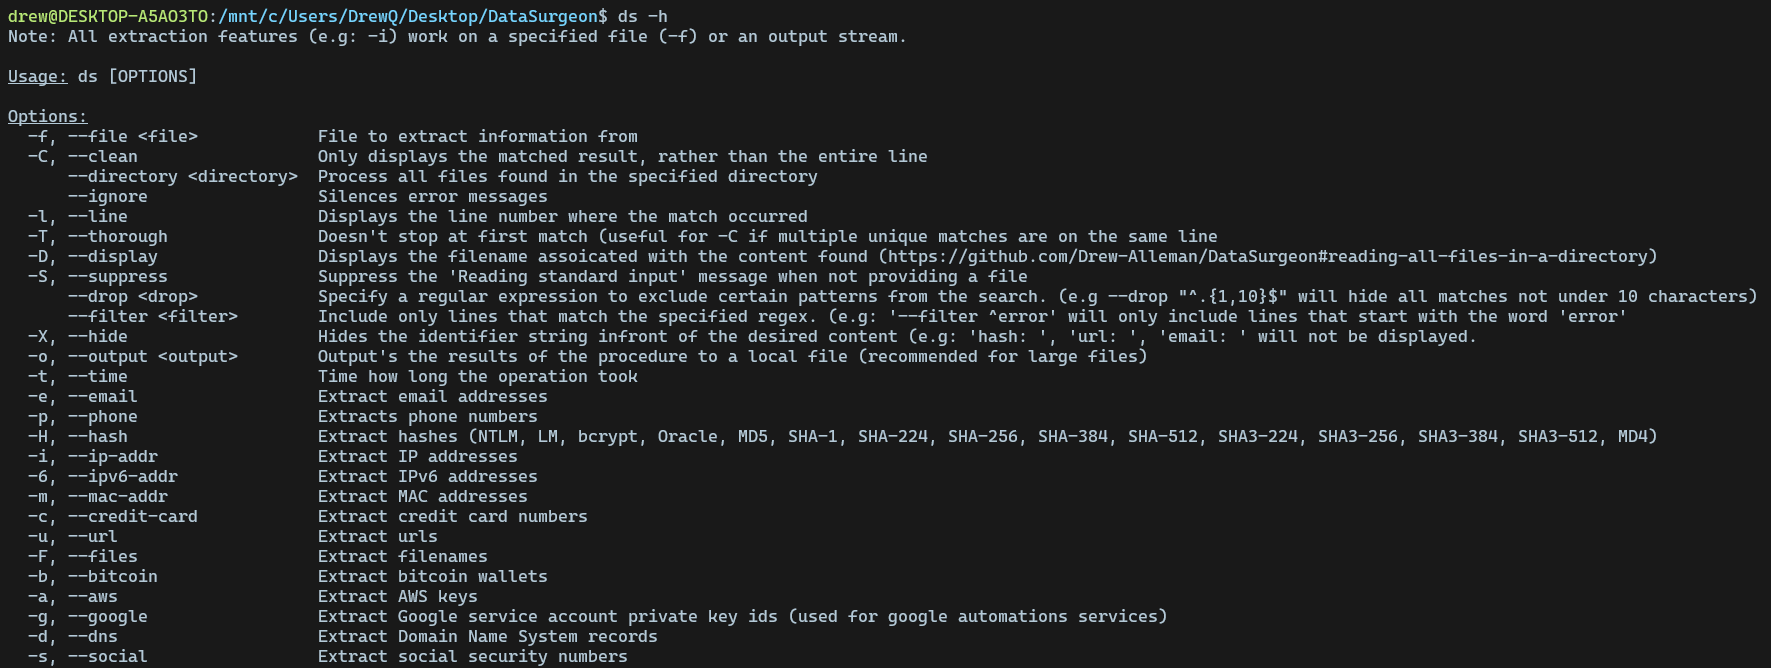
DataSurgeon preview

DataSurgeon

GitHubdrew-alleman/datasurgeon

Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text

ctfdata-exfiltrationforensics+6
9082 years ago
Previous12Next