
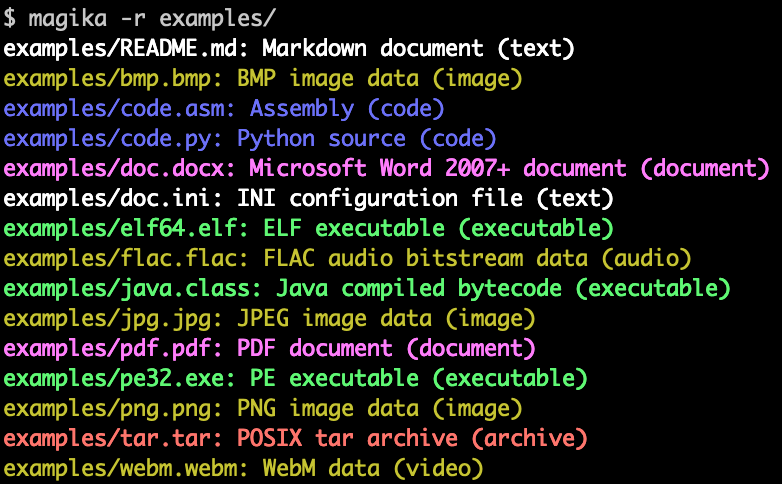
magika
 google/magika
Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
google/magikaFast and accurate AI powered file content types detection
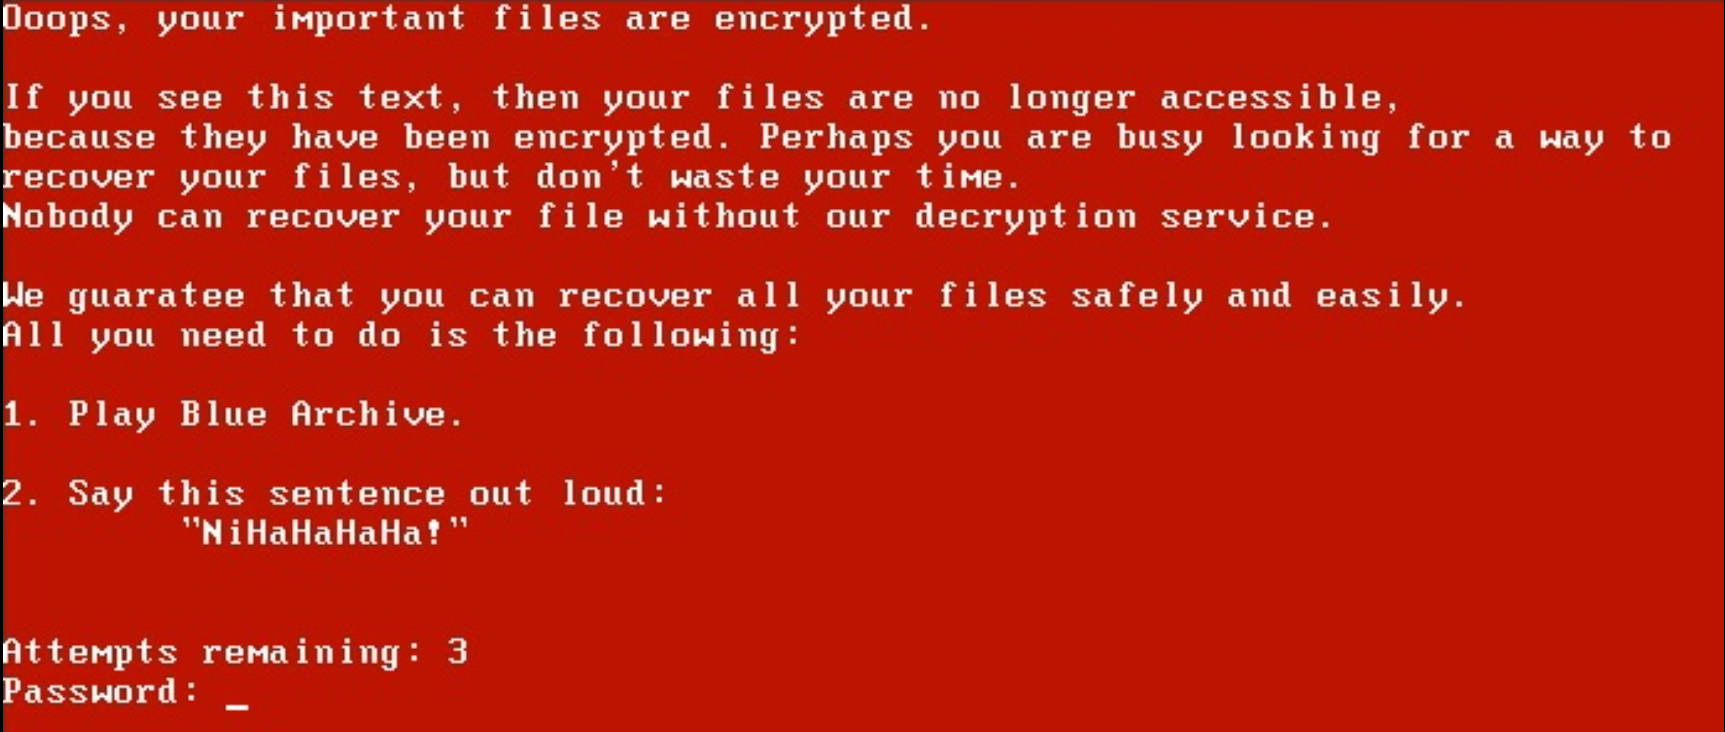 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
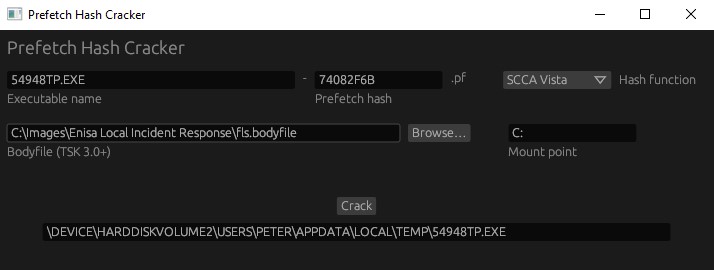 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 utkusen/wholeaked
a file-sharing tool that allows you to find the responsible person in case of a leakage
 t4d/stalkphish
StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
 dawnl3ss/cve-2023-32784
Retrieve the master password of a keepass database <= 2.53.1
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781