Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
274 results
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
15.6k
16h 40m ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.

digital-forensicsdns-analysisforensics+3
5.5k18h 2m ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k24 days ago
ngrep preview

ngrep

GitHubjpr5/ngrep

ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

dns-analysisforensicsinformation-gathering+3
1.0k8 months ago
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.2k1 day ago
FACT preview

FACT

GitHubunicornunicode/fact

Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
cloud-securitydigital-forensicsforensics
173 years ago
TrueTree preview

TrueTree

GitHubthemittenmac/truetree

A command line tool for pstree-like output on macOS with additional pid capturing capabilities
digital-forensicsforensicsincident-response+1
2888 days ago
ctf-tools preview

ctf-tools

GitHubzardus/ctf-tools

Some setup scripts for security research tools.

binary-analysiscryptographyctf+9
9.6k8 days ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.5k17 days ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

binary-analysisdefensive-toolsdigital-forensics+6
8842 years ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool

data-recoverydigital-forensicsforensics+7
721 year ago
malware-iocs preview

malware-iocs

GitHubdoctorwebltd/malware-iocs

Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…

curated-resourcesforensicsincident-response+4
2441 month ago
ubuntils preview

ubuntils

GitHubasmitdesai/ubuntils

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
configuration-auditingdefensive-toolsdigital-forensics+7
414 days ago
chatlog preview

chatlog

GitHubsjzar/chatlog

chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
database-securityforensicsinformation-gathering+1
9.2k1 year ago
hashID preview

hashID

GitHubpsypanda/hashid

Software to identify the different types of hashes -
forensicshash-analysisinformation-gathering+3
1.5k11 years ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8582 years ago
iDescriptor preview

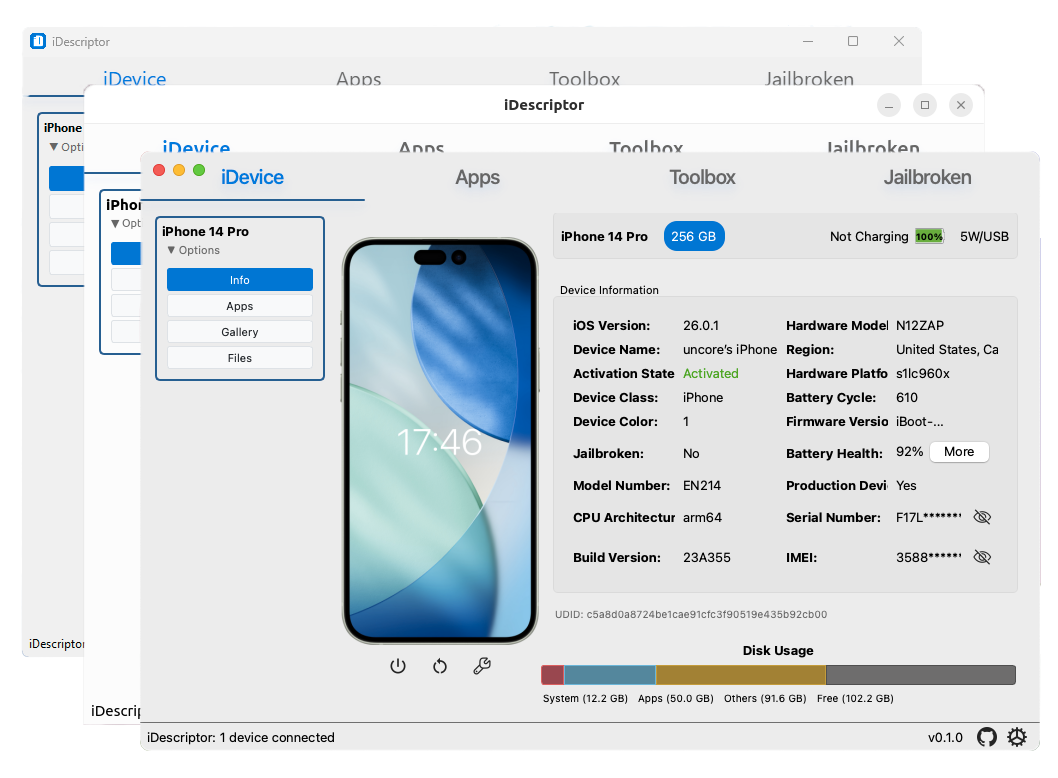
iDescriptor

GitHubidescriptor/idescriptor

privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.7k1 day ago
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

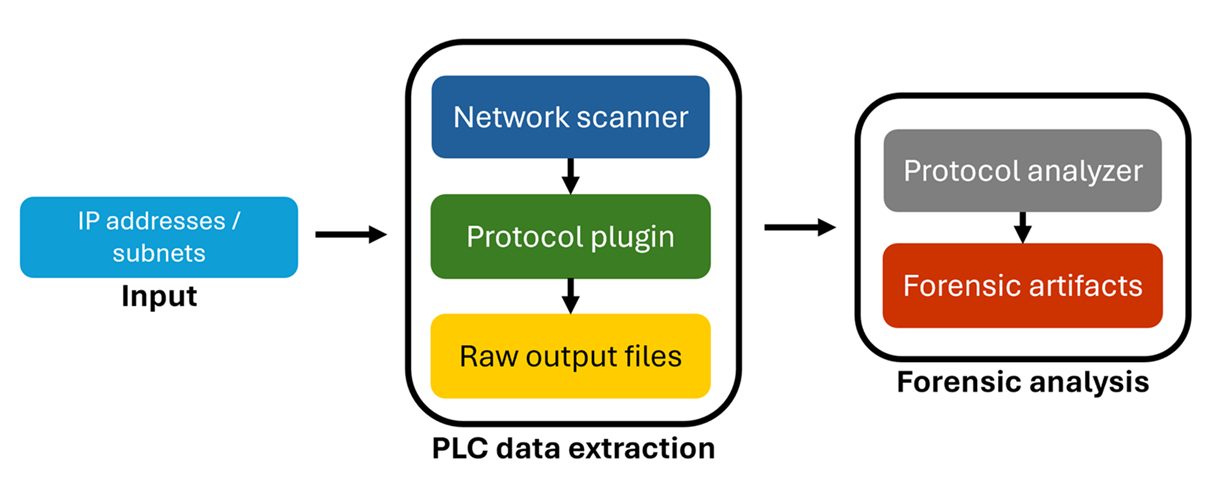
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…

digital-forensicsforensicsincident-response+2
3751 year ago
Previous12…16Next