
kAFL
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+4
intellabs/kaflA fuzzer for full VM kernel/driver targets
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 icicle-emu/icicle
Emulation-based fuzzer for MSP430 firmware that finds and analyzes memory-corruption bugs with detailed crash reports and reproducible inputs.
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…
 angr/angr
A powerful and user-friendly binary analysis platform!
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 quarkslab/conf-presentations
Quarkslab conference talks
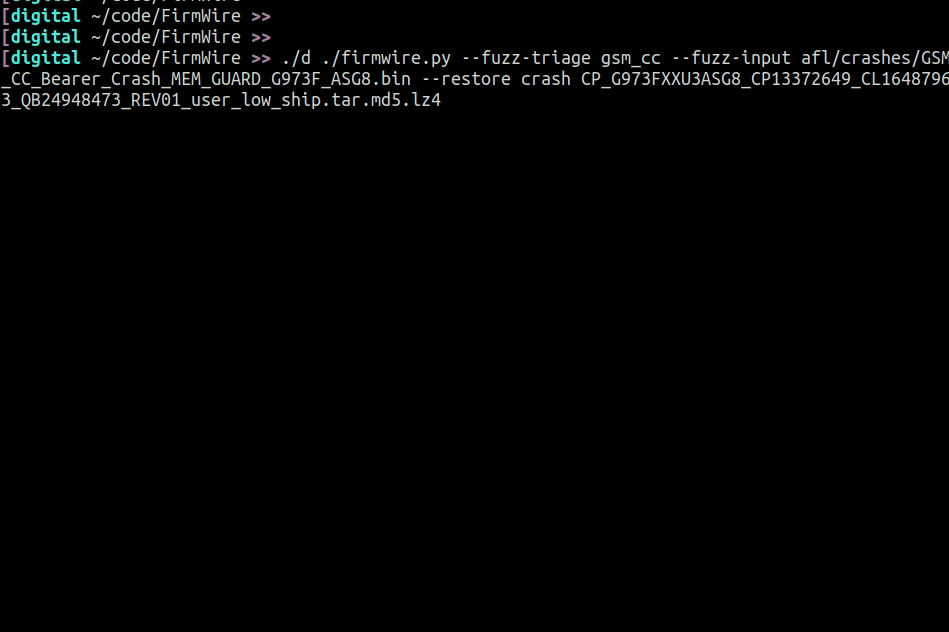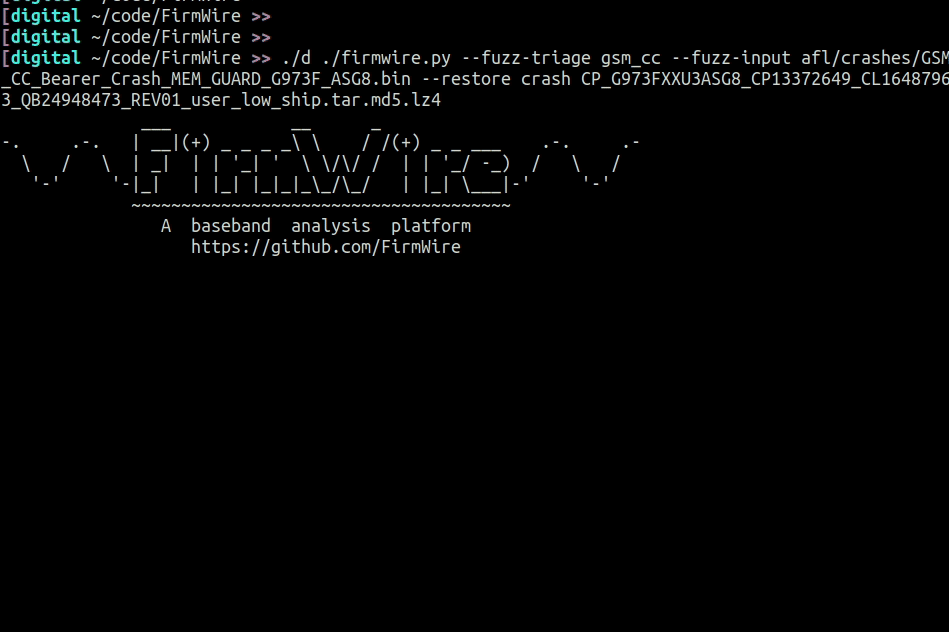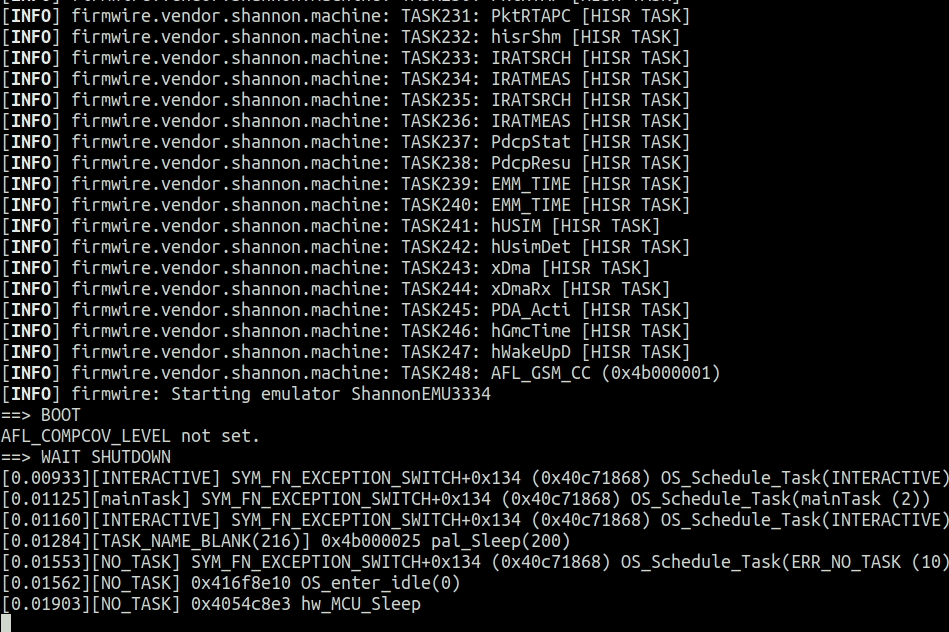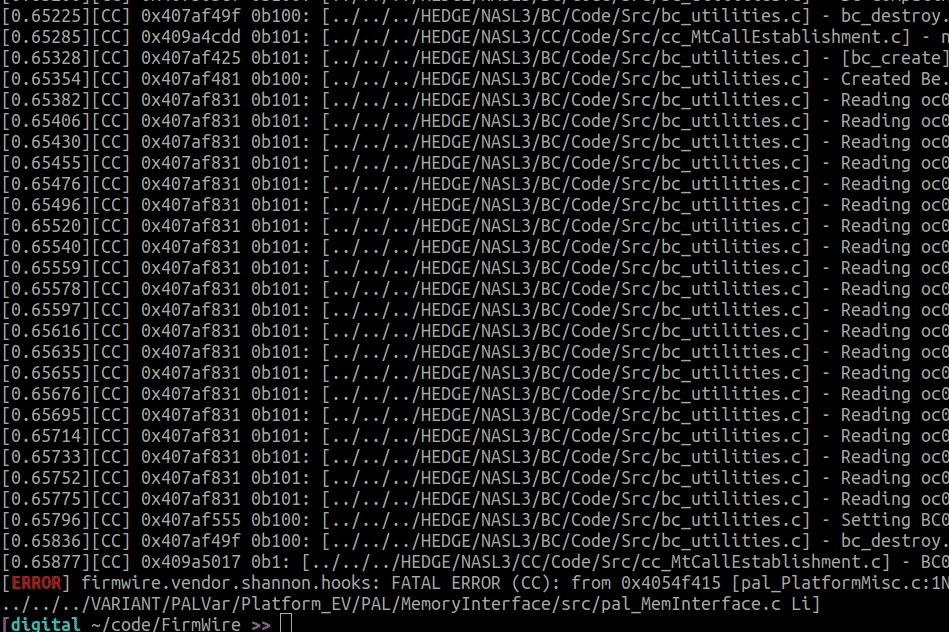 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
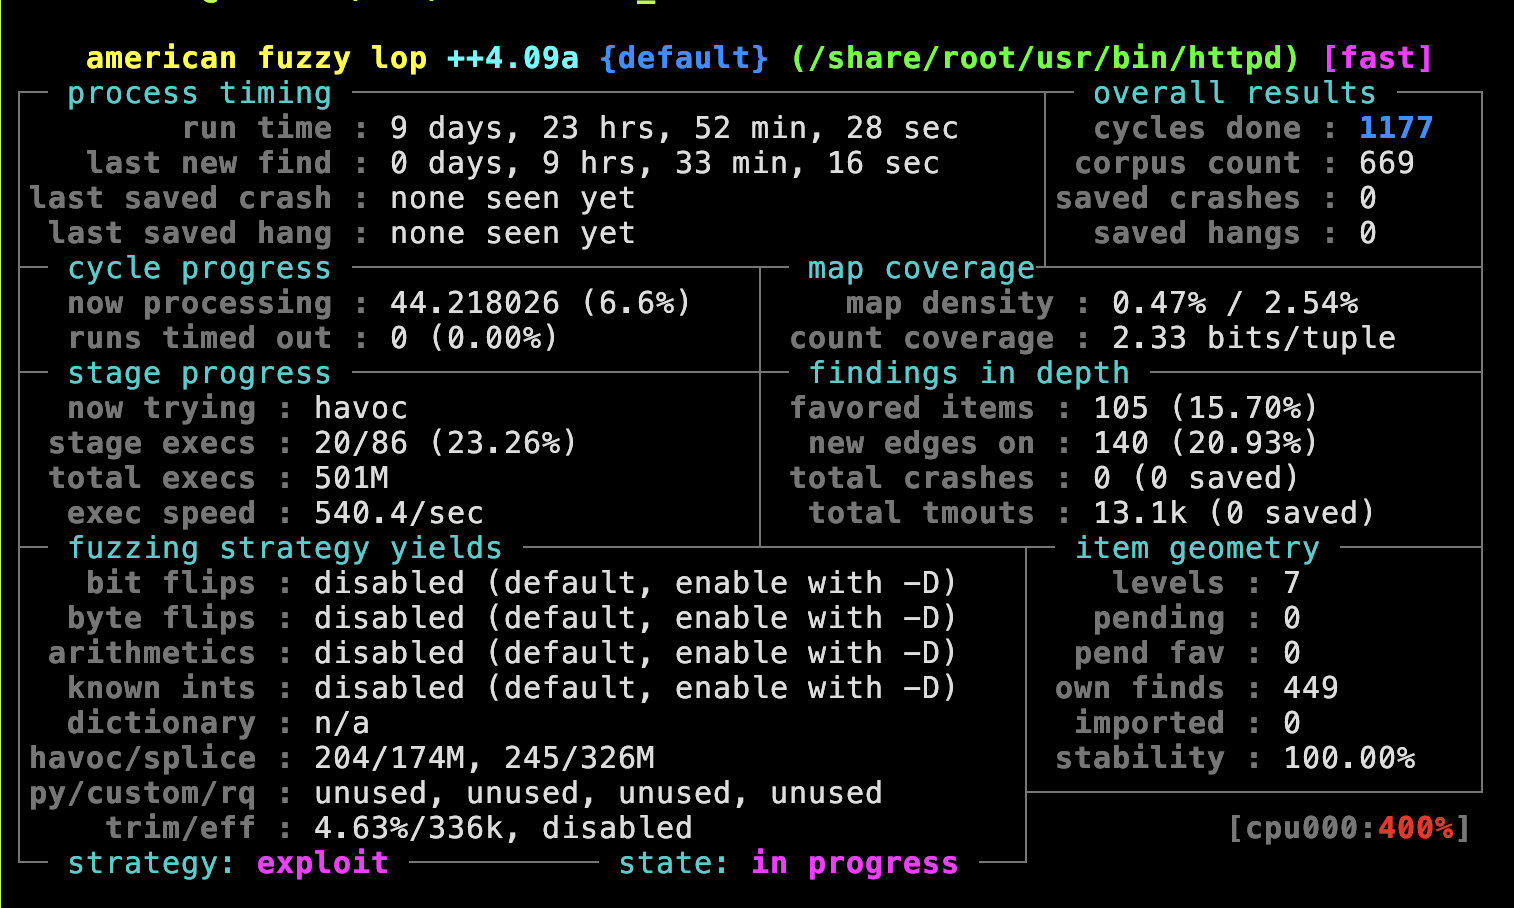 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…