

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
71.1k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
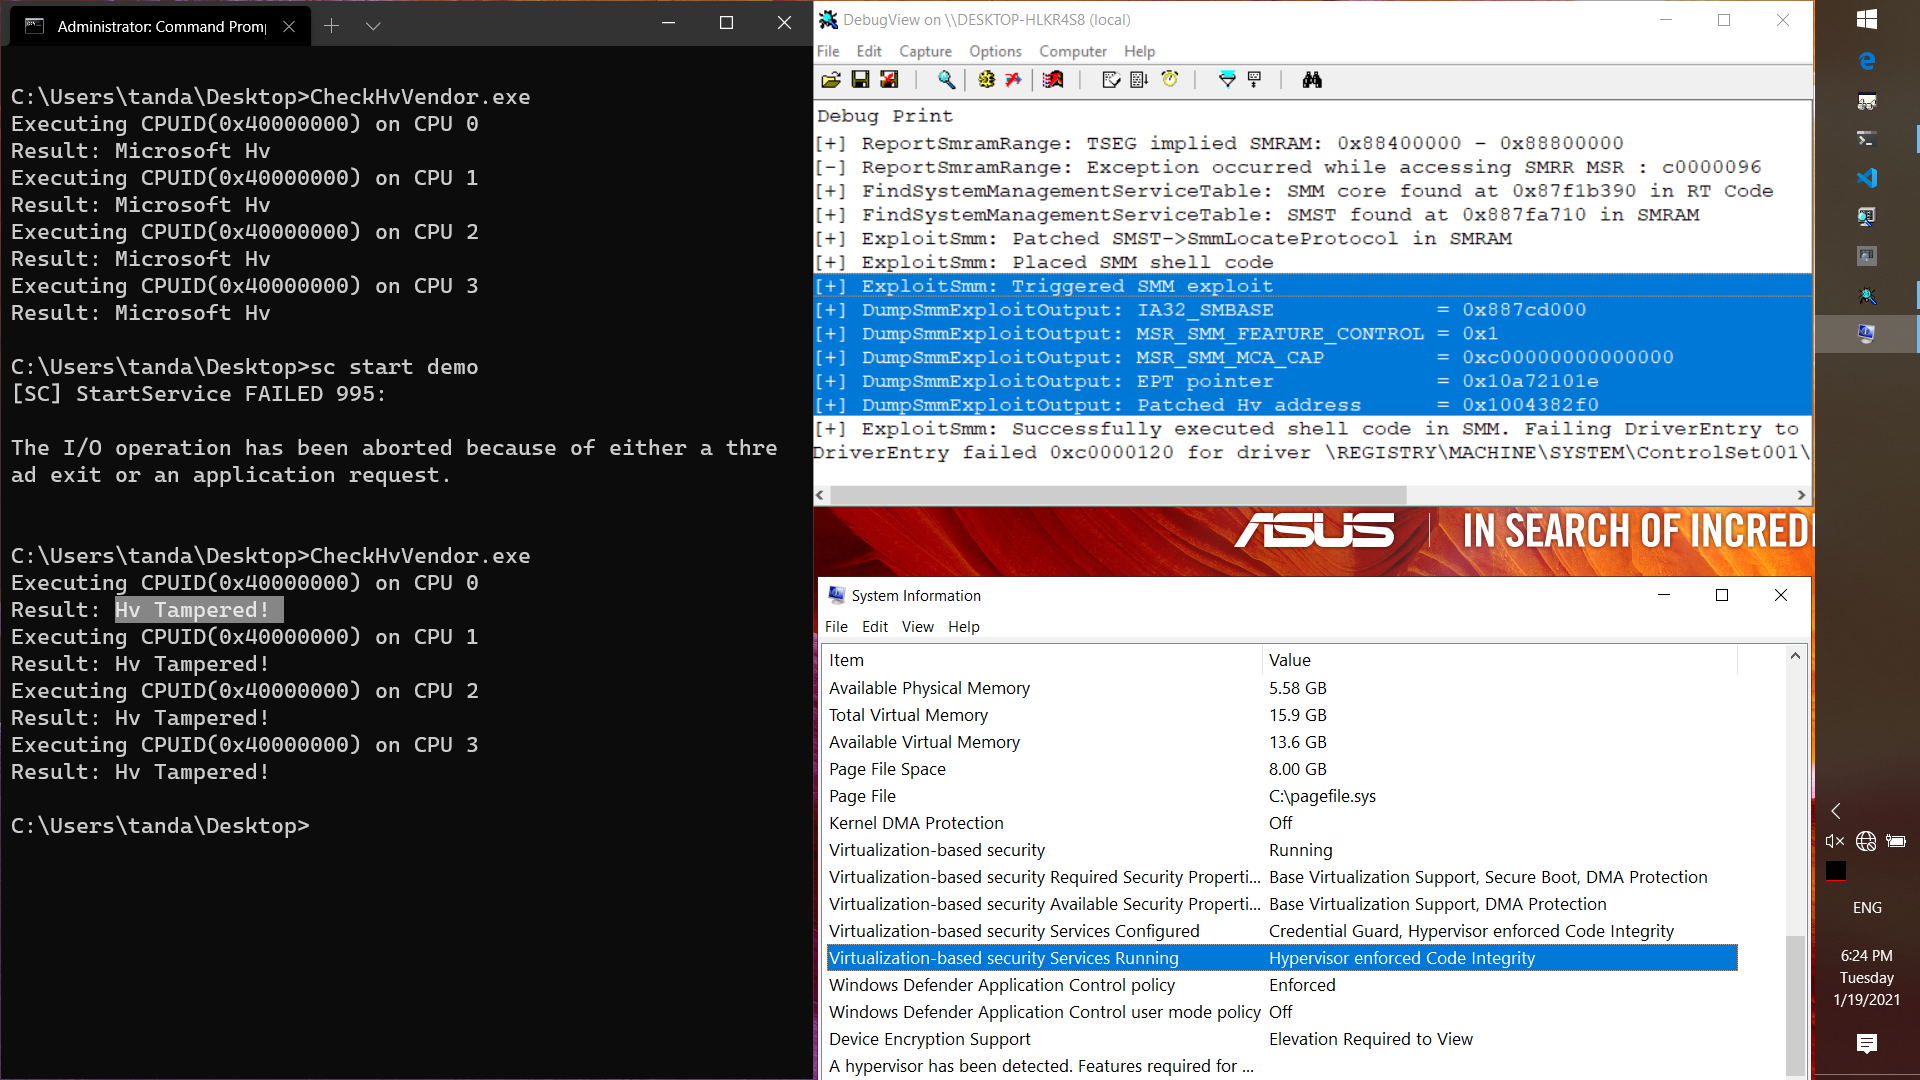 tandasat/smmexploit
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 blasty/wake-and-break
PSP exploit for AMD navi31 (RX 7900) GPUs that disables firmware signature checks so the card loads unsigned SMU, SDMA, MEC, IMU and RLC firmware;…
 zb3/tiandy-research
This repository contains the results of my August 2020 research of Tiandy's IPC/NVR firmware. I found two vulnerabilities that could be used to…