
openwrt
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
educationembedded-systems-securityfirmware-analysis+7
28.6k
openwrt/openwrtLinux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 mretallack/dronecamera
Drone HASAKEE FPV video app for Android
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 nishantjoshi00/flipper-template
Zig development template for Flipper Zero with automated build pipeline, SDK integration, and cross-compilation for ARM Cortex-M4. Supports Sub-GHz,…
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
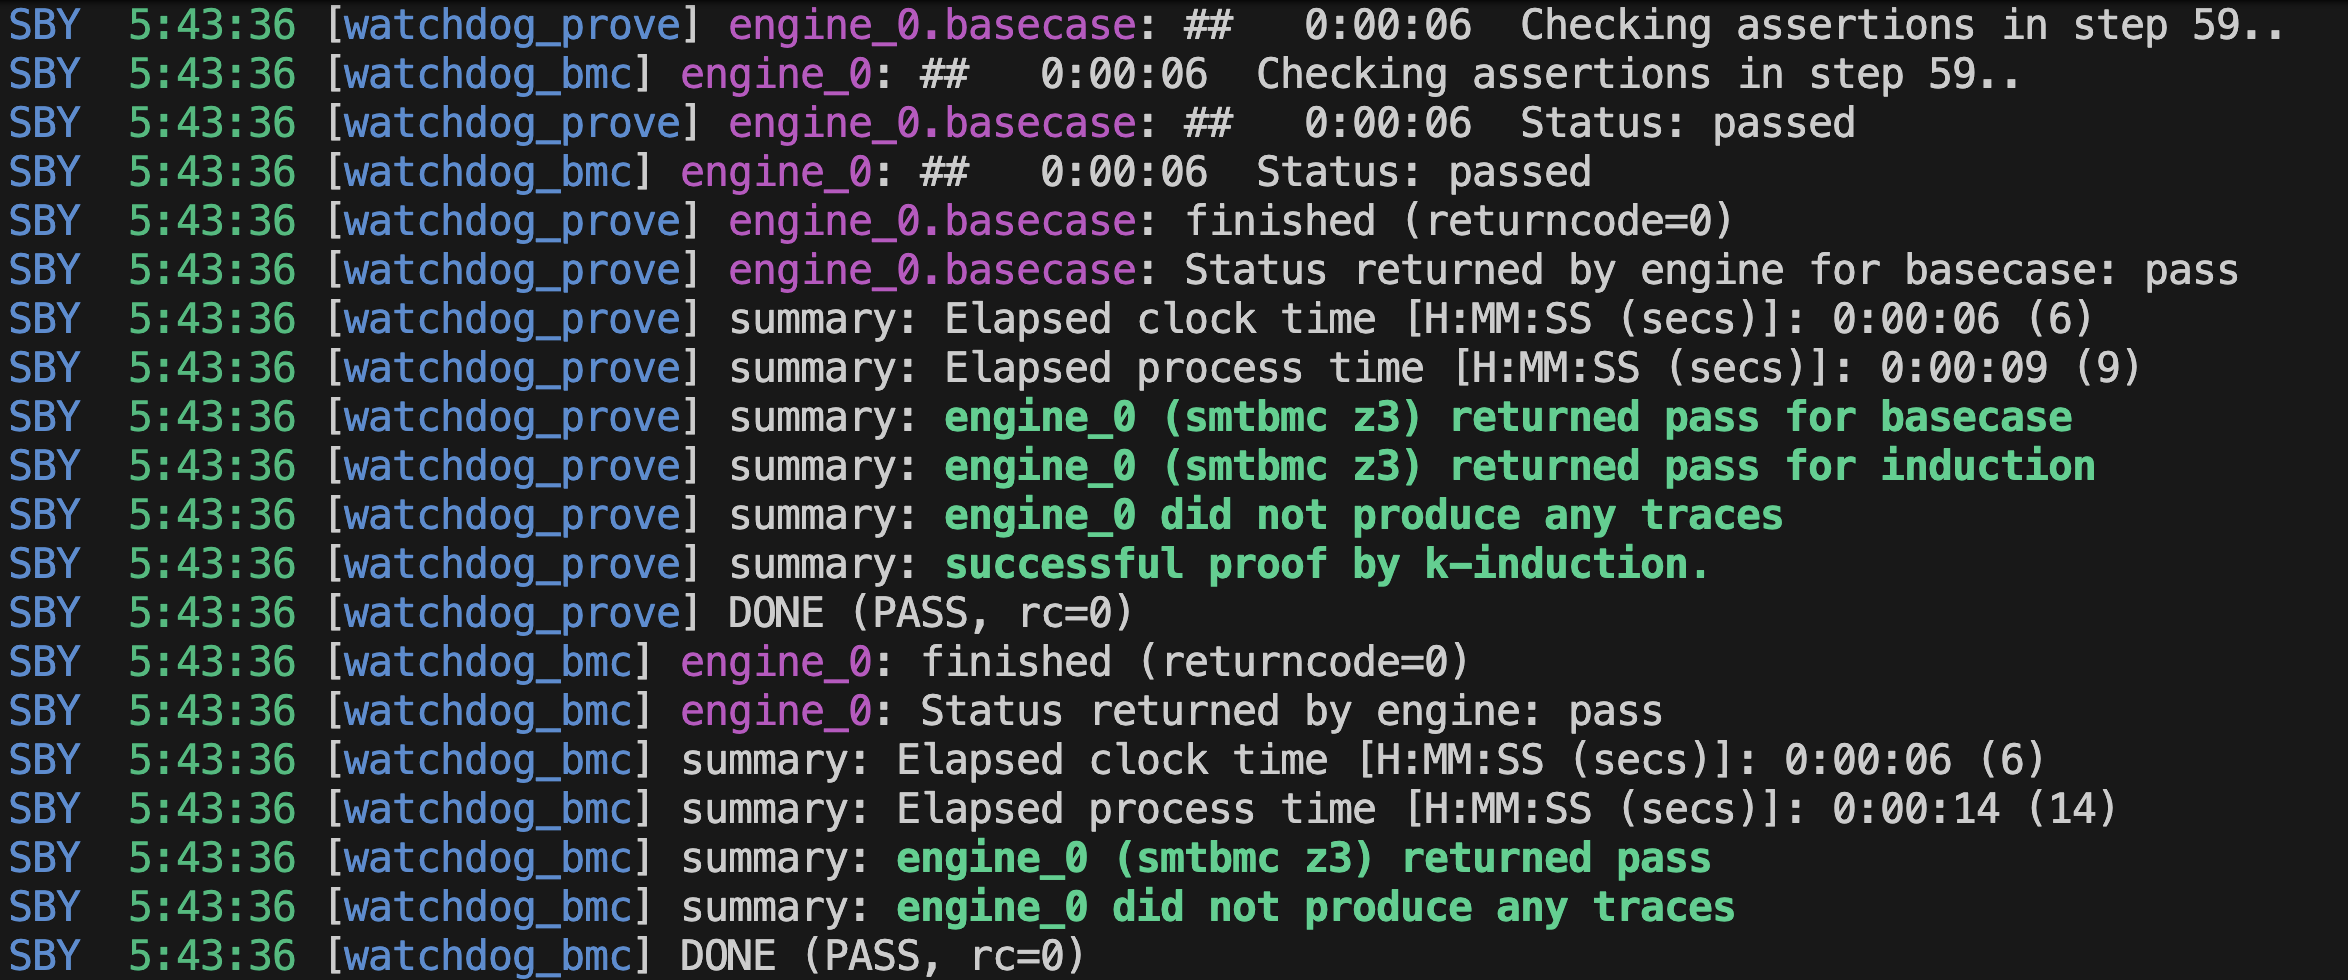 park07/amradio
FPGA-based 12-channel AM radio broadcast system with formal verification of a hardware watchdog for fail-safe emergency alert transmission in…
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.