

 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 scriptingxss/embedos
EmbedOS - Embedded security testing virtual machine
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
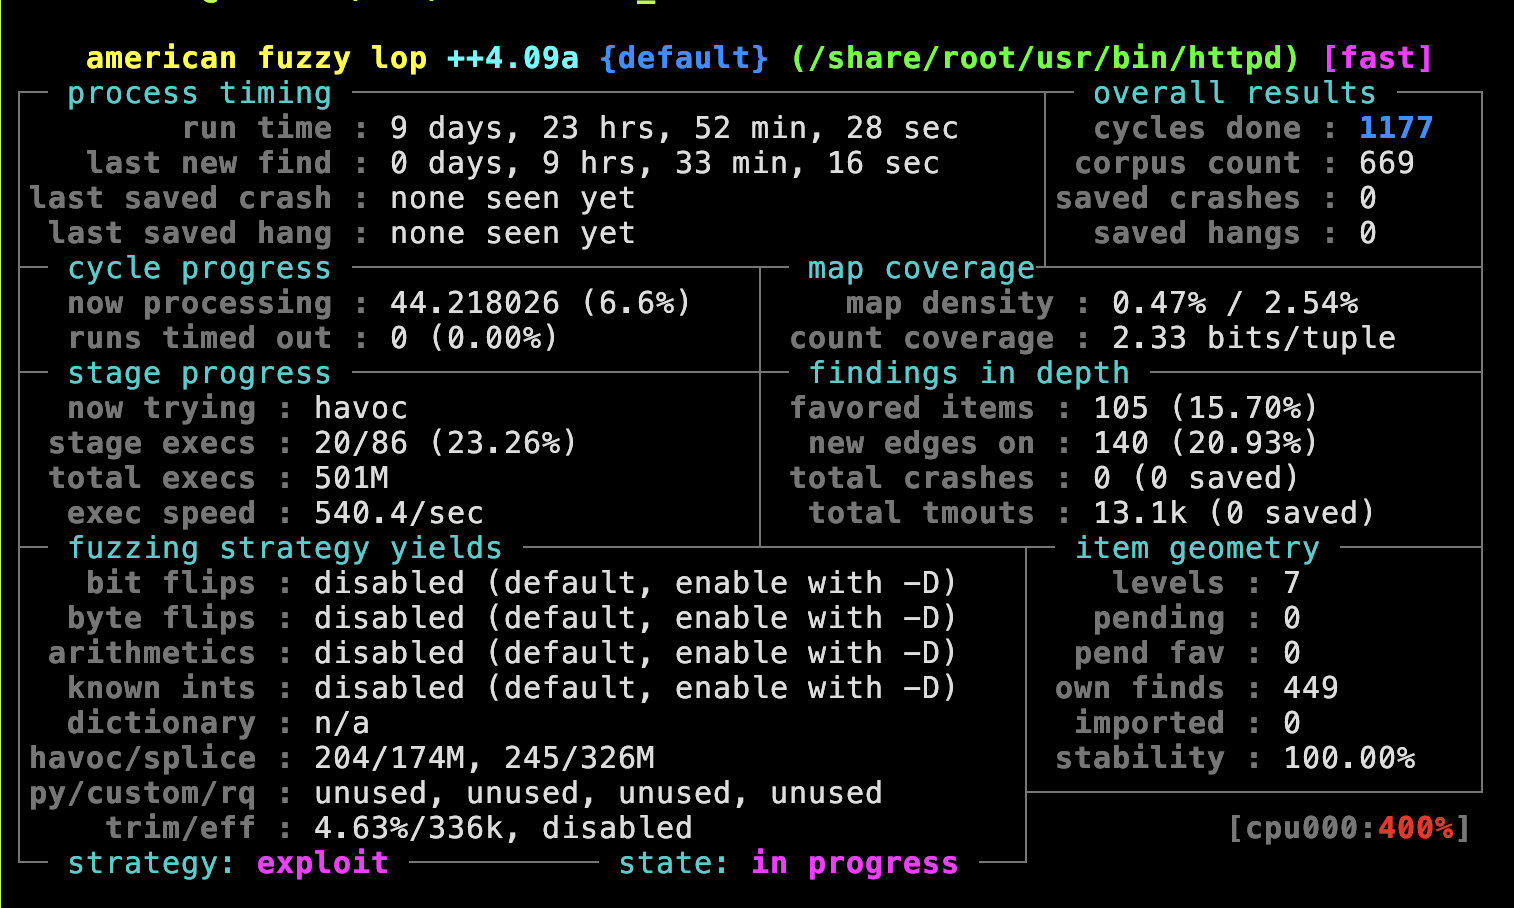 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 ffri/shadebios
PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
 innotecsystem/device-reversing
Este repo contiene write-ups de reversing de dispositivos.
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 hunt-benito/the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass
Proof-of-concept demonstrating a firmware signature verification bypass in Phison S11 SSDs, allowing attackers to re-sign modified firmware by…
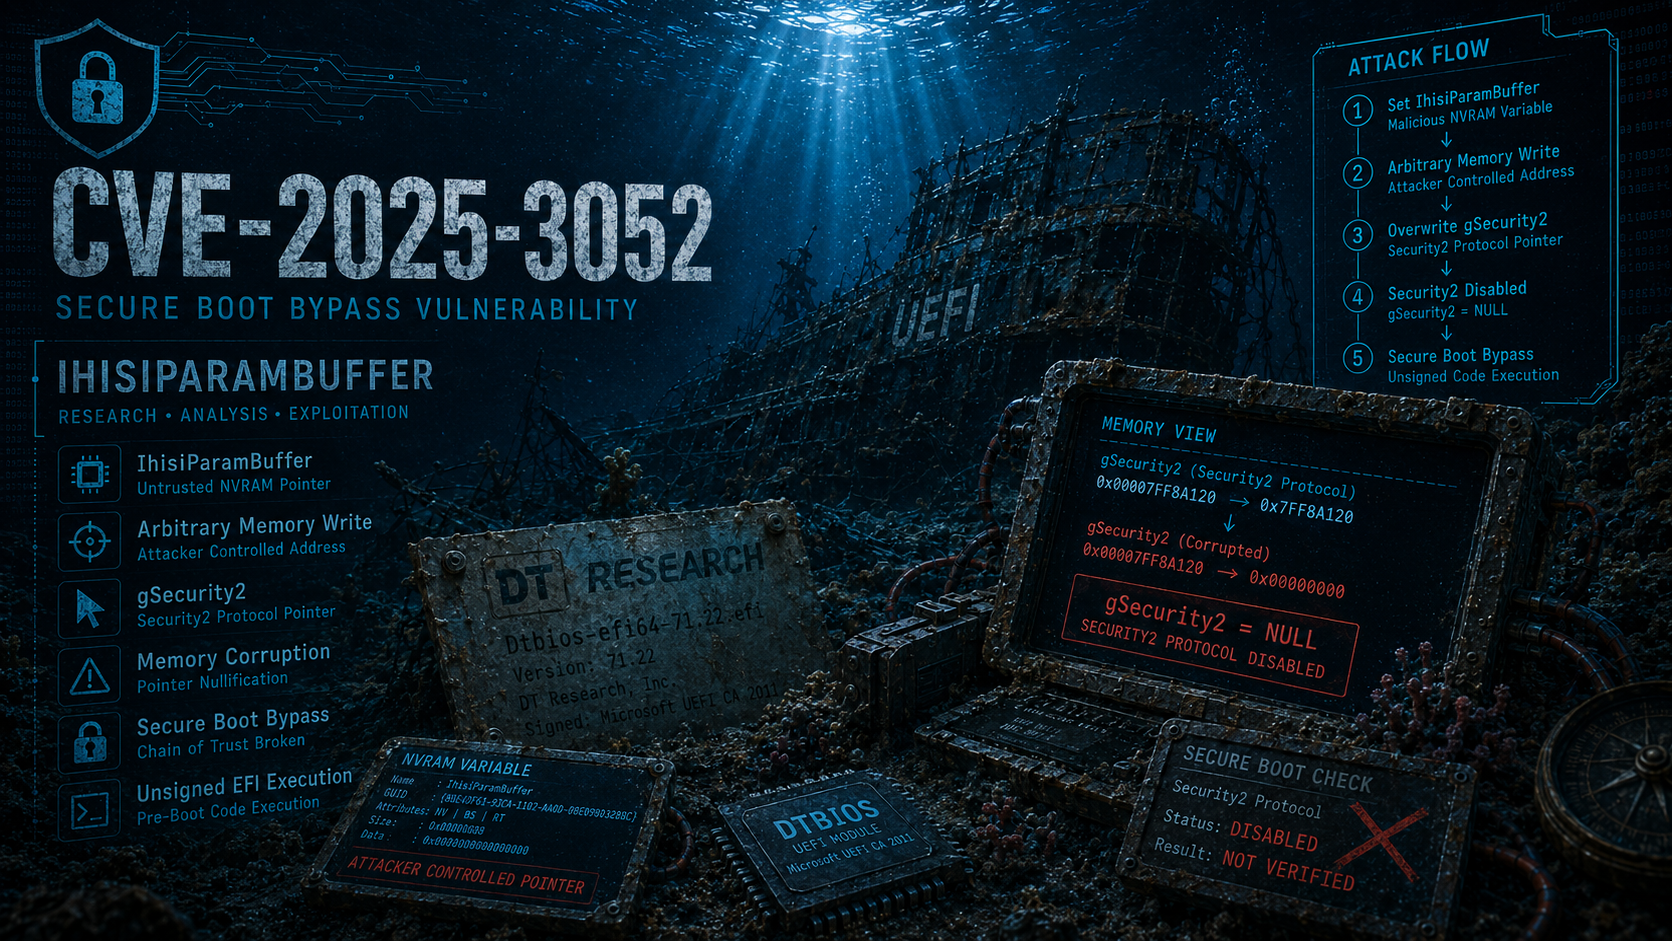 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。