cve-2026-34473-unauthenticated-dos-zte-routers

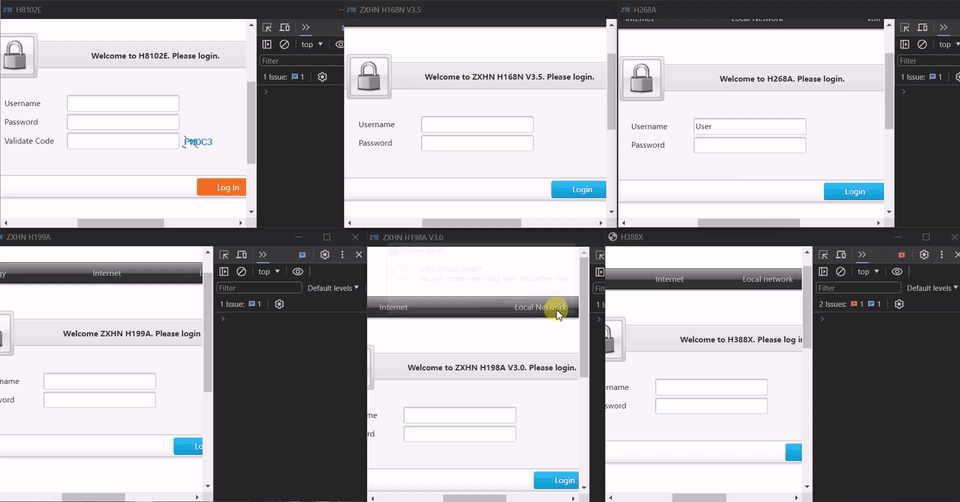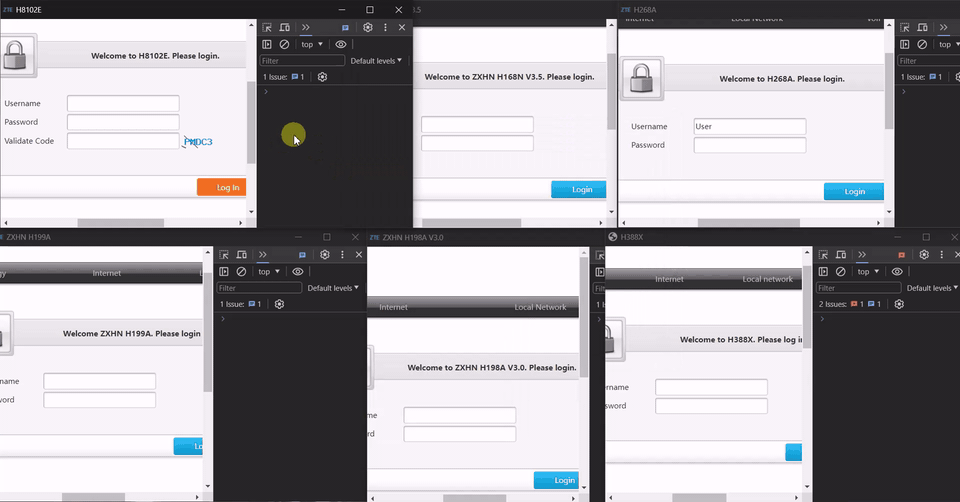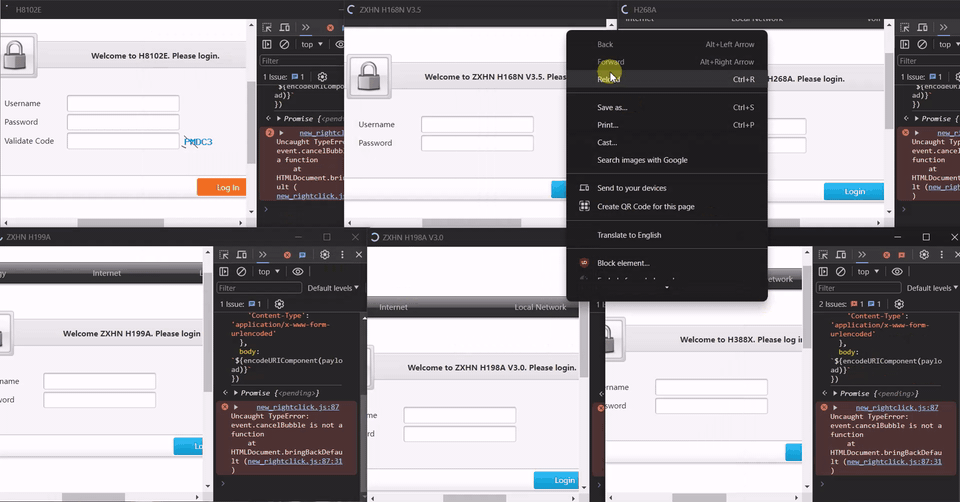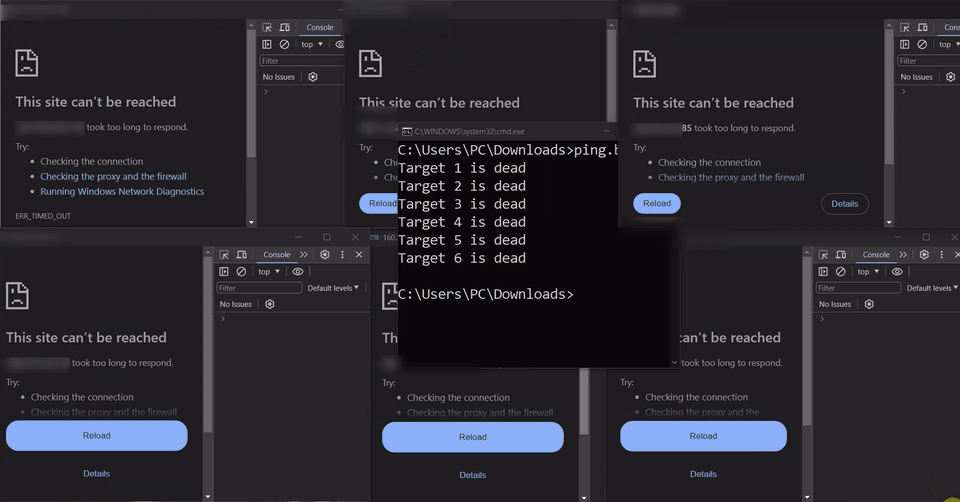
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.

Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.

Watchguard Sysa-dl file format

Bazzite plus a TPM boot attestation layer. Work in progress: builds unverified, UKI mechanism unresolved. Spec: github.com/plunder707/attested-gaming

Demonstrates a local access control bypass in AMI Aptio 5 NvLock module, allowing modification of NVRAM variables including administrator password,…

Cookie-based authentication vulnerability on Tk-Rt-Wr135G

CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)

CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)

Proof-of-concept of vulnerability found in Totolink A720R router

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…

DoS against Belkin smart plugs via crafted firmware injection

Rom-0 file password decrypter

Proof-of-concept demonstrating memory leaks in AMD SEV-SNP firmware guest message headers and CPUID request, enabling extraction of sensitive guest…

解决网络安全漏洞

Osqery extension HP BIOS WMI

KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…

CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…

Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…