go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

Emulation-based fuzzer for MSP430 firmware that finds and analyzes memory-corruption bugs with detailed crash reports and reproducible inputs.

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…

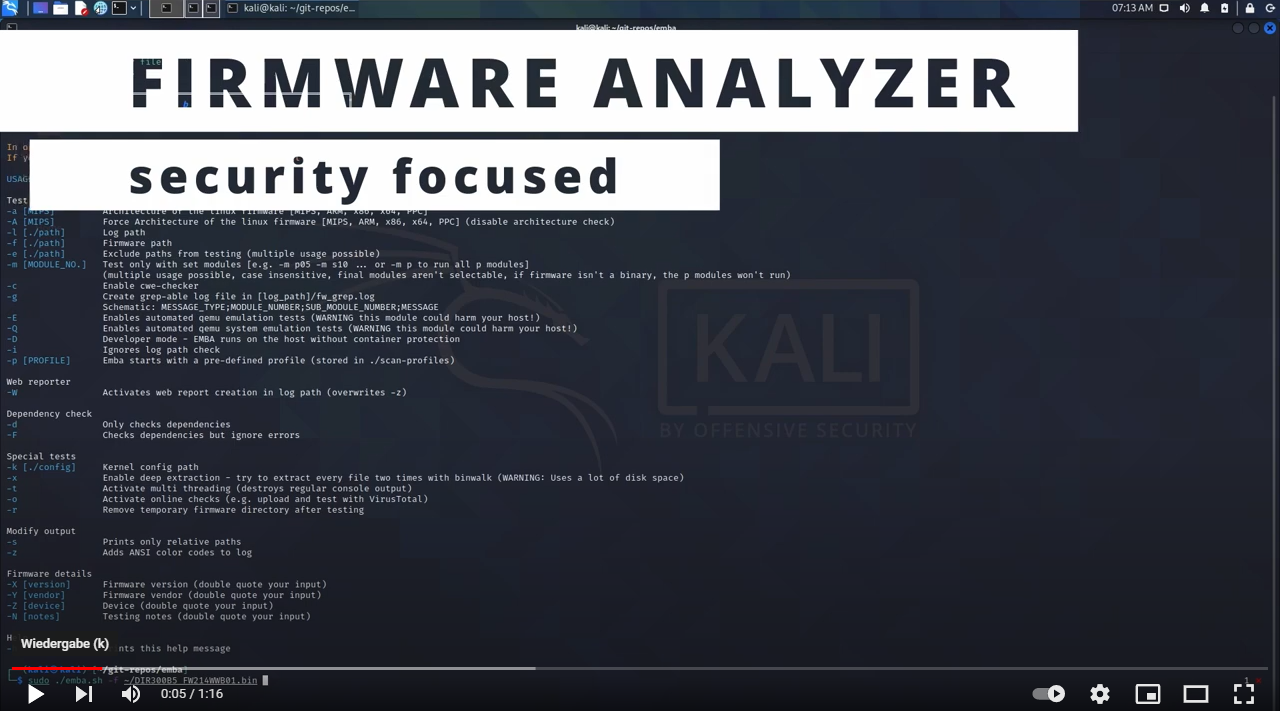
EMBA - The firmware security analyzer

Platform for emulation and dynamic analysis of Linux-based firmware

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis

A fuzzer for full VM kernel/driver targets

Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…

This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…

The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.

The IoT Security Testing Guide (ISTG) provides a comprehensive methodology for penetration tests in the IoT field, offering flexibility to adapt…

Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.

Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.

Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…

ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…

Proof-of-concept demonstrating memory leaks in AMD SEV-SNP firmware guest message headers and CPUID request, enabling extraction of sensitive guest…