

Archived
CVE-2017-2751
 badersz/cve-2017-2751
Mini-paper on CVE-2017-2751, HP EFI password extraction.
educationexploitationfirmware-analysis+3
badersz/cve-2017-2751Mini-paper on CVE-2017-2751, HP EFI password extraction.
 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
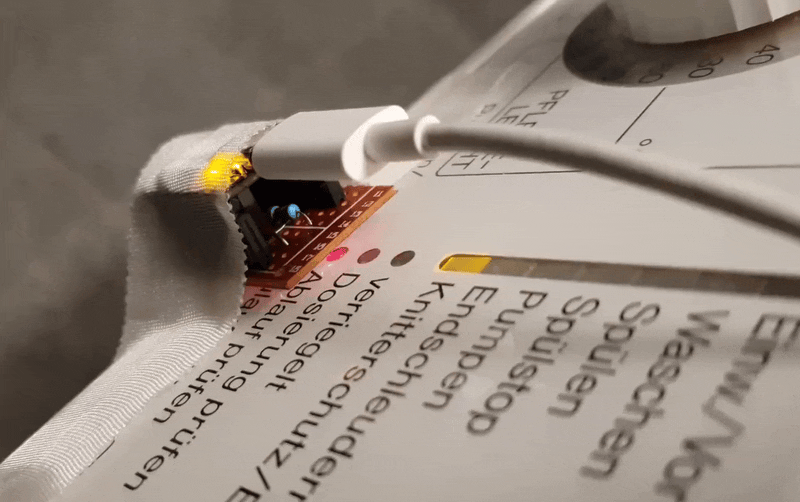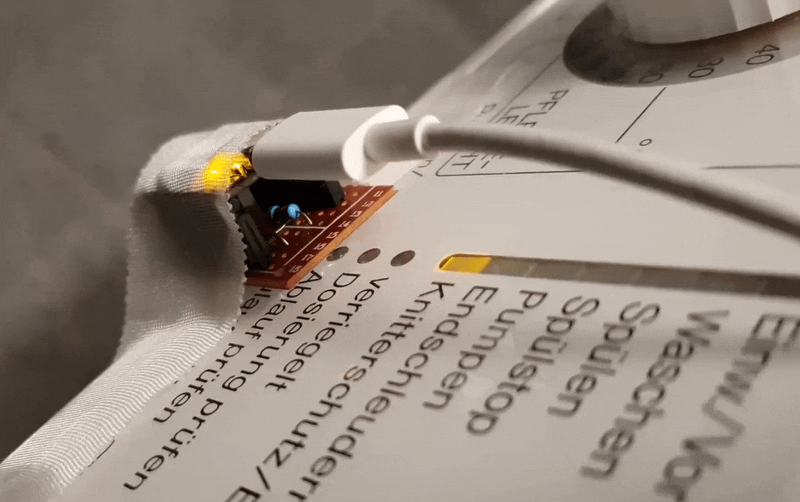 medusalix/freemdu
Open hardware and software tools for communicating with Miele appliances via their optical diagnostic interface
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
 baiyibai/pico-usb-wifi
Firmware for Raspberry Pi Pico W that creates a driverless USB Wi-Fi adapter with transparent layer-2 bridging, WPA2/WPA3 authentication, and…
 hydrausb3/wch-ch56x-lib
Library for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 jaydcarlson/c2-printf
Print trace messages over a Silicon Labs C2 debugger connection
 minanagehsalalma/cve-2026-6837-zyxel-export-cgi-command-injection
Public writeup, PoC, and emulation materials for CVE-2026-6837 affecting Zyxel export-cgi PKCS#12 export handling.
 gadorach/vankyo-s30-bootloader-unlock
Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
 supermagnum/galdralag-firmware
A cryptographic framework for Baochip-1x .
 plunder707/attestos
Bazzite plus a TPM boot attestation layer. Work in progress: builds unverified, UKI mechanism unresolved. Spec: github.com/plunder707/attested-gaming