

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
angr/angrA powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
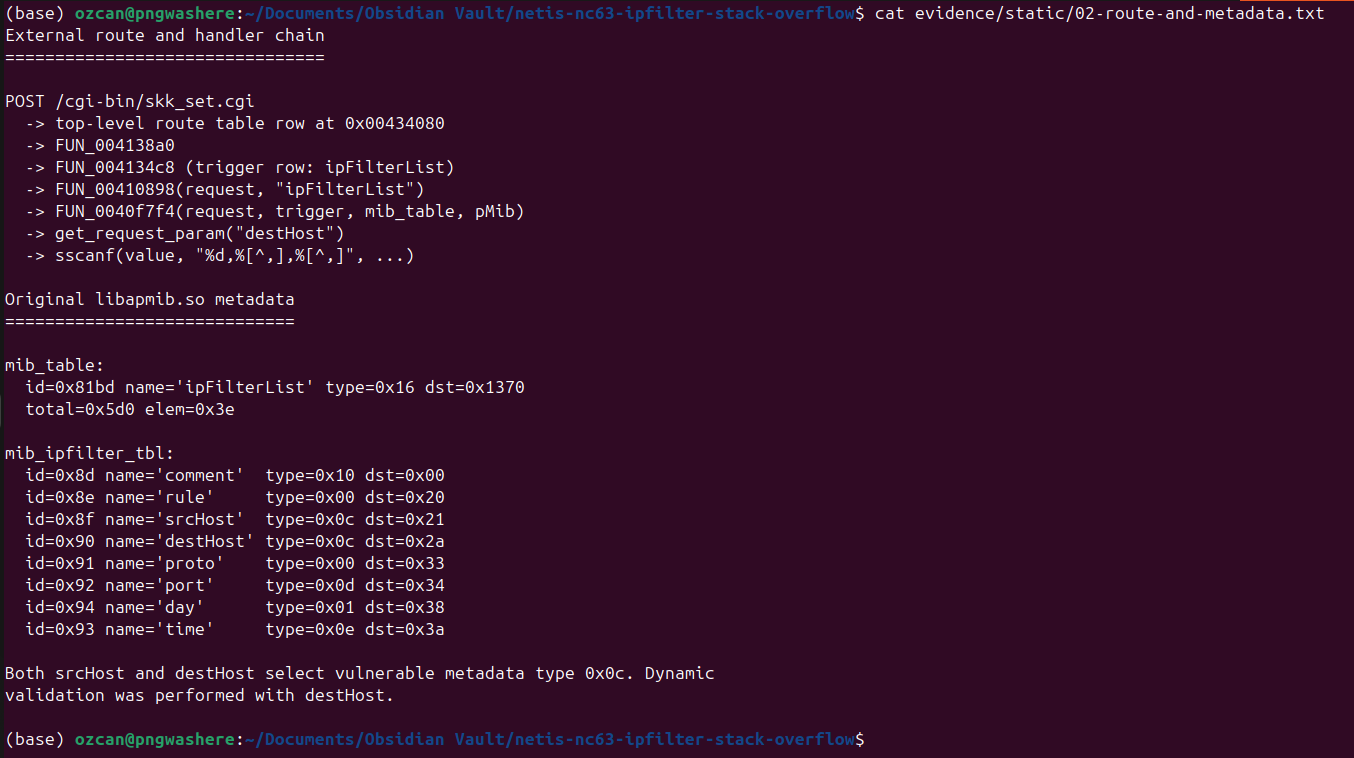 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 ozcanpng/cve-2026-76070
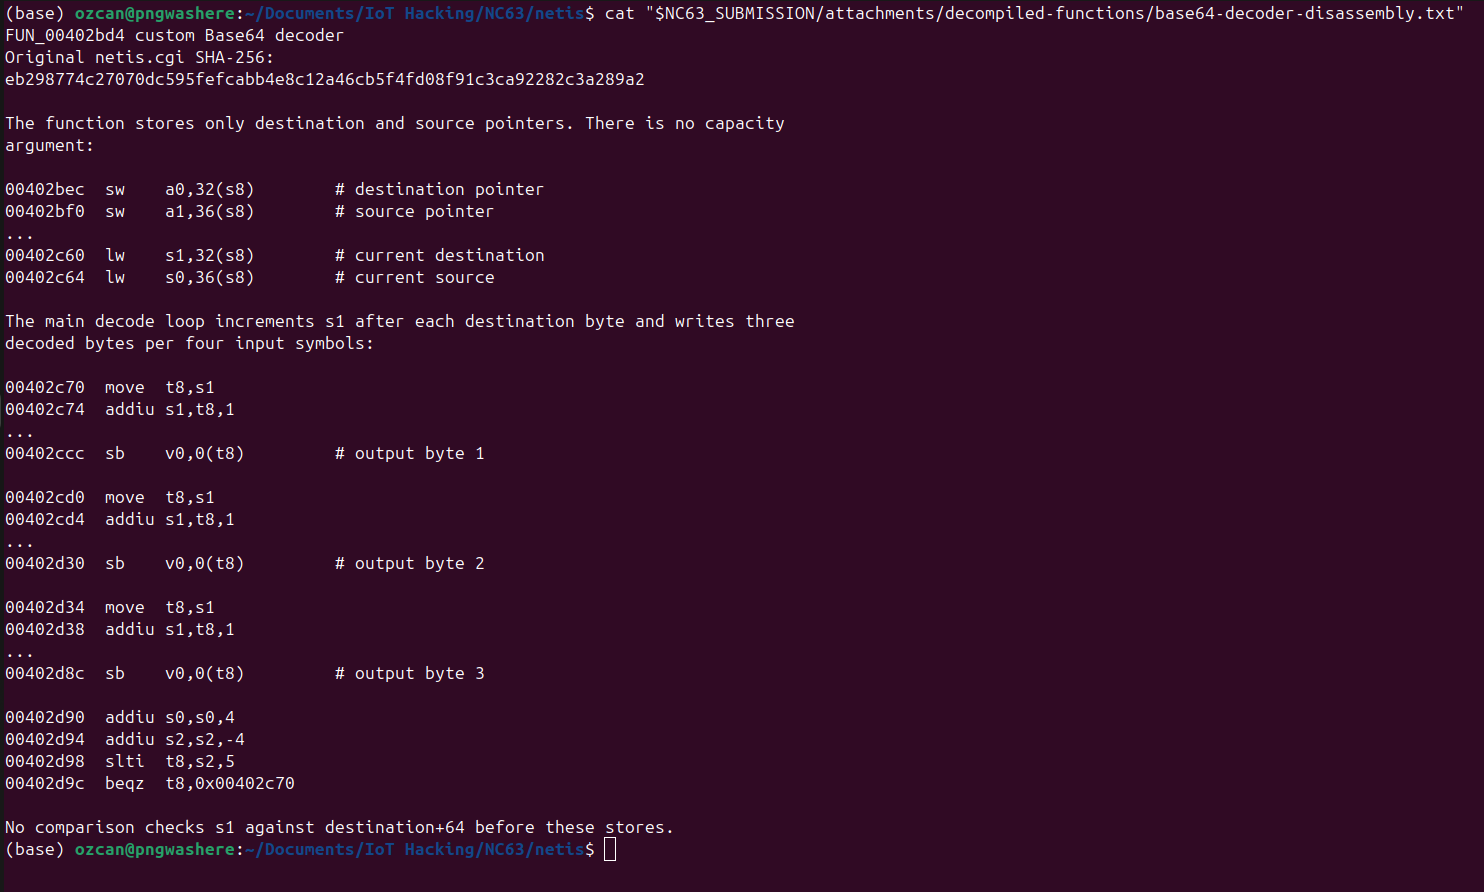
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 kemrec/cve-2025-0324-axis-vapix-privesc
Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…