
CVE-2024-56426
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
android-securitybinary-exploitationembedded-systems-security+7
4
xcracker000/cve-2024-56426CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
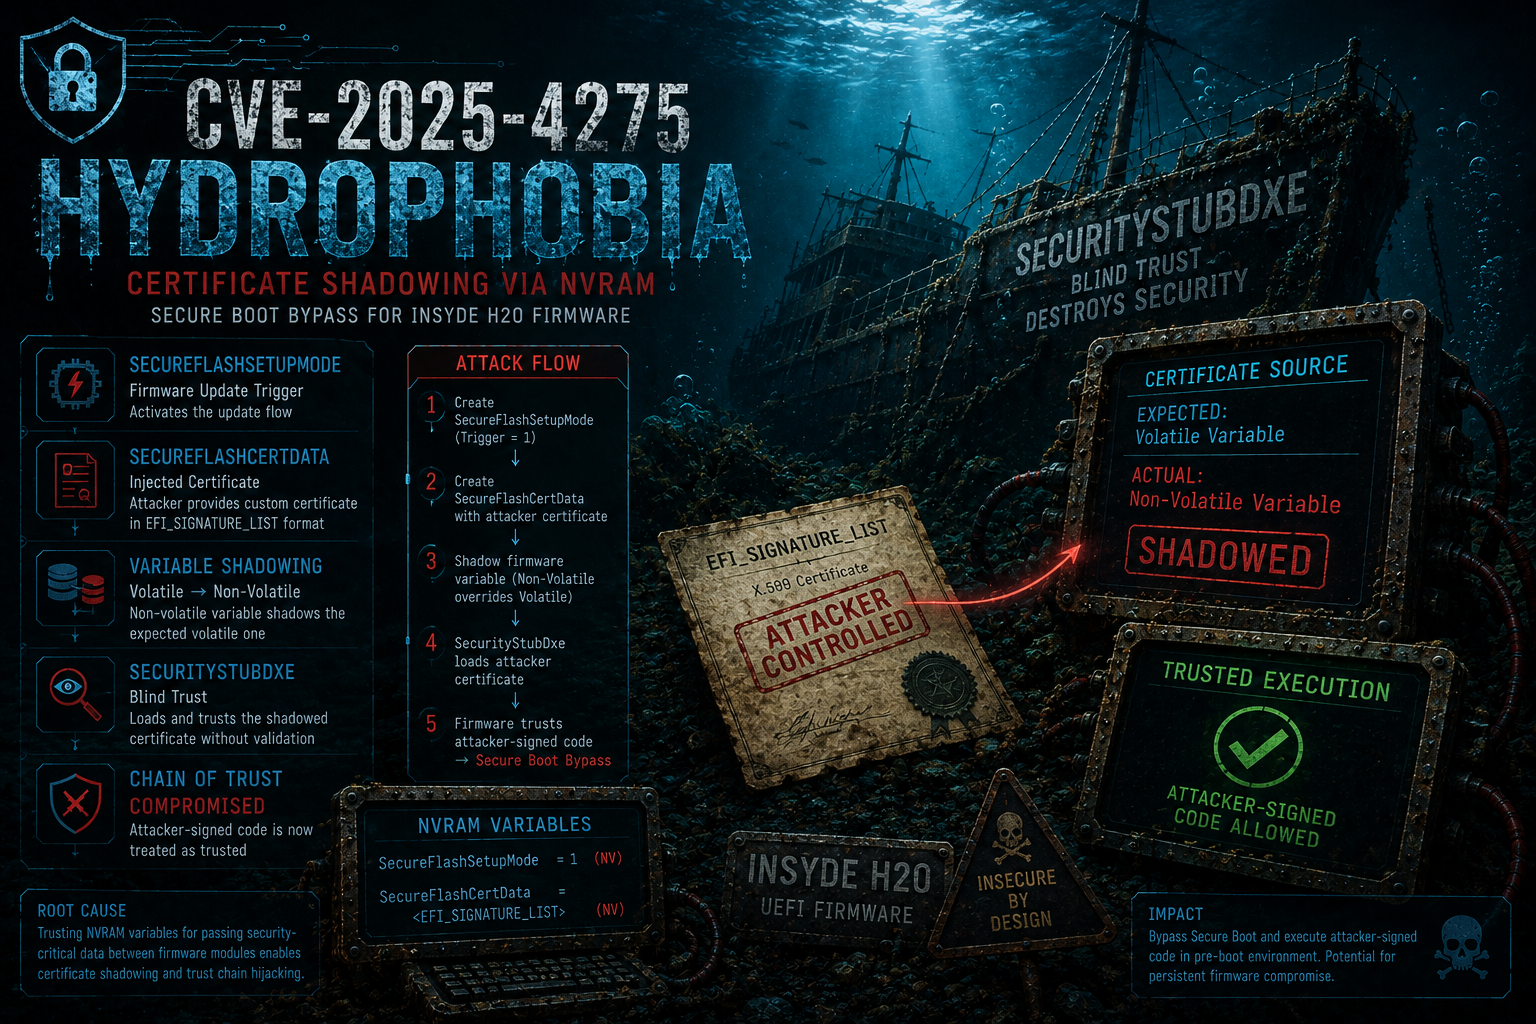 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 dudux/routerfirmwares
A bunch of routers firmware images. Principally those that are not available and they do need to be extracted via JTAG, UART, desoldering flash or…
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 mercul1ninna/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
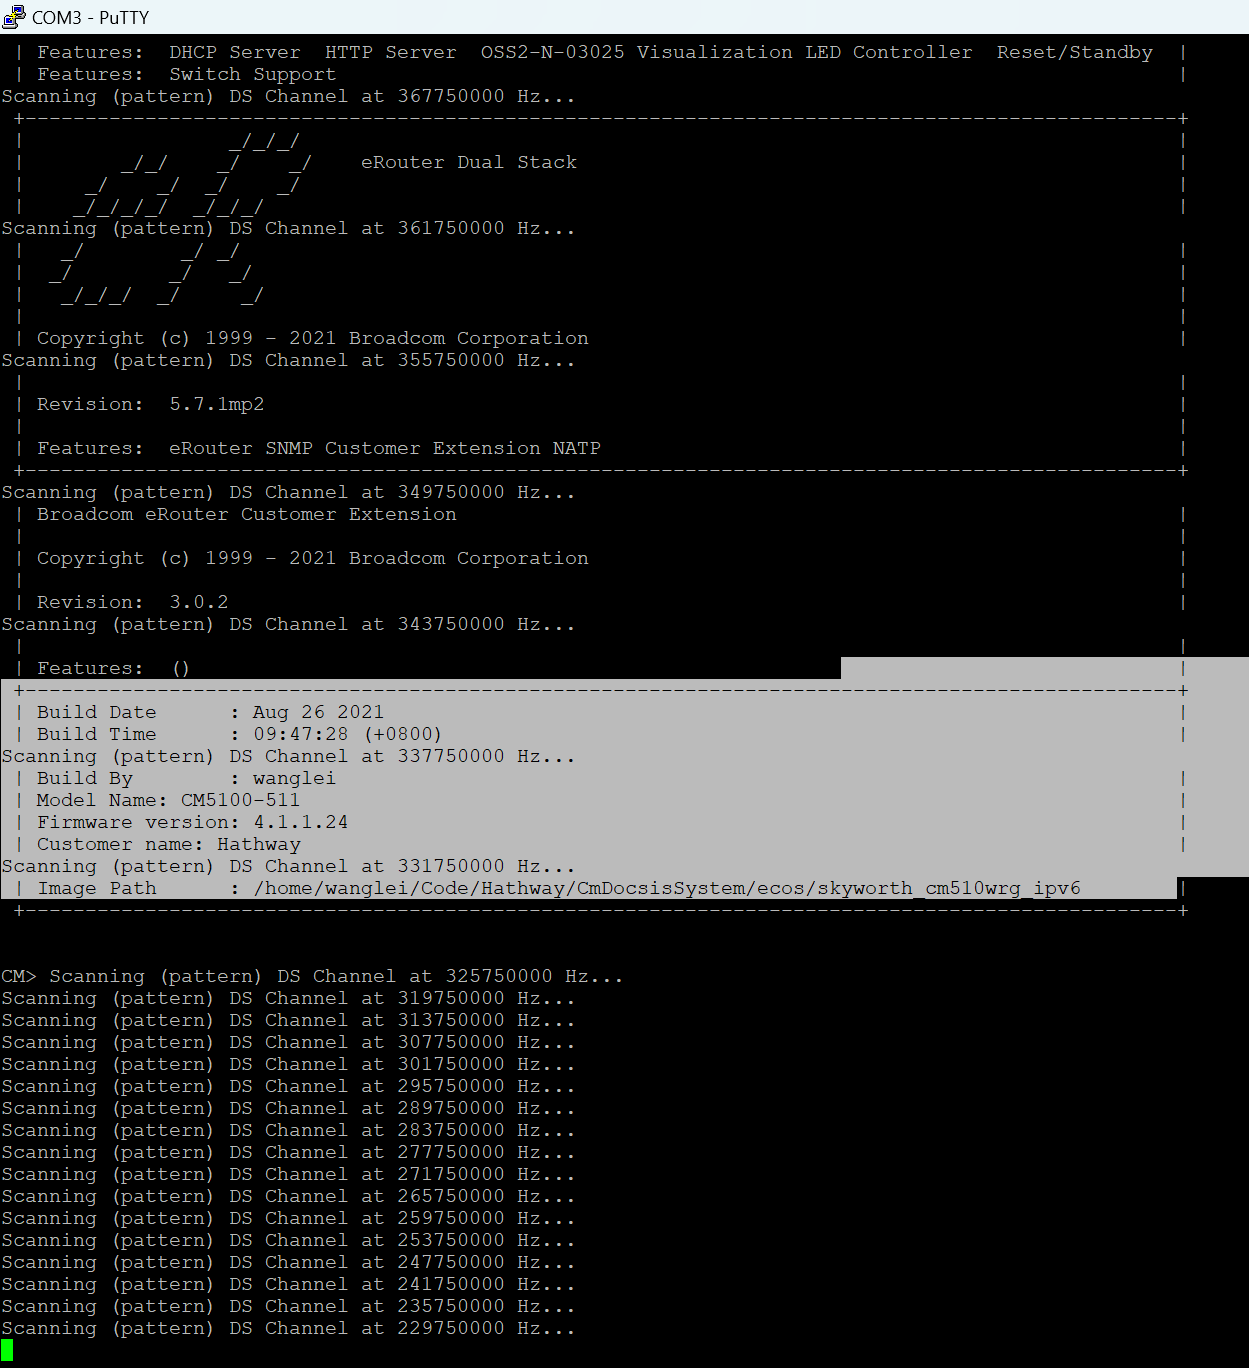 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
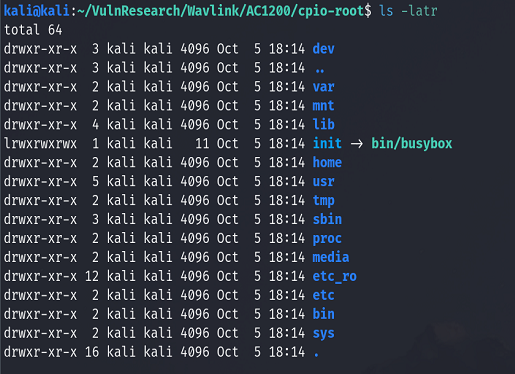 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 seifallahhomrani1/cve-2023-0861-poc
Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers
 lukejenkins/cve-2022-24693
Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
 xchwarze/wifi-pineapple-cloner-builds
Build repo from Universal Wifi pineapple hardware cloner
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 codykociemba/nolongerevil-thermostat
Breathe fresh life into your bricked Nest, now with 100% less evil!
 donfanning/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
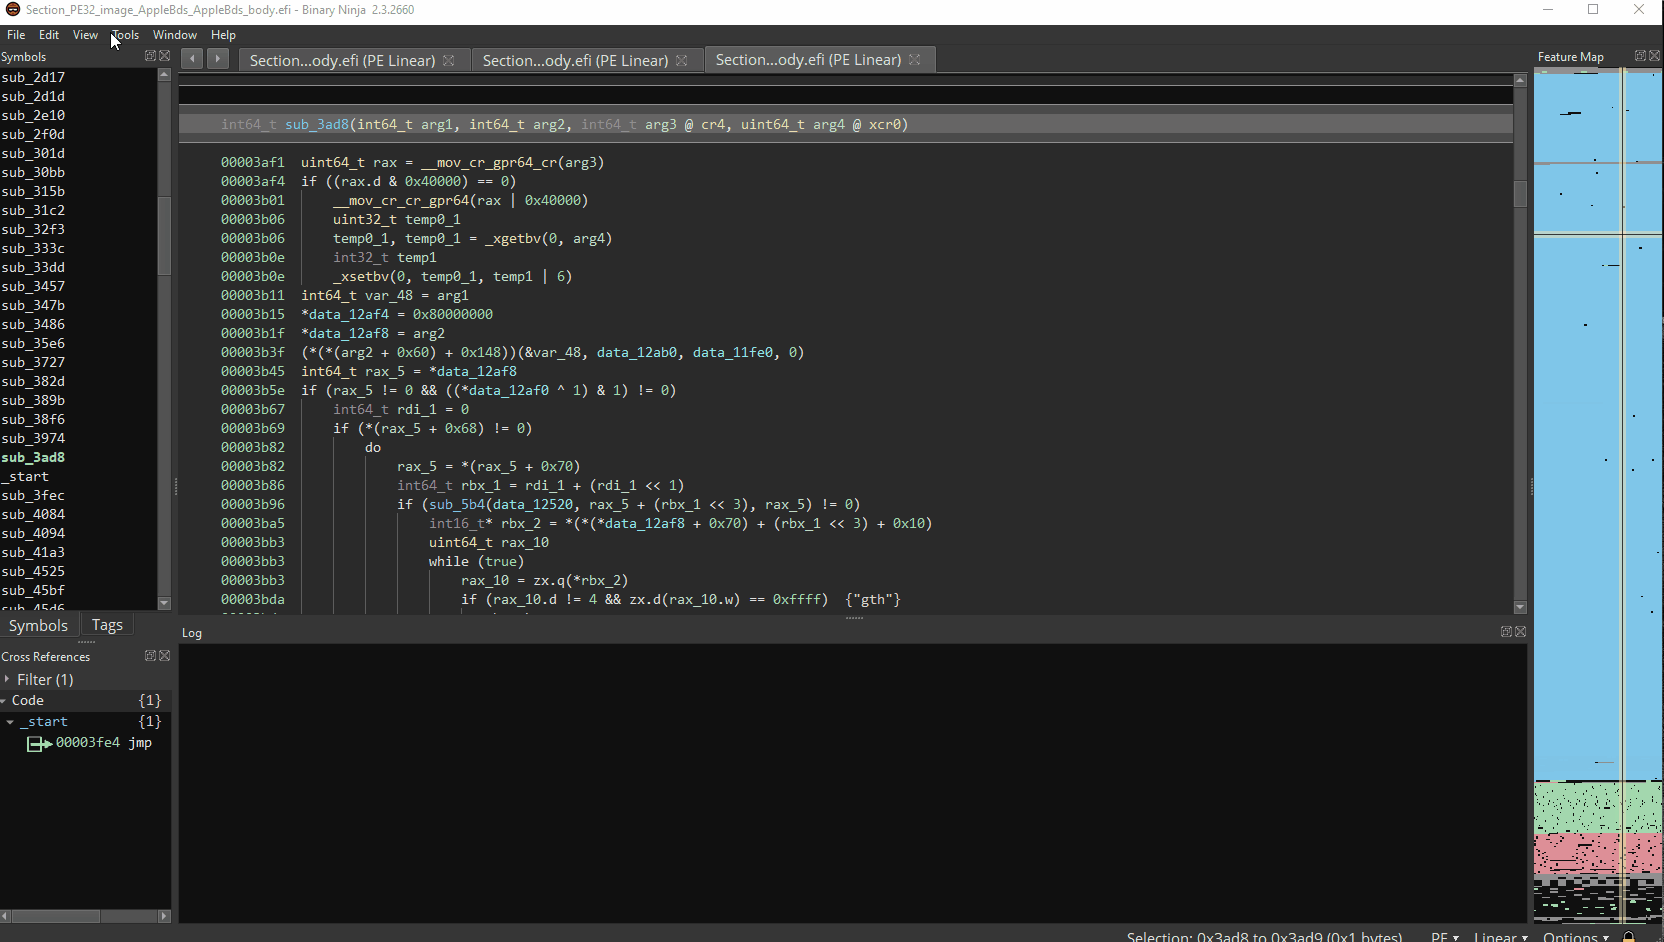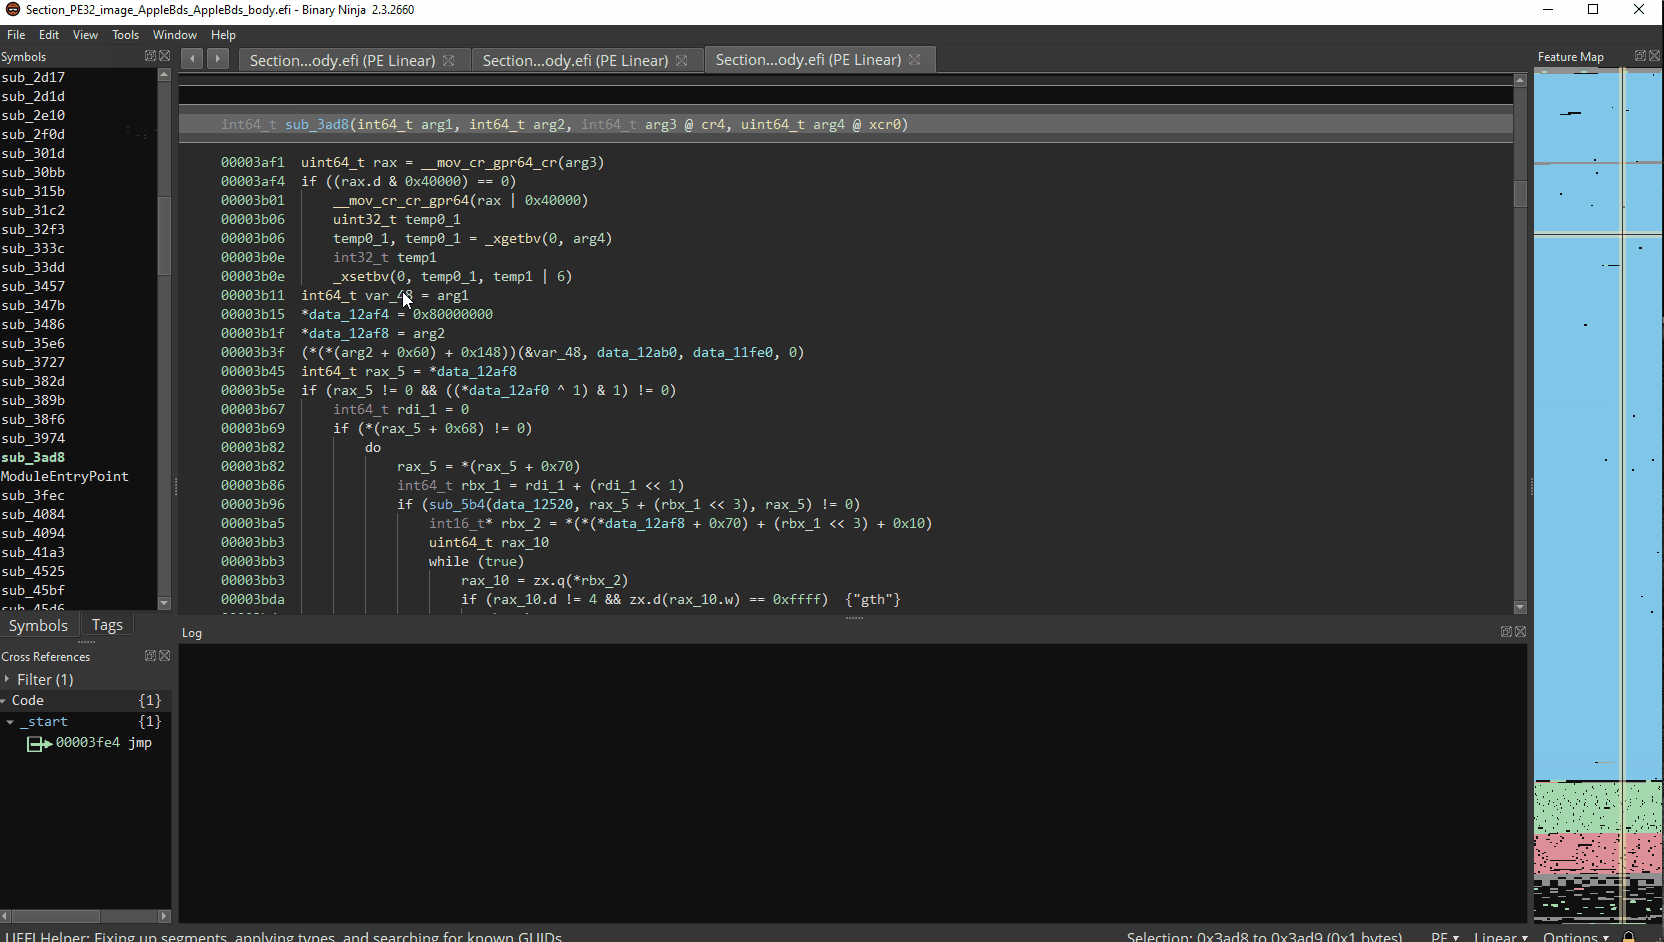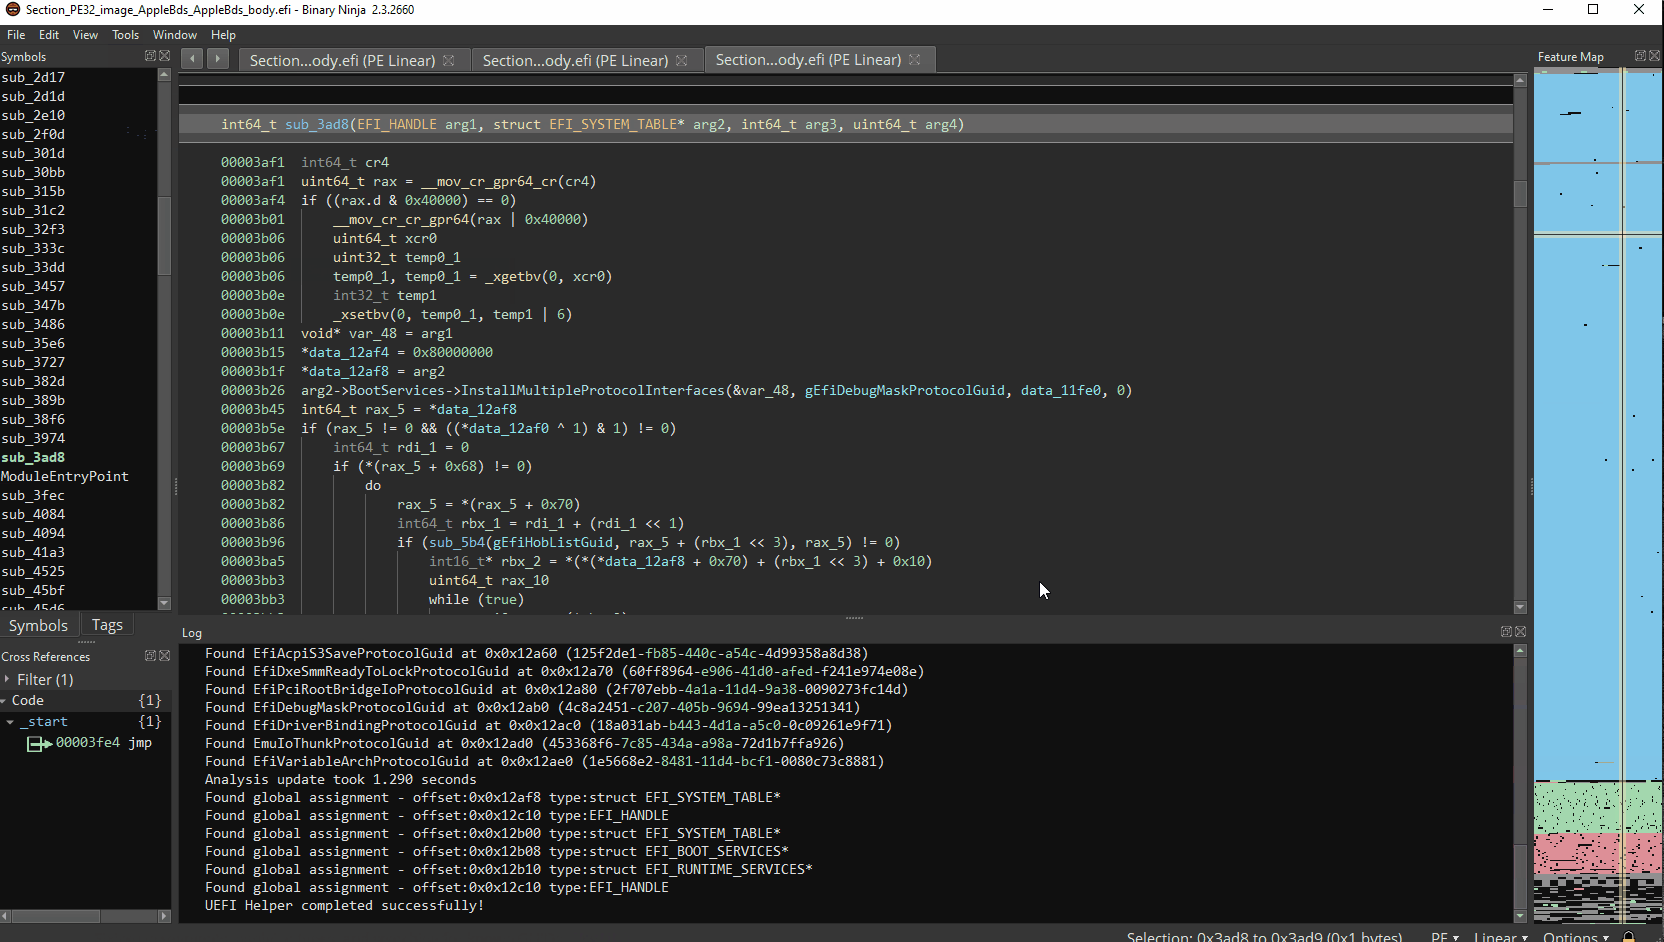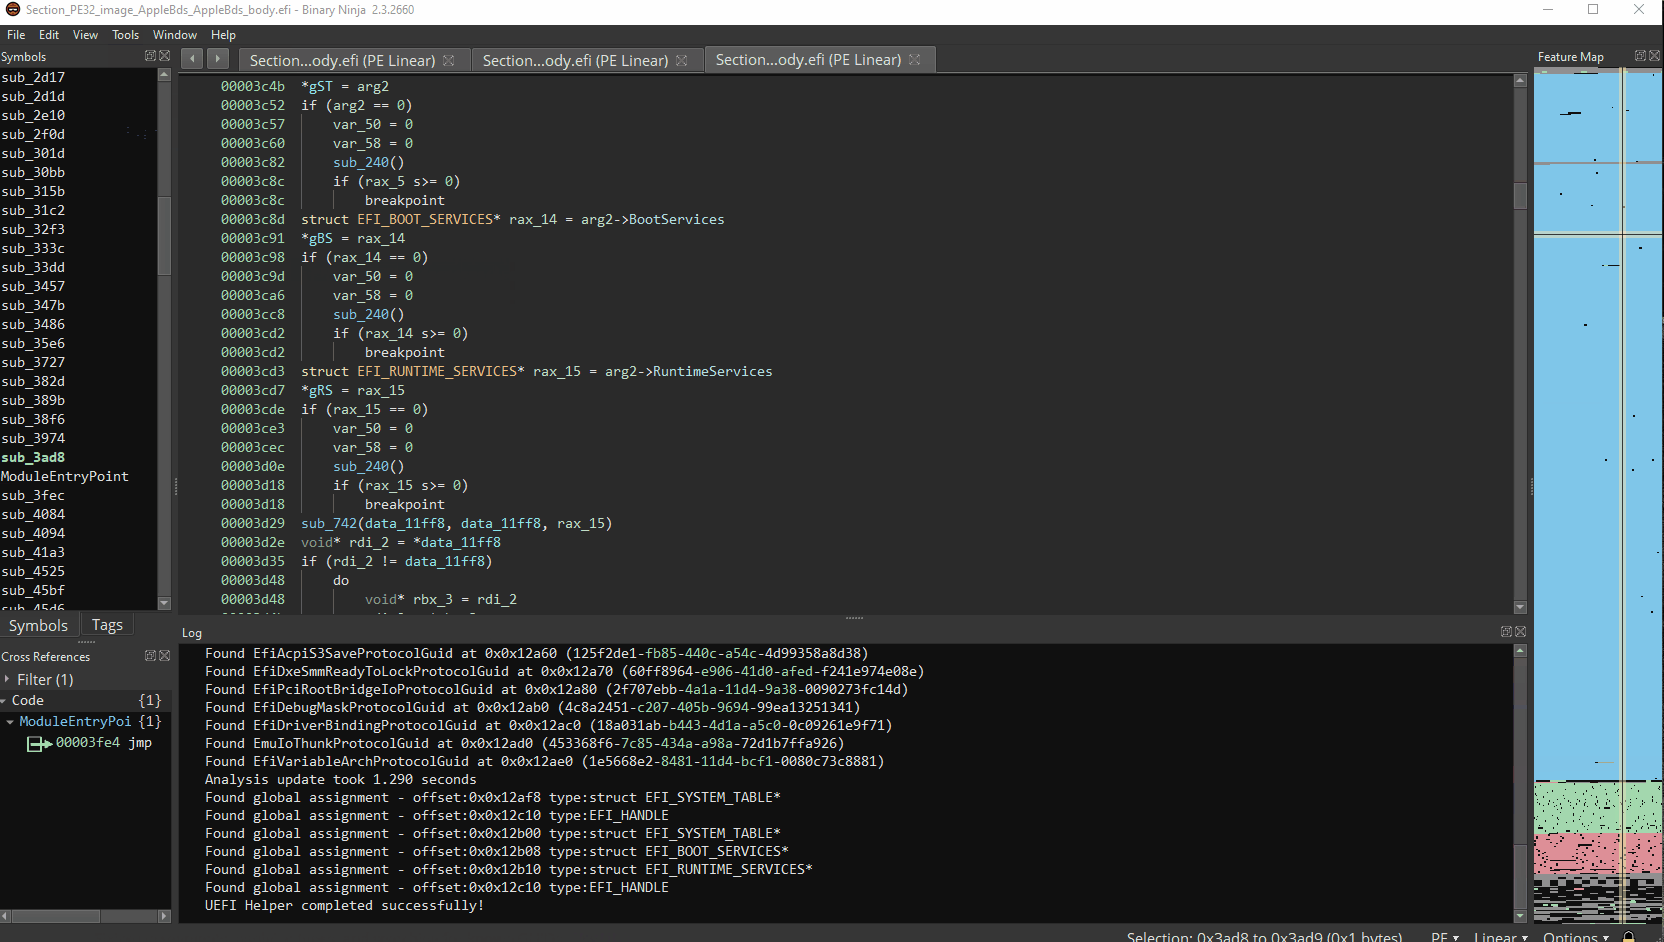 zznop/bn-uefi-helper
Helper plugin for analyzing UEFI firmware
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
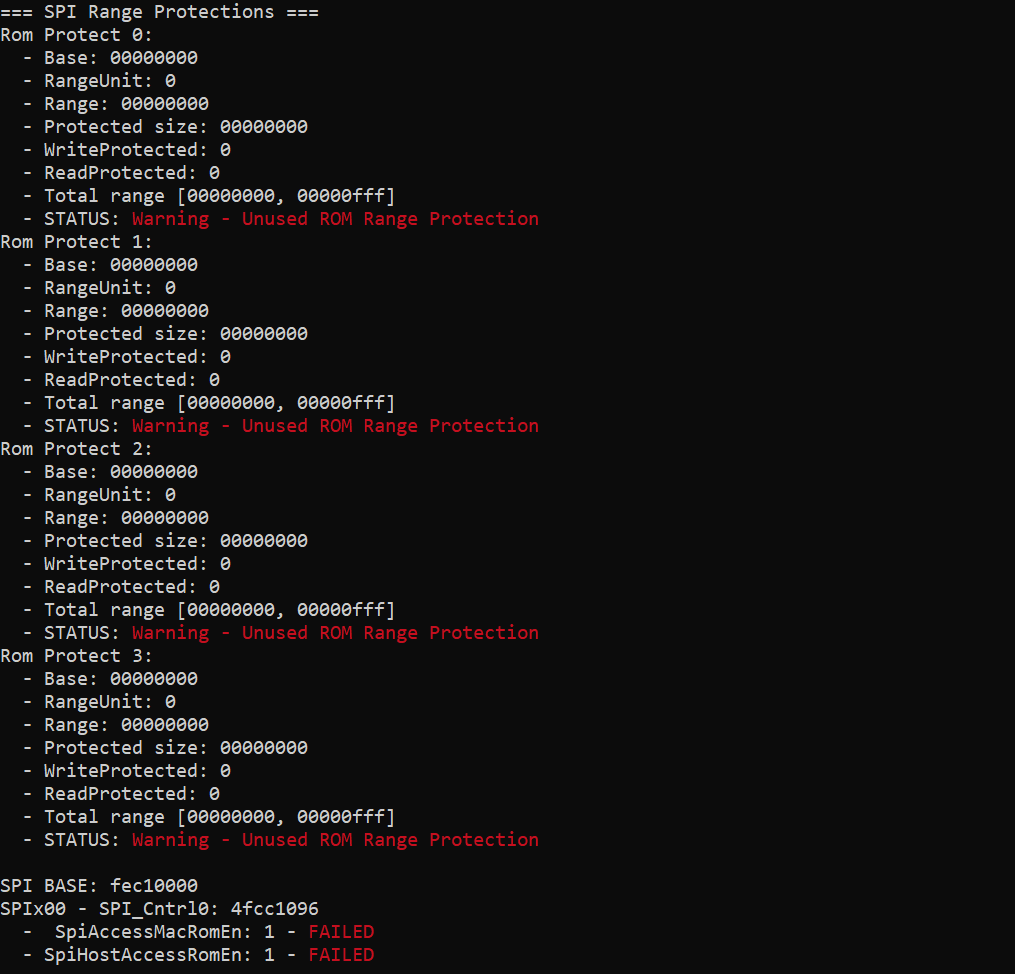 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…