
ABrake27
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
binary-analysiseducationexploitation+8
vvirei333/abrake27iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 innotecsystem/device-reversing
Este repo contiene write-ups de reversing de dispositivos.
 raspberrypi/rp2350_hacking_challenge
Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 hunt-benito/the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass
Proof-of-concept demonstrating a firmware signature verification bypass in Phison S11 SSDs, allowing attackers to re-sign modified firmware by…
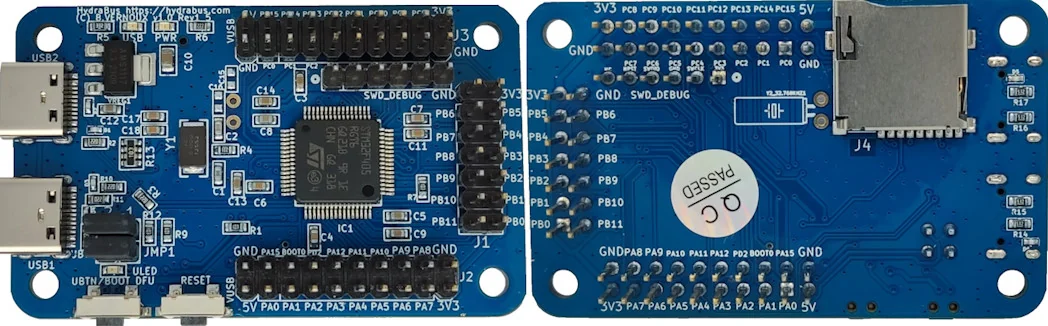 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
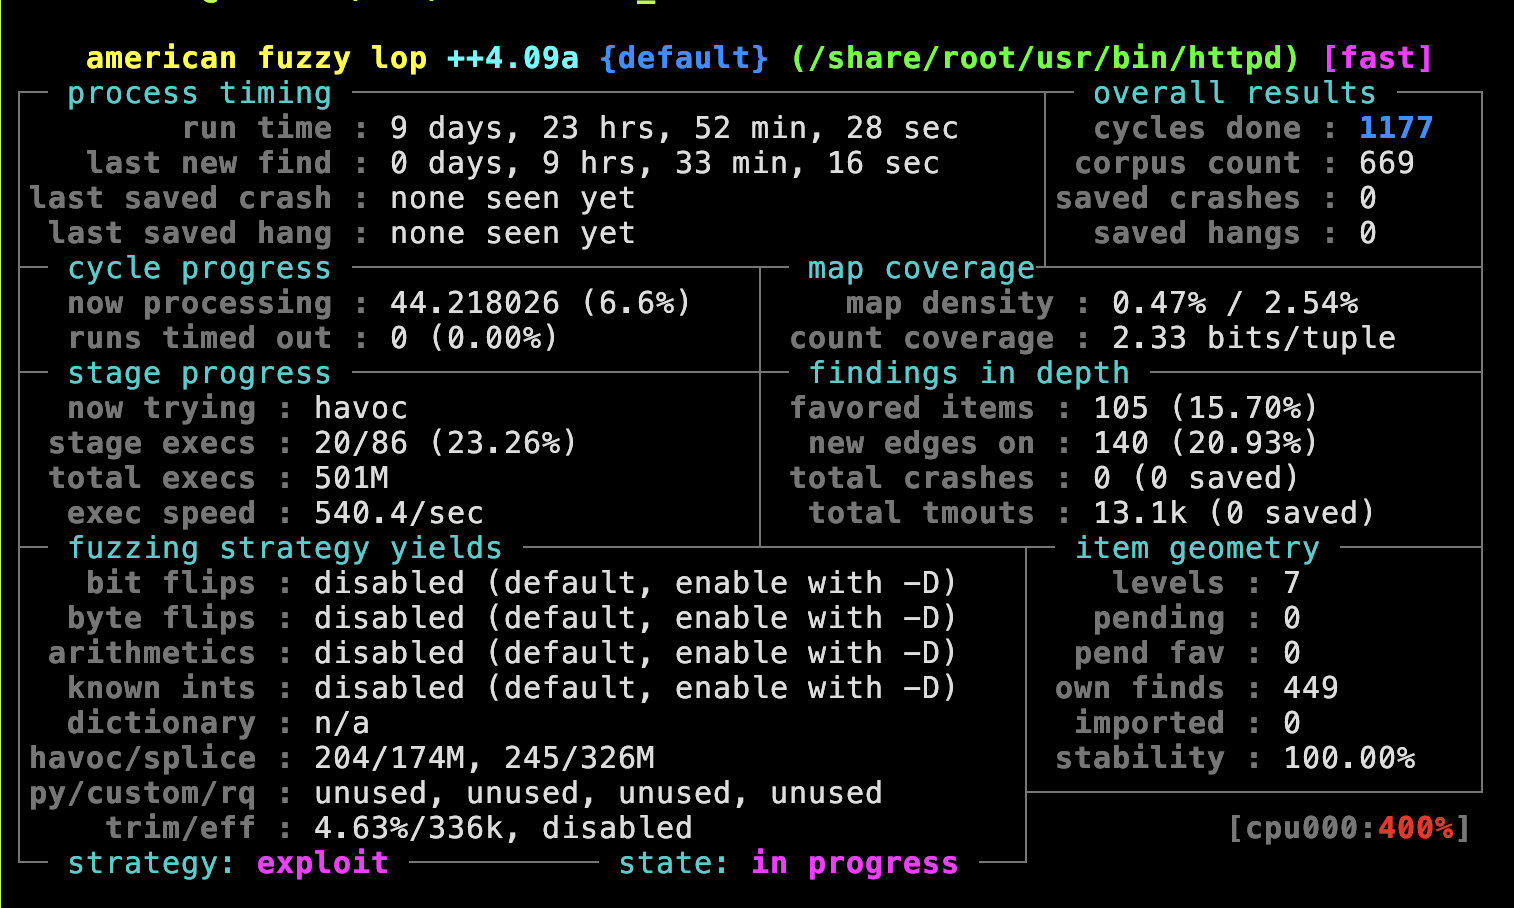 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 george0papasotiriou/cve-2026-21009-ecdsa-nonce-reuse-in-iot-firmware-signing
Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…
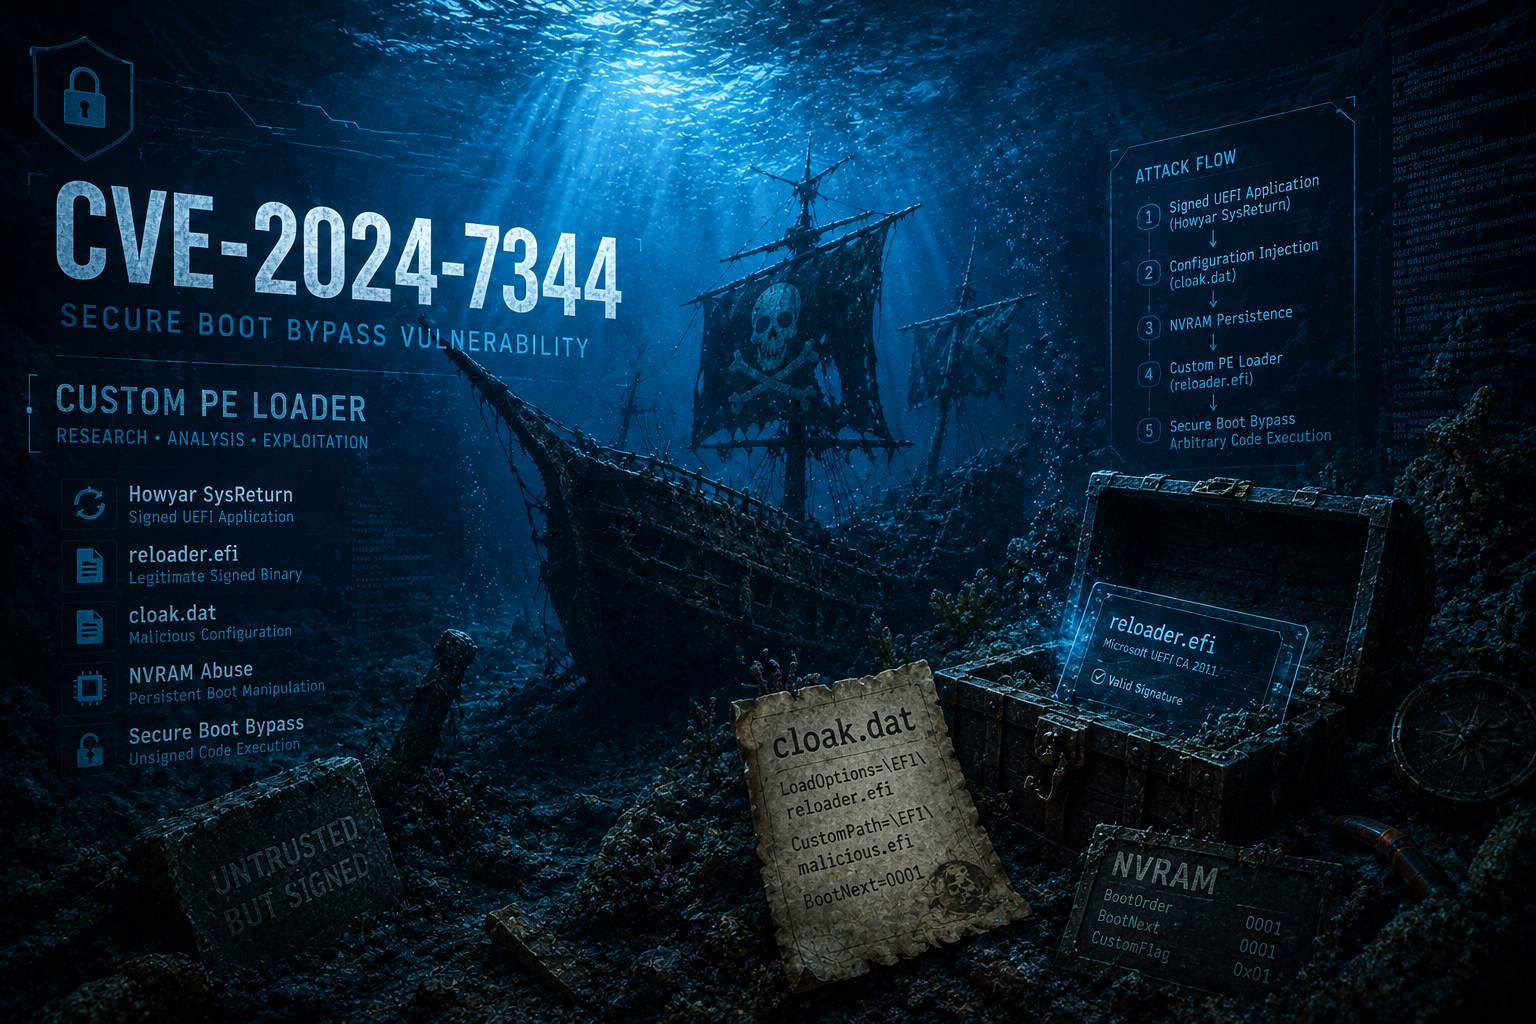 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
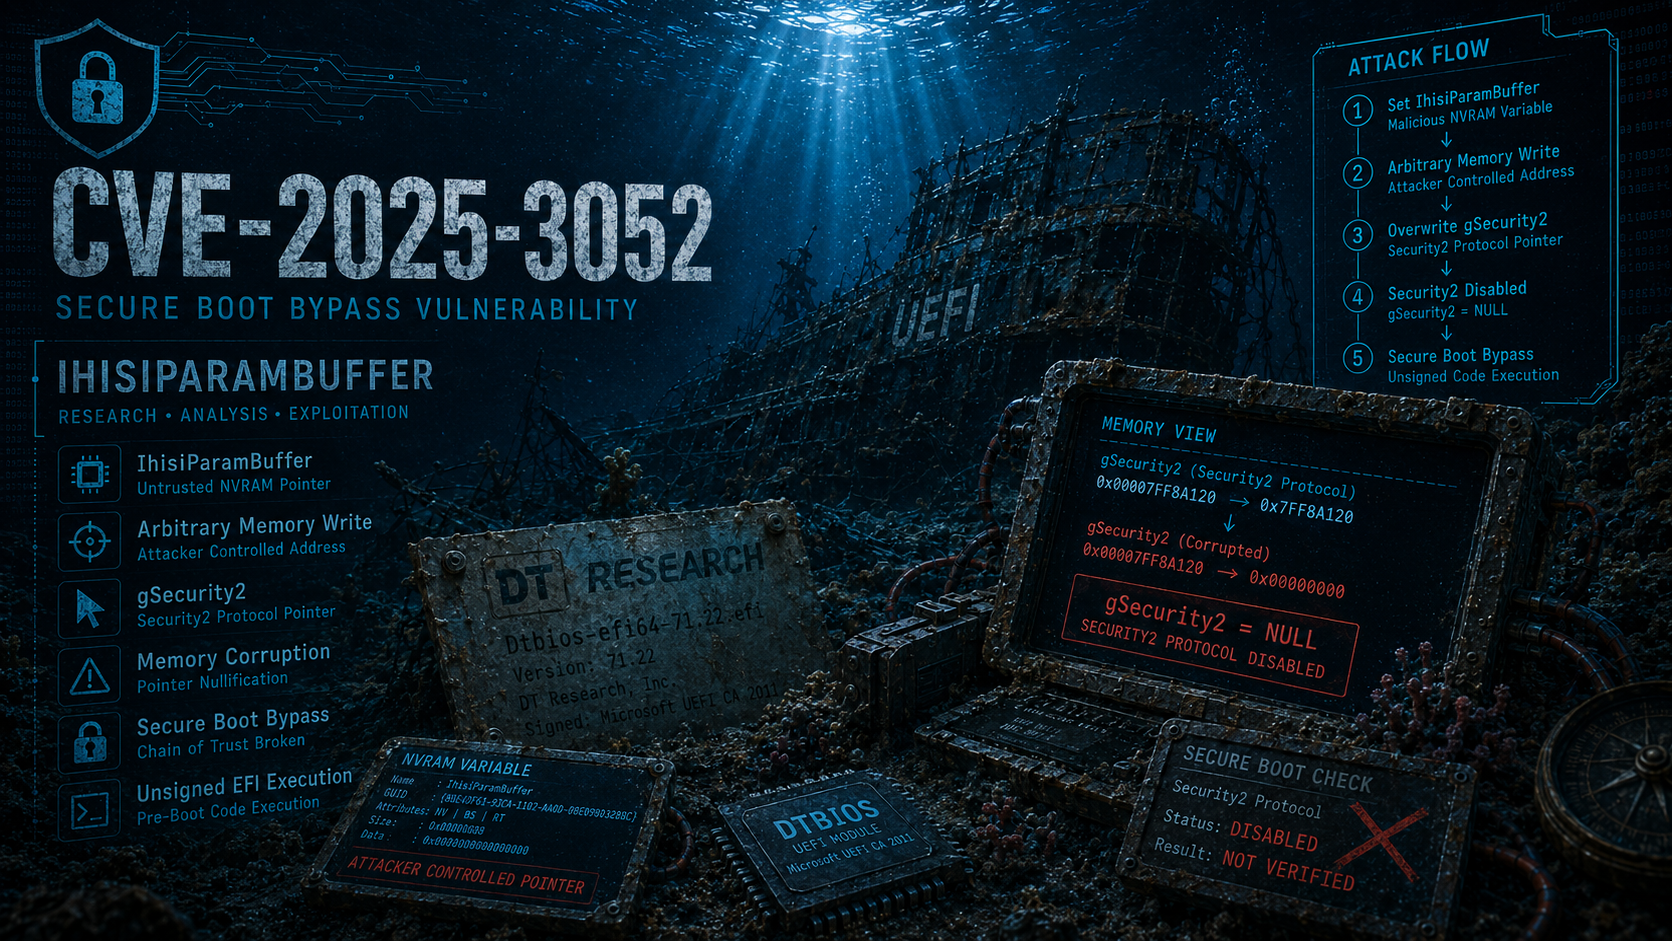 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
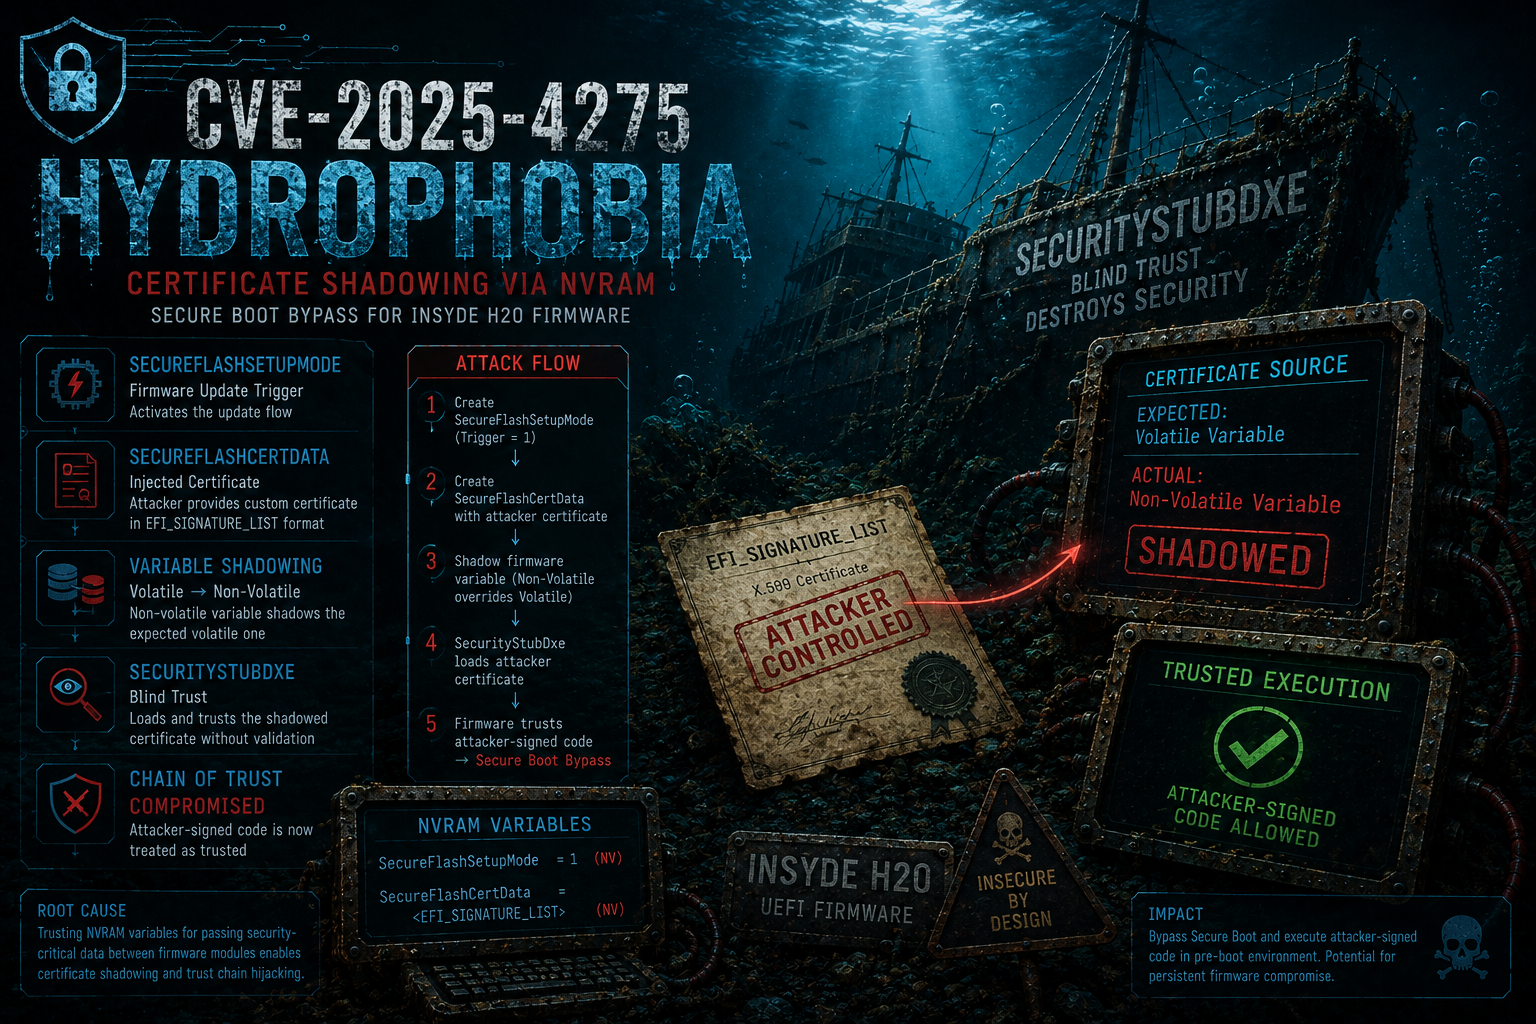 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
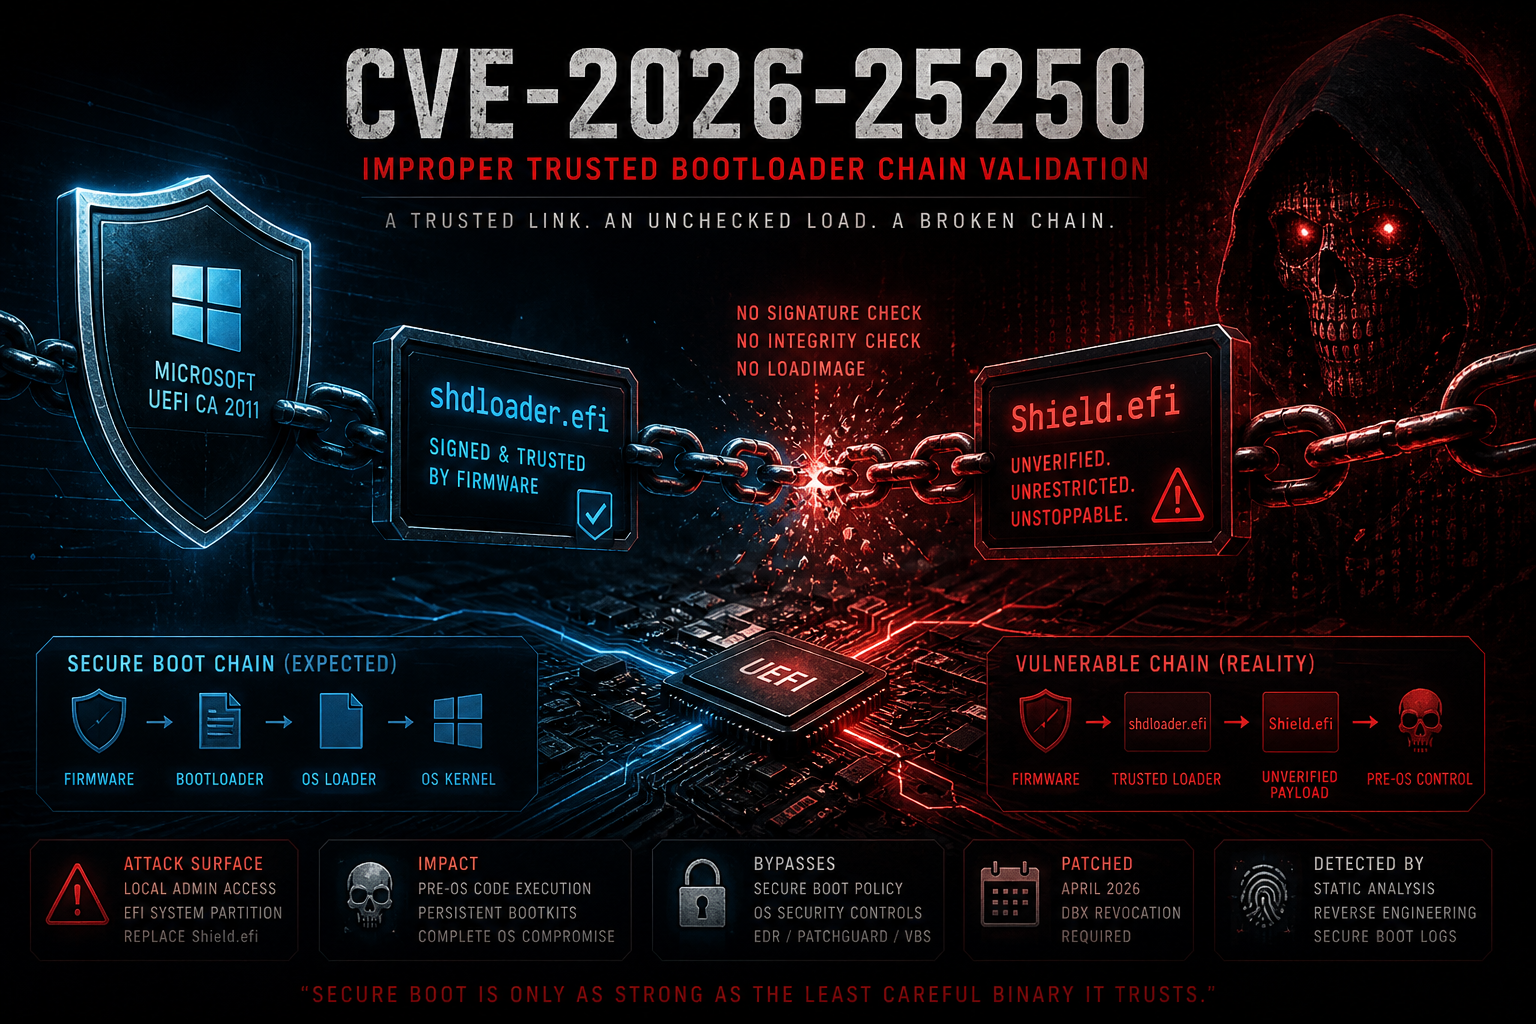 themalwareguardian/cve-2026-25250
Analysis and exploit for CVE-2026-25250, a Secure Boot bypass in Horizon DataSys Reboot Restore where shdloader.efi loads Shield.efi without…
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.