cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…

Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.

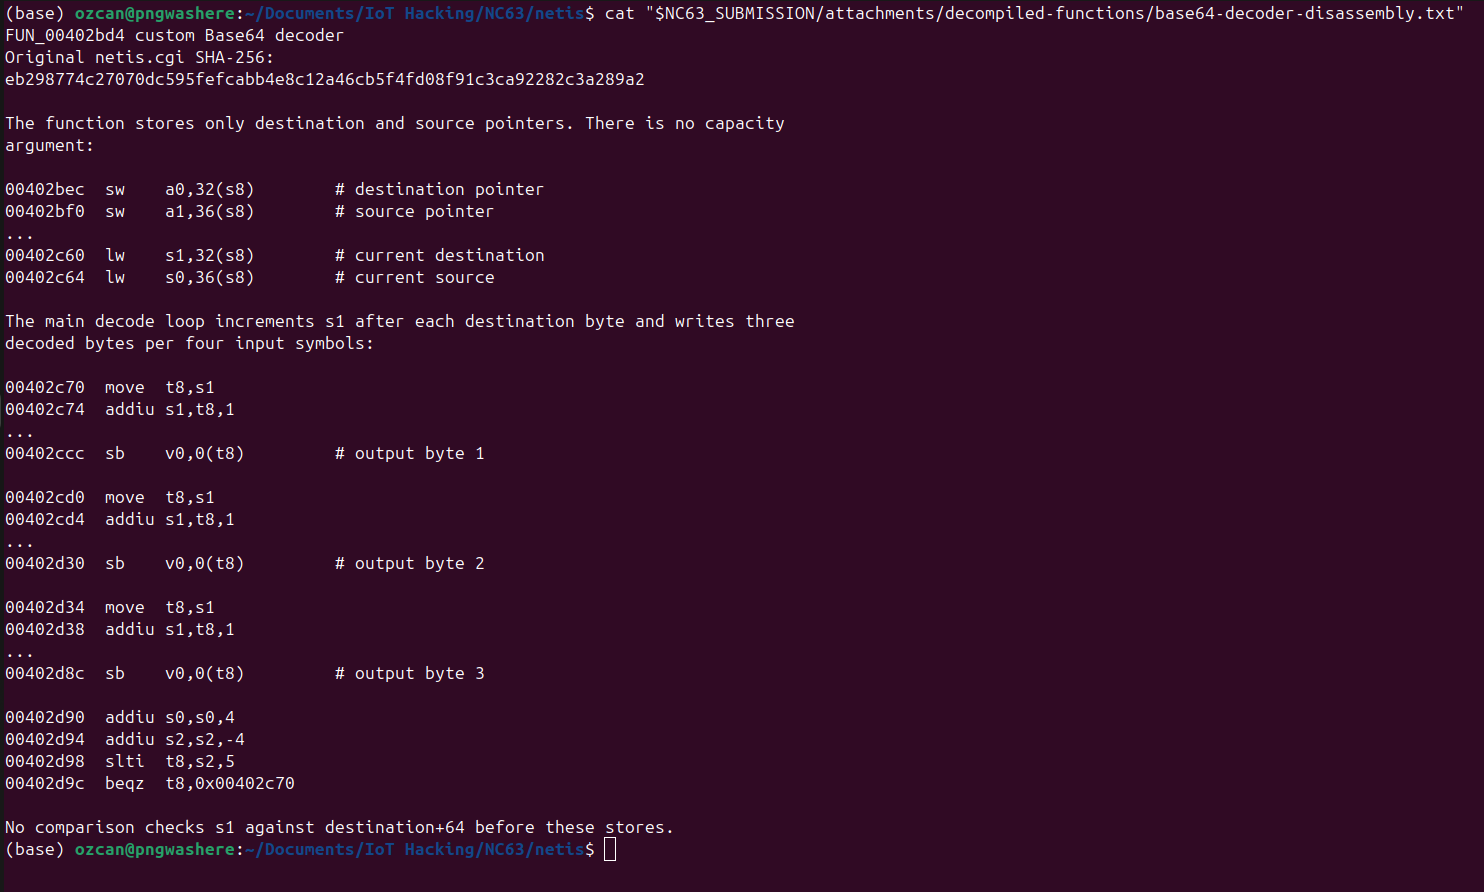
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi

解决网络安全漏洞

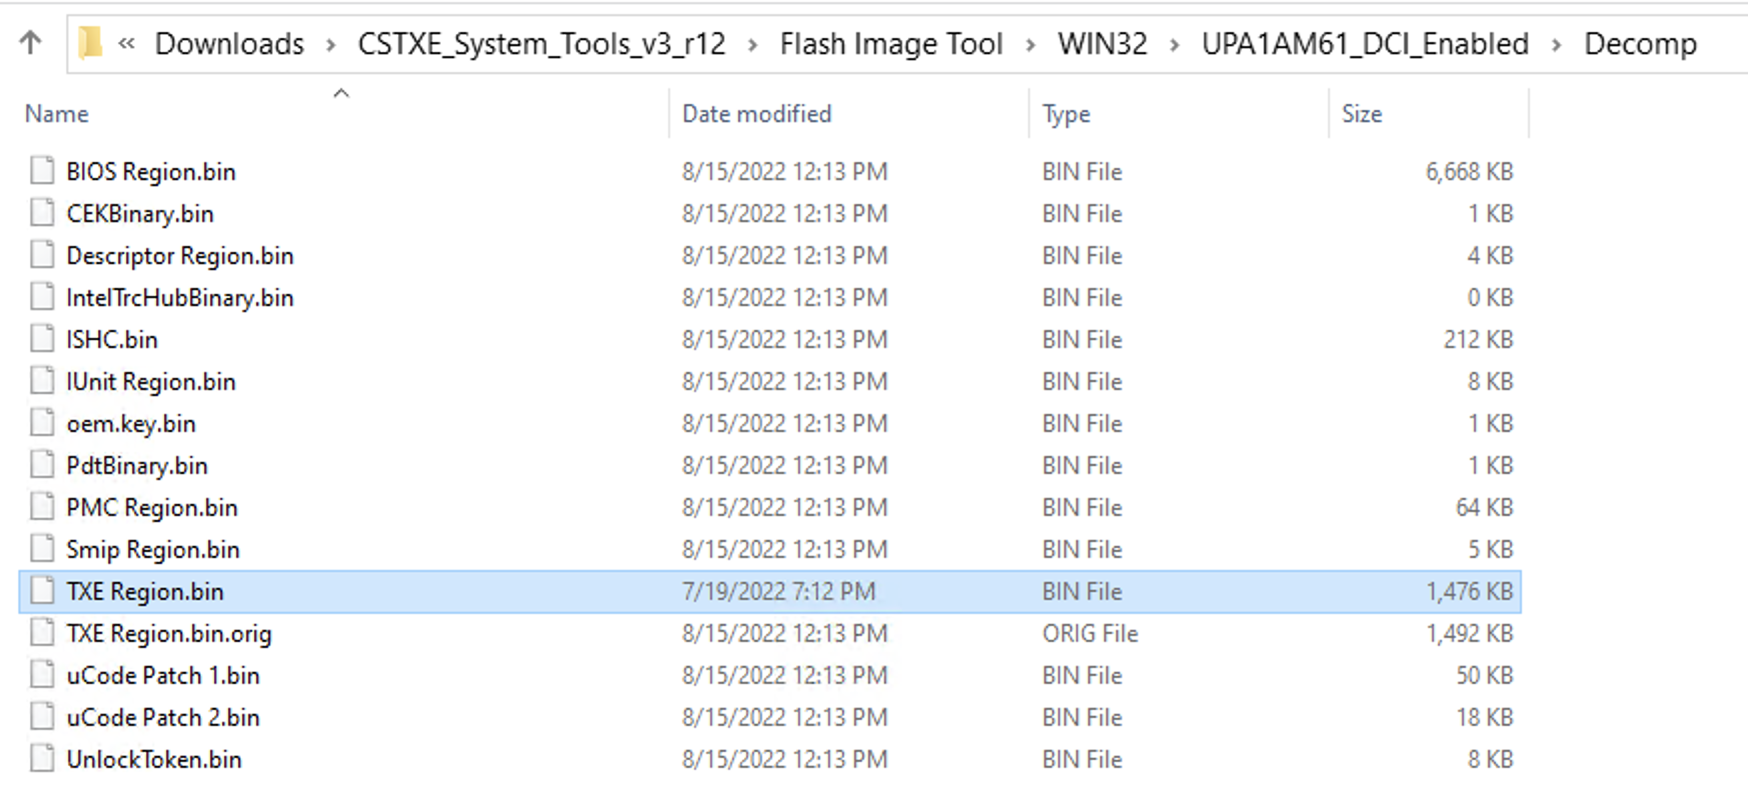
Intel Management Engine JTAG Proof of Concept - 2022 Instructions

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

Heap analysis tooling for mempool

This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.

Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…

Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…

CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)

Proof-of-concept exploit for CVE-2026-1668.

Security issue in the hypervisor firmware of some older Qualcomm chipsets

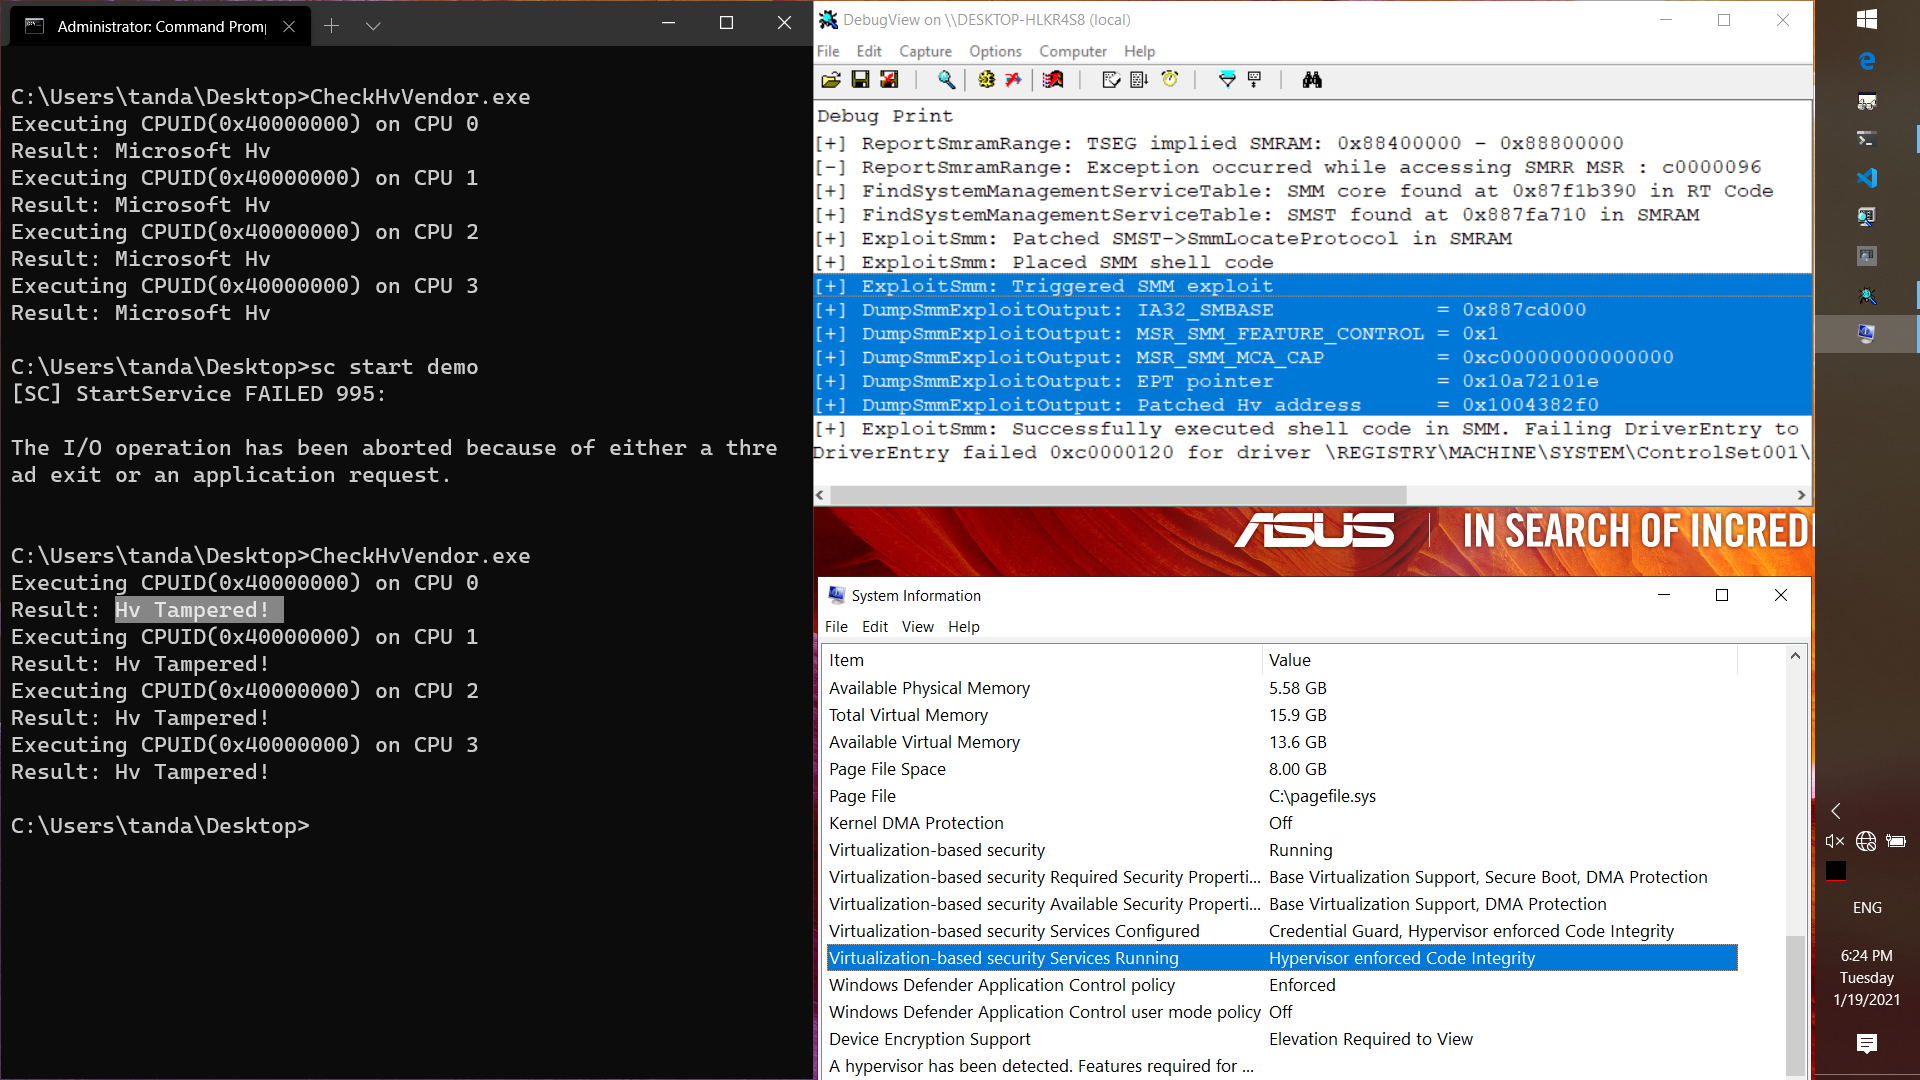
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.