Vulnerability-DLink-CVE-2025-14659

Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…

Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…

Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…

The first analysis framework for CPU microcode

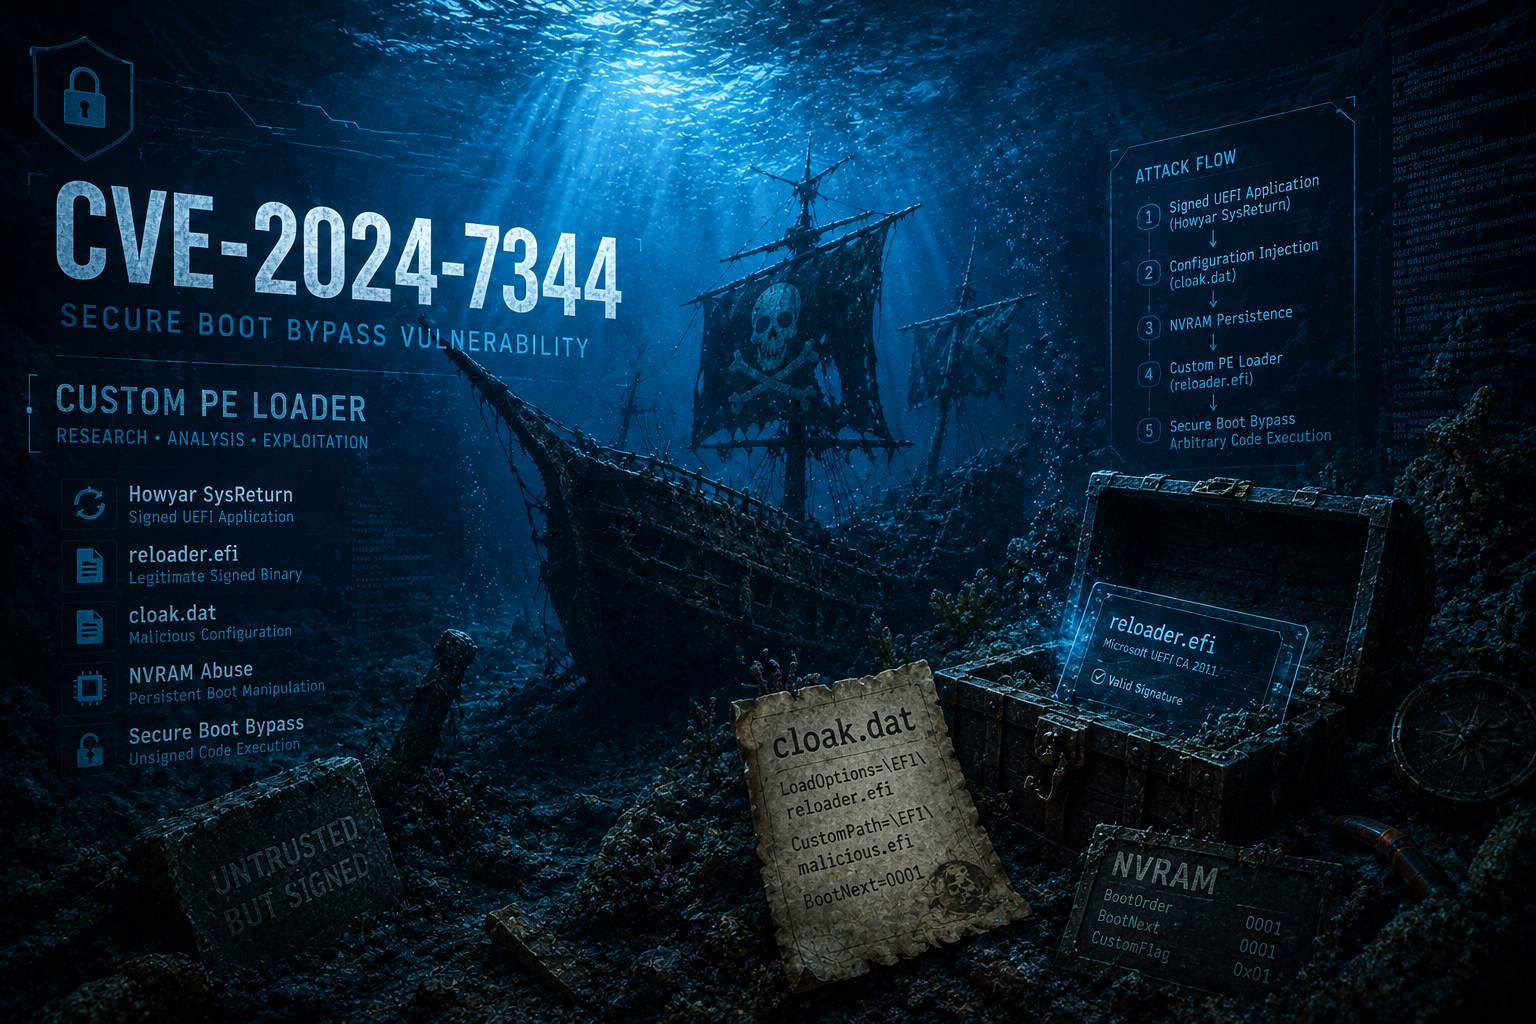
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…

Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.

An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.

Custom C exploit for CVE-2020-8423 targeting MIPS routers, featuring hooked open() syscall and tailored for Linux kernel 2.6.31.

Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…

Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…

Flipper Zero app for infrared electronic shelf-label (ESL) protocol research, featuring custom image transmission, NFC tag scanning, and a web-based…

BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…

Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…