
CVE-2026-96515
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
binary-analysisembedded-systems-securityexploitation+7
1
whoami-012/cve-2026-96515Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 minanagehsalalma/cve-2026-6837-zyxel-export-cgi-command-injection
Public writeup, PoC, and emulation materials for CVE-2026-6837 affecting Zyxel export-cgi PKCS#12 export handling.
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 synacktiv/yealink_tools
Reverse engineering scripts designed for extracting Yealink VOIP upgrade files
 ets-mse/secure-boot-cert-servicing
Standalone assessment and servicing for the Secure Boot 2011 to 2023 certificate rollover (CVE-2023-24932 / KB5025885). Assess-only by default; no…
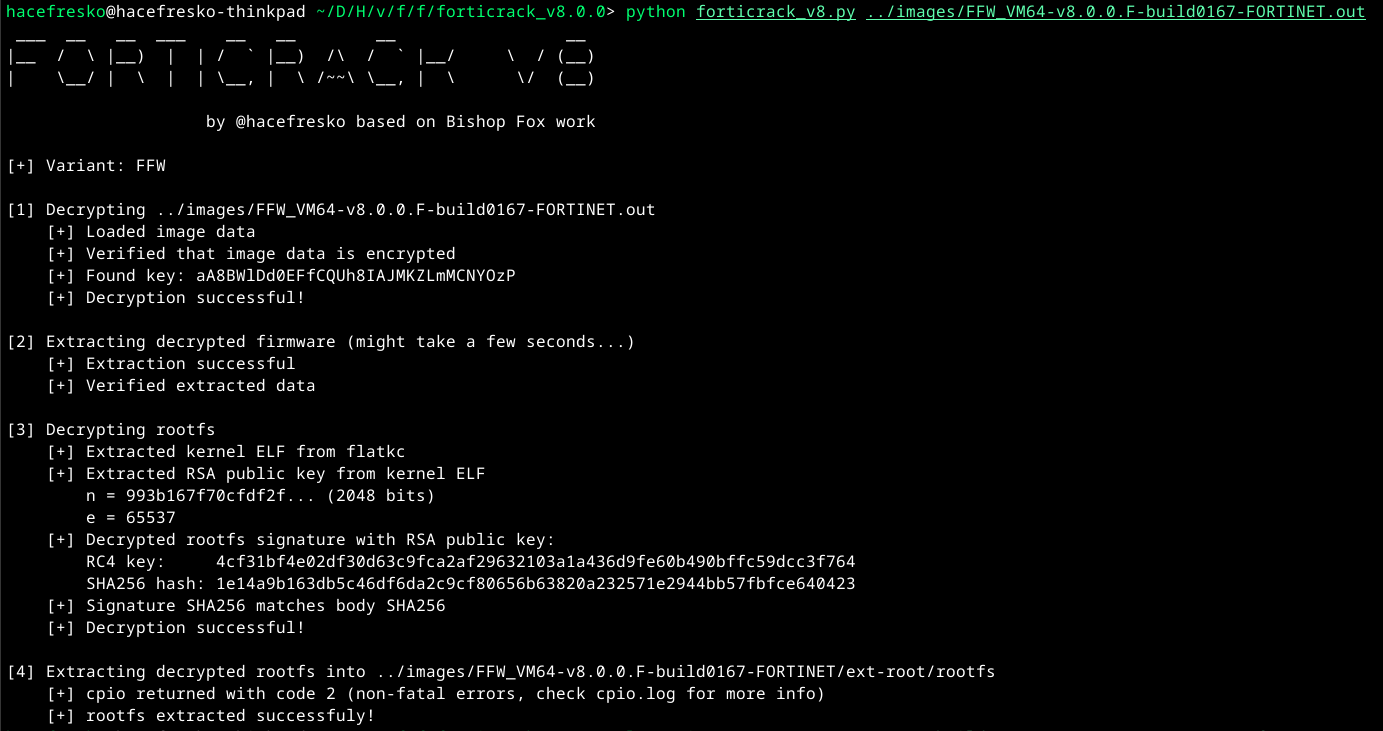 hacefresko/forticrack_v8
Decrypt and extract FortiOS 8.0.0 firmware images.
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 pauljrowland/bootholefix
This script will remediate the BootHole bug identified in CVE-2020-25632 and/or CVE-2021-20233.
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
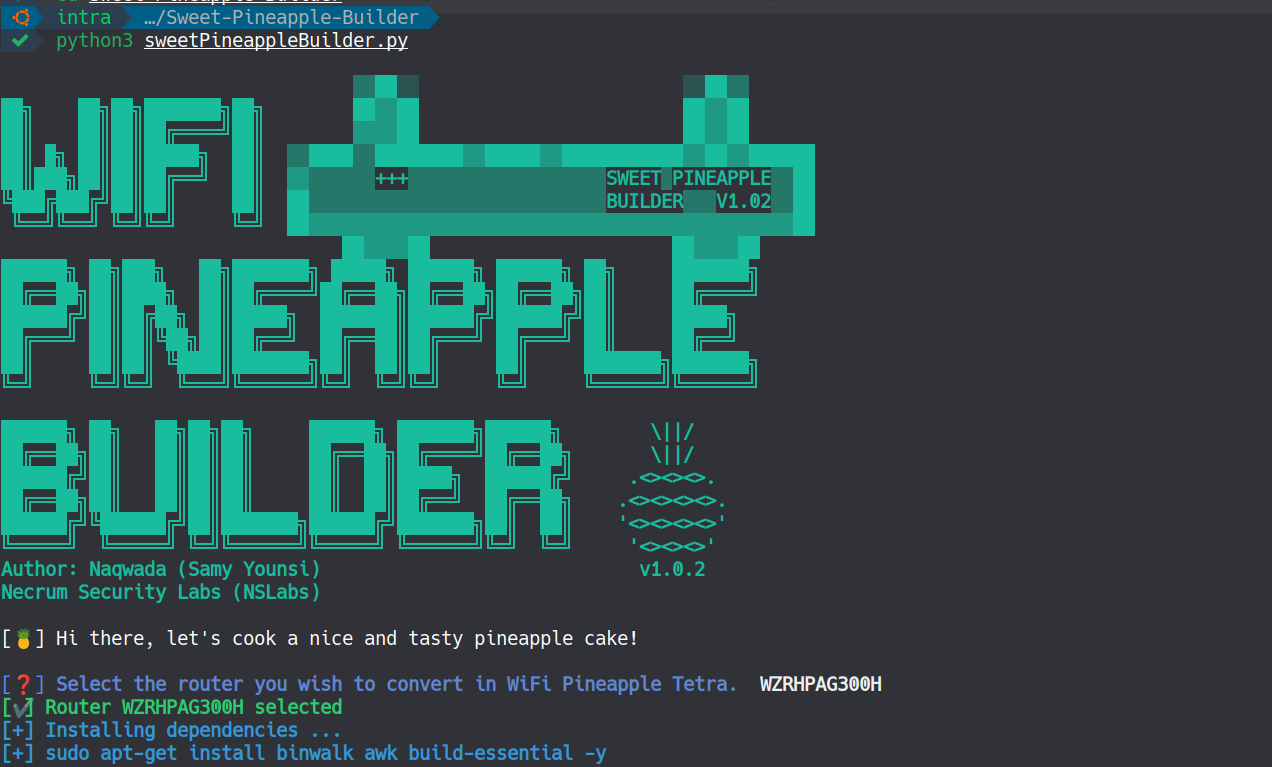
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
 pixel-props/build.prop
Bash script to build your own system.prop
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering