

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
61 results
CVE-2026-95675 preview

CVE-2026-95675

GitHubd6fault/cve-2026-95675

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…

embedded-systems-securityexploitationfirmware-analysis+6
1
1 day ago
CVE-2026-96515 preview

CVE-2026-96515

GitHubwhoami-012/cve-2026-96515

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
binary-analysisembedded-systems-securityexploitation+7
1 day ago
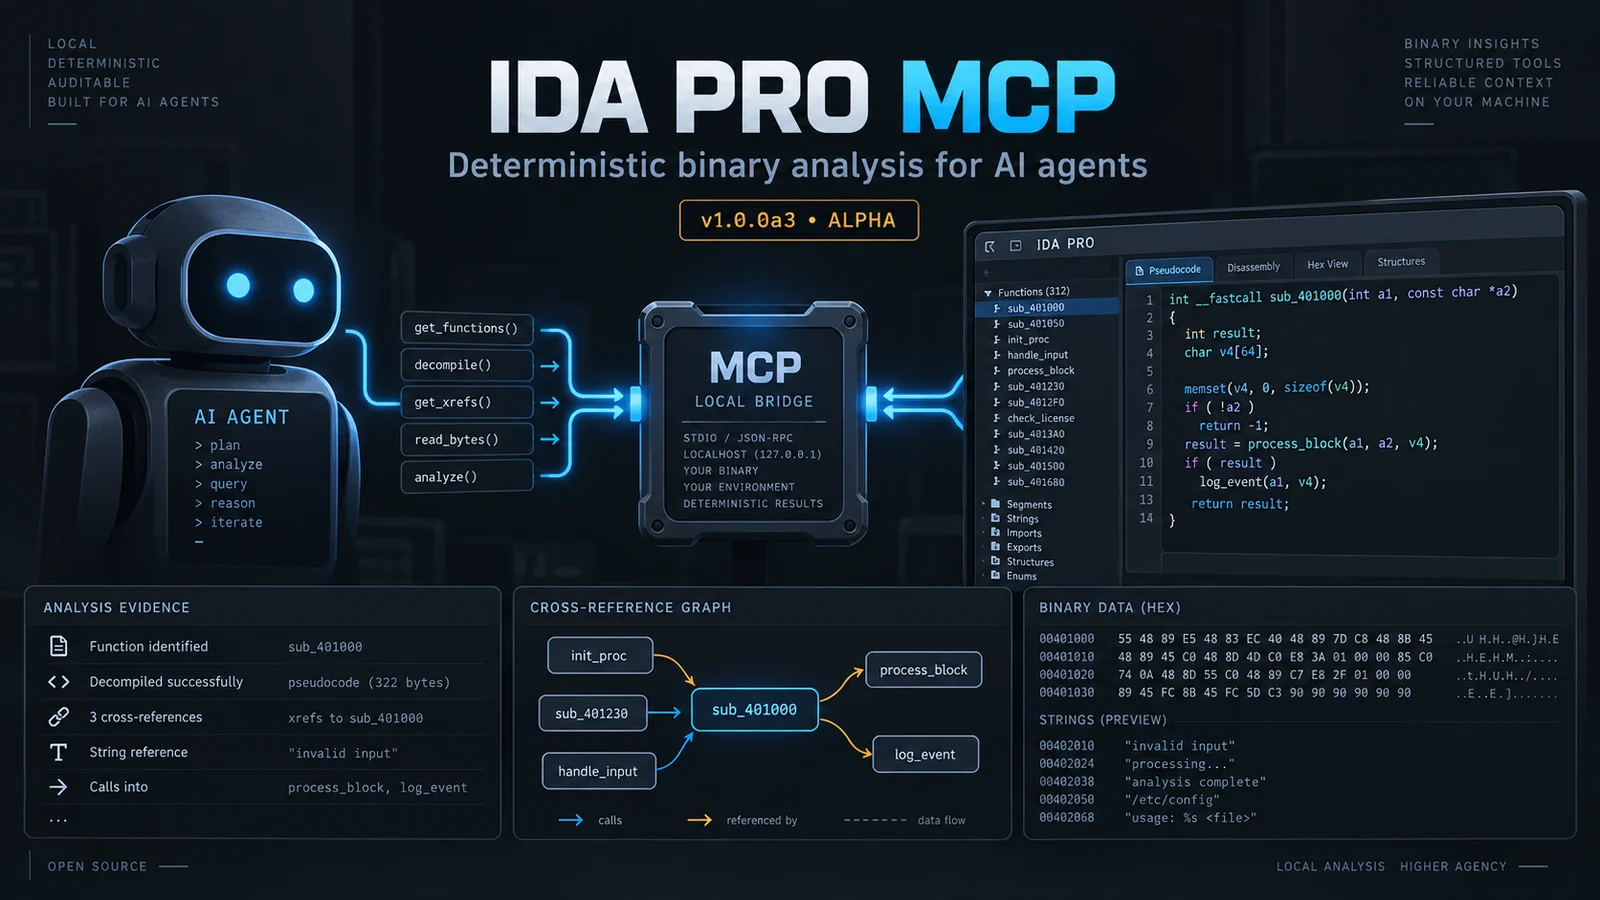
ida-pro-mcp preview

ida-pro-mcp

GitHubgrecandrei/ida-pro-mcp

Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
ai-assisted-reversingai-securitybinary-analysis+7
85 days ago
tapo-c260-rce preview

tapo-c260-rce

GitHubl0lsec/tapo-c260-rce

PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
command-and-controlembedded-systems-securityexploitation+7
26 months ago
grandstream-cve-2026-2329-analysis preview

grandstream-cve-2026-2329-analysis

GitHubvivianuba/grandstream-cve-2026-2329-analysis

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
binary-analysiseducationfirmware-analysis+4
1 month ago
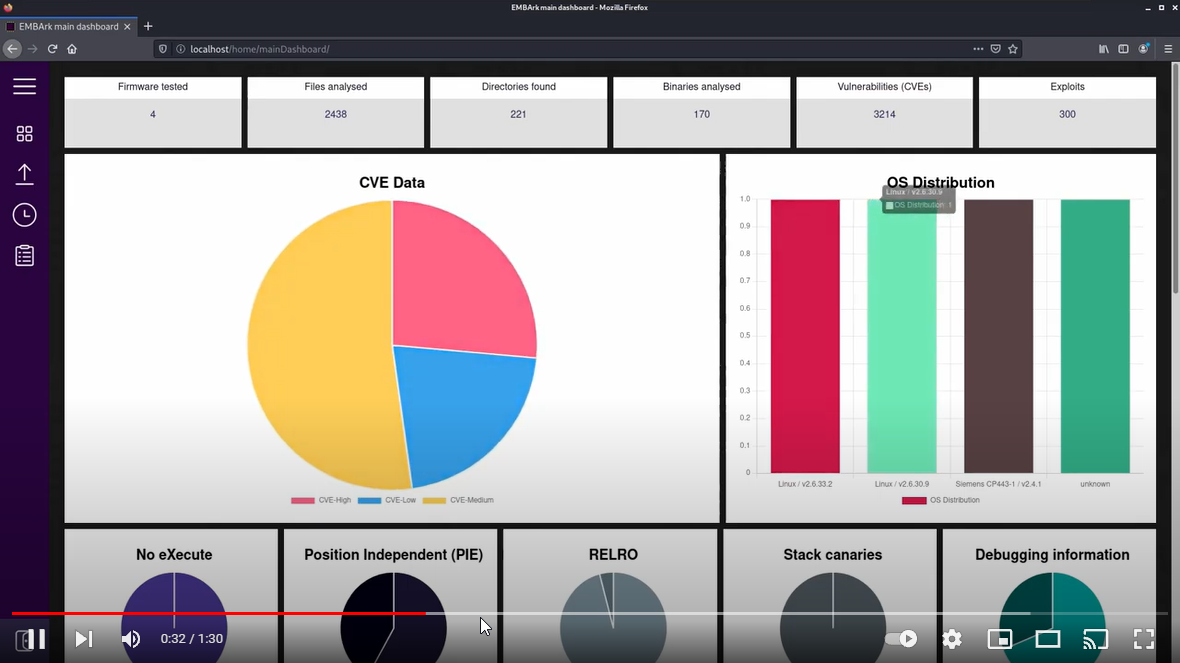
embark preview

embark

GitHube-m-b-a/embark

Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.

embedded-systems-securityfirmware-analysishardware-iot-security+3
3951 month ago
ipsw preview

ipsw

GitHubblacktop/ipsw

iOS/macOS Research Swiss Army Knife

ai-assisted-reversingbinary-analysisdebuggers+9
3.7k7h 41m ago
libsigrok preview

libsigrok

GitHubsigrokproject/libsigrok

C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…

embedded-systems-securityfirmware-analysisgeneral-purpose-utilities+4
4392 years ago
CVE-2026-6837-zyxel-export-cgi-command-injection preview

CVE-2026-6837-zyxel-export-cgi-command-injection

GitHubminanagehsalalma/cve-2026-6837-zyxel-export-cgi-command-injection

Public writeup, PoC, and emulation materials for CVE-2026-6837 affecting Zyxel export-cgi PKCS#12 export handling.
embedded-systems-securityexploitationfirmware-analysis+3
31 month ago
QuestStack preview

QuestStack

GitHubstarseed12345/queststack

Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
android-securitybinary-exploitationembedded-systems-security+5
20528 days ago
asadbg preview

asadbg

GitHubnccgroup/asadbg

asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
binary-analysisdebuggersembedded-systems-security+5
814 years ago
idahunt preview

idahunt

GitHubnccgroup/idahunt

idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
binary-analysisembedded-systems-securityfirmware-analysis+4
3943 years ago
LogoFail-PoC preview

LogoFail-PoC

GitHubd0rb/logofail-poc

This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.

binary-exploitationeducationexploitation+5
82 years ago
routers-exploit preview

routers-exploit

GitHubelbertavares/routers-exploit

Proof-of-concept exploits for TP-Link routers, including remote command execution and authentication bypass vulnerabilities.

educationexploitationfirmware-analysis+4
116 years ago
uofw preview

uofw

GitHubuofw/uofw

The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
binary-analysiseducationembedded-systems-security+3
4377 months ago
blogpost_cve-2018-19987-analysis preview

blogpost_cve-2018-19987-analysis

GitHubnahueldsanchez/blogpost_cve-2018-19987-analysis

This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
educationexploitationfirmware-analysis+4
25 years ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
Detect-CVE-2024-0762 preview

Detect-CVE-2024-0762

GitHubtadash10/detect-cve-2024-0762

Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature

firmware-analysisincident-responsemalware-analysis+3
2 years ago
Previous1234Next