

 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#
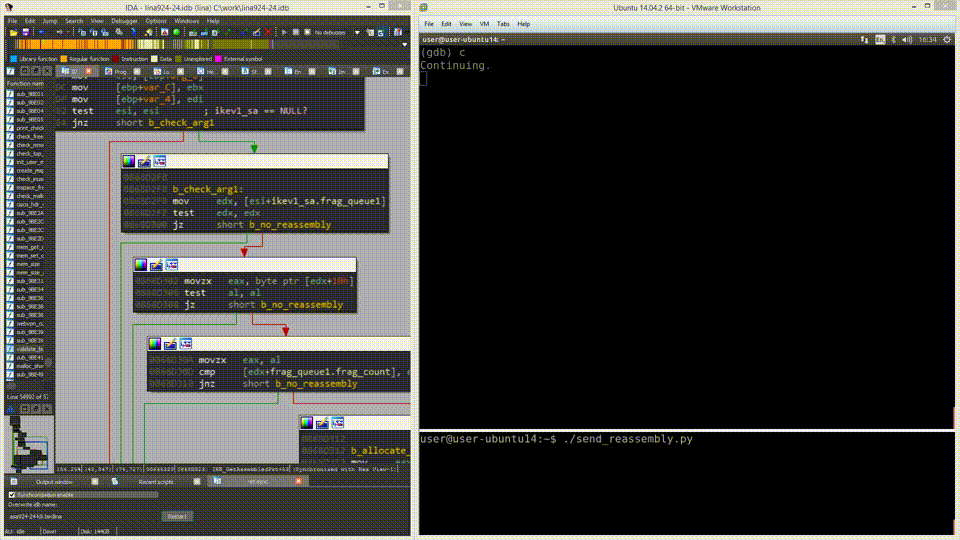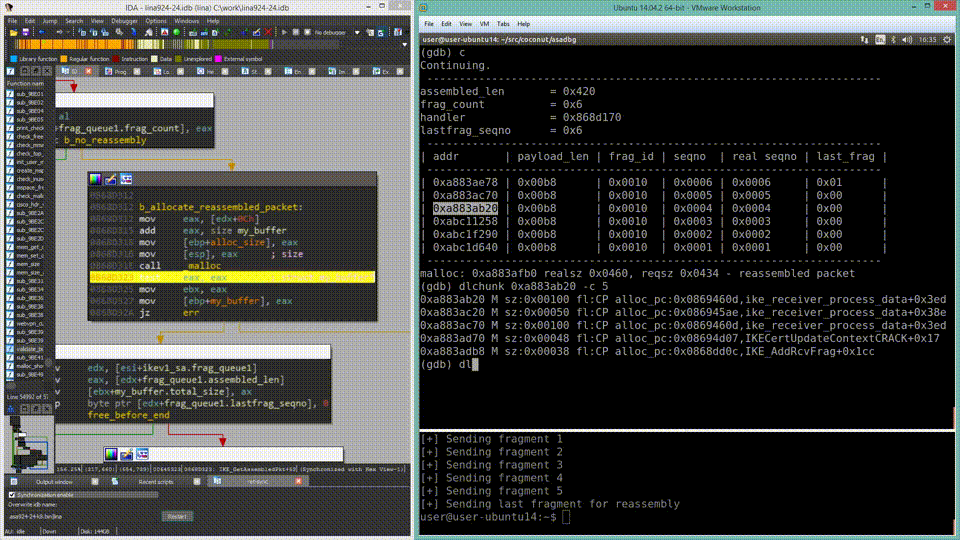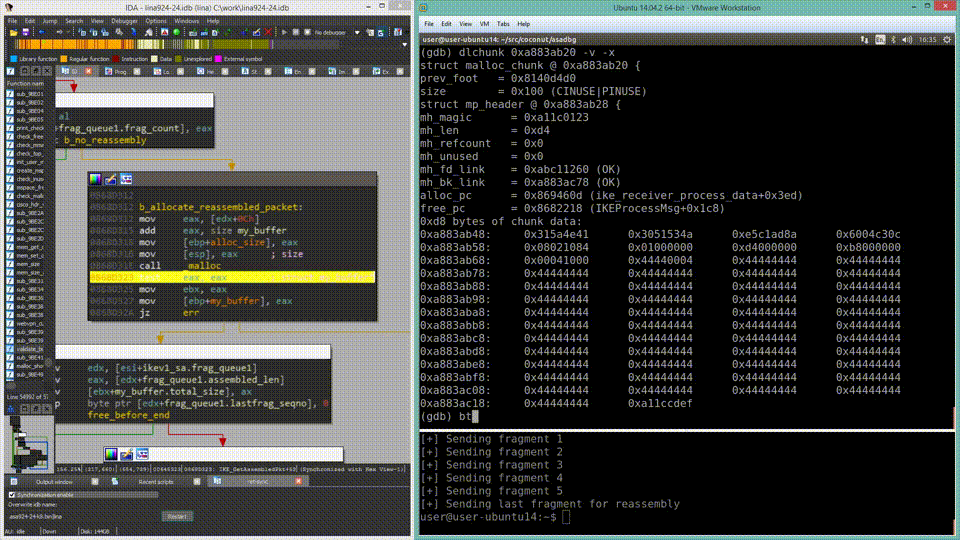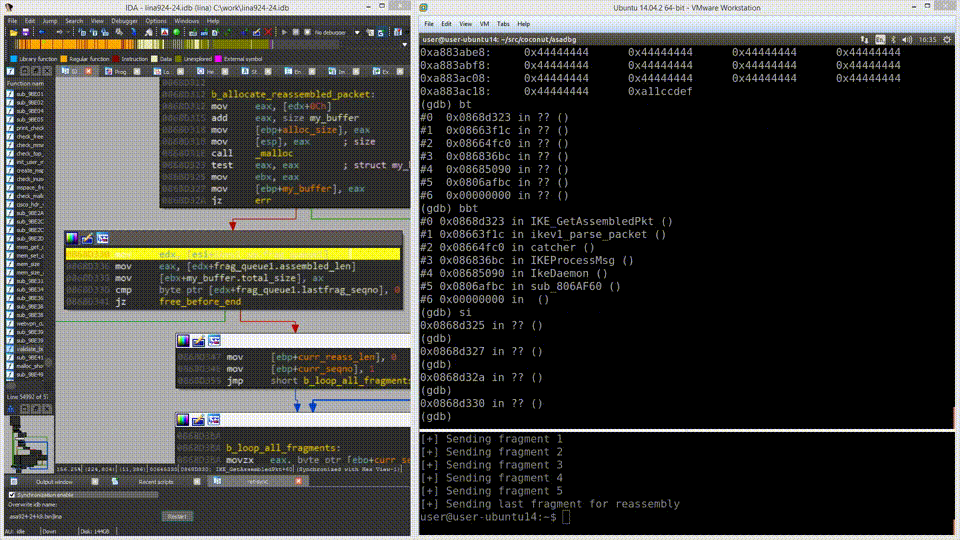 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team