
nexmon
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
embedded-systems-securityfirmware-analysishardware-hacking+6
2.9k
seemoo-lab/nexmonThe C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 nccgroup/zipdefrag
Presented at Recon Montreal 2018
 infobyte/nec_aterm_tools
Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.
 veereshgadige/aziot-cctv-cve-2025-50777
CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
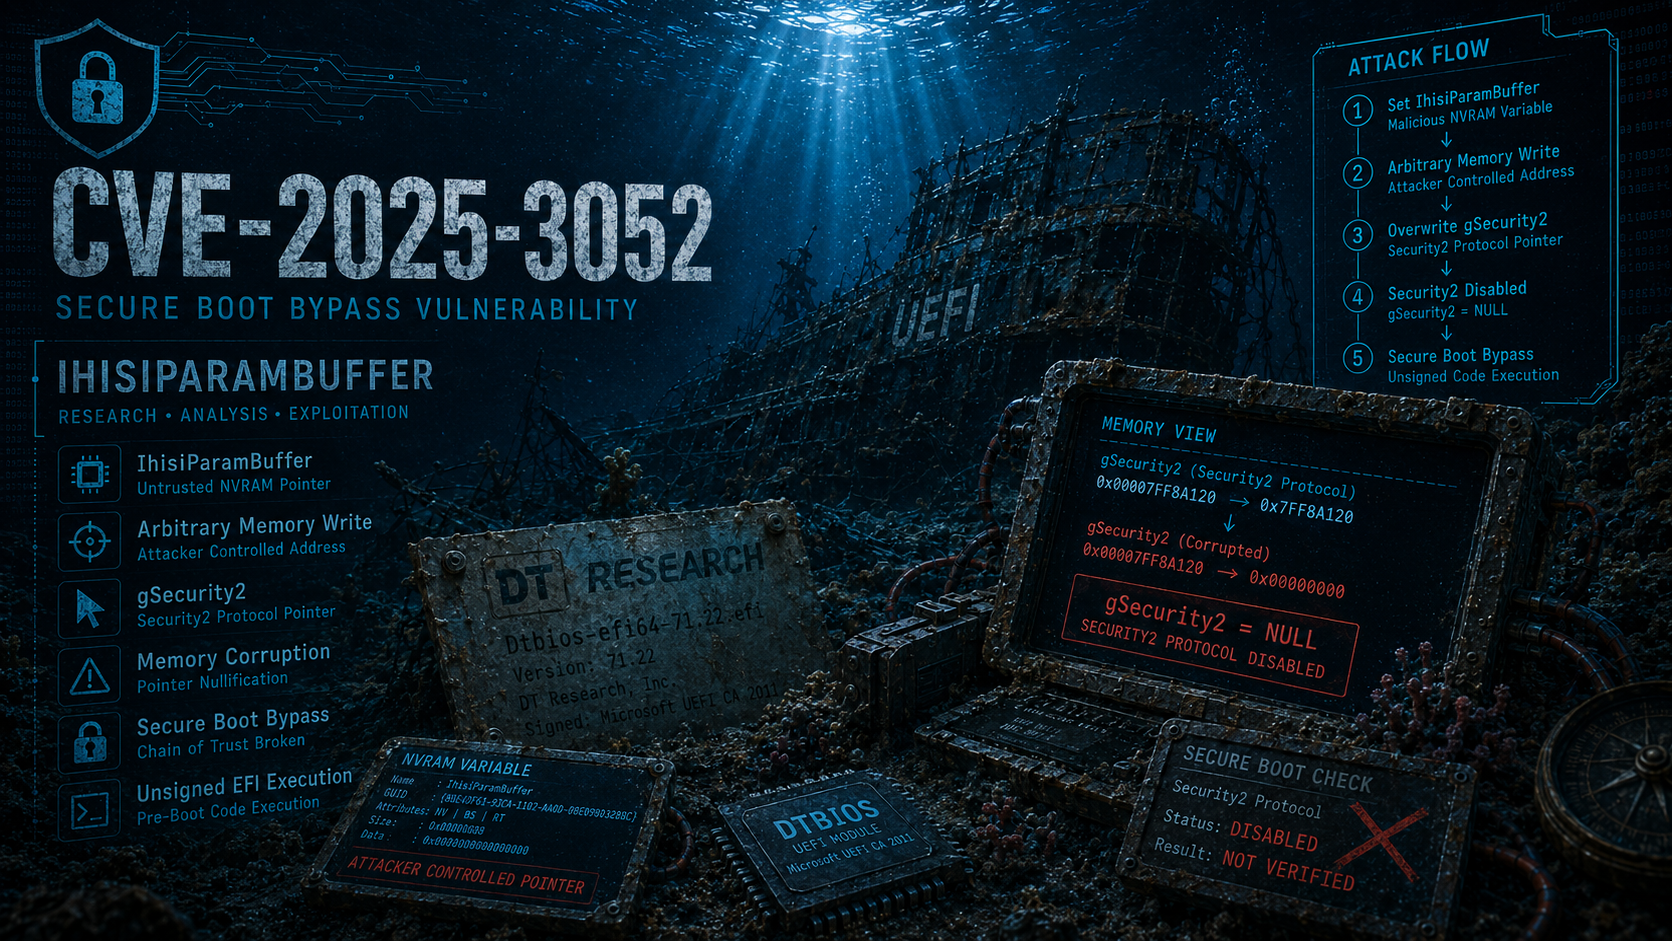 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
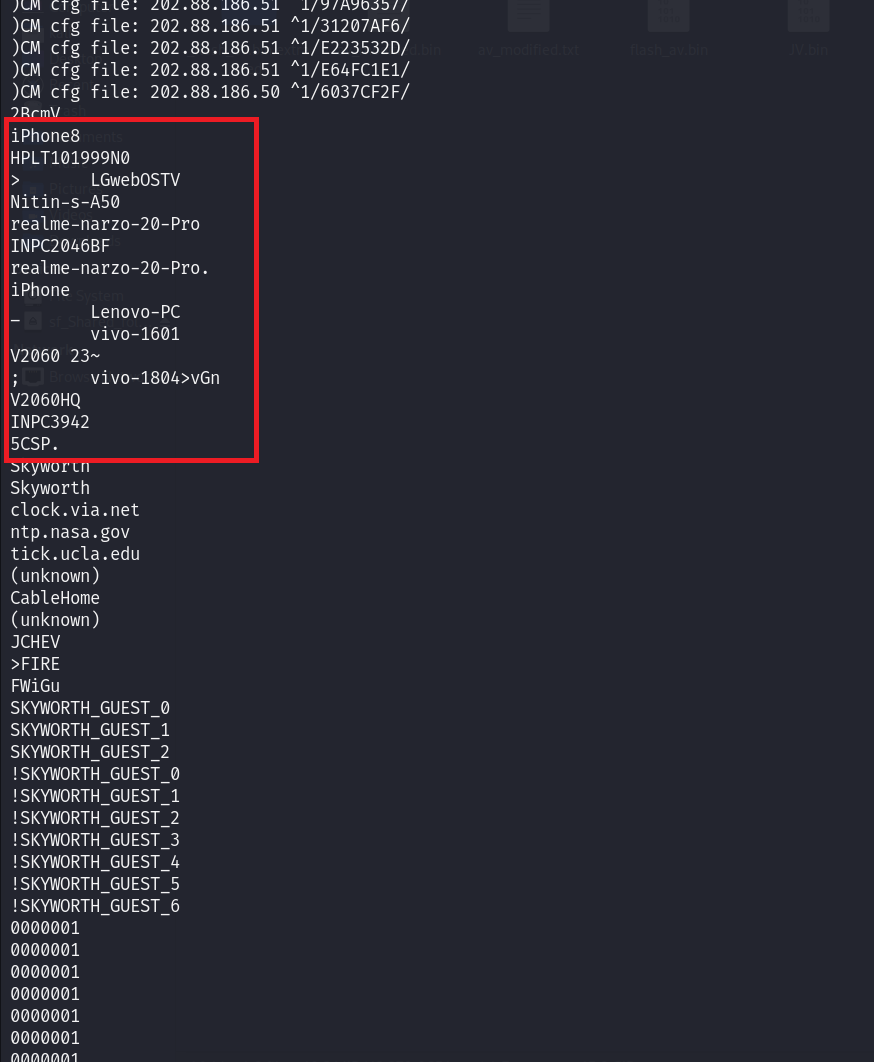 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
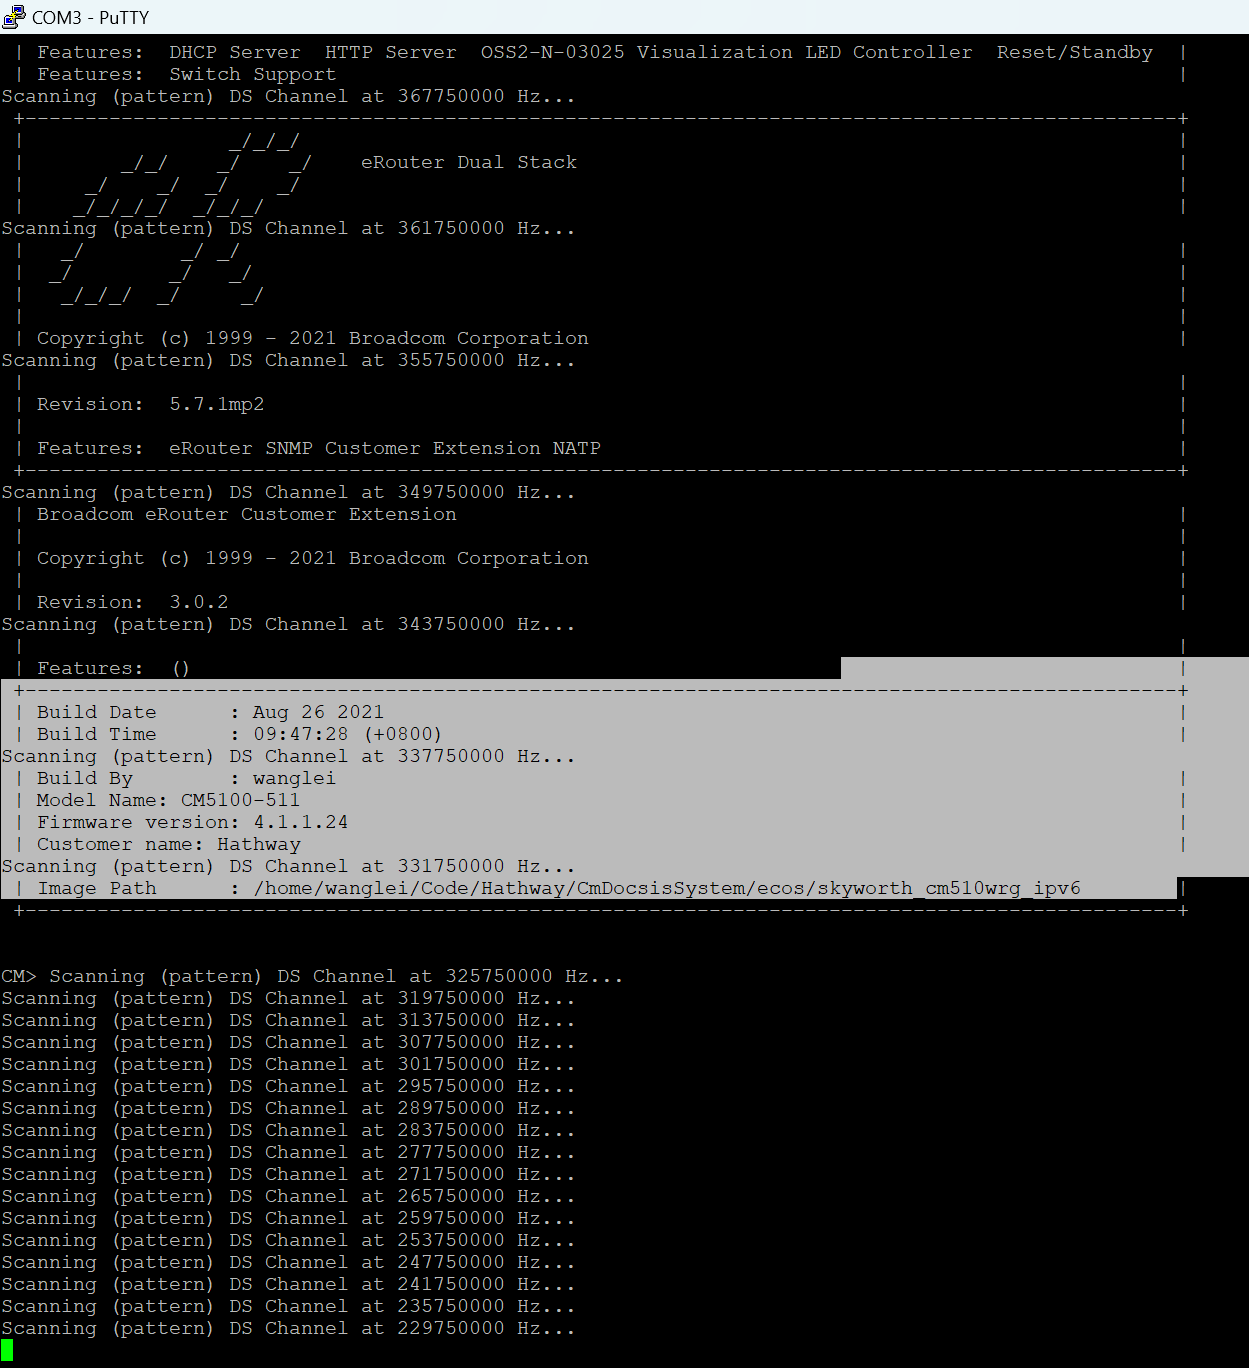 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
 fans0n-fan/treck20-related
PoC for CVE-2020-11896 Treck TCP/IP stack and device asset investigation
 nccgroup/powerg-tools
Tools for reverse engineering and interacting with the PowerG radio protocol
 zhazhalove/osquery_cve-2024-23443
Osqery extension HP BIOS WMI