
USB Spy
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
digital-forensicsexploitationfirmware-analysis+6
christophe.duvernois/usb-spyIntercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…

 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 i12bp8/tagtinker
Flipper Zero app for infrared electronic shelf-label (ESL) protocol research, featuring custom image transmission, NFC tag scanning, and a web-based…
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 teutekeune/ibssloader
Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 lnversed/cve-2020-8423
Custom C exploit for CVE-2020-8423 targeting MIPS routers, featuring hooked open() syscall and tailored for Linux kernel 2.6.31.
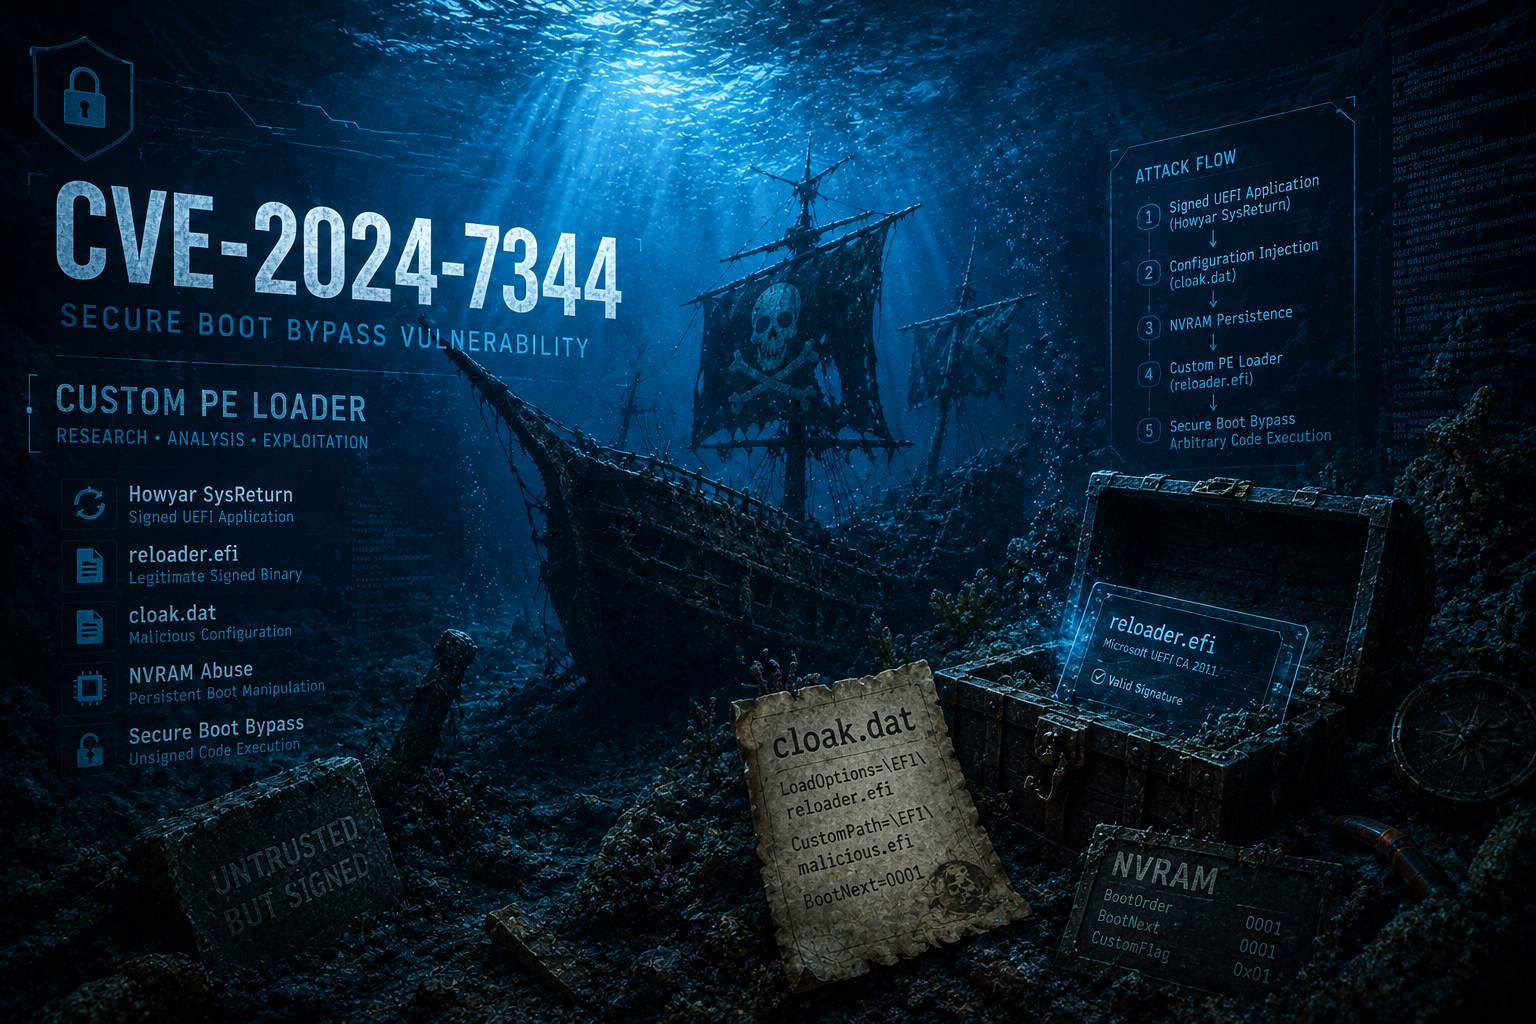 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…