grandstream-cve-2026-2329-analysis

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…

Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.

TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators

Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…

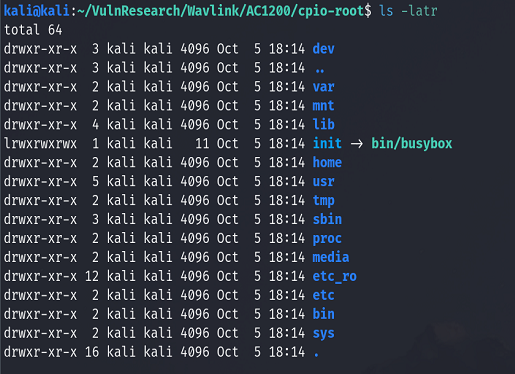
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…

Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…

Exploit setup for CVE-2025-7545 targeting vulnerable Binutils in firmware environments, including environment configuration and PDF documentation.

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.