
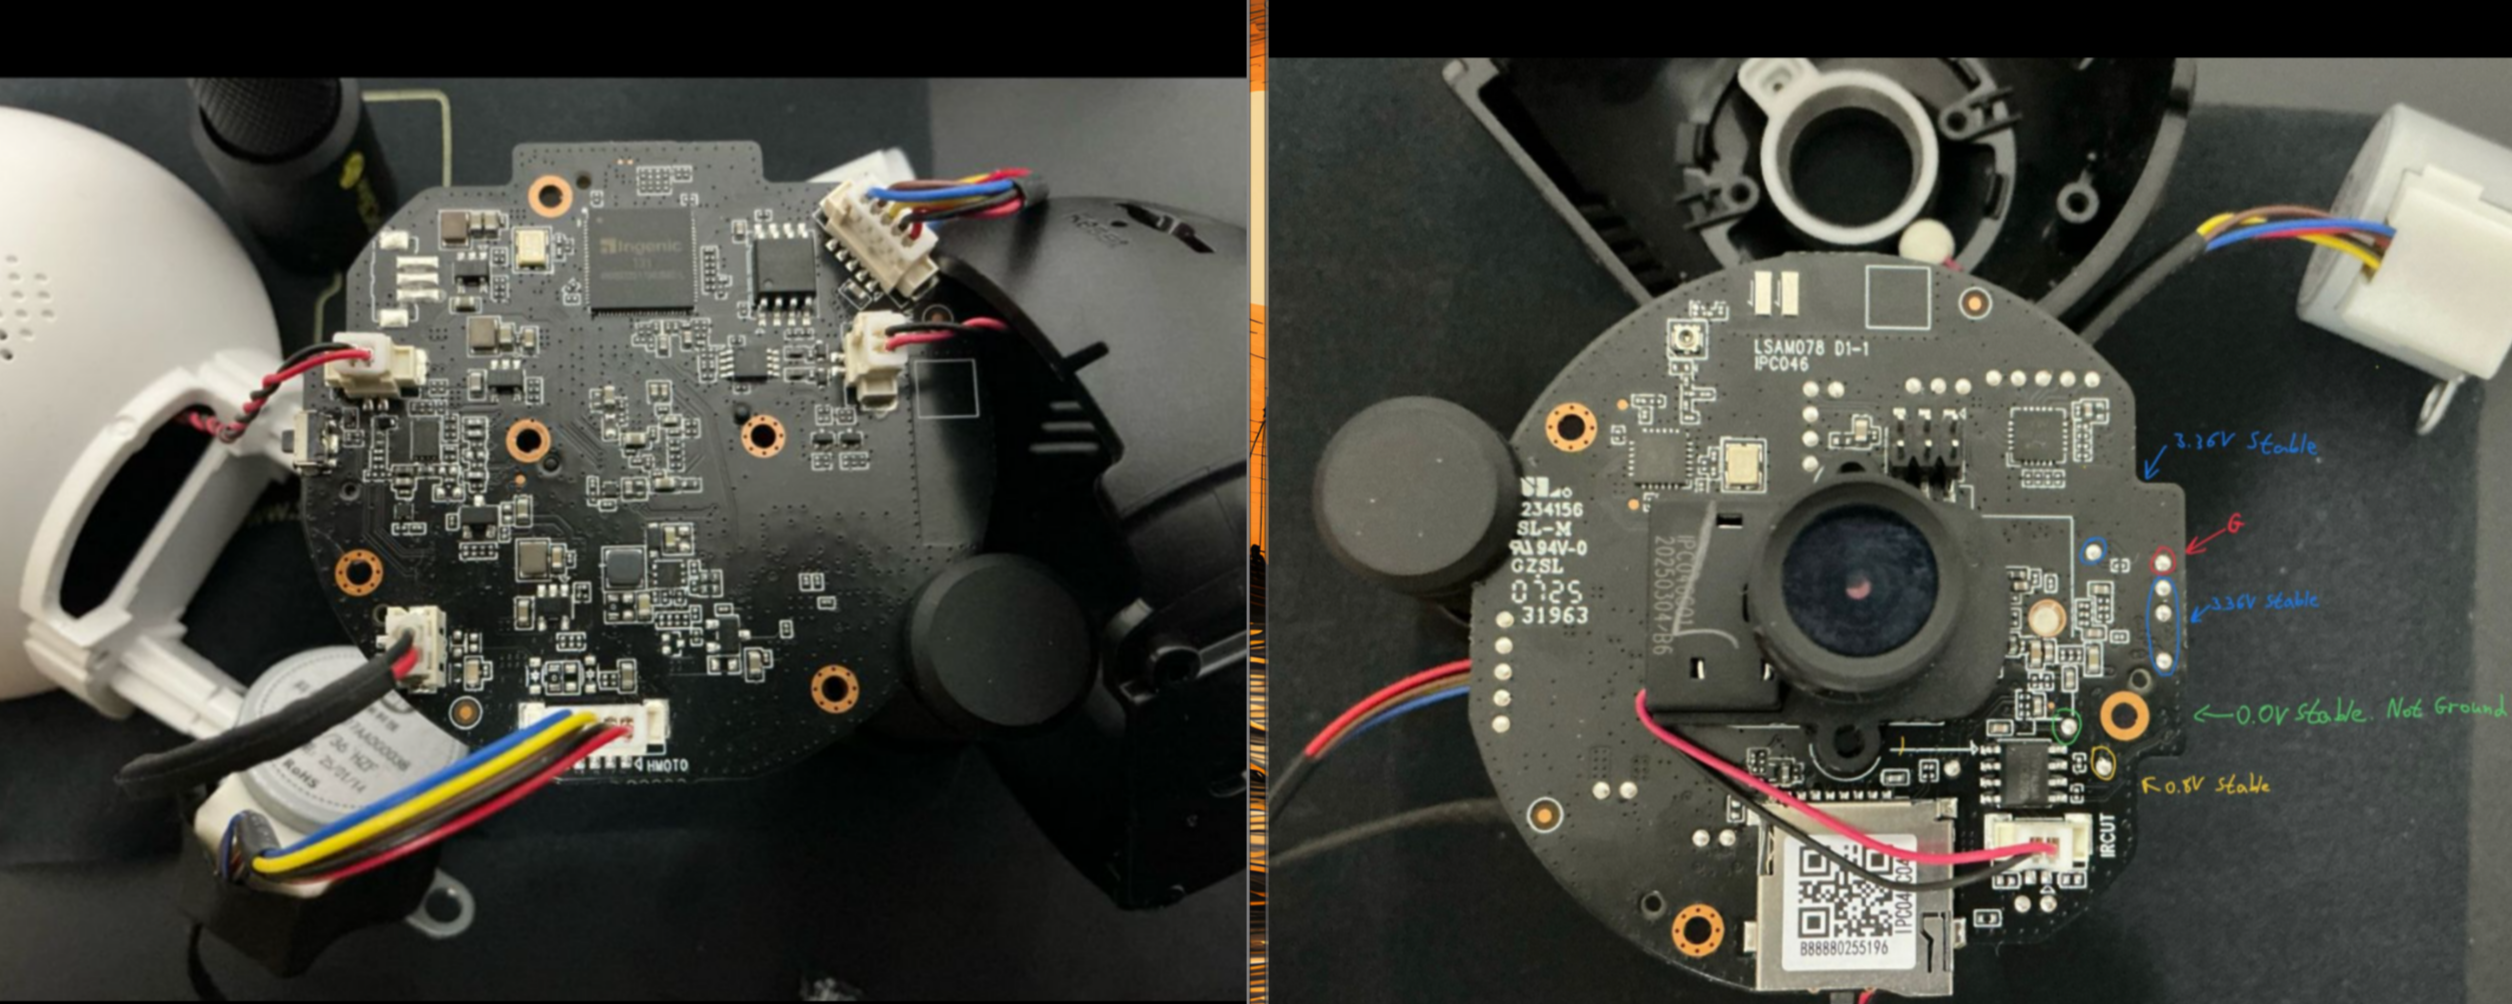
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
11
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 onekey-sec/unblob
Extract files from any kind of container formats
 o7-machinehum/phantomdrive
Seemingly normal USB drive with a hidden security feature
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 badersz/cve-2017-2751
Mini-paper on CVE-2017-2751, HP EFI password extraction.
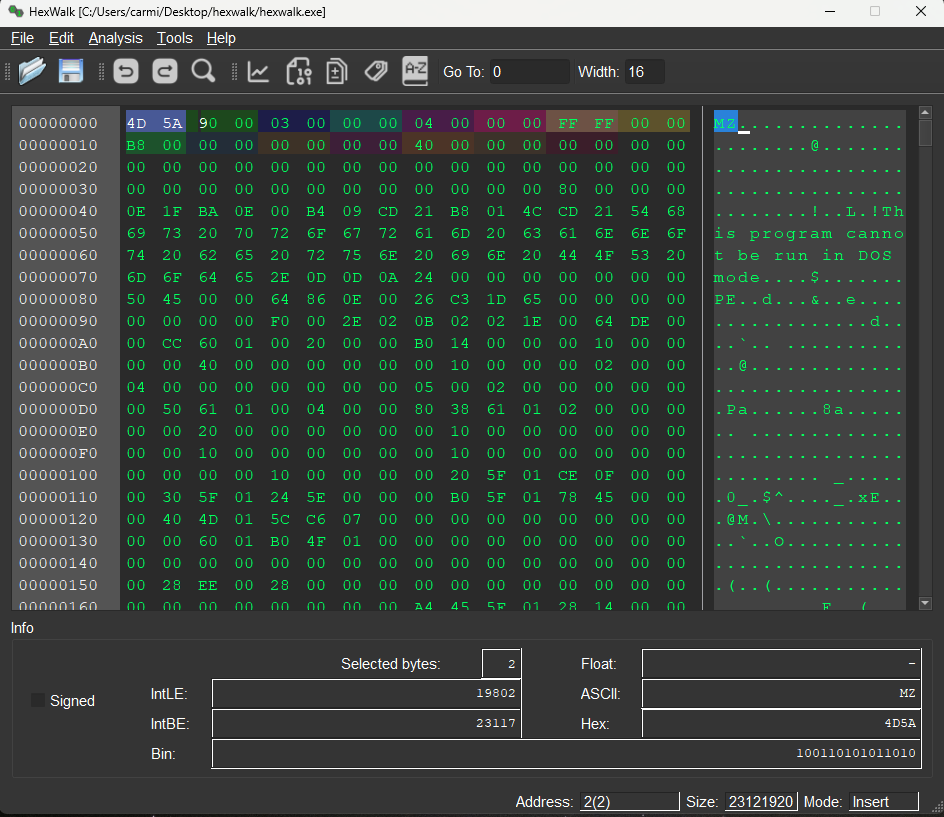 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
 coremaze/me2-writeup
Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 nccgroup/zipdefrag
Presented at Recon Montreal 2018
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
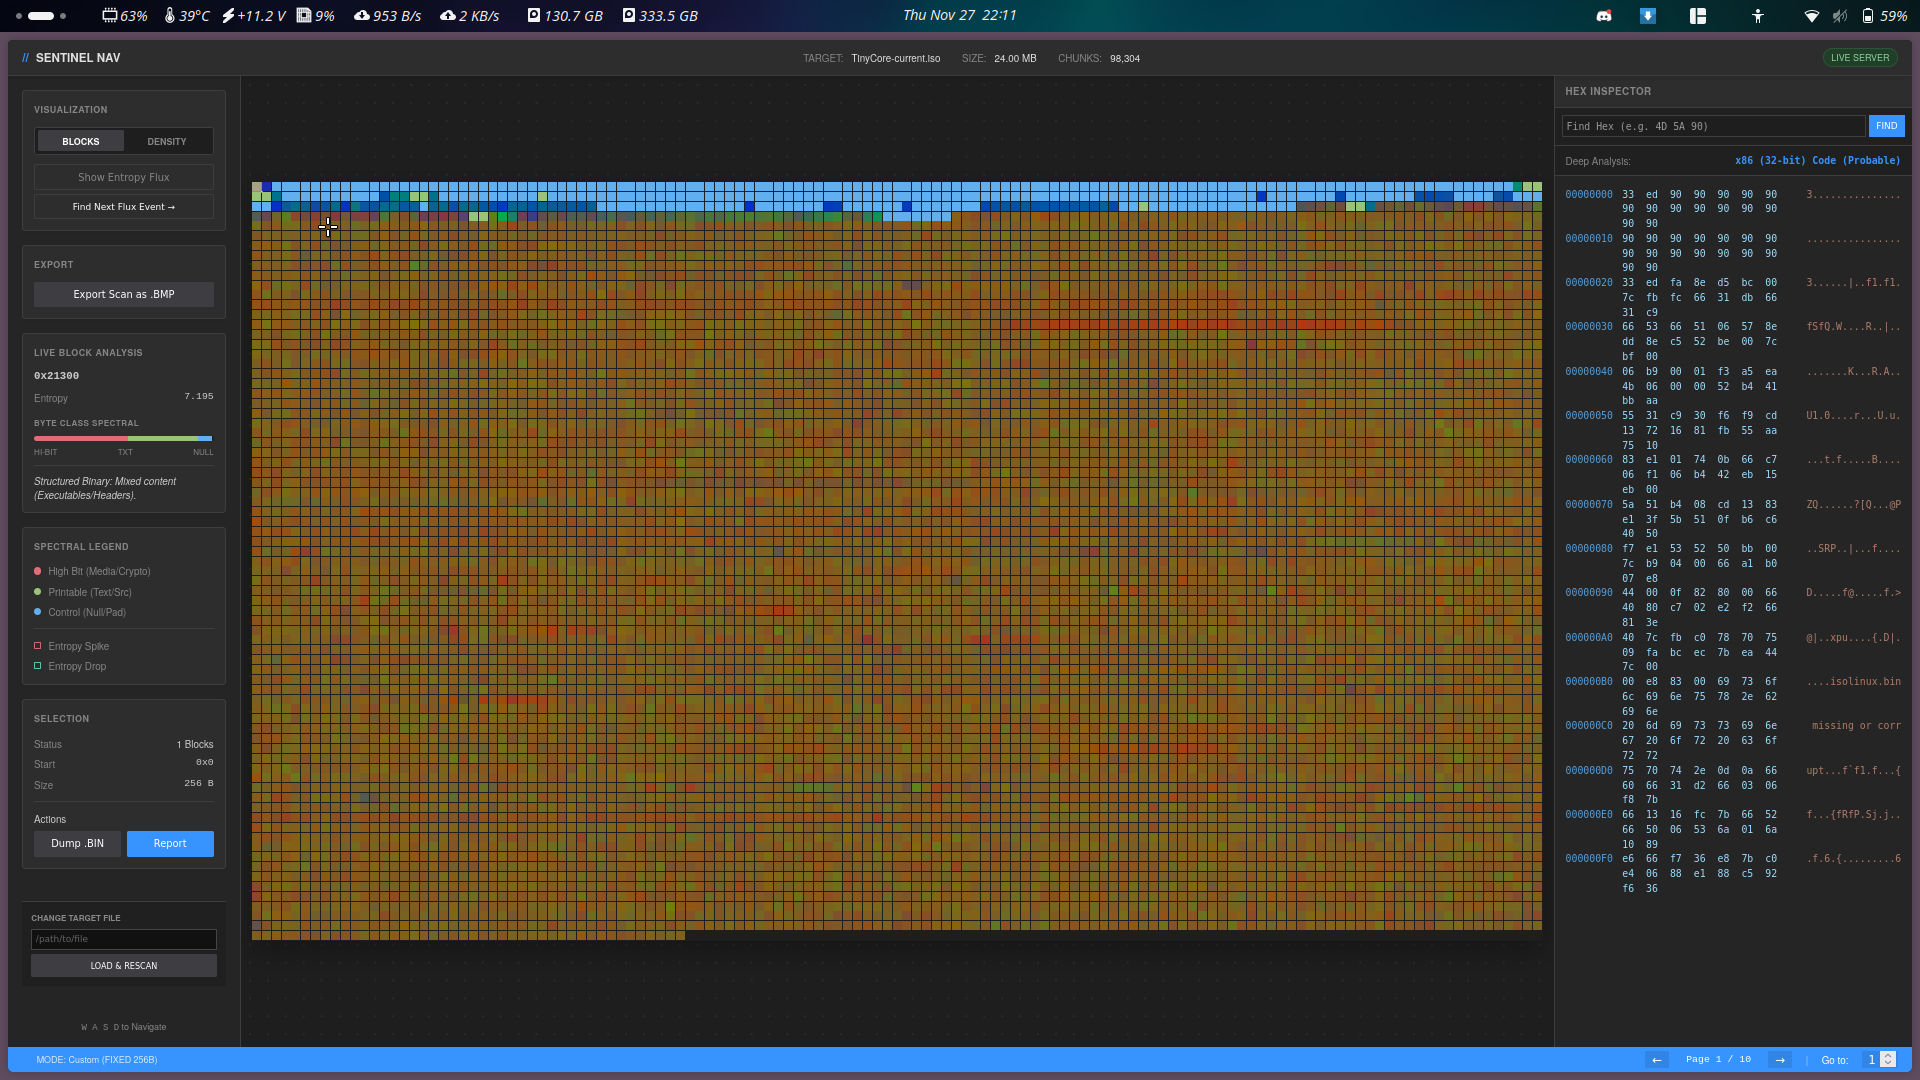 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.