
evilwaf
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
fingerprint-spoofinginformation-gatheringosint+6
890
matrixleons/evilwafevilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
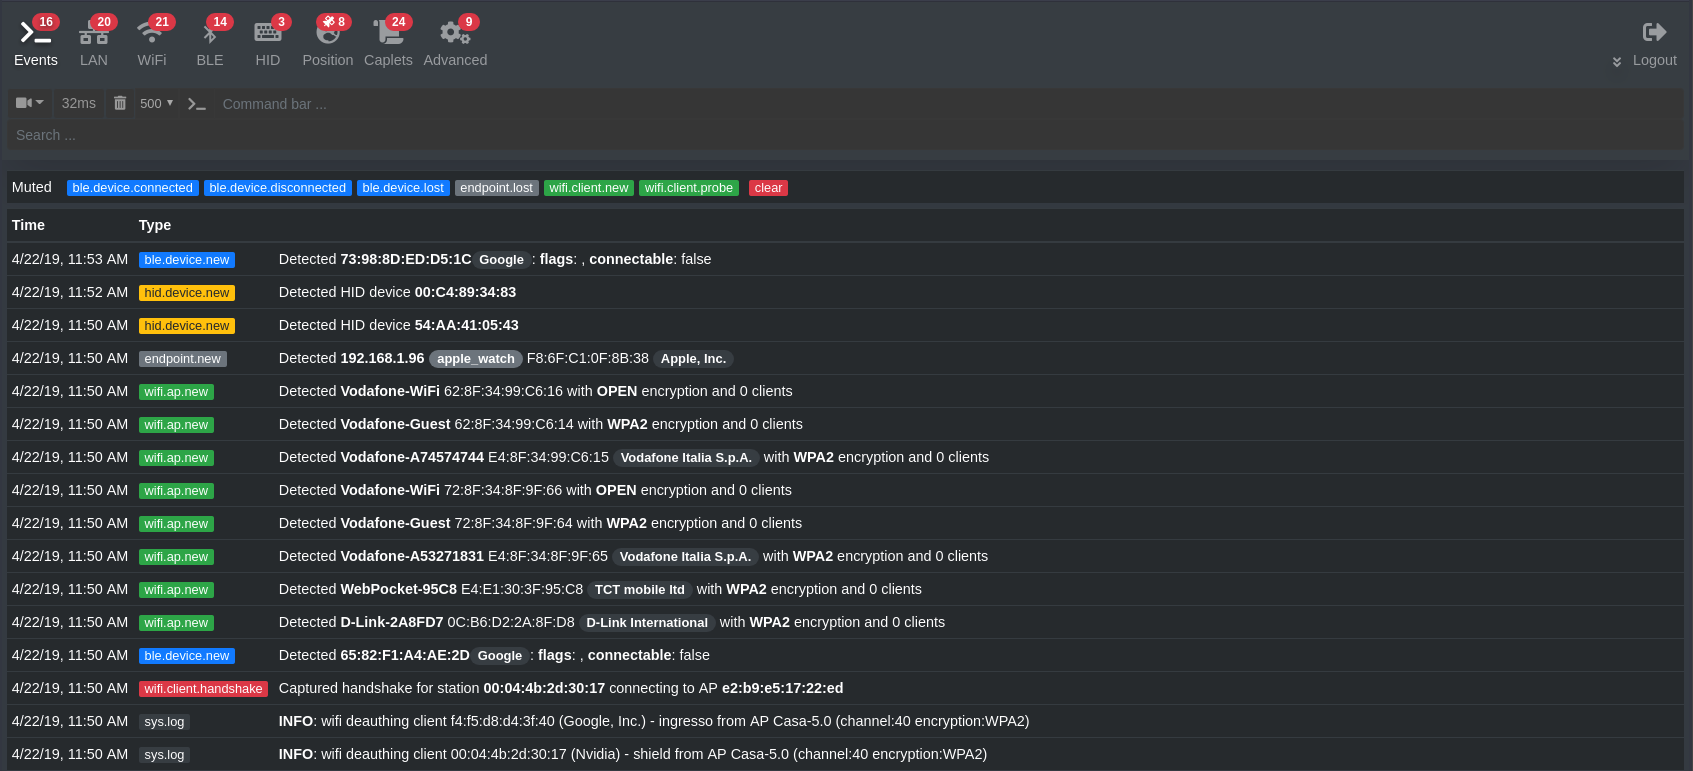 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
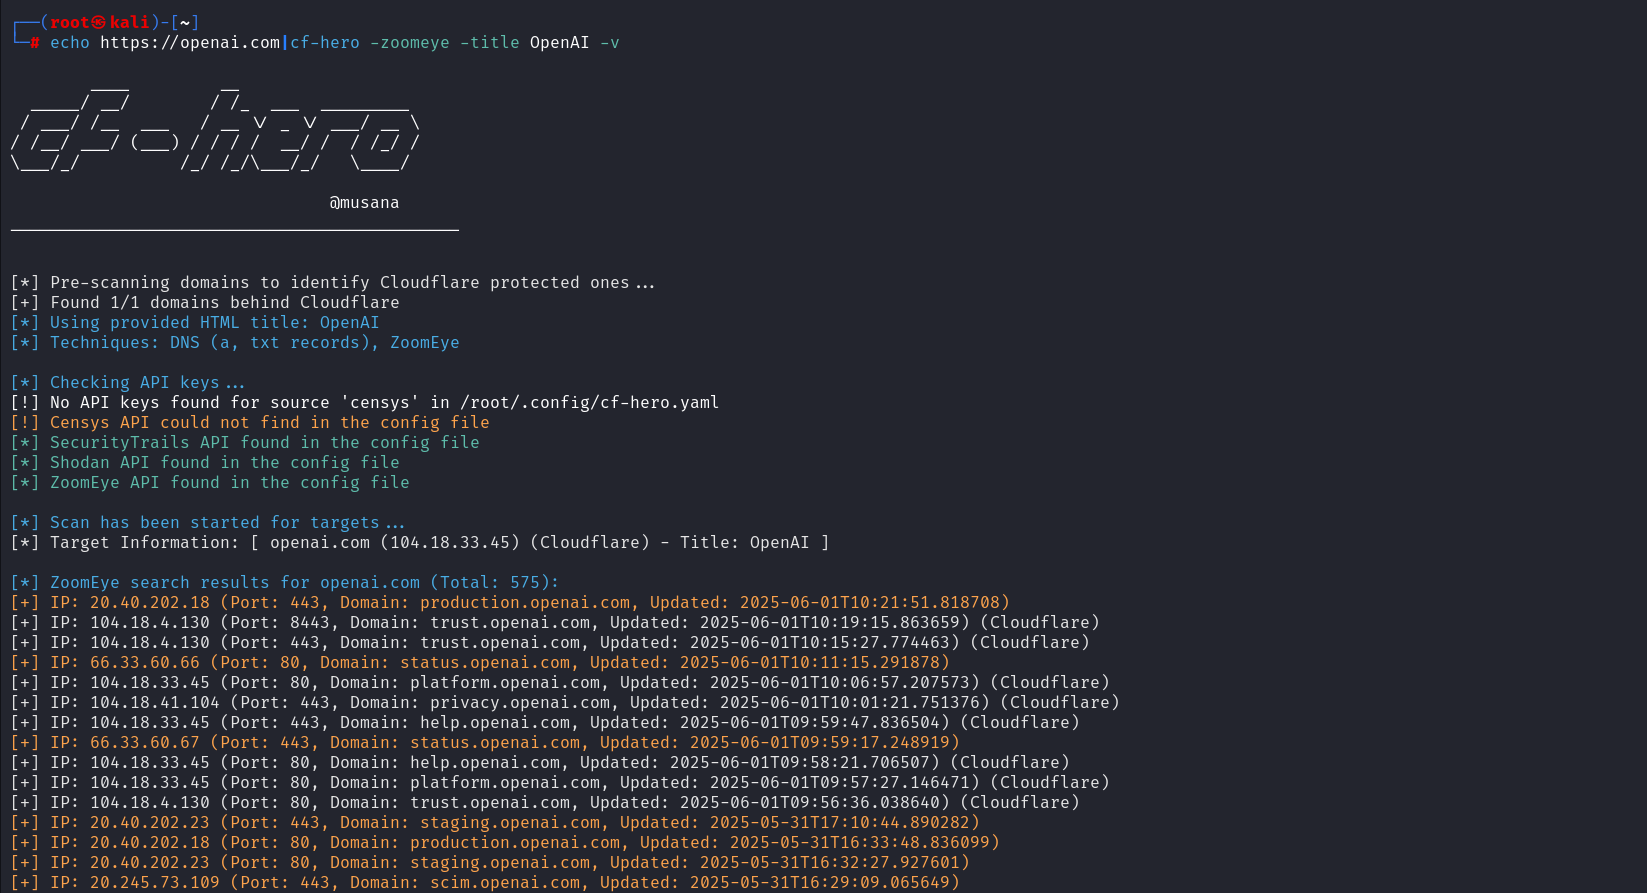 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 mysk-research/loupe
A privacy-focused iOS app that raises awareness about what native apps can see
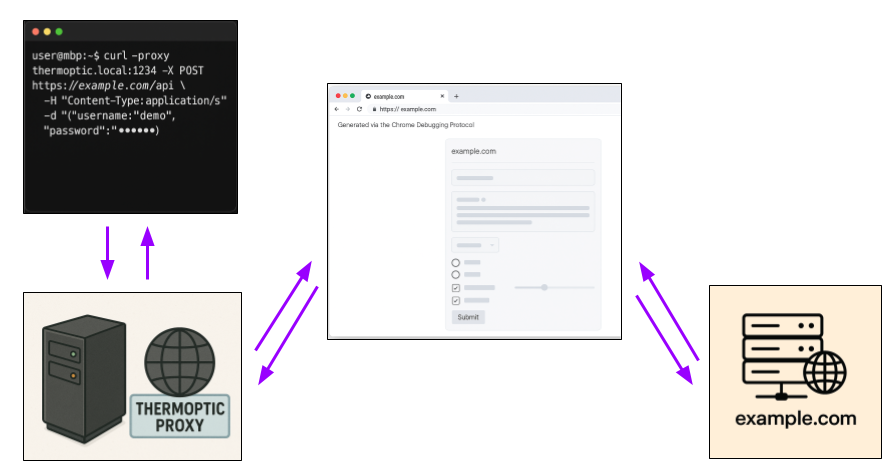 mandatoryprogrammer/thermoptic
A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
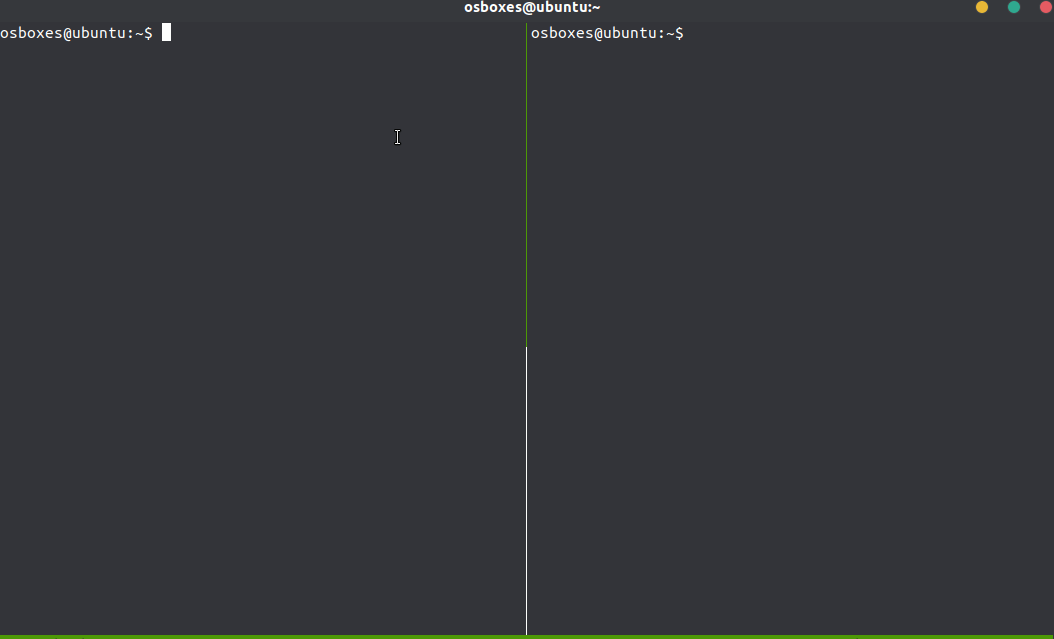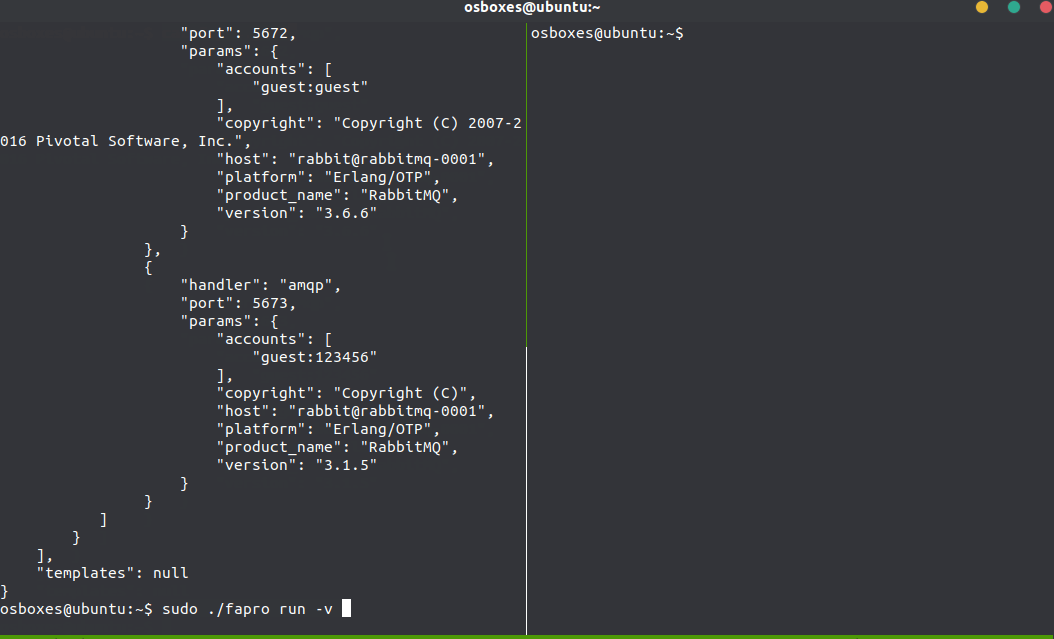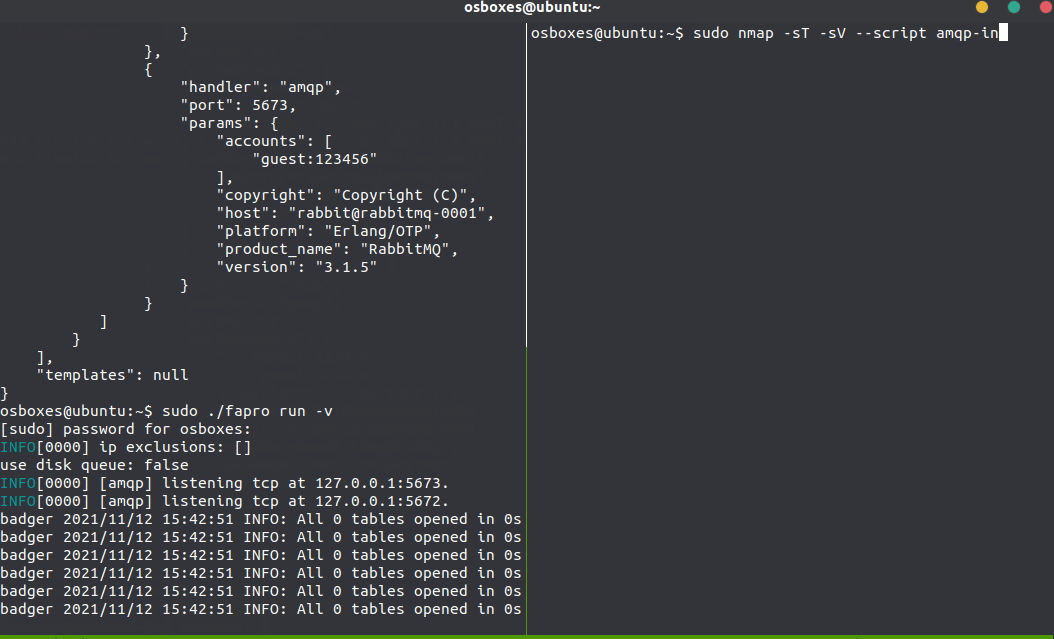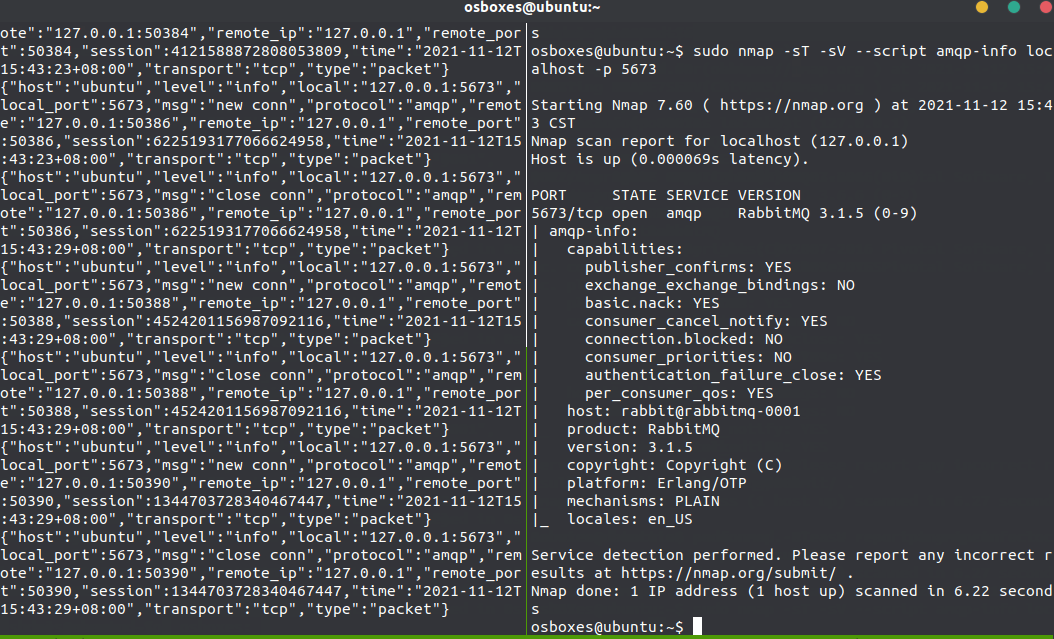 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 privacytests/privacytests
Automates browser privacy testing and renders human-readable results across fingerprinting, tracking, and data-leak vectors.
 mdp/linkedin-extension-fingerprinting
Documents and identifies 2,953 Chrome extensions silently probed by LinkedIn, providing tools to fetch extension names and analyze browser…