
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 b9ph0met/px-vm
Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
 tiliondev/fortress
Stealth Chromium engine that stops scrapers and browser agents from getting blocked, with one line of code change.
 vxfemboy/ghostport
A high-performance port spoofing tool built in Rust. Confuse port scanners with dynamic service emulation across all ports. Features customizable…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
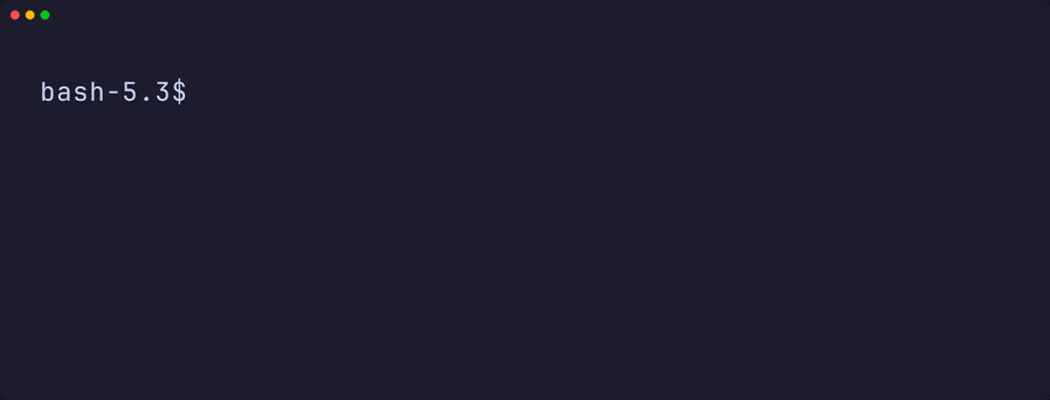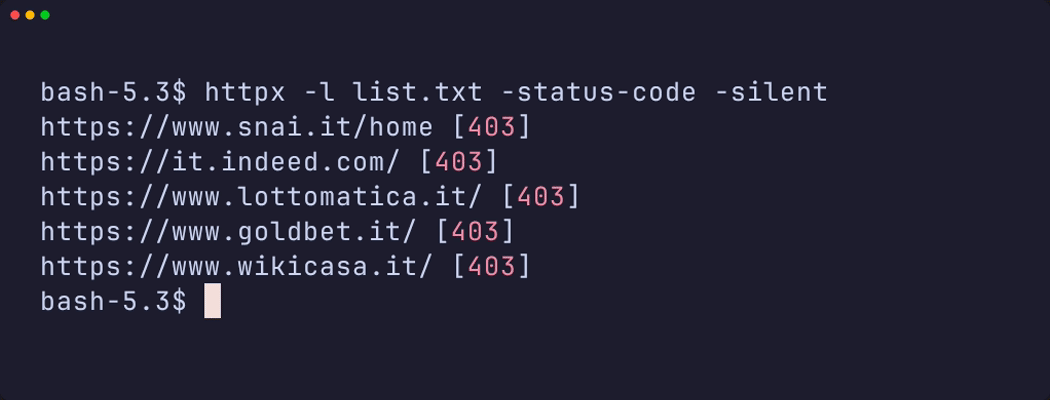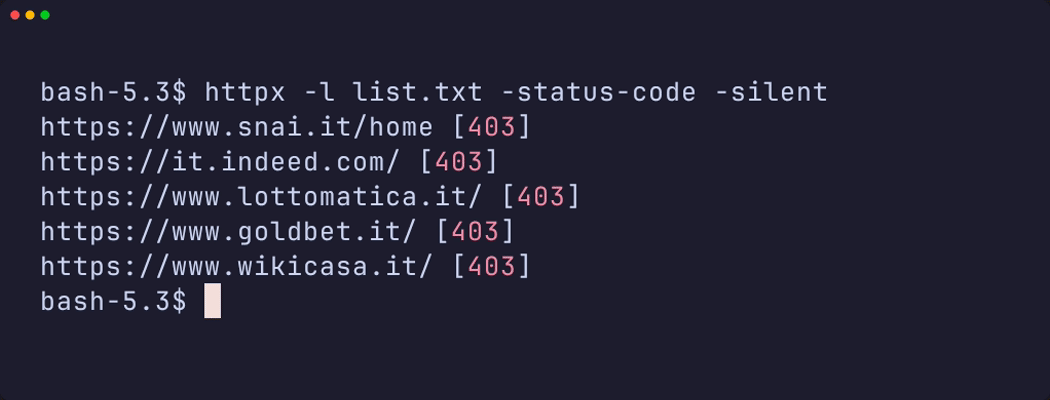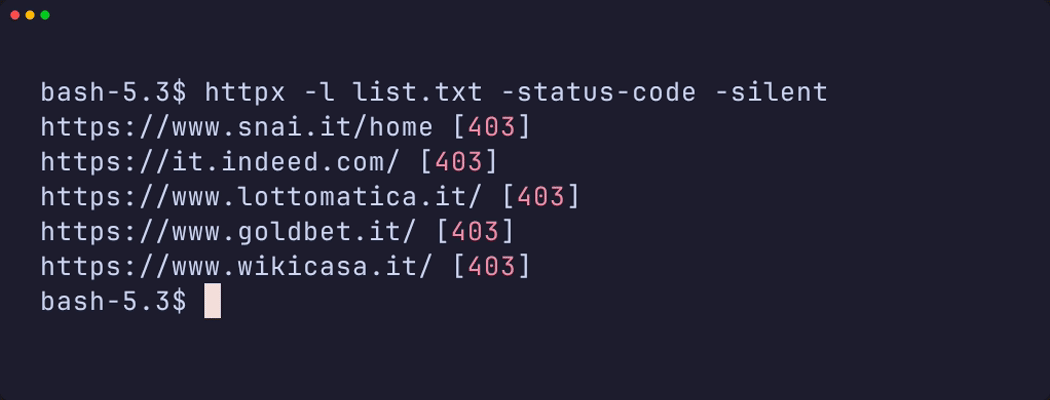 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 gmh5225/f31
Tool for hiding Kali Linux on the network
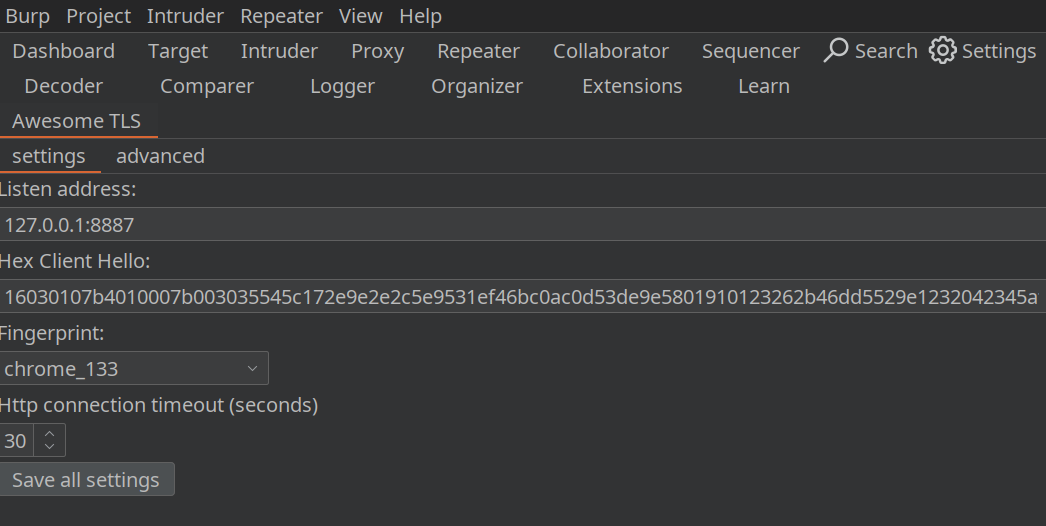 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
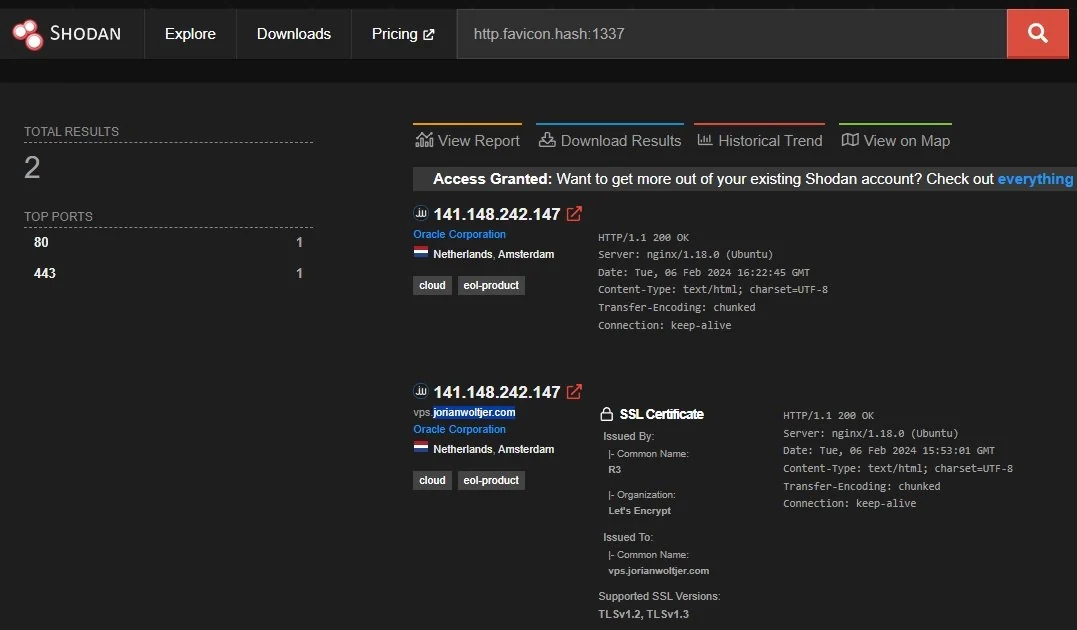 jorianwoltjer/shodan-favicon-preimage
Generate a favicon that results in any target hash on Shodan
 mohamedlahmeri01/vi-bot
Client-side bot detection library with 28 weighted modules, behavioral analysis, browser fingerprinting, honeypots, and server-side verification.…
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 privacytests/privacytests
Automates browser privacy testing and renders human-readable results across fingerprinting, tracking, and data-leak vectors.
 mdp/linkedin-extension-fingerprinting
Documents and identifies 2,953 Chrome extensions silently probed by LinkedIn, providing tools to fetch extension names and analyze browser…