
F31
 gmh5225/f31
Tool for hiding Kali Linux on the network
anti-botdefensive-toolsfingerprint-spoofing+6
gmh5225/f31Tool for hiding Kali Linux on the network
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 uazo/cromite
Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
 berstend/puppeteer-extra
💯 Teach puppeteer new tricks through plugins.
 privacytests/privacytests
Automates browser privacy testing and renders human-readable results across fingerprinting, tracking, and data-leak vectors.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 mdp/linkedin-extension-fingerprinting
Documents and identifies 2,953 Chrome extensions silently probed by LinkedIn, providing tools to fetch extension names and analyze browser…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
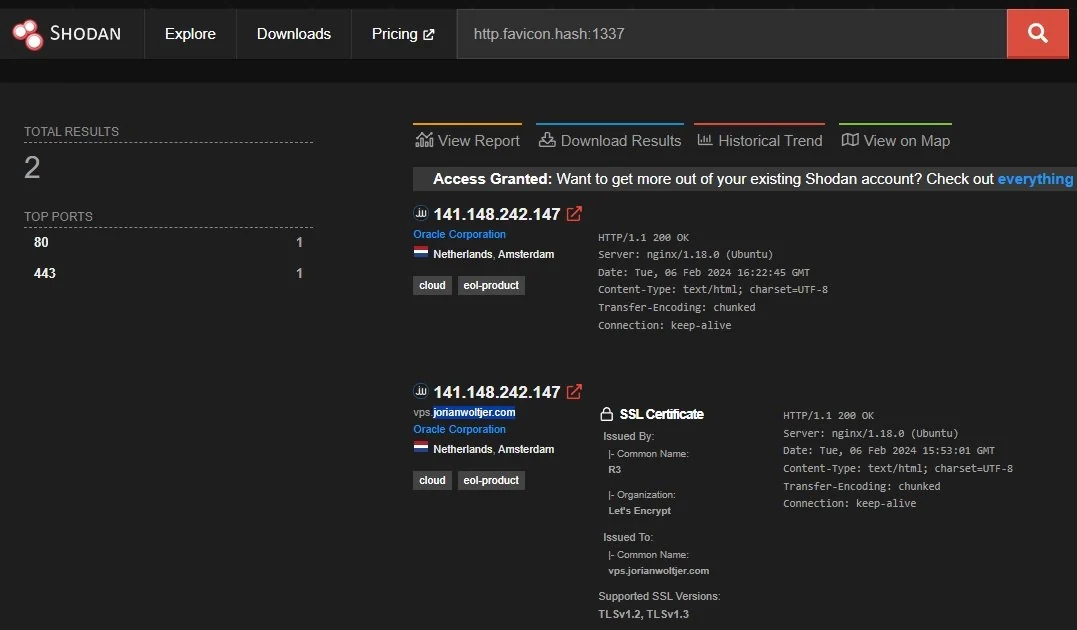 jorianwoltjer/shodan-favicon-preimage
Generate a favicon that results in any target hash on Shodan
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles