

garble
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
anti-botbinary-analysiscode-analysis+4
5.8k
burrowers/garbleObfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 bromite/bromite
Android Chromium fork with built-in ad blocking, anti-fingerprinting mitigations, DNS-over-HTTPS, and hardened privacy and security defaults.
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
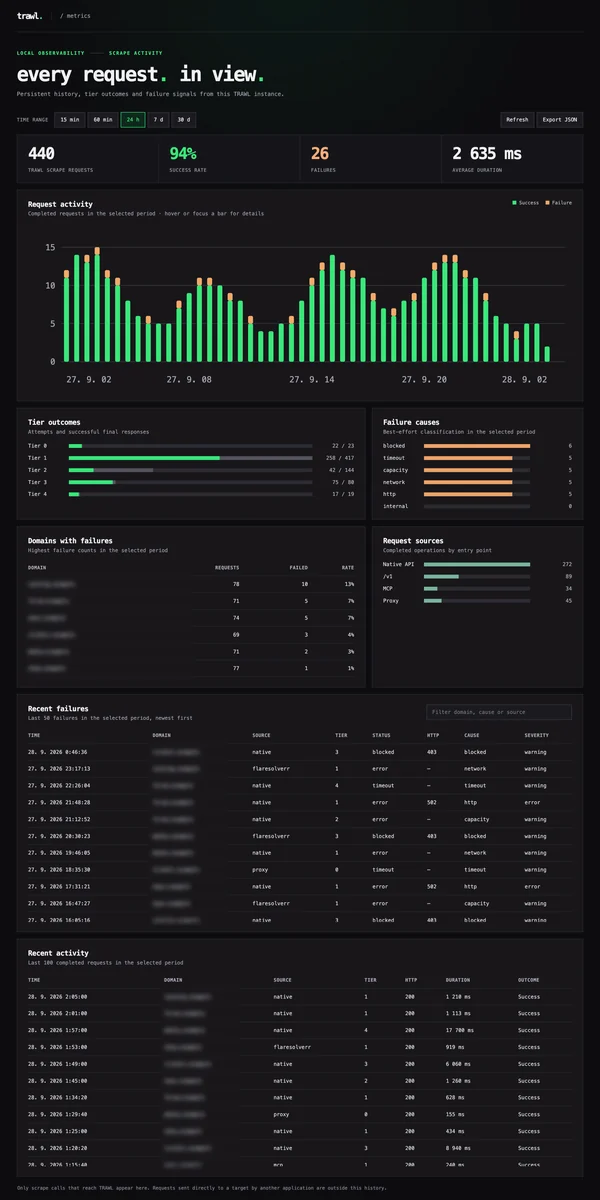 germondai/trawl
Self-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 gmh5225/f31
Tool for hiding Kali Linux on the network
 berstend/puppeteer-extra
💯 Teach puppeteer new tricks through plugins.
 microsoft/playwright
Browser automation framework with a single API for Chromium, Firefox, and WebKit. Supports web testing, scraping, screenshots, and network…
 1837620622/cloudflare-bypass-2026
Cloudflare Turnstile 绕过工具 | Cloudflare Bypass Tool based on SeleniumBase UC Mode | 支持 Mac/Windows/Linux
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
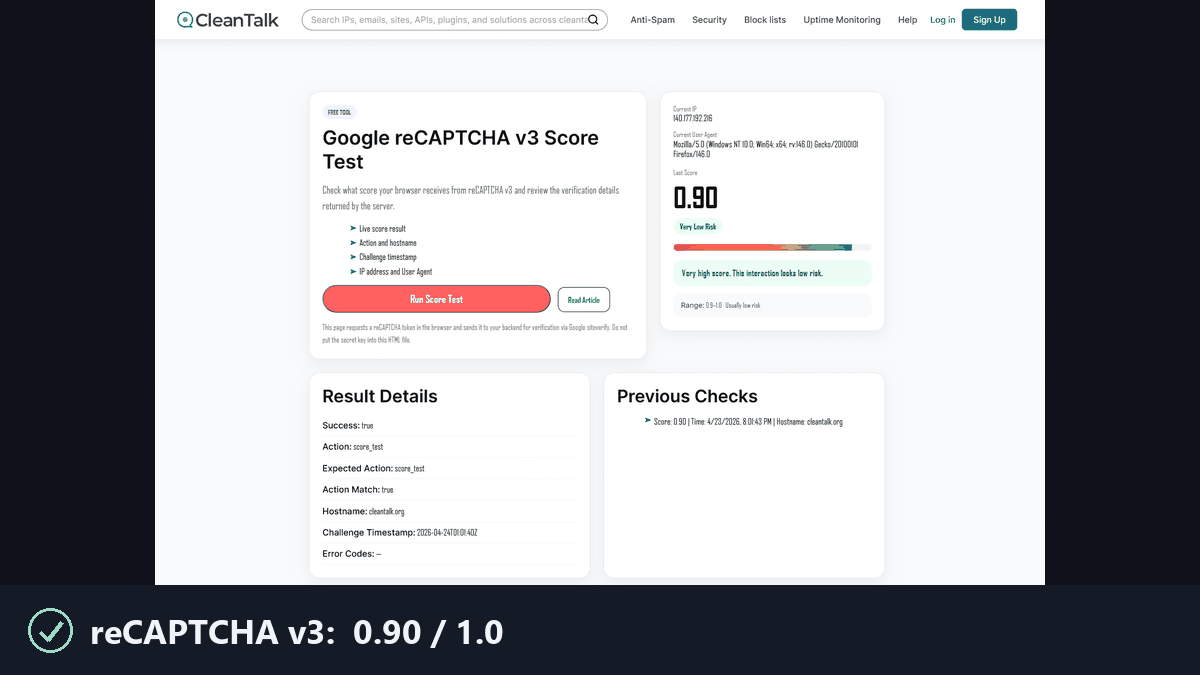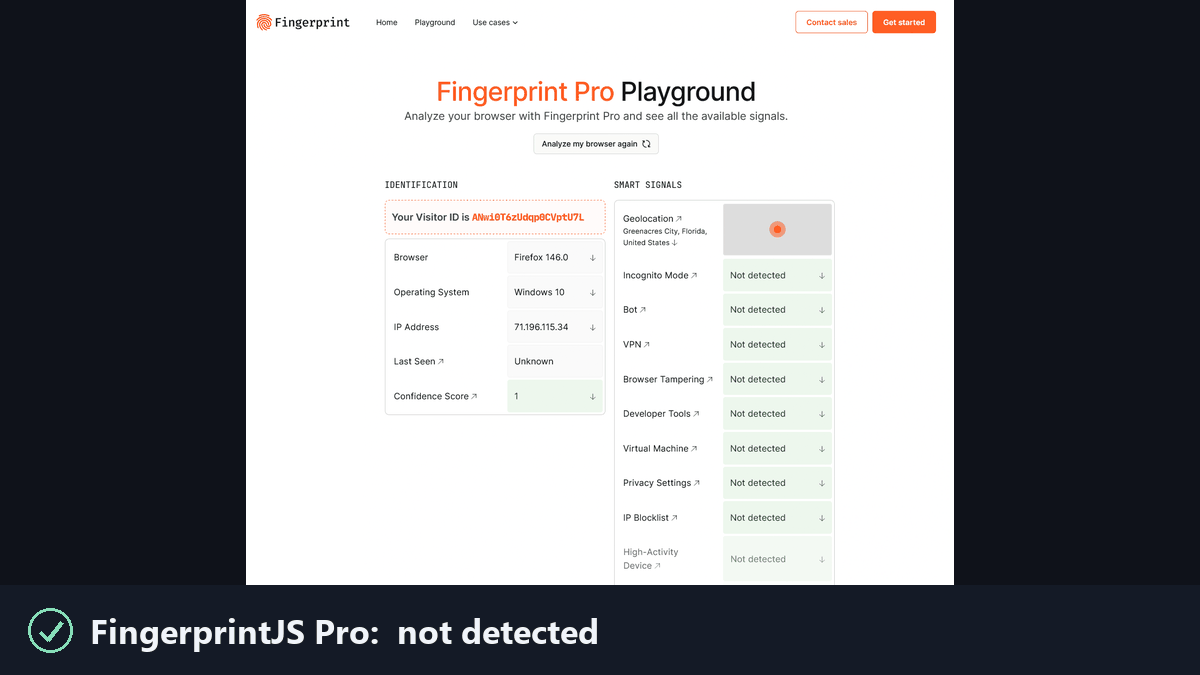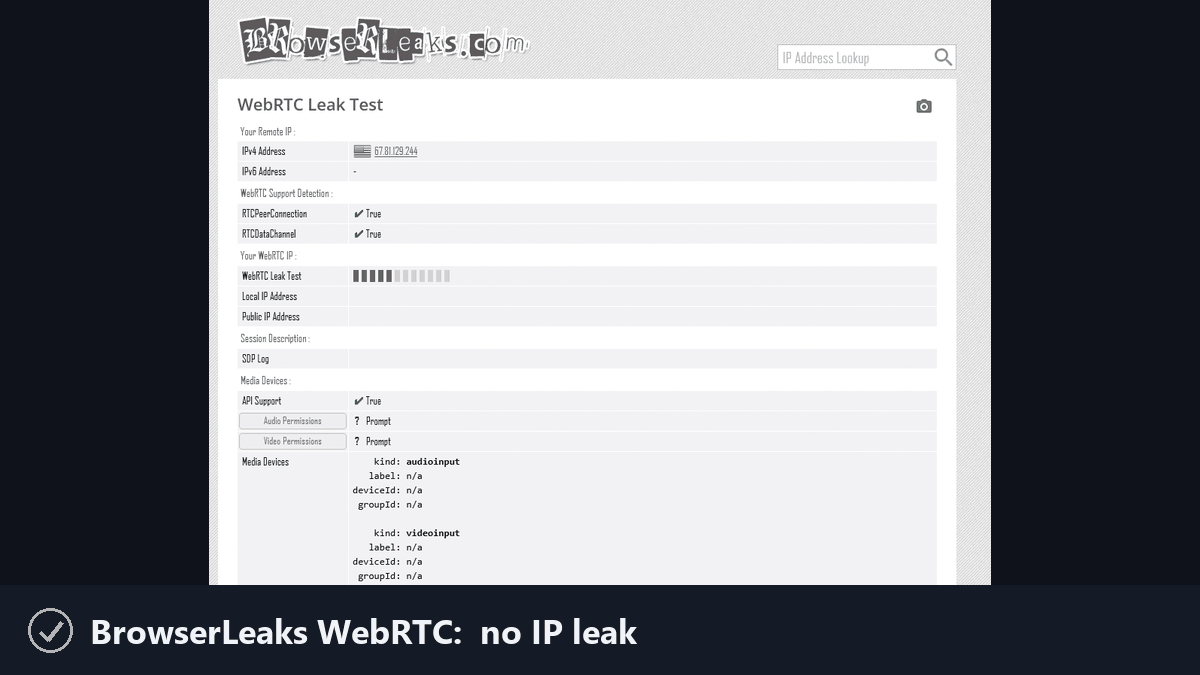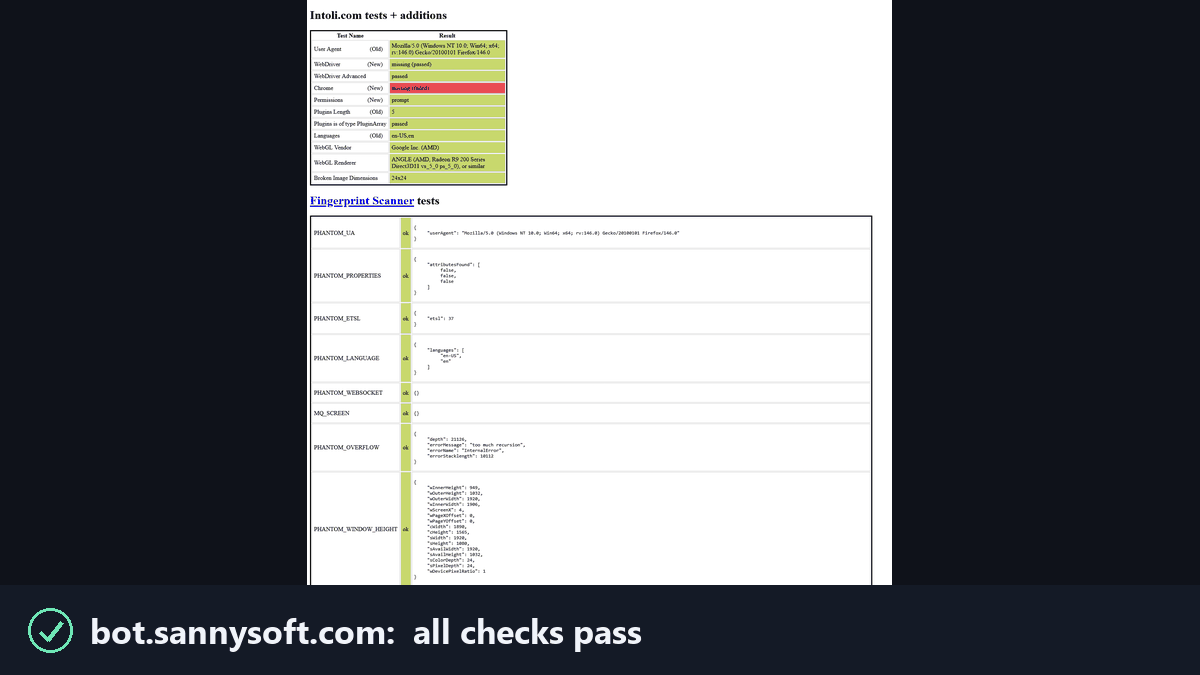 feder-cr/invisible_playwright
Playwright that anti-bots cannot see, so no captchas: same API, anti-detect stealth headless Firefox, undetected fingerprint, bypass bot detection,…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis