

elfxtract
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
binary-analysiseducationexploitation+2
73
m0n1x90/elfxtractAutomated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 infobyte/cve-2022-27255
Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
 sinsinology/cve-2024-6670
Proof-of-concept exploit for Progress WhatsUp Gold SQL injection authentication bypass (CVE-2024-6670). Includes root cause analysis and automated…
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
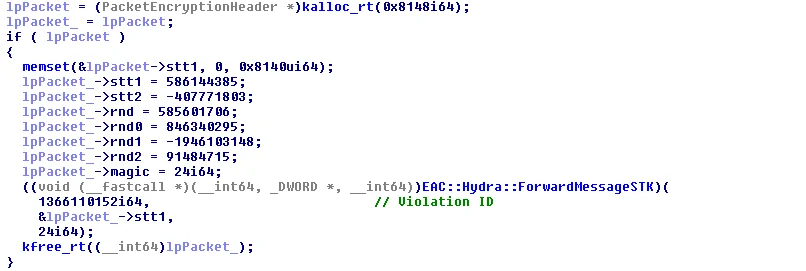 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…