Demonstration-of-CVE-2023-38831-via-Reverse-Shell-Execution

This project demonstrates a simulated exploitation of the WinRAR vulnerability CVE-2023-38831 to execute a reverse shell. The purpose of this task…

This project demonstrates a simulated exploitation of the WinRAR vulnerability CVE-2023-38831 to execute a reverse shell. The purpose of this task…

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…

Async mass-checker for authorized internal testing of CVE-2026-2631 exposure.

A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…

Python script to execute CVE-2025-24071

Mass vulnerability scanner targeting CVE-2024-36401 in GeoServer, using WFS requests to discover feature types and deliver payloads for automated…

Nuclei template for CVE-2024-46982, enabling automated detection and exploitation of the vulnerability in web applications.

A swiss army knife for pentesting networks

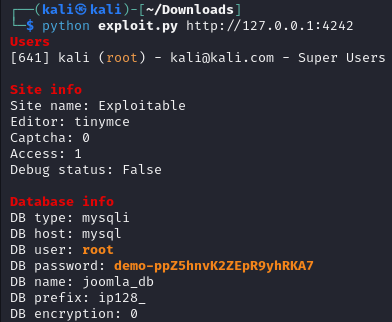
This Python implementation serves an educational purpose by demonstrating the exploitation of CVE-2023-23752. The code provides insight into the…

This is a proof of concept of the critical WinBox vulnerability (CVE-2018-14847) which allows for arbitrary file read of plain text passwords. The…

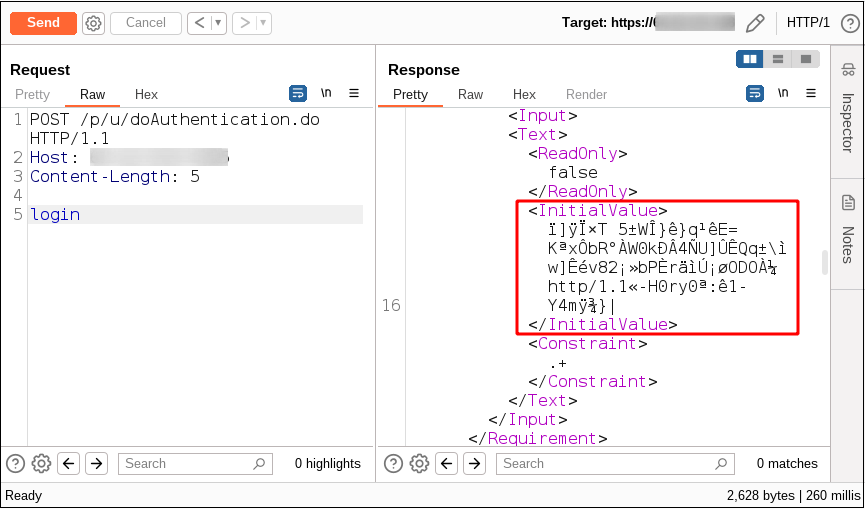
Python exploit for CVE-2025-5777 (CitrixBleed 2) memory leak in Citrix NetScaler. Sends malformed POST requests to leak ~127 bytes of RAM per…

the proof of concept written in Python for an unauthenticated malicious user can use a path traversal vulnerability to read arbitrary files on the…

This project is used for scanning cve-2020-0796 SMB vulnerability

Red Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.

Passive security checker for CVE-2026-48908 affecting SP Page Builder.

Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…

Python-based scanner to detect CVE-2014-6271 (Shellshock) vulnerability in CGI-enabled servers, using Google search to discover potential targets.

Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…