
CVE-2026-73570
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
educationemail-securityexploitation+3
5
horkimhab/cve-2026-73570Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
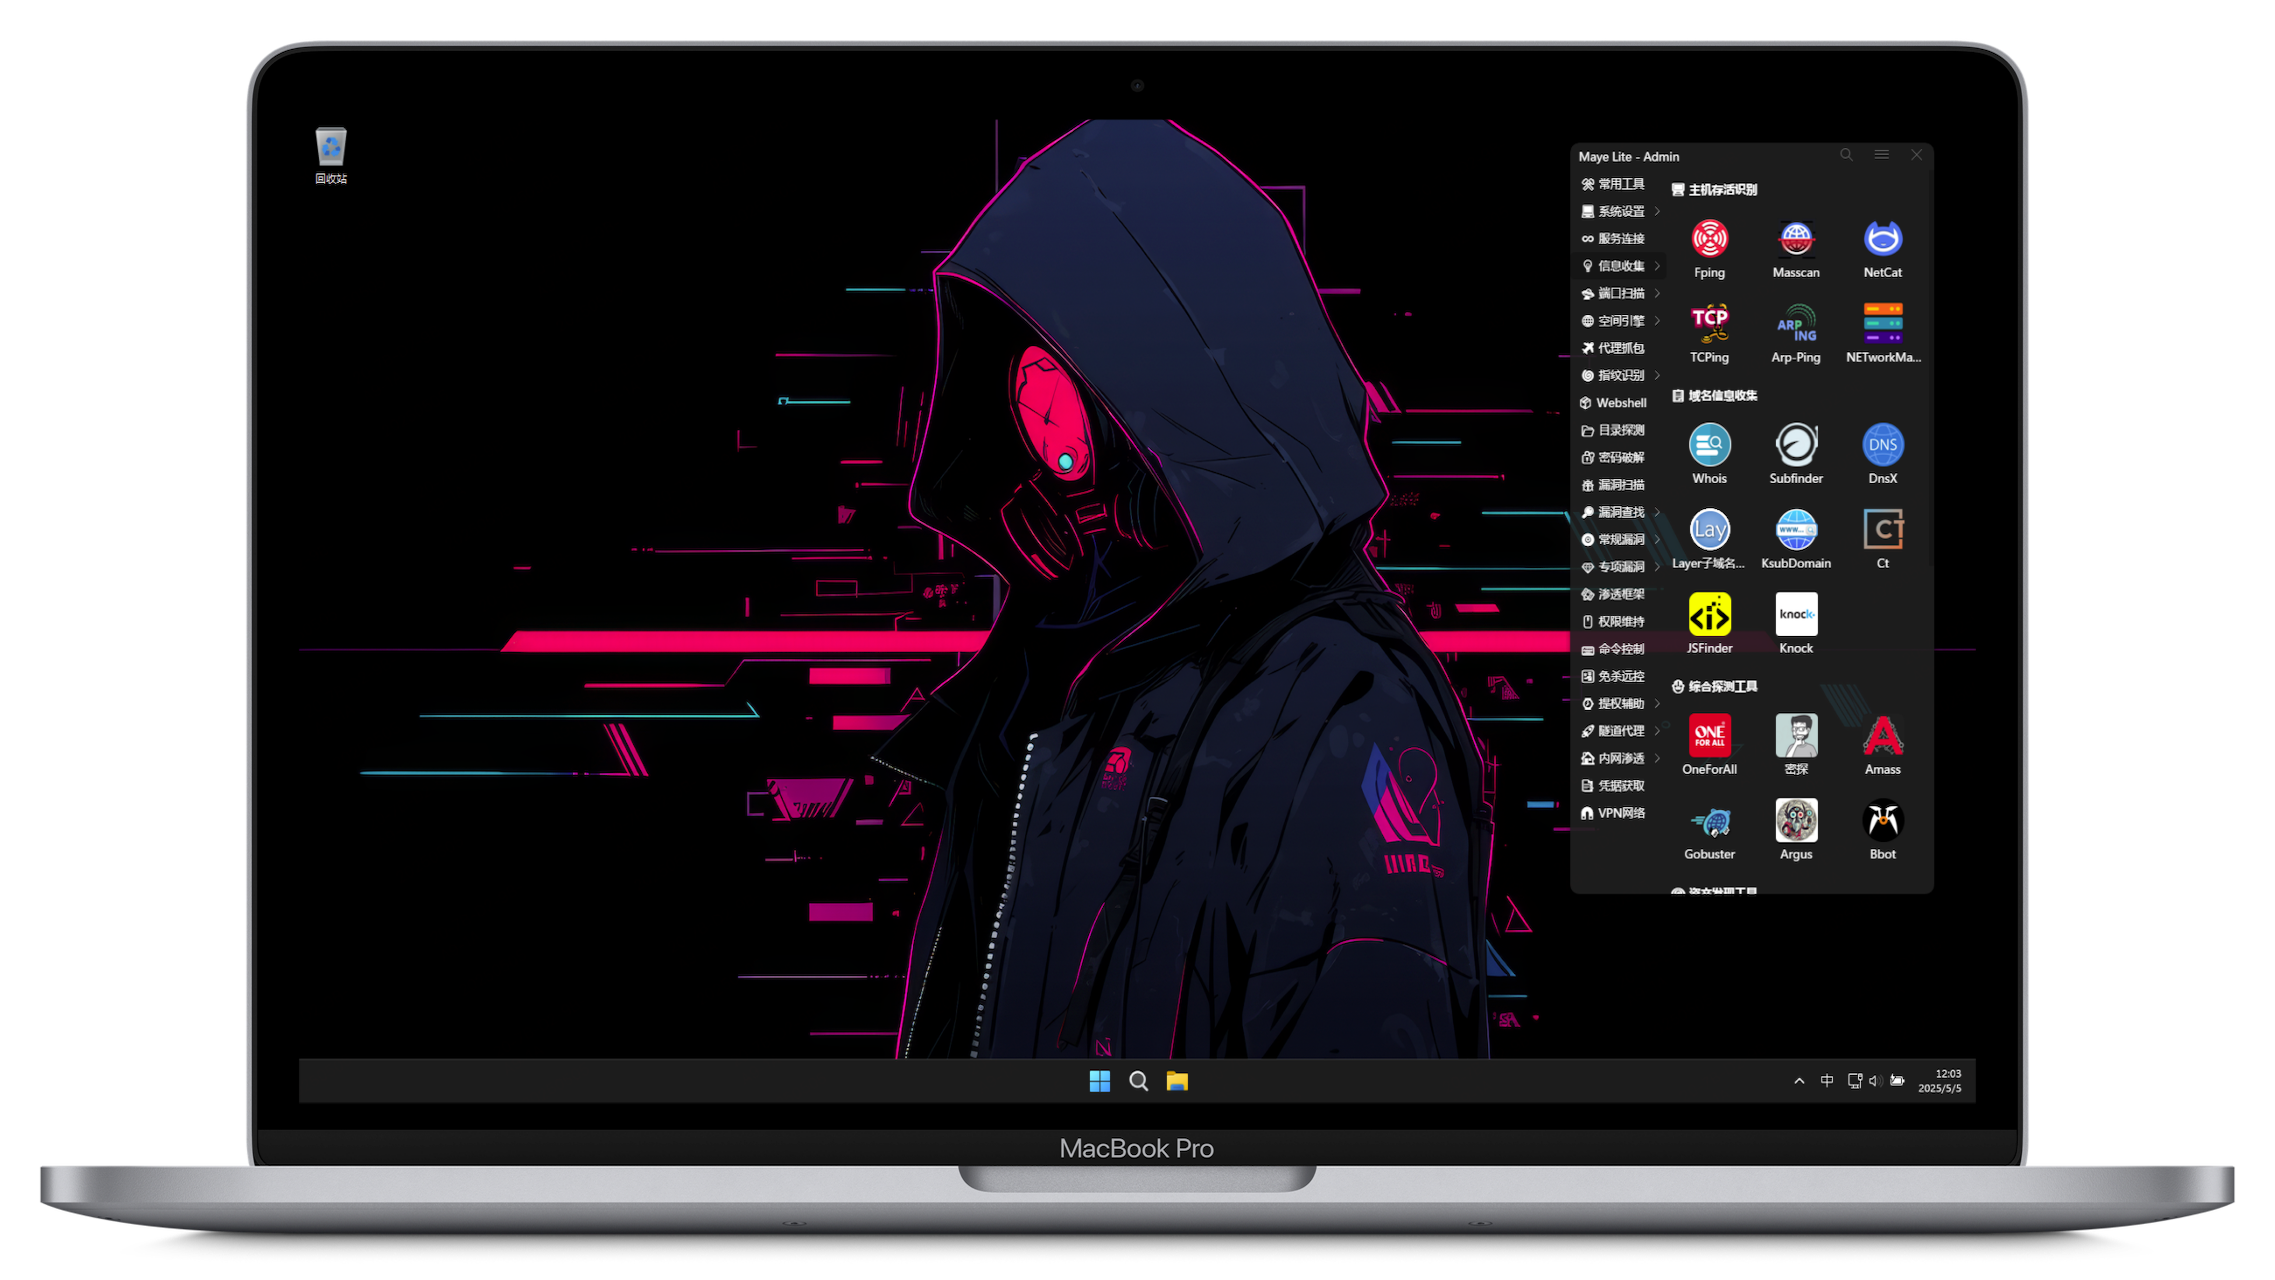 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 adk86/cve-vulnerability-research-exploit-analysis
Researched and executed real-world CVE exploits in a controlled sandbox: CVE-2000-0168 DoS on Windows 95, ARP Spoofing with NTLMv2 credential…
 ikkisoft/parrotng
Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
 zerozenxlabs/cve-2025-61882-oracle-ebs
Operational exploit for CVE-2025-61882 in Oracle E-Business Suite, with research artifacts for defensive validation, detection engineering, incident…
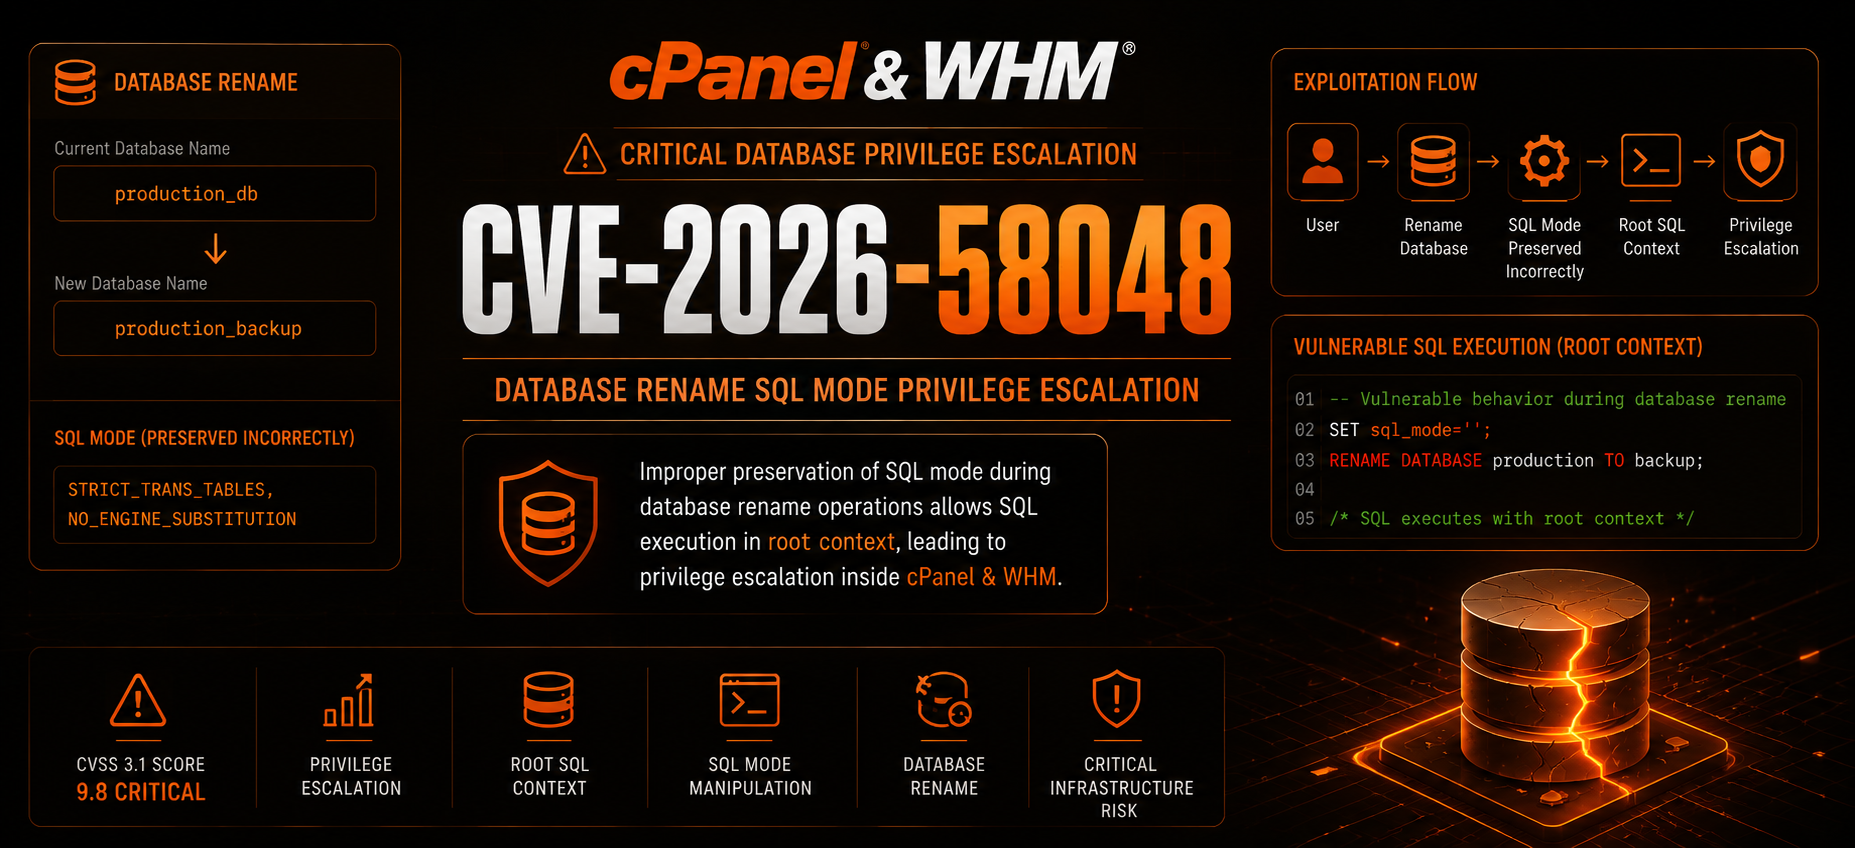 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
 sachinart/cve-2025-61882
Multi-threaded scanner for CVE-2025-61882 in Oracle E-Business Suite, exploiting HTTP request smuggling to achieve unauthenticated remote code…
 greynoise-intelligence/zimbra_cve-2022-37042-_cve-2022-27925
Exploit for Zimbra Collaboration Suite vulnerabilities CVE-2022-37042 and CVE-2022-27925, enabling unauthenticated remote code execution and file…
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 venablee/cve-2026-30251
Reflected XSS vulnerability disclosure for ZenShare Suite login_newpwd.php, allowing arbitrary JavaScript execution via crafted URL in codice_azienda…
 gquere/cve-2017-6913
Stored XSS proof-of-concept exploit for open-xchange OX App Suite webmail, demonstrating unescaped HTML time tag event attributes leading to…
 knqyf263/ssrfnginx
Exploit Server-Side Request Forgery (SSRF) vulnerabilities through nginx configurations. Enables testing and exploitation of SSRF in web applications.