burp-alfresco-referer-proxy-cve-2014-9301

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Proof-of-concept exploit for CVE-2024-2054, demonstrating insecure deserialization RCE in Artica-Proxy administrative web application. Includes…

Exploit script for CVE-2025-55182 that deploys a Godzilla memory shell on vulnerable web servers, with support for proxy and encoding options.

Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…

Python-based proof-of-concept exploit for CVE-2021-3019 targeting Lanproxy, enabling remote code execution via directory traversal in the web proxy…

Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…

Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)

CVE-2015-3224

Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…

Go-based MITM exploit demo for OpenSSL CVE-2014-0224 (CCS Injection) targeting RC4-SHA cipher, with server/client proxy setup for testing TLS…

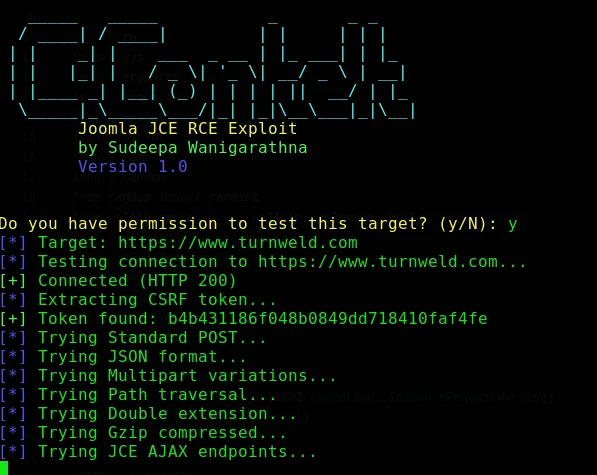
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…

Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…

Proof-of-concept exploit for CVE-2019-14319, demonstrating a specific vulnerability in a web application for security testing and verification.

PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…

PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…

Automated scanner for unauthenticated arbitrary file upload and remote code execution in ProSolution WP Client (CVE-2026-2942). Supports…